KOPEXA · ISO 27001
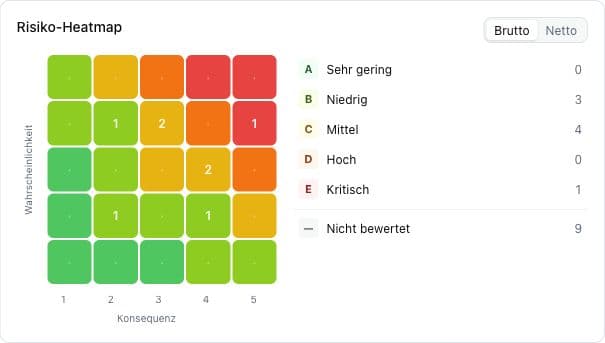
Prepare for your audit. Keep your evidence together.
Which requirements are still open? Who owns them? Where is the evidence? Prepare for your ISO 27001 audit with connected risks, tasks and documents in Kopexa.
For ISO 27001, TISAX, NIS2, DORA and other requirements.
Request a personal demoIn your demo: see what remains before the audit
- 01Assess risks
- 02Assign actions
- 03Keep evidence ready
“I often didn't know where to put the evidence. Now it's: bring it on, I find the right place instantly!”
Teams working with Kopexa







From an open item to traceable evidence.
- 01
Establish your starting point
Record the scope of your ISMS and the requirements that remain open. In your demo, we discuss where you are today.
- 02
Give the work clear ownership
Connect risks and actions to responsible people and tasks. Policies and documents remain linked to the work.
- 03
Keep evidence traceable
Use versioning, approvals and recurring currency reviews to show what has been implemented and what still needs attention.
Kopexa supports preparation and ongoing ISMS operations. An independent certification body performs the certification audit. Timing and outcomes depend on your starting point and implementation.
CSN Solutions · Customer story
CSN Solutions: Less evidence stress. More time for the actual ISMS.
How an IT service provider modernized its ISO 27001 management system, built up over more than ten years, with Kopexa, all the way to a strength in the audit report.
Before
An ISMS certified for more than ten years ran on SharePoint, Excel, tickets and network drives. As the company grew, those tools stopped scaling with it.
With Kopexa
Kopexa connects controls, policies, tasks and evidence in one system and guides the team through daily ISMS work along clear audit trails.
Rated a strength in the audit report
Continuous audit readiness during day-to-day operations and a recertification report that explicitly documents the use of Kopexa as a strength.
Read the full case studyWhat to expect from your personal demo
01
Your situation
We discuss your standards, current setup and the tasks that take up your time.
02
Your look at the product
We show you how assets, risks, measures and evidence work together in Kopexa.
03
Your next steps
Ask your questions and decide at your own pace afterwards. There is no obligation.
Your questions before the demo
Is Kopexa only for ISO 27001?
Kopexa is an integrated GRC platform. You can manage ISO 27001, TISAX, NIS2, DORA and other requirements in one shared system.
We already have an ISMS. Is Kopexa a fit?
Kopexa also supports developing an existing ISMS. During the demo, we review your current processes and how to organize risks, measures and evidence centrally.
Can we manage several standards at once?
Yes. Shared information and evidence can be reused across requirements. We show you how this works for your standards during the demo.
What happens to our spreadsheets and existing tools?
Bring your questions about Excel, SharePoint or your current software. We discuss which content you want to retain and assess the relevant migration and integration options.
Do I need to create a trial account?
No. You request a personal demo. We contact you with time slots and show you the product without registration or obligation.
Do security, not ISMS upkeep.
With Kopexa you are not just better at audits. Your security lives day to day instead of aging in a folder. See it live.
Request a personal demo