ISMS
Keep information security under control.
"Show the auditor the truth. With one click."
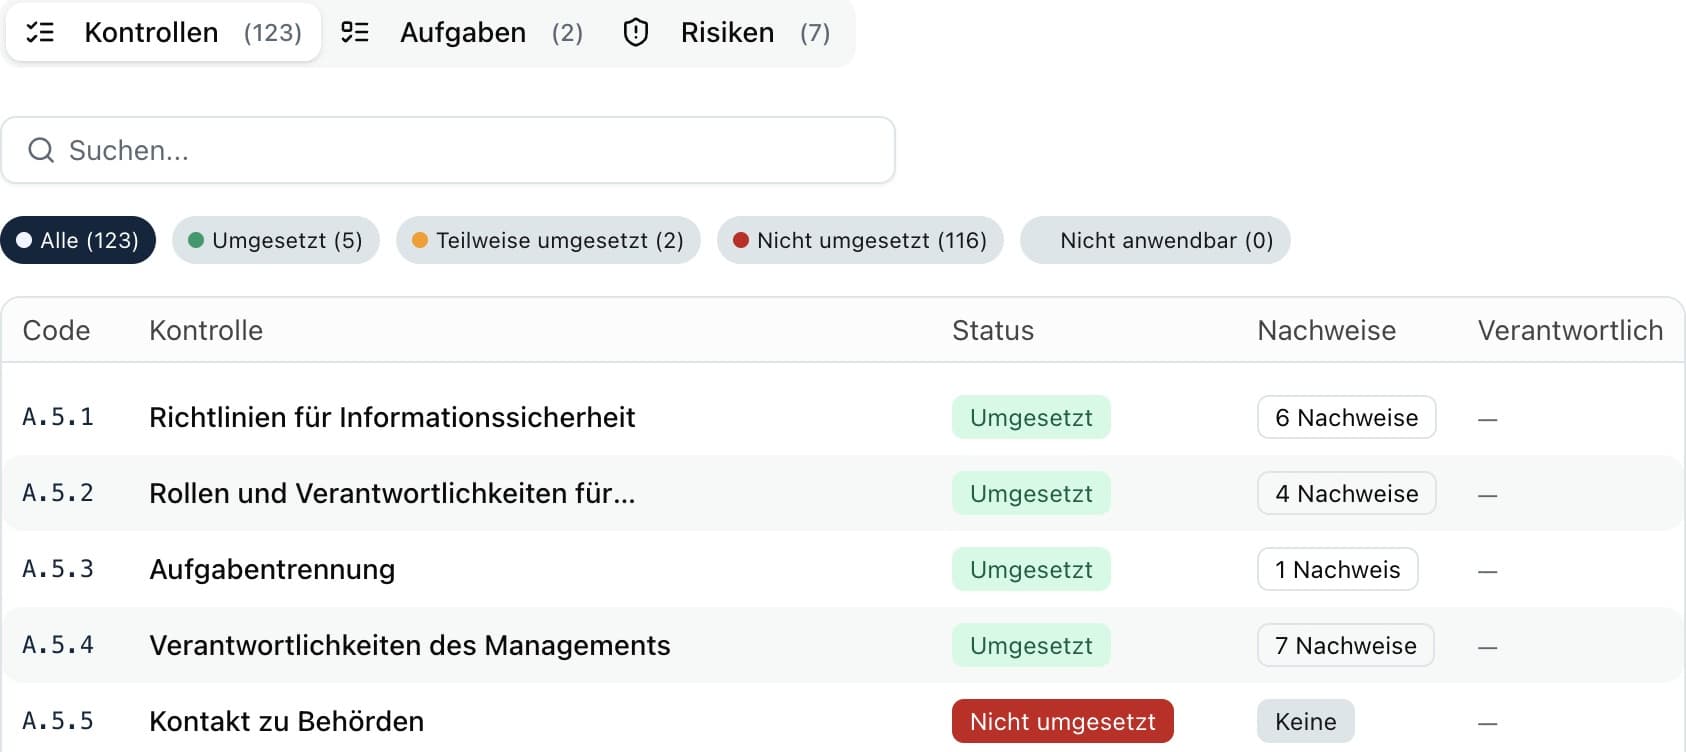
- Controls + Measures · dual model for any standard
- Live gap analysis · status now, not in the quarterly
GRC software · One shared foundation
Kopexa connects risks, processes, controls and evidence in one shared GRC platform. For ISO 27001, NIS2, TISAX, quality management and further requirements – without maintaining information twice.
From 249 EUR/month · Hosted in Europe
One shared foundation. For teams, integrations and AI assistants.
Compliance is not a folder. It is infrastructure.
Our customers






Customer voice · ISO 27001
“I often didn’t know where to put the evidence. Now it’s: bring it on, I find the right place instantly!”
Gunnar Mentzel · Information Security Officer · CSN Solutions
Read the customer storyWhy Kopexa
Policies in versions. Risks across Excel tabs. Evidence in the inbox. Works fine. Until the first auditor asks how it connects.
73 files. Nobody knows which is current.
Cross-mapping across all modules
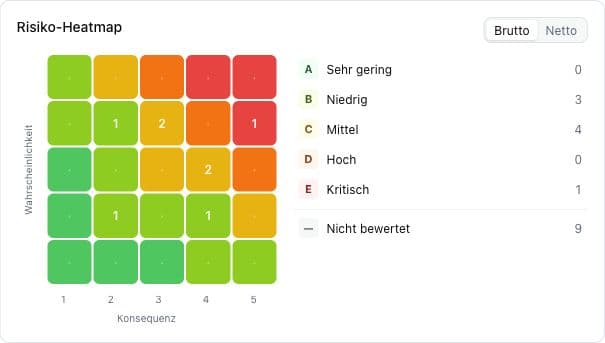
Risk, control, policy, evidence, asset, and vendor in one data layer. The auditor clicks through, instead of searching.
Capture → Connect → Demonstrate
01
Bring your risks, assets and processes together. See which business functions depend on which systems, people and suppliers.
Explore this workflow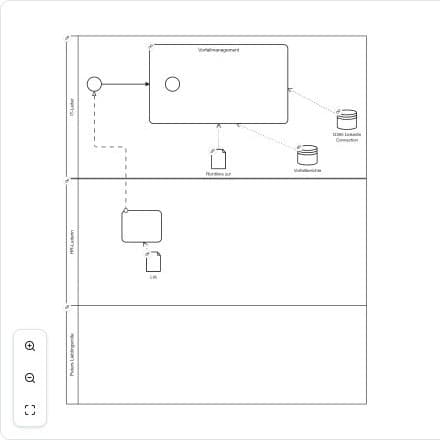
02
Link tasks to risks, controls and processes. Your team sees what needs doing and can discuss the work in its context.
Explore this workflow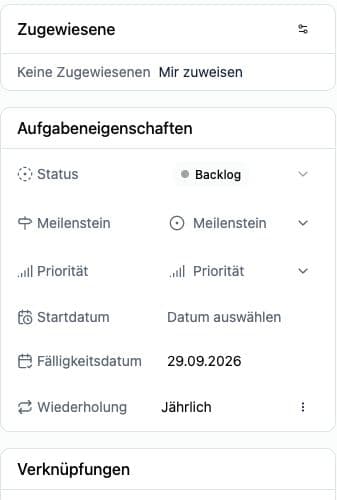
03
Review whether a policy is still current, independently of its version and approval. Set reviewers and review intervals so accountability stays clear.
Explore this workflow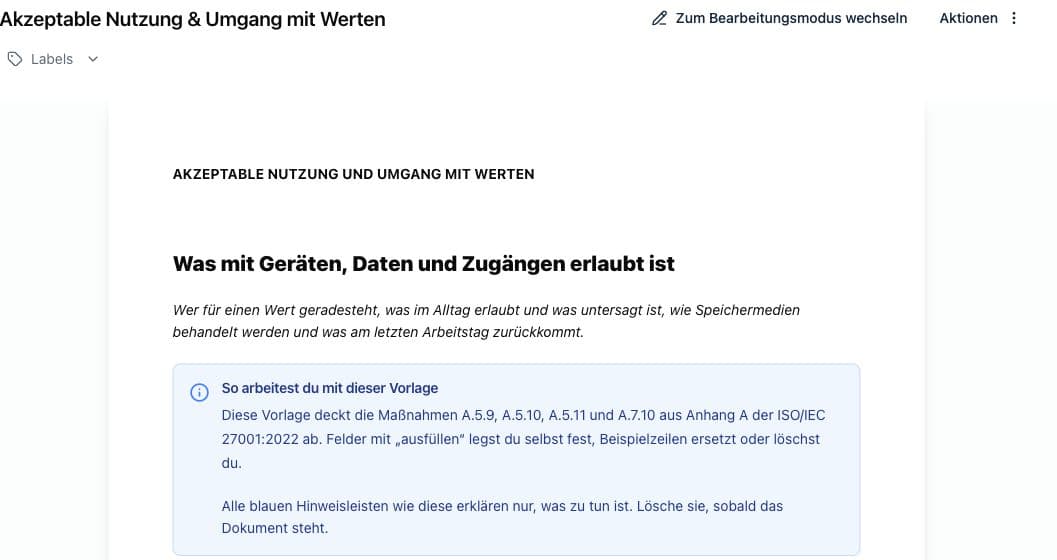
Connect ChatGPT or Claude to Kopexa through MCP. Ask about your work instead of copying information into a chat.
Example conversation · Kopexa MCP
You ask
“Show me all open measures for the next ISO 27001 audit.”
From your Kopexa space
| Measure | Owner | Status |
|---|---|---|
| Review access rights | IT team | Open |
| Update the security policy | ISMS team | Open |
Example data. In use, the assistant retrieves current information from your selected space within your permissions.
Kopexa’s built-in AI also supports your team, for example when developing risk scenarios. Your team stays in charge of decisions.
Explore it in a demoTurn requirements into responsibilities, controls and evidence.
Find your next stepConnect the work that currently sits in spreadsheets, folders and tickets.
Find your next stepUse a shared foundation rather than maintaining each standard separately.
Find your next stepThe platform
Four modules, one data layer. Risk, security, quality, and documents share the same assets, policies, and evidence. No duplicate maintenance. No tool sprawl. No SharePoint as your management system.
ISMS
"Show the auditor the truth. With one click."
ERM
"Not where it's burning. Whether you have it handled."
QMS
ISO 9001 processes, document control, internal audits, CIP workflow. One tool, many management systems.
Explore this areaDMS
Policies and evidence versioned, approved, and acknowledged. No SharePoint chaos, no 'which version is current?'.
Explore this areaCreate a new version
Develop changes together before releasing them.
Review and approve
Make the approved version clear to your team.
Check it is still current
Set a reviewer and an interval, independently of version approval.
Incident management
When an incident occurs, your team needs a shared picture. Bring impact, responsibilities, recorded reporting obligations and progress together in Kopexa.
Record the incident, assess its impact and link affected assets and parties.
Keep the owner, severity and reporting status together with the incident.
Review recorded reporting deadlines and the timeline from detection to resolution.
The ecosystem
Cloud providers, dev tools, business apps. Ready-made frameworks. And an OSCAL builder for everything else that shows up.
Integrations


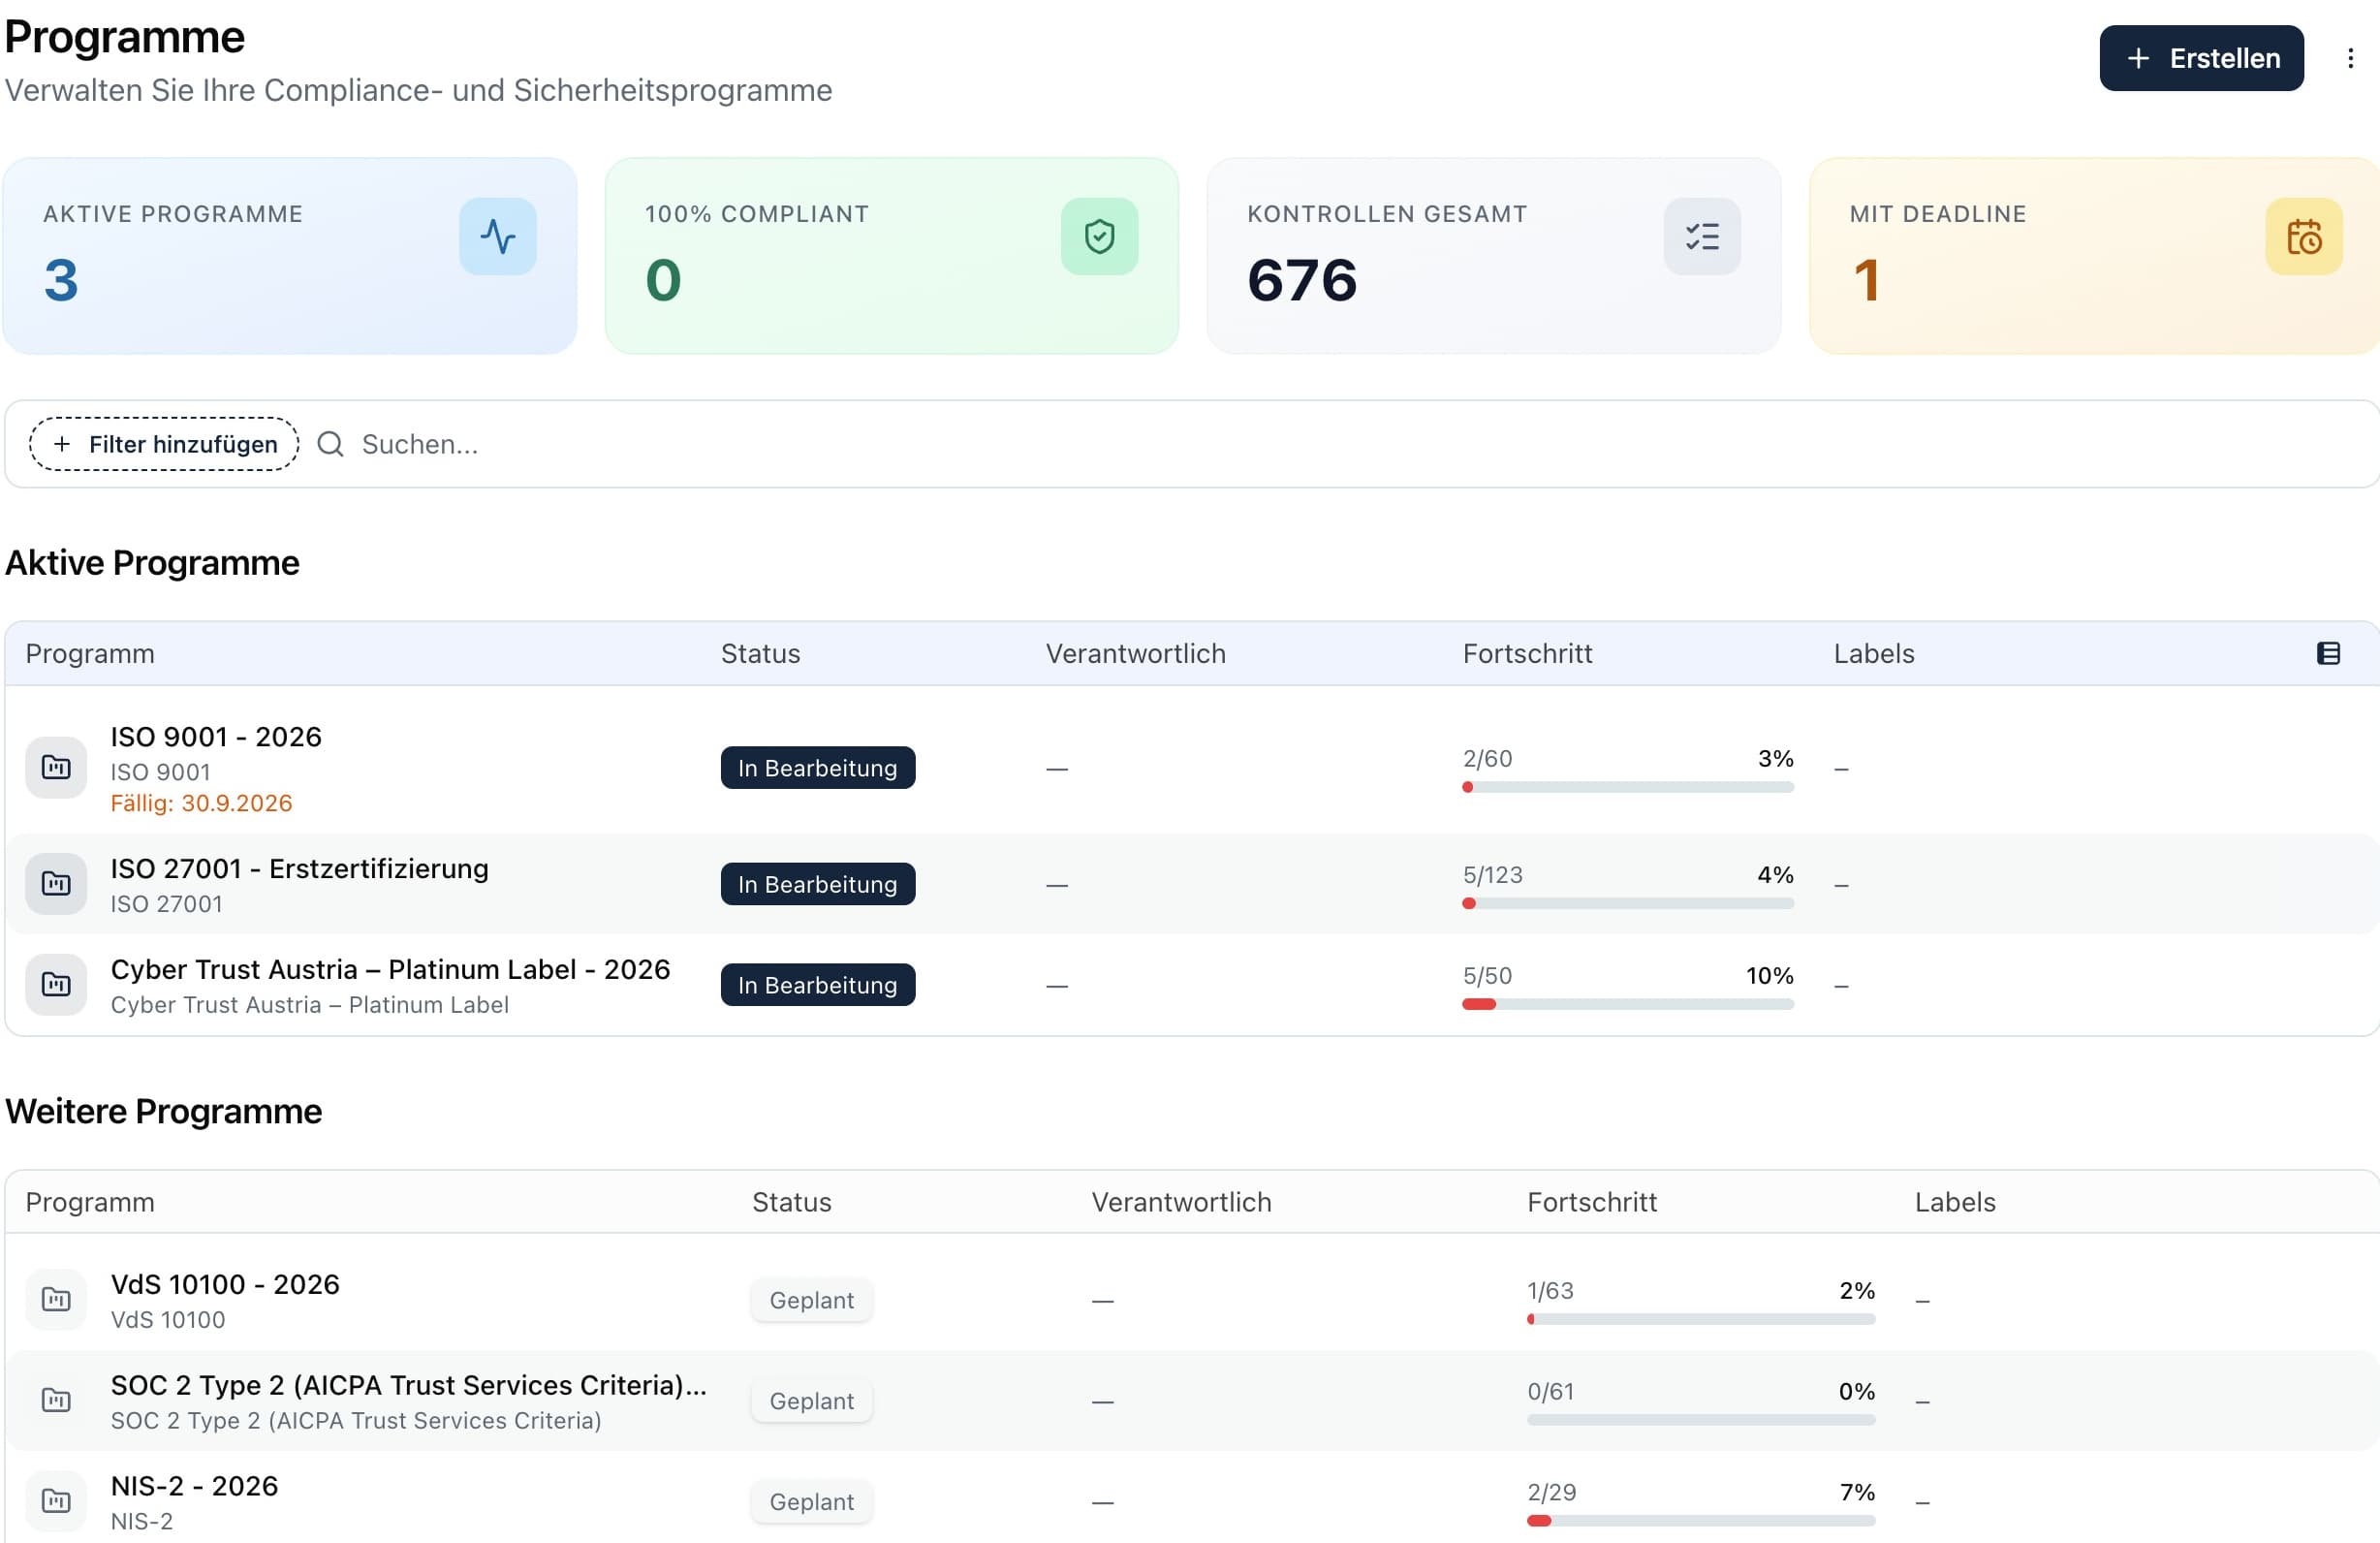
Manage ISO 27001, NIS2, TISAX and further programs together. Keep progress and responsibilities in view, and connect the work to your risks, tasks and evidence.
Find your standardCompare estimated implementation effort for different framework combinations. These model estimates are a starting point, not a guarantee for your project.
Latest case study
All case studies
Pricing
Get started with Lite from €249 per month.
Kopexa Pro from €599 per month with unlimited users per space. Compare the plans to find the right fit for your team.
View pricingAn existing management system is a starting point. In the demo, we can look at your policies, controls and evidence and discuss how to bring them together. CSN Solutions modernized an ISMS with more than ten years of history.
Yes. Kopexa connects frameworks through shared risks, actions and evidence. The framework calculator helps you explore possible overlaps; its estimates are not a guaranteed saving.
Kopexa also covers risk management, quality, policies, business processes and impact analysis. Shared links let these areas work together.
We’ll explore workflows relevant to your team, such as connecting risks and actions, reviewing policies or understanding process dependencies. You can ask questions about your starting point and implementation.
Show us where your team is today. Together, we’ll explore how Kopexa can support your processes, frameworks and everyday work.
Book a demo