Explore the Kopexa blog
Compliance & Regulation
What new rules mean for your organisation, and how to turn requirements into practical next steps.
1–10 of 18
NIS2 and DORA reporting deadlines compared in 2026
NIS2 and DORA use different deadline anchors. Compare initial, intermediate and final reports without starting the wrong timer.
 Julian Köhn·
NIS2 company-size thresholds in 2026: Assess Germany correctly
Assess NIS2 scope in Germany: review activity, employees, turnover, balance-sheet total and related companies in the right order.
Julian Köhn·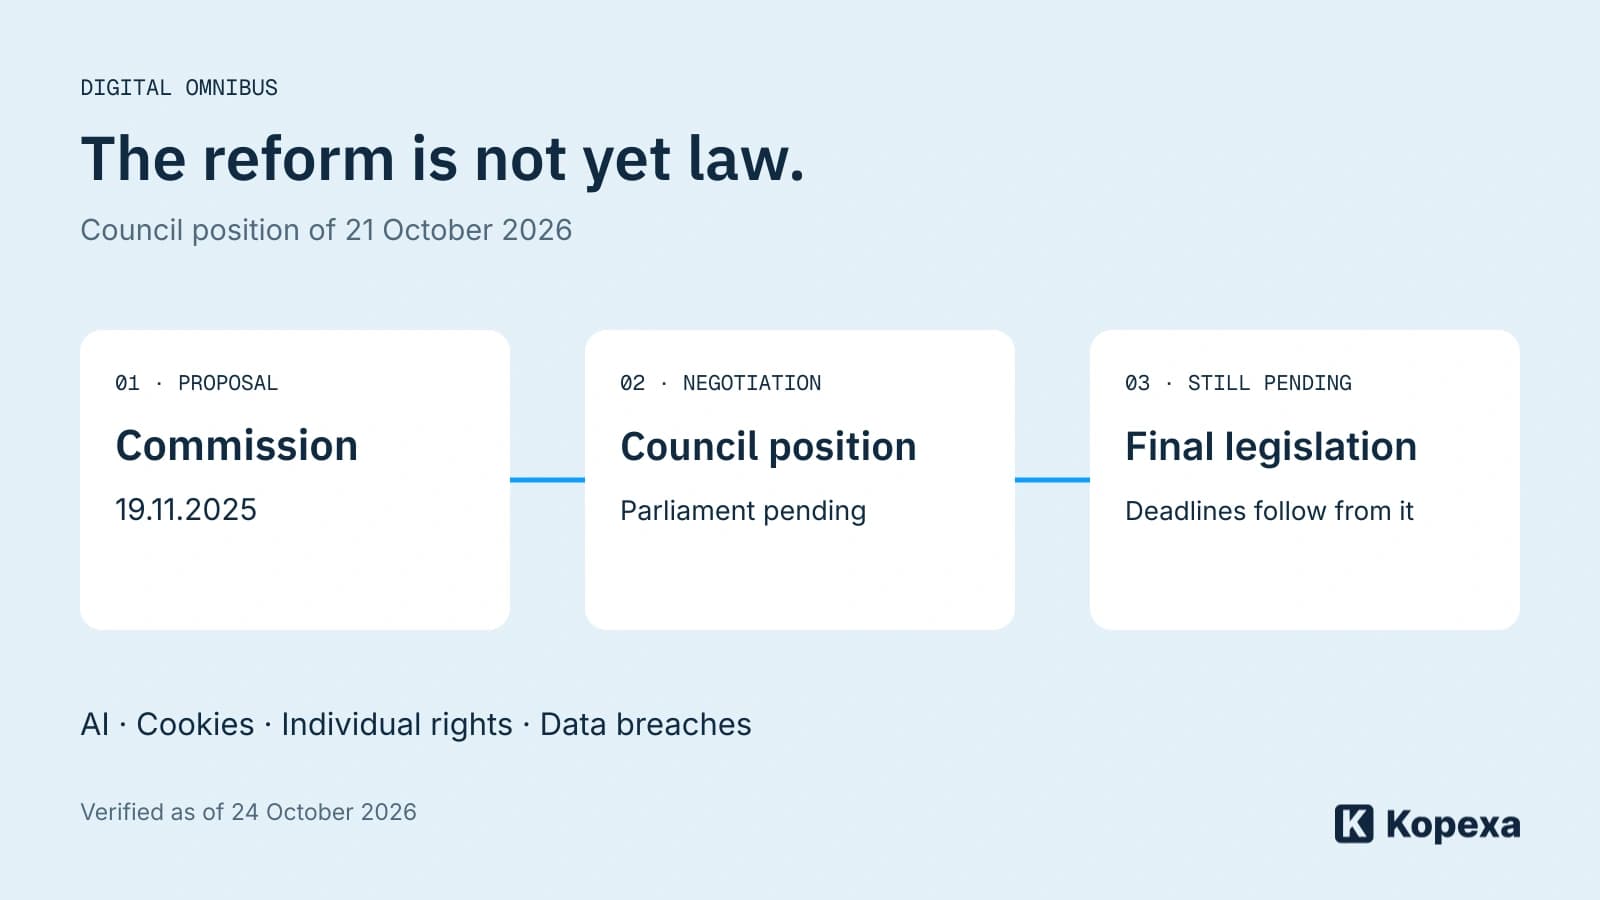
Digital Omnibus: What the GDPR reform would change for AI, cookies and businesses
What the EU Council proposes for AI training, cookies and data breaches: the GDPR reform explained, its current status and implications for businesses.
Julian Köhn·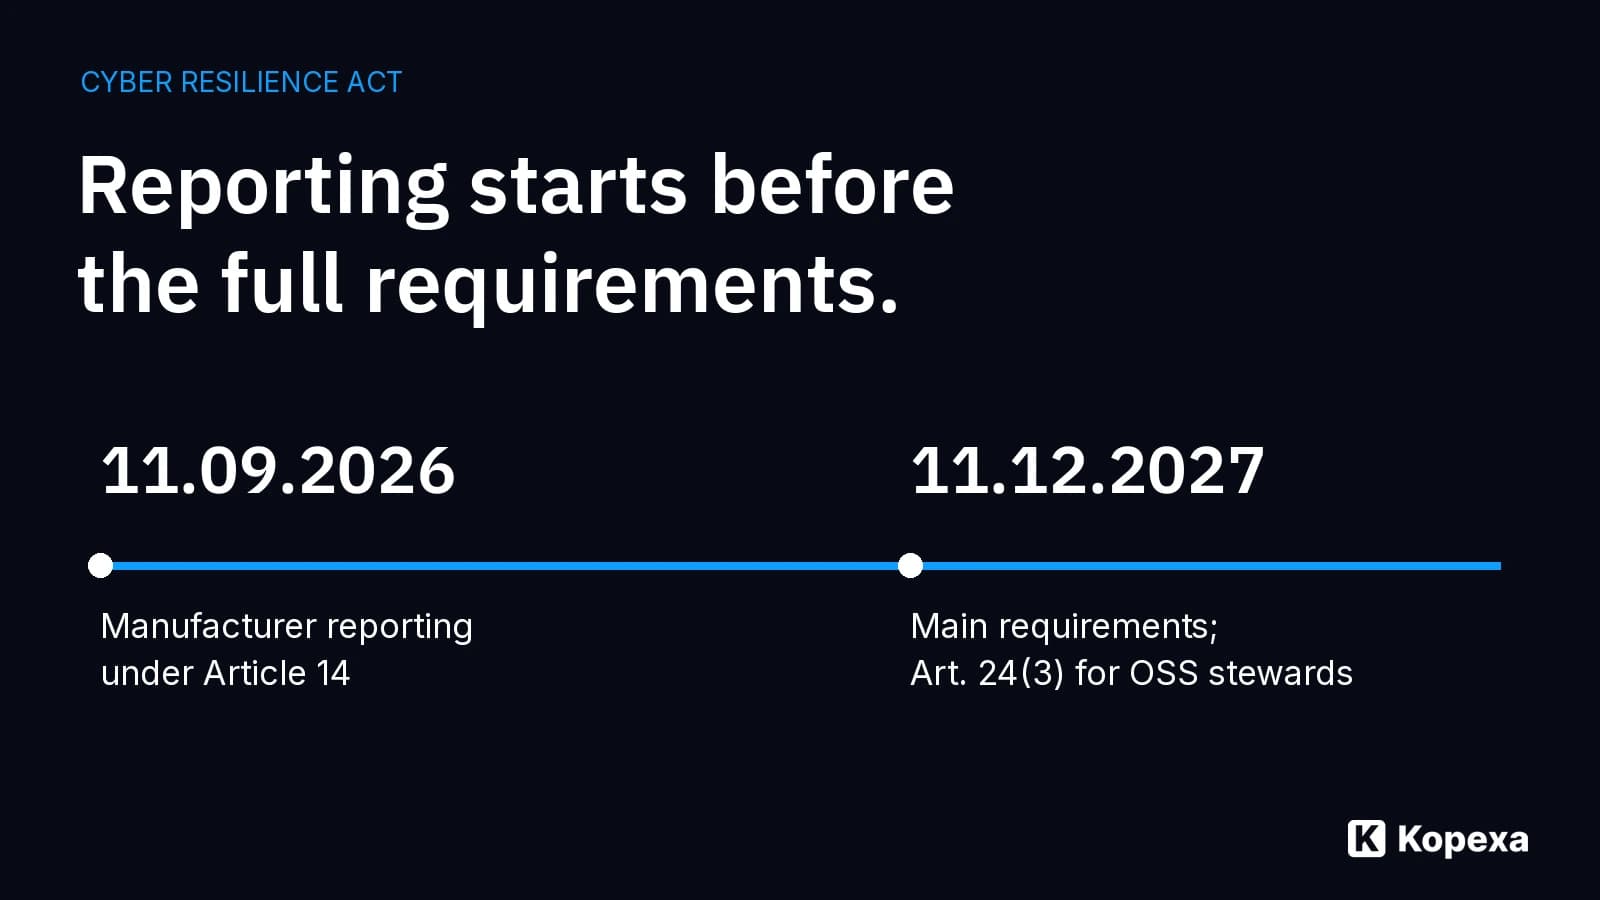
CRA reporting obligations: Why manufacturers cannot wait until 2027
CRA reporting duties have applied since 11 September 2026. Understand the reporting stages, affected manufacturers and the decisions needed before using the SRP.
Julian Köhn·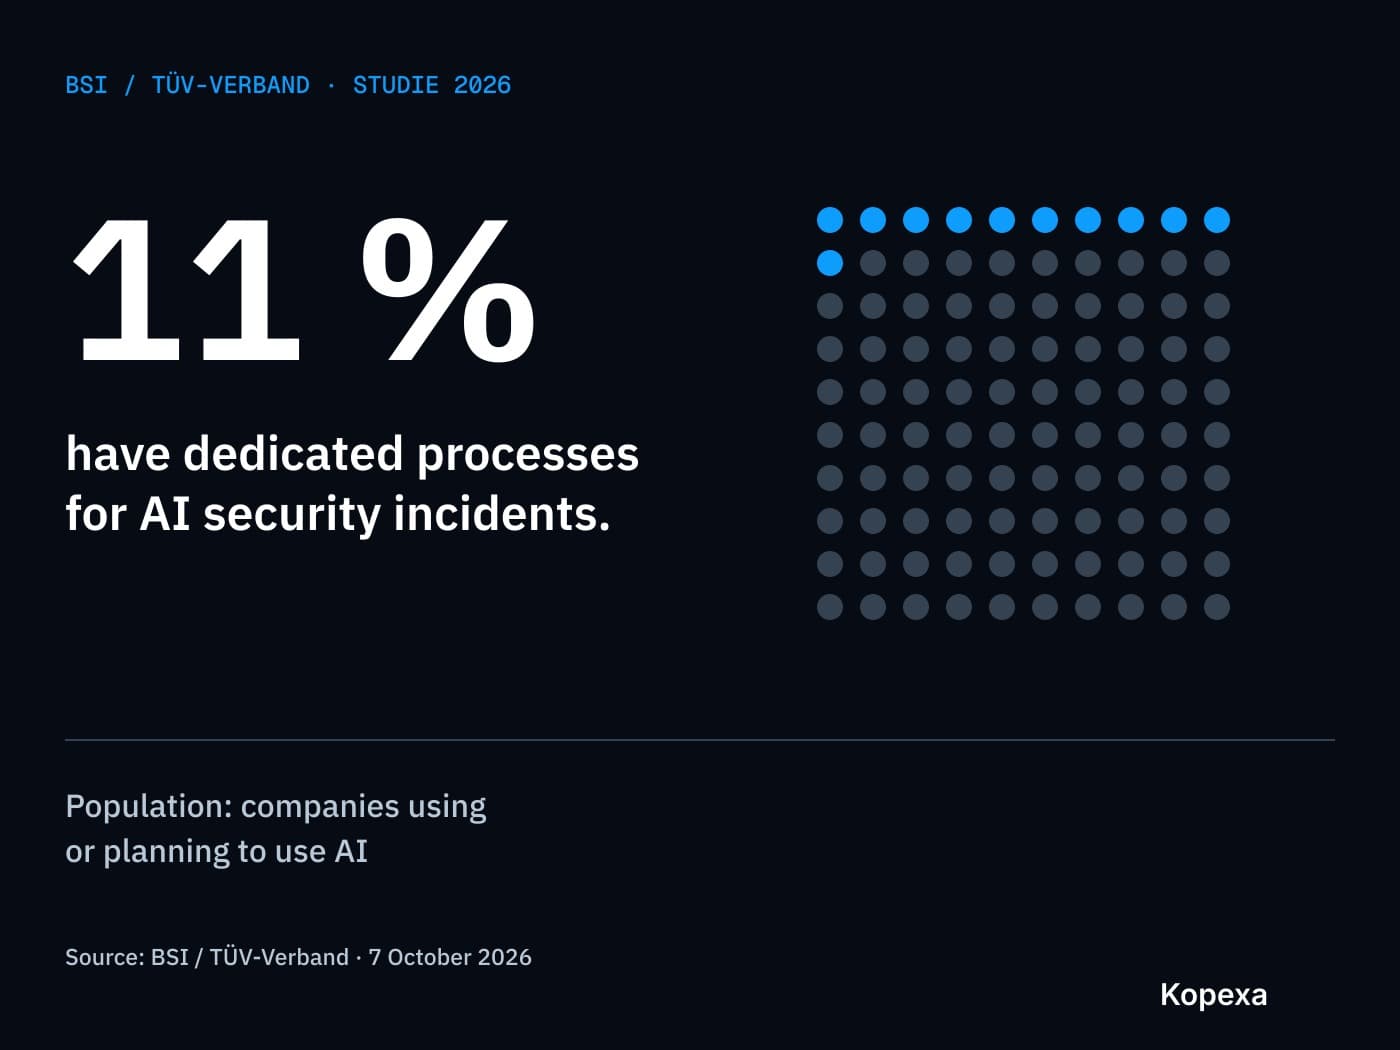
BSI/TÜV study: only 11% have dedicated AI incident processes
The 2026 AI security study identifies gaps in organisational preparation. What the 11% figure means and who was surveyed.
Julian Köhn·
France Travail: CNIL closes order following security improvements
France Travail has demonstrated the required security improvements. CNIL closes its order: what changed and what the decision means.
Julian Köhn·
AI Dependency as a Compliance Risk: What the Anthropic Case Teaches Every CTO
A US decree cut off access to leading AI models overnight. Why AI dependency is a real compliance risk that belongs in NIS2, ISO 27001 and DORA.
 Nikolai Shulgin·
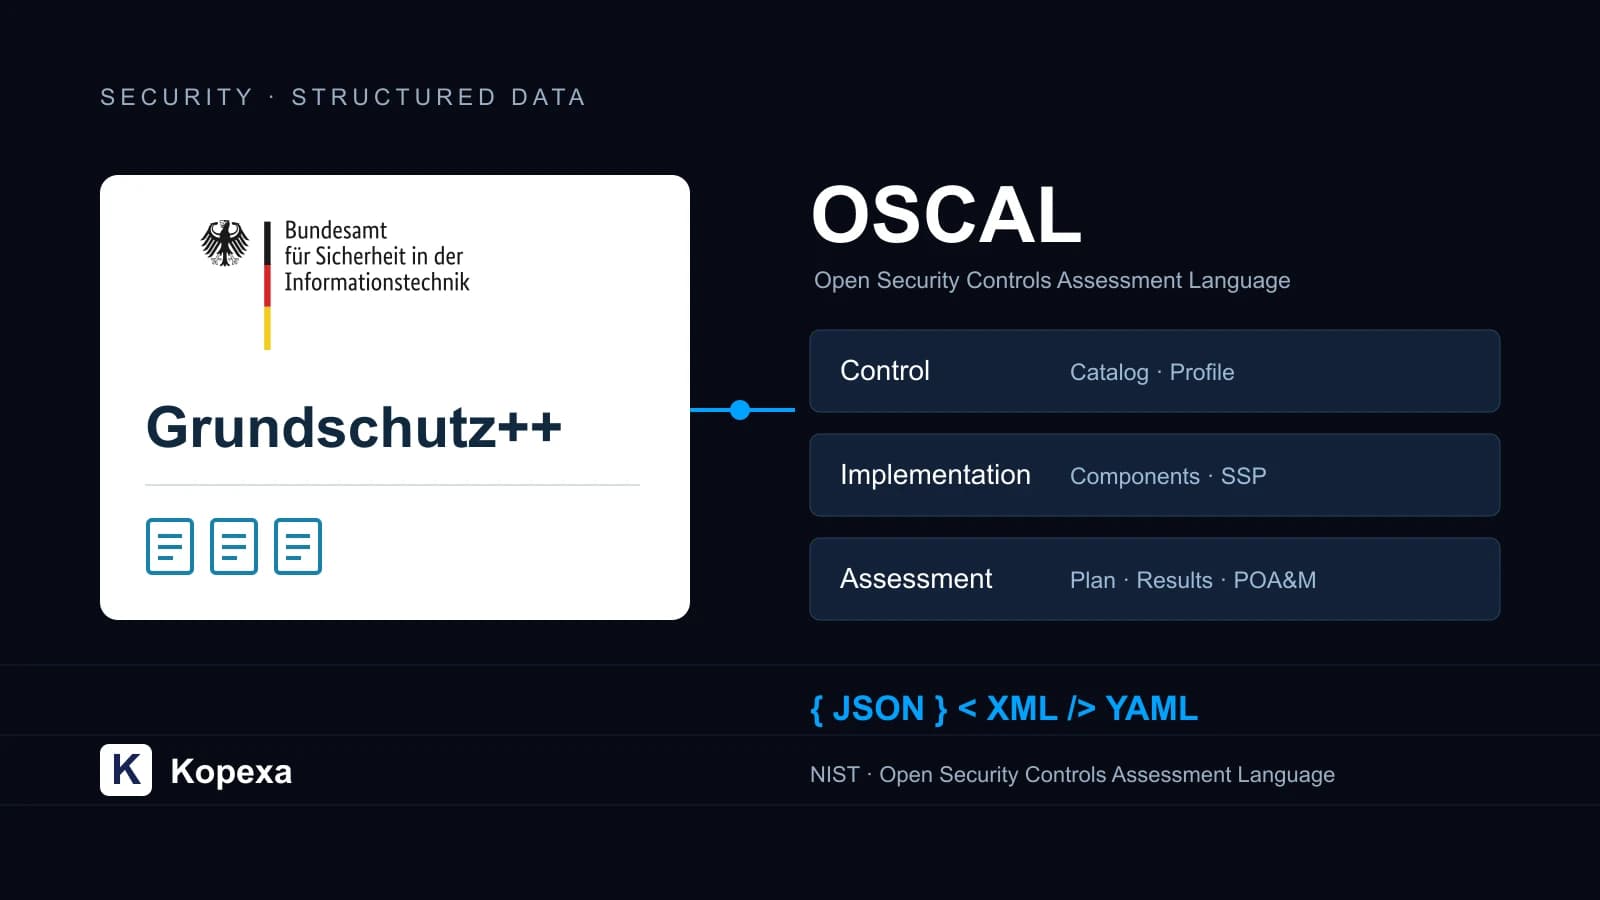
What Is OSCAL? A Deep Dive Into Compliance as Code and BSI Grundschutz++
What is OSCAL? Understand the data standard, its three layers and its relationship to BSI Grundschutz++, evidence and Compliance as Code.
Julian Köhn·
Third-Party Risk: Make Your Suppliers Audit-Ready
A practical guide to vendor risk management under NIS2, DORA and ISO 27001. With concrete checklists and documentation templates for your compliance team.