Understand security. Make better decisions.
News, analysis and practical knowledge on information security, privacy and compliance.
News in focusPrivacy & Engineering
VMware ESX: CVSS 2.7, yet known exploitation
CVE-2026-41709 concerns insufficient VMware ESX logging. Why its new KEV listing matters to patch and risk owners despite the low CVSS score.
3 min read
Put knowledge to work
Practical guides
Software for NIS2 implementation: Coordinate measures across departments
Choose NIS2 software: separate scope assessment, measures, incidents and management decisions. Includes a practical supplier test case.
 Julian Köhn·
ISO 27001 software for IT providers: Answer customer questions faster
Assess ISO 27001 software for IT providers: keep customer engagements, privileged access and shared evidence clearly scoped.
Julian Köhn·
ISO 27001 software: Prepare for certification and close open gaps
Choose ISO 27001 software by testing scope, risk treatment, SoA and dependable evidence during a pilot, beyond comparing document templates.
Julian Köhn·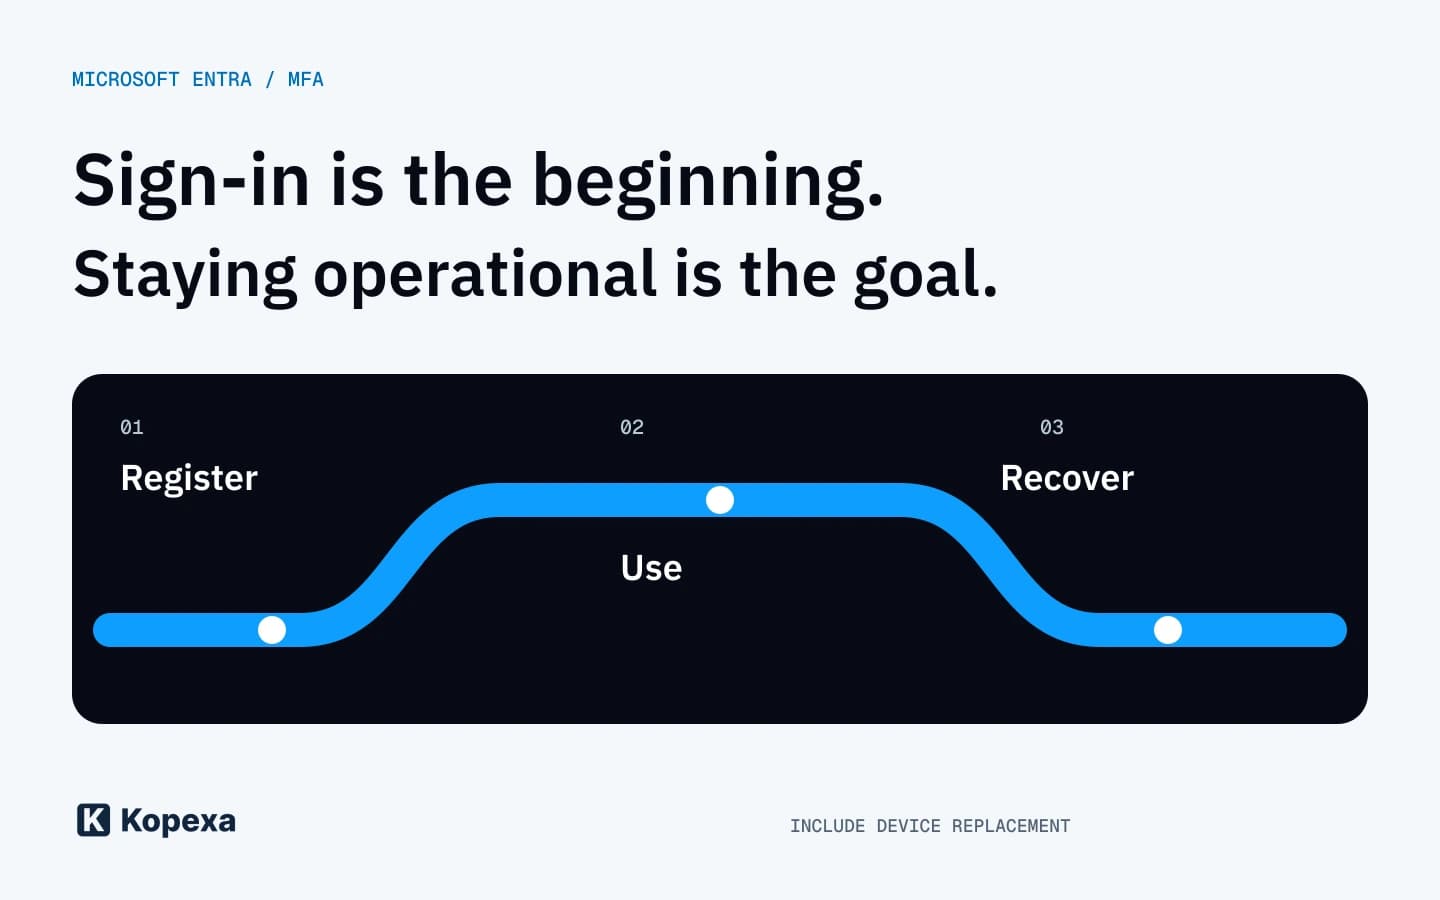
Microsoft Entra: Prepare passkeys before SMS MFA retires
Microsoft is retiring its own SMS and voice delivery for Entra MFA. Understand the affected user groups and prepare migration, recovery and operational acceptance.
Julian Köhn·
Risk management software for financial services: Coordinate ICT risks
Distinguish ICT risk management from credit, market and liquidity risks. Includes a provider-dependency and risk-approval test case.
Julian Köhn·
Choosing risk management software: From assessment to decision
Choose risk management software using a decision case: test assessment methods, measure effectiveness, history and risk acceptance.
Julian Köhn·Perspectives from practice
Opinion & analysis
Build on solid foundations
What Is an ISMS? Definition, Examples and Implementation Guide
What an ISMS is, which documents you need and how to build it: a clear definition, three examples and a practical implementation plan.
Updated 10 min read
What Is OSCAL? A Deep Dive Into Compliance as Code and BSI Grundschutz++
What is OSCAL? Understand the data standard, its three layers and its relationship to BSI Grundschutz++, evidence and Compliance as Code.
Updated 10 min read
ISO 27001 and Data Protection: GDPR, TOMs and Evidence
Does ISO 27001 cover GDPR? Understand Article 32 TOMs and follow eight practical steps, with evidence, ownership and a worked example.
Updated 8 min read
The article series
Evidence that holds up in practice
Go deeper, step by step. All published parts, in the right order.
The article series
Moving your ISMS
Go deeper, step by step. All published parts, in the right order.
Still looking for the right answer?
117 articles on information security, compliance and privacy.