These organisations work with Kopexa






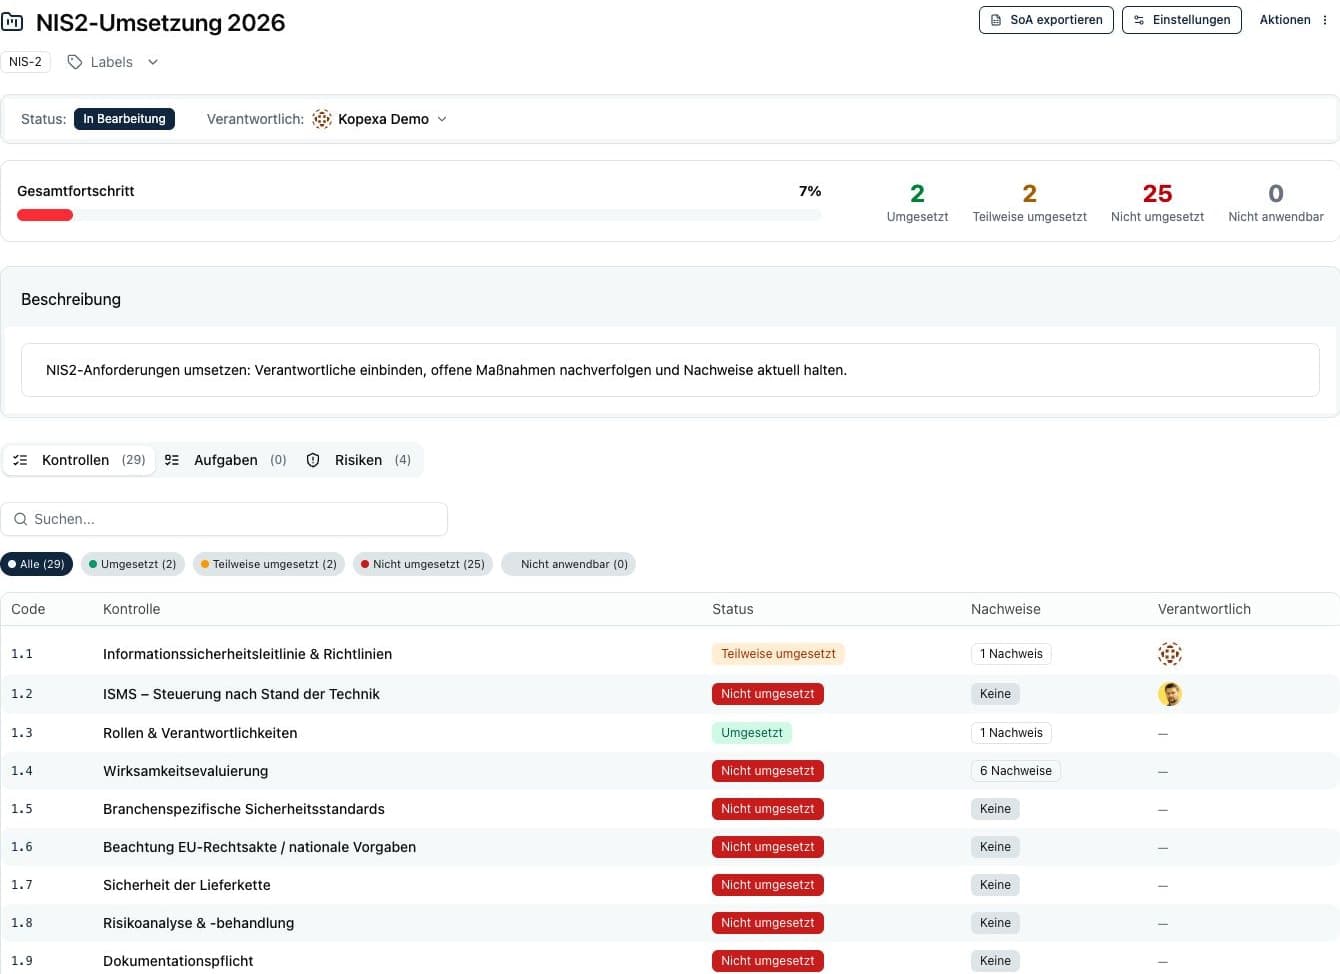
From requirements to implementation
Go beyond knowing what to do. Keep implementation connected.
- 01
Open items have a next step.
Use Kopexa’s dedicated NIS2 framework, assign owners and connect implementation to tasks. IT and business teams work from the same status instead of reconciling separate spreadsheets.
Explore tasks and actions - 02
Evidence stays with the question it answers.
Link policies and evidence to requirements. Document versions and currency reviews help you explain to management or assessors what has been implemented and what needs further work.
Explore policies and evidence - 03
Supplier assessments lead to practical follow-up.
Send questionnaires and reminders automatically. Answers can feed into risk ratings according to your configurable rules. Follow up on open reviews and tasks directly at the supplier.
Explore supplier management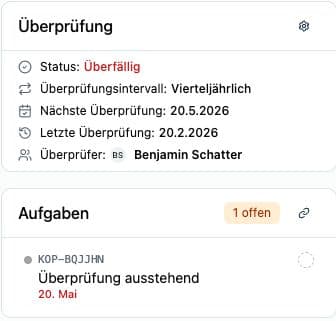
Already running an ISMS?
Add NIS2. Reuse the work you have done.
An existing ISMS provides a useful starting point. Bring your risks, policies and evidence into Kopexa and link them to requirements. The dedicated NIS2 framework helps you see your current status and additional work. Manage implementation alongside ISO 27001 and other programmes.
Explore ISO 27001 mapping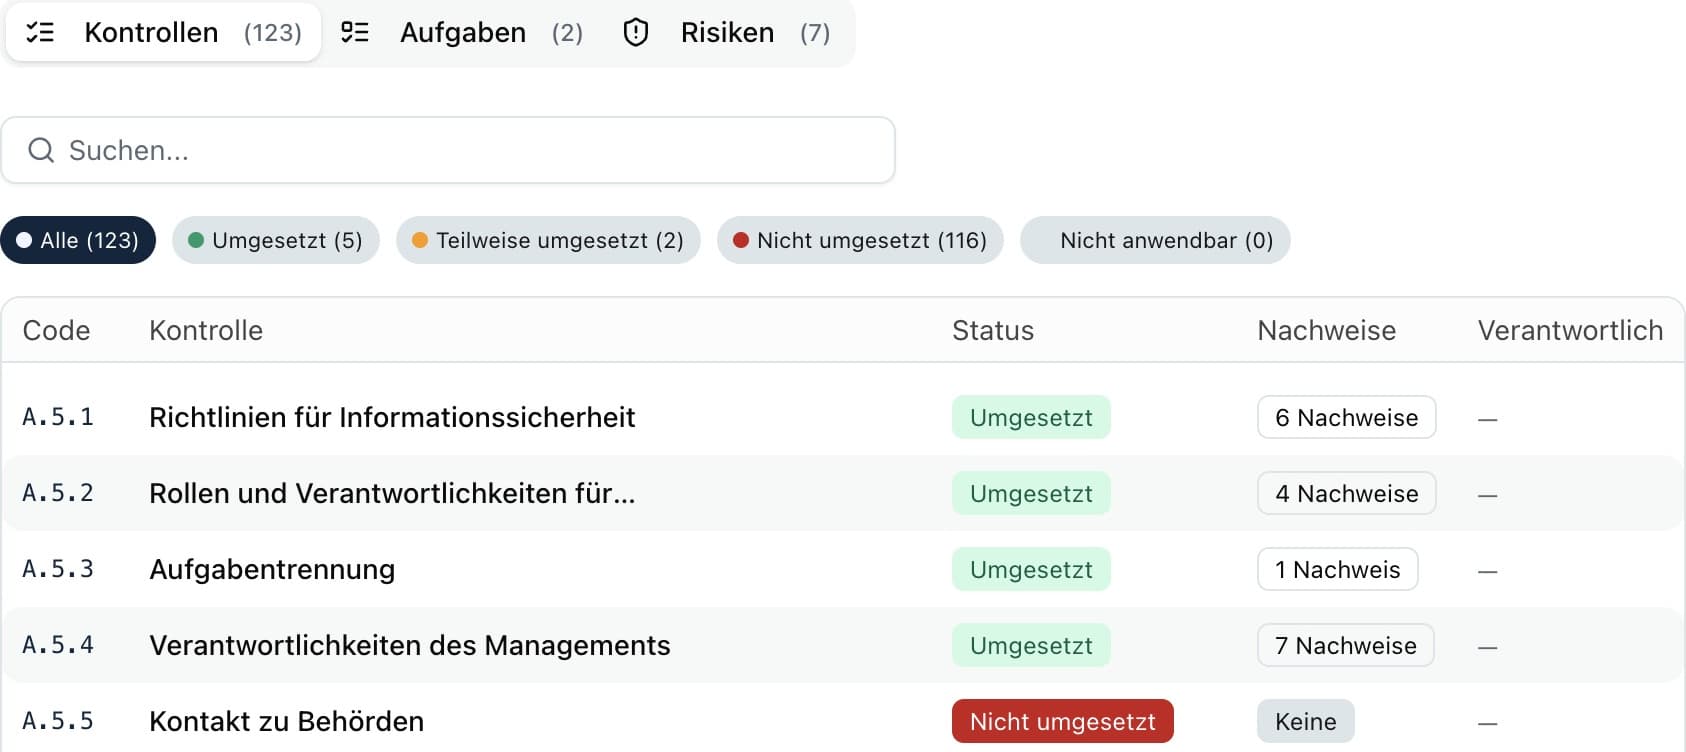
Customer experience · ISO 27001
„I often didn't know where to put the evidence. Now it's: bring it on, I find the right place instantly!“
Experience from ISMS work at CSN Solutions.
Applicability in Germany
What is NIS2 — and does it apply to your company?
NIS2 is EU cybersecurity Directive 2022/2555. German implementation has applied since 6 December 2025. The BSIG defines which entities are in scope and their risk management, registration and reporting obligations.
Essential entities
For entity types in Annex 1, generally at least 250 employees or annual turnover above EUR 50 million together with an annual balance sheet total above EUR 43 million. Specific entity types and size-independent cases also exist.
Important entities
For entity types in Annex 1 or 2, generally at least 50 employees or annual turnover and an annual balance sheet total each above EUR 10 million. Special rules and company relationships also need consideration.
Supplying a regulated customer can bring additional security requirements. This alone does not automatically make your company a regulated entity under the BSIG.
Check applicability under § 28 BSIGStill checking whether NIS2 applies?
Use our sector calculator for initial orientation. Then establish the criteria relevant to your company before defining the implementation scope.
Requirements and obligations
NIS2 compliance goes beyond a list of measures.
Implementation in Germany brings together appropriate security measures, documented decisions and statutory procedures. Kopexa helps you coordinate that work and make progress traceable.
Risk and effectiveness
Assess risks, choose appropriate measures and evaluate their effectiveness.
Operations and supply chain
Include backups, recovery and the security of direct suppliers in implementation.
Registration and reporting
Treat applicability, registration and reporting significant incidents as distinct tasks.
Management and training
Oversee implementation, clarify responsibilities and plan training.
NIS2 knowledge and practical resources
Find the answer to your next question.
Explore requirements, implementation, costs or reporting obligations, according to your next step.
Plan
Obligations
Frequently asked questions about NIS2
When did German NIS2 implementation take effect and what are the deadlines?
German implementation has applied since 6 December 2025. In-scope entities need to address risk management, registration, reporting and management obligations. The applicable BSIG rules and the specific entity determine the requirements. Our NIS2 roadmap and registration guide support further planning.
What are the reporting deadlines for security incidents?
For significant incidents, § 32 BSIG generally requires an early warning within 24 hours and an incident notification within 72 hours of becoming aware. The final report is generally due no later than one month after the incident notification. Additional reporting rules apply to ongoing incidents. Our reporting guide explains the process.
Which companies are affected by NIS2?
Applicability depends on entity type, size criteria and special rules under § 28 BSIG. The general threshold for important entities in relevant categories is at least 50 employees or annual turnover and an annual balance sheet total each above EUR 10 million. Company relationships also matter. Customer requirements imposed on suppliers are a separate consideration.
What are the main requirements of NIS2?
§ 30 BSIG covers risk analysis, incident handling, operational continuity, supply chain security and evaluating the effectiveness of measures, among other requirements such as training, access and cryptography. Registration, reporting and management obligations are regulated separately. Our requirements page explains these areas.
What penalties apply for NIS2 violations?
The fines are governed by § 65 BSIG. The applicable maximum depends on the entity, the violation and, where relevant, turnover. Management obligations and liability are separate considerations. Our sanctions guide explains the distinctions.
Do I need ISO 27001 to be NIS2-compliant?
An existing ISO 27001 ISMS provides a useful basis for implementing NIS2. Kopexa offers a dedicated NIS2 framework: work through requirements, reuse existing risks and evidence, and address outstanding items. Mapping helps connect requirements. A blanket coverage percentage cannot reliably describe your organisation’s implementation.
How does software help with NIS2 compliance?
Kopexa connects requirements to risks, policies, tasks and evidence. Involve owners, follow up on open work and explain implementation status. Supplier assessments and recurring reviews belong to the same workflow. Evaluate the product in a demo based on your starting point.
What does NIS2 compliance cost?
Budget separately for internal time, necessary security measures and any software or external support. Scope and effort depend on your organisation and existing practices. Kopexa’s pricing page shows current plans; our NIS2 cost guide supports budgeting. Generic project durations or savings are not a reliable basis.
Your personal Kopexa demo
Show us where your NIS2 work gets stuck today.
Bring an open requirement, a supplier process or your existing ISMS. See the workflow in the product: from ownership and tasks to the supporting evidence.
Personal and tailored to your starting point. Request your demo on the next page.
View pricing and plans