Ahold Delhaize begins controlled restart after cyber incident
Ahold Delhaize is restarting certain systems after a cyber incident while stores remain open. What the retailer has confirmed.
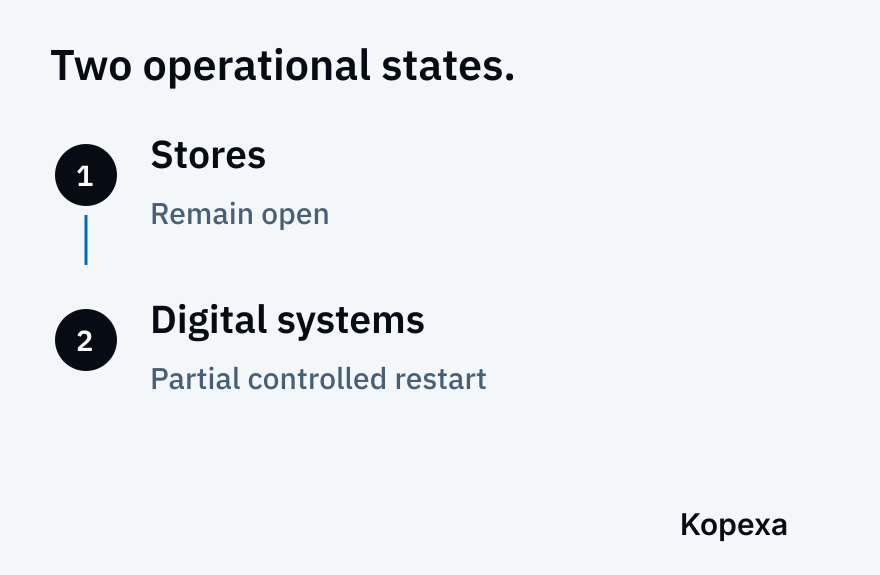
Stores remain open while parts of IT are offline: Ahold Delhaize has begun a controlled restart of certain systems following a cybersecurity incident. The retailer announced this on 13 October 2026.
What the company has confirmed
On 12 October, Ahold Delhaize reported a security issue within its network. Some systems were taken offline as a precaution. Its 13 October update describes disruption for customers, associates and partners, with impacts varying by brand.
Stores in Europe and the United States remained open. Internal teams and external cybersecurity specialists were investigating and working towards safe restoration.
A restart is not a complete all-clear
The announcement describes a controlled relaunch of certain systems, rather than full recovery of every affected service. At that stage of the investigation, the company reported no evidence that customer or associate data had been taken. This is a time-bound statement during an ongoing investigation.
These announcements do not identify a ransomware family or attribute the incident to a particular attacker.
Our view: availability has several layers
An organisation is rarely entirely online or entirely offline. Sales, ordering, communications and administration can be affected differently. Incident communication therefore needs care: a statement about stores does not answer every question about connected processes.
The case also differs from a simple success announcement about restarted servers. For business partners, the relevant issue is which specific service is reliably available again and which limitations remain.
Our article on the Fehmarnbelt incident and business continuity explores operating without central IT. The third-party risk guide explains how to assess external dependencies.
Cover: Albert Heijn store in Holten, archive 2009, Steven Lek / Tukka, Wikimedia Commons, public domain. Not a photograph of the current incident. Crop and design: Kopexa.

Sources
- Ahold Delhaize: Initial statement () [Accessed ]
- Ahold Delhaize: Update on cybersecurity incident () [Accessed ]