AhsayCBS: attackers target backup servers; hotfixes available
Attacks on AhsayCBS highlight the need to protect backup management itself. The vendor and Huntress report available hotfixes and compromise guidance.
The system managing recovery copies has itself become a target: attackers are chaining two vulnerabilities against AhsayCBS servers. Hotfixes are now available, superseding older reports that described an unpatched attack path.
What Huntress observed
Huntress reports exploitation from 7 October. Attackers bypass authentication and subsequently execute commands. Observed activity included webshells and XMRig miners masquerading as Microsoft Edge.
The vulnerabilities are CVE-2026-105133 and CVE-2026-105134. A familiar product name on a process is therefore not evidence of its origin.
Current patch status
The vendor’s 13 October update states that 10.3.4.45 and 9.15.2.70 address the vulnerabilities. Ahsay also describes the upgrade path for older major versions. In its 12 October update, Huntress independently confirms that 10.3.4.45 blocks the original entry point in the attack chain.
The full version matters: 10.3.4 is not the same as 10.3.4.45. Huntress corrected its original assessment of version 10.3.4.
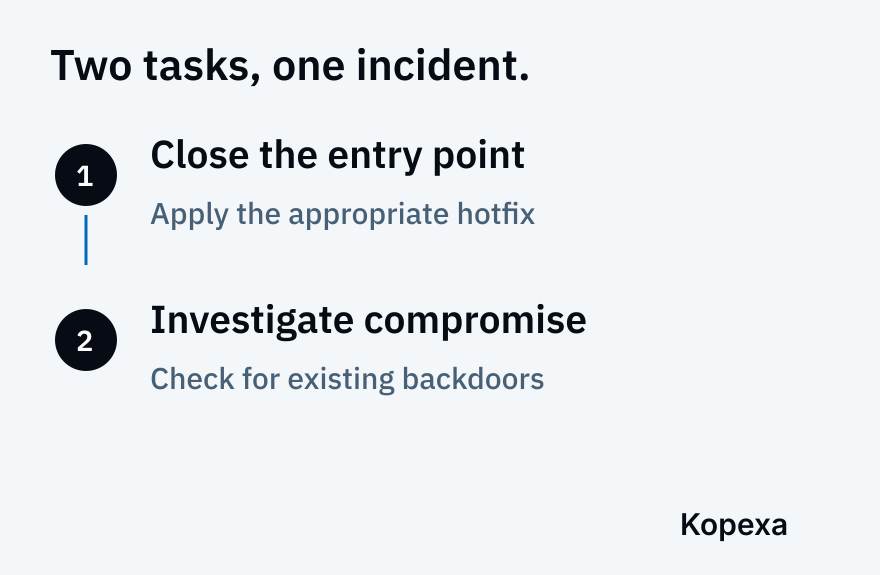
Updating does not remove an existing backdoor
Where compromise indicators exist, Ahsay recommends rebuilding the backup server using its recovery instructions. Unauthorised accounts and replication receivers are among the warning signs it lists. Detailed checks should follow the latest vendor guidance.
Our interpretation: backup data, backup administration and recoverability are separate security concerns. Having a copy does not prove that the console managing it is adequately protected.
For outsourced services, this makes responsibilities, administrative access and responses to vendor warnings particularly relevant. Our third-party risk guide explains that connection.
Cover: AI-generated illustrative photograph of an ordinary server room, not a specific Ahsay deployment or affected organisation. Design: Kopexa.
Sources
- Huntress: AhsayCBS exploitation research and updated mitigation () [Accessed ]
- Ahsay: Vulnerability Status Update, 13 October () [Accessed ]