Explore the Kopexa blog
Compliance & Regulation
What new rules mean for your organisation, and how to turn requirements into practical next steps.
11–18 of 18
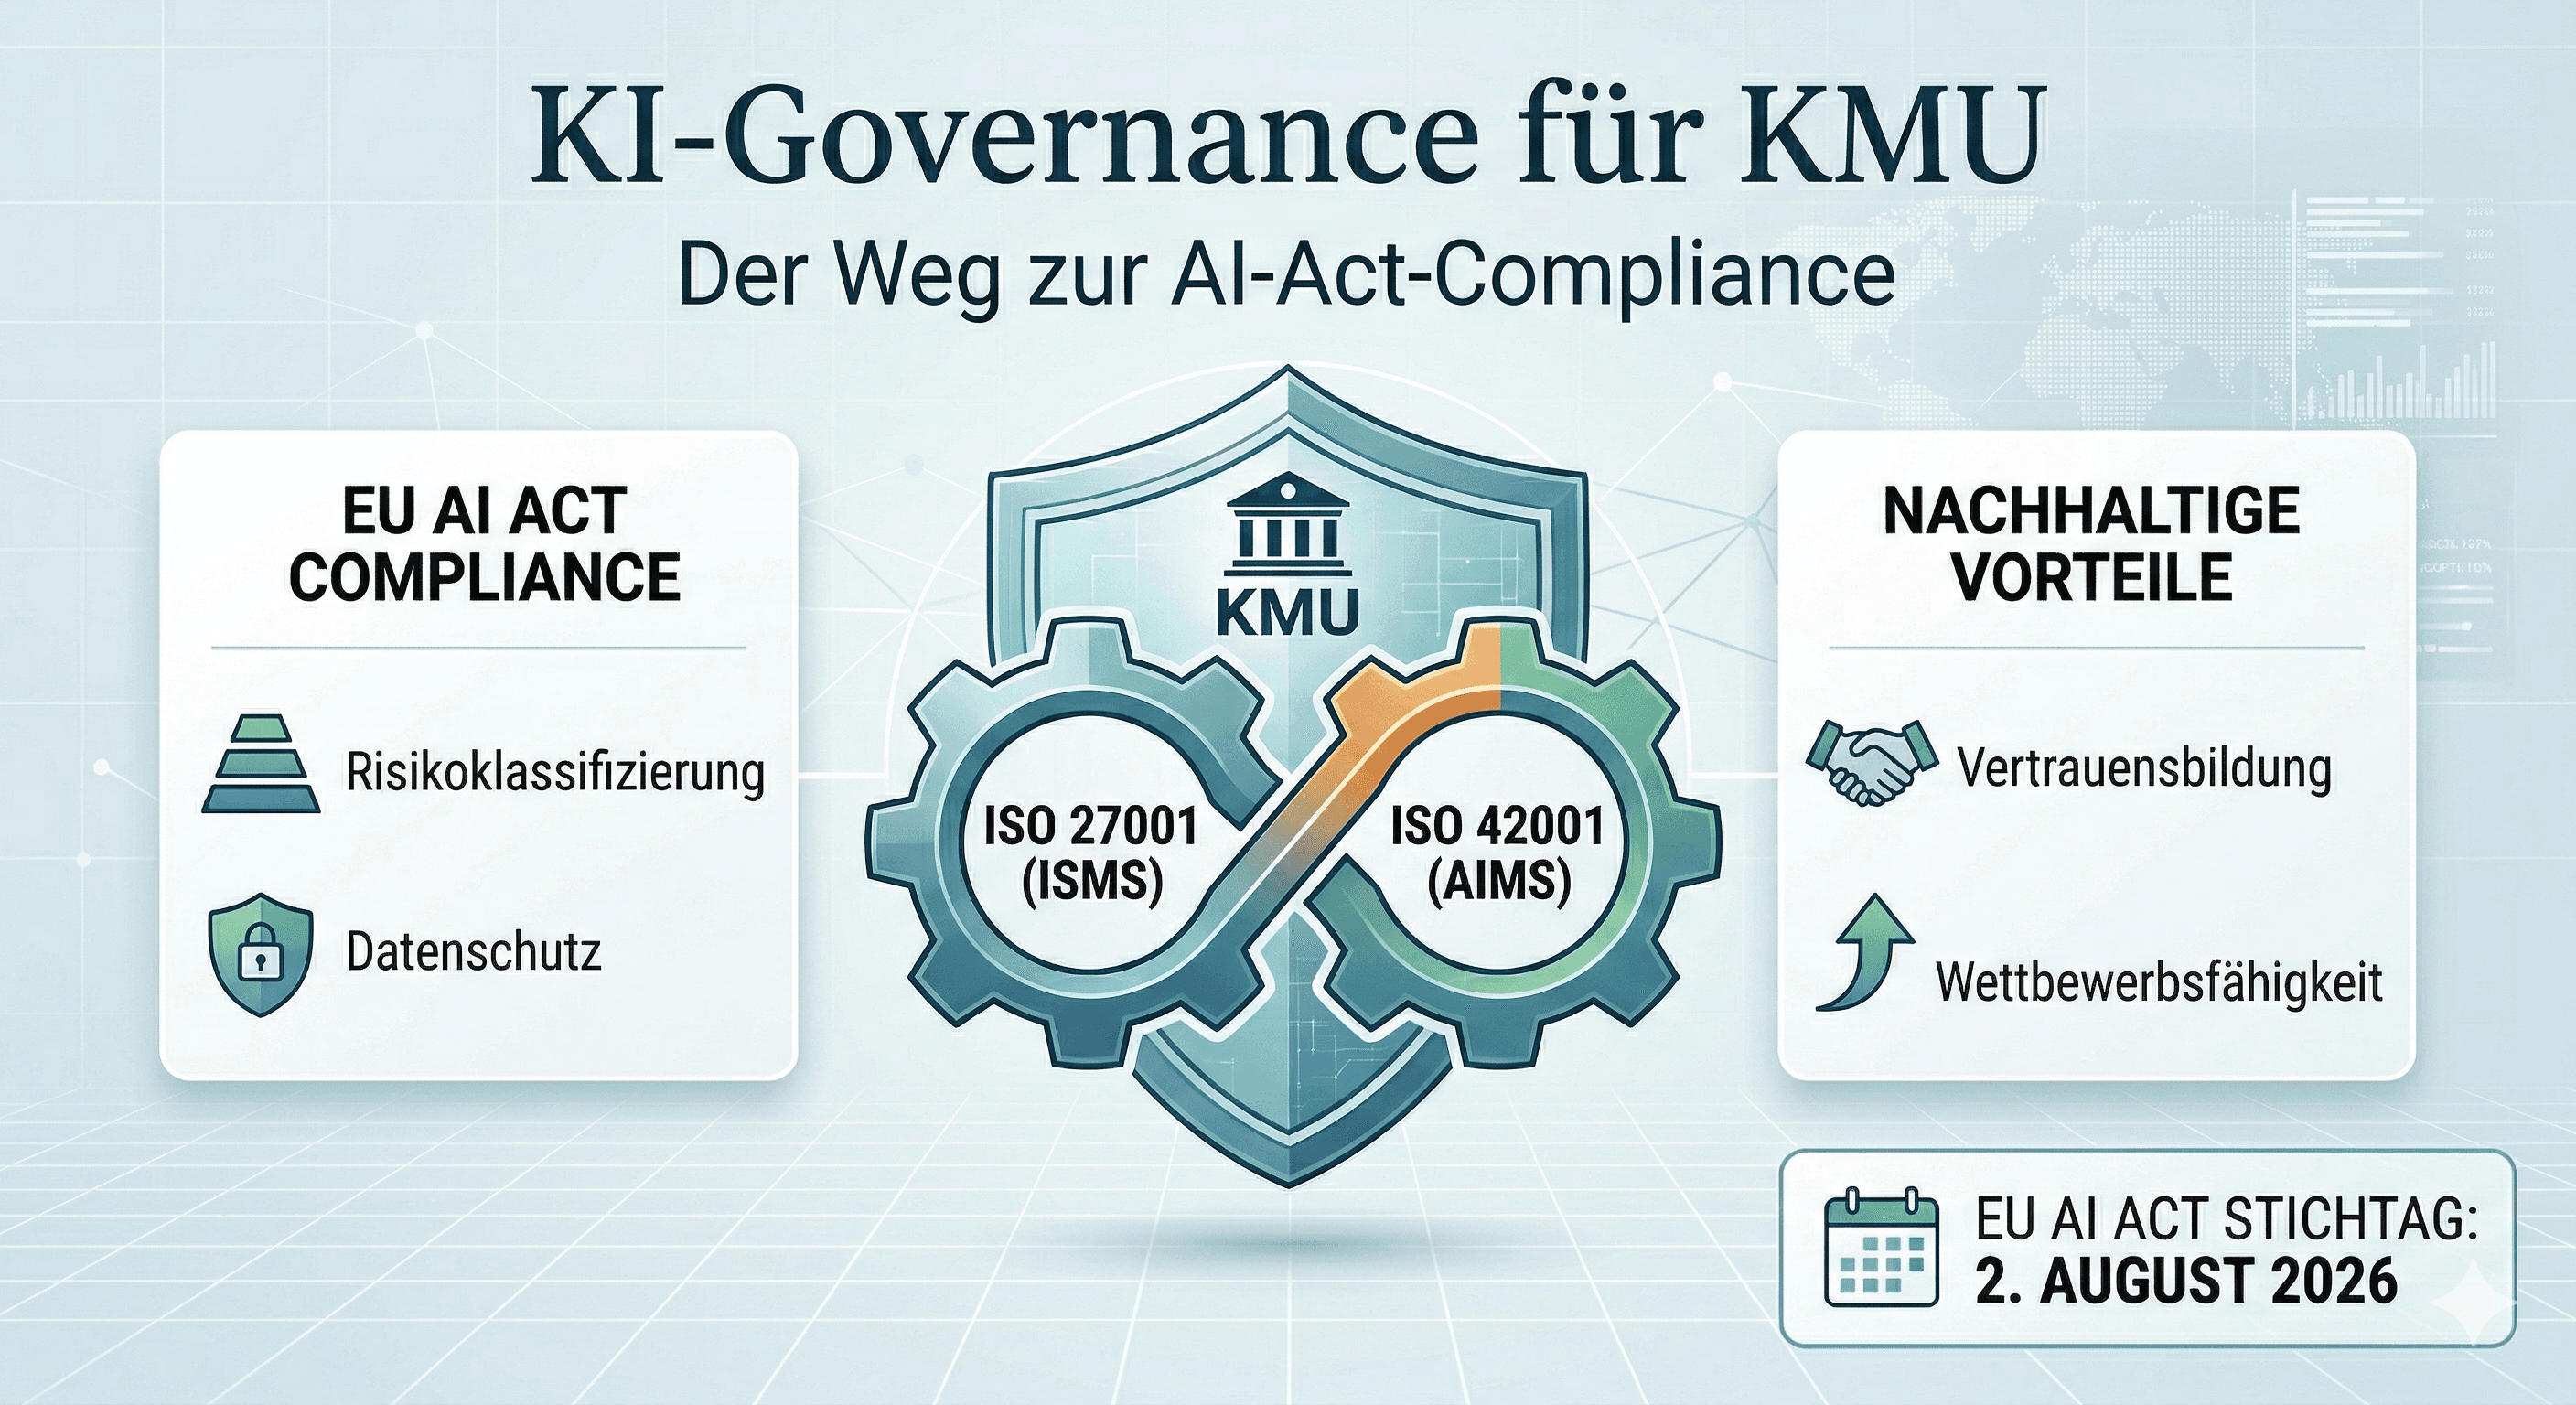
AI Governance for SMEs: The Path to AI Act Compliance
The EU AI Act will come into force in August 2026. Learn how, as an SME, you can systematically identify AI risks, integrate them into ISO 27001 and ISO 42001, and remain compliant.
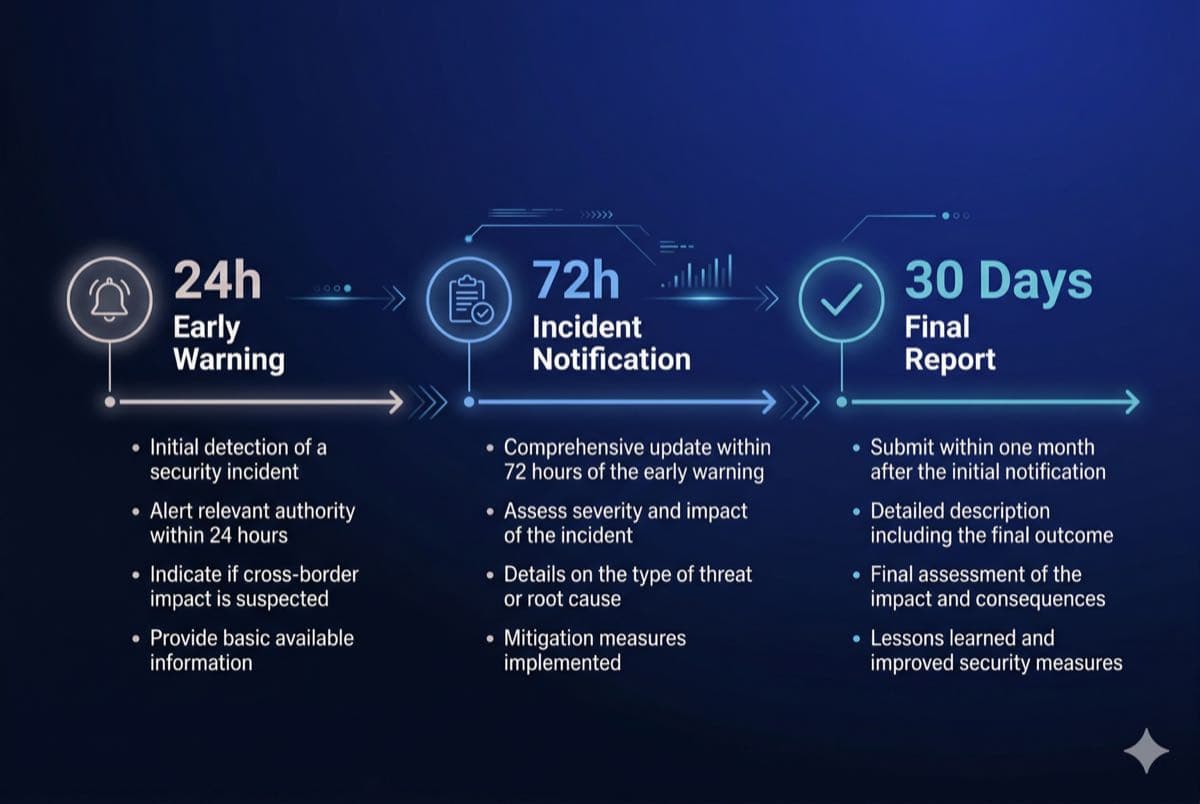
NIS2 reporting: 24 hours, 72 hours and the final report
Report NIS2 incidents in Germany: assess significance, meet section 32 BSIG deadlines and prepare a reliable incident response process.
NIS2 requirements: Ten areas and your next steps in Germany
Understand Germany's NIS2 requirements: ten areas under section 30 BSIG, registration, incident reporting and management responsibilities.
 Julian Köhn·
NIS2 fines: Penalties and management liability under Germany's BSIG
Understand German NIS2 fines: the EUR 10m and 7m limits, turnover thresholds, registration penalties, management liability and supervisory powers.
Julian Köhn·
NIS2 Executive Management: Training Obligation & Liability 2025
Mandatory training under NIS2: who is affected? What liability do directors face? All content, obligations & risks explained simply. Get informed now.
Julian Köhn·
NIS2: The Underestimated Obligation for SMEs and Suppliers
NIS 2 obliges SMEs and suppliers to meet higher cybersecurity standards, reporting channels and ISMS integration for greater digital resilience.
Julian Köhn·
NIS-2, GDPR & ISO 27001: Strategic Compliance Integration
European companies face NIS-2, GDPR & ISO 27001. Learn how integrated compliance strategies reduce costs and build trust.
ESG Compliance: How to Master the New Reporting Obligations
The CSRD is coming: learn how to use ESG compliance as a strategic advantage and turn it into a game-changer with Kopexa!
Julian Köhn·