1–9 of 54 articles
By publication date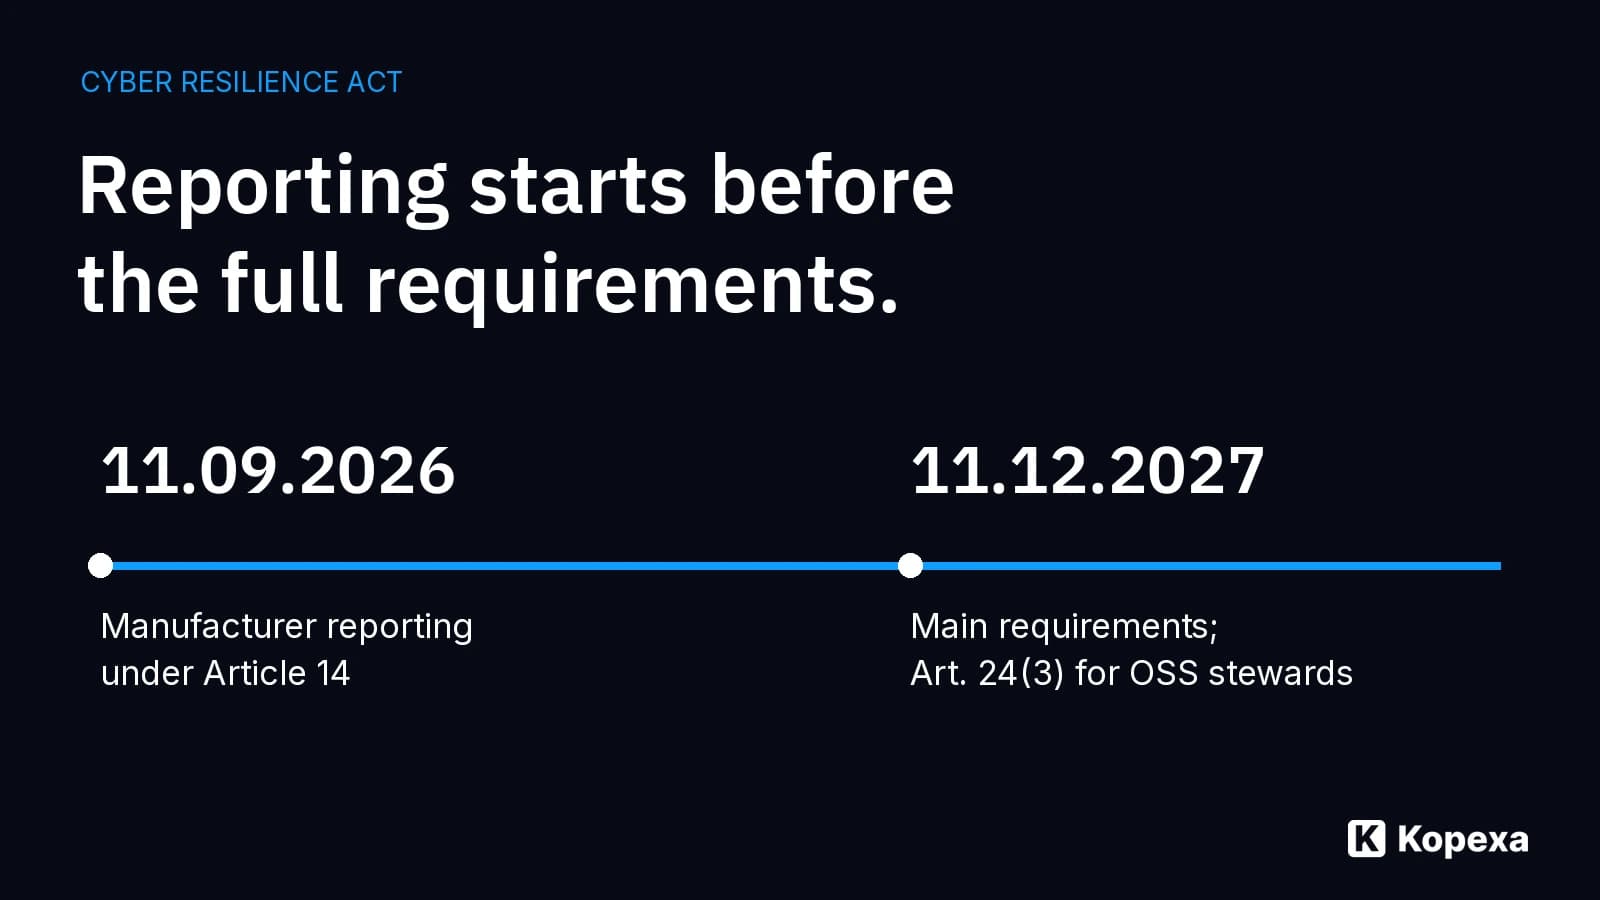
CRA reporting obligations: Why manufacturers cannot wait until 2027
CRA reporting duties have applied since 11 September 2026. Understand the reporting stages, affected manufacturers and the decisions needed before using the SRP.
 Julian Köhn·
Data protection and business value: What the new regulators' study shows
CNIL, ICO and CNPD explore the economic role of data protection. What their study means for data governance, due diligence and cyber risk, without promises of returns.
Julian Köhn·
Xandr fine: consent is not an assumption
A NOK 92 million fine over the processing of Grindr users’ data: what the Xandr decision shows about consent and accountability across advertising chains.
Julian Köhn·
Dealership data breach: supplier assurance needs more than a certificate
The GeNesys breach highlights digital supply-chain risk. How to check TISAX scope, current evidence and operational information security.
Julian Köhn·
Ahold Delhaize begins controlled restart after cyber incident
Ahold Delhaize is restarting certain systems after a cyber incident while stores remain open. What the retailer has confirmed.
Julian Köhn·
AhsayCBS: attackers target backup servers; hotfixes available
Attacks on AhsayCBS highlight the need to protect backup management itself. The vendor and Huntress report available hotfixes and compromise guidance.
Julian Köhn·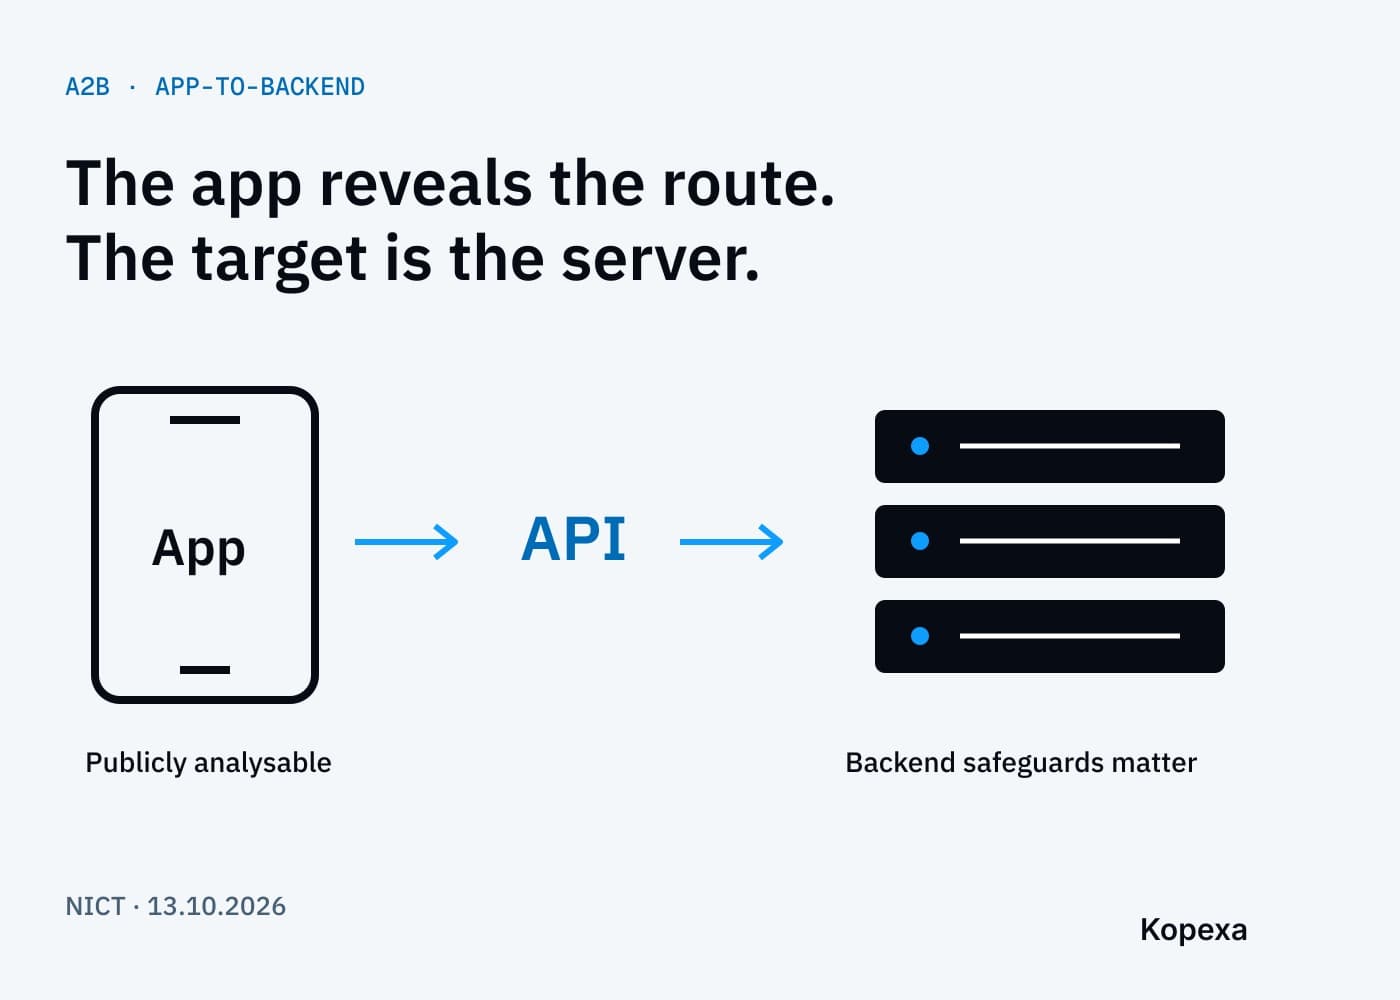
NICT warns of A2B attacks: an app can reveal the route to its server
A new NICT warning describes backend attacks informed by public Android apps. The risk is not confined to the app itself.
Julian Köhn·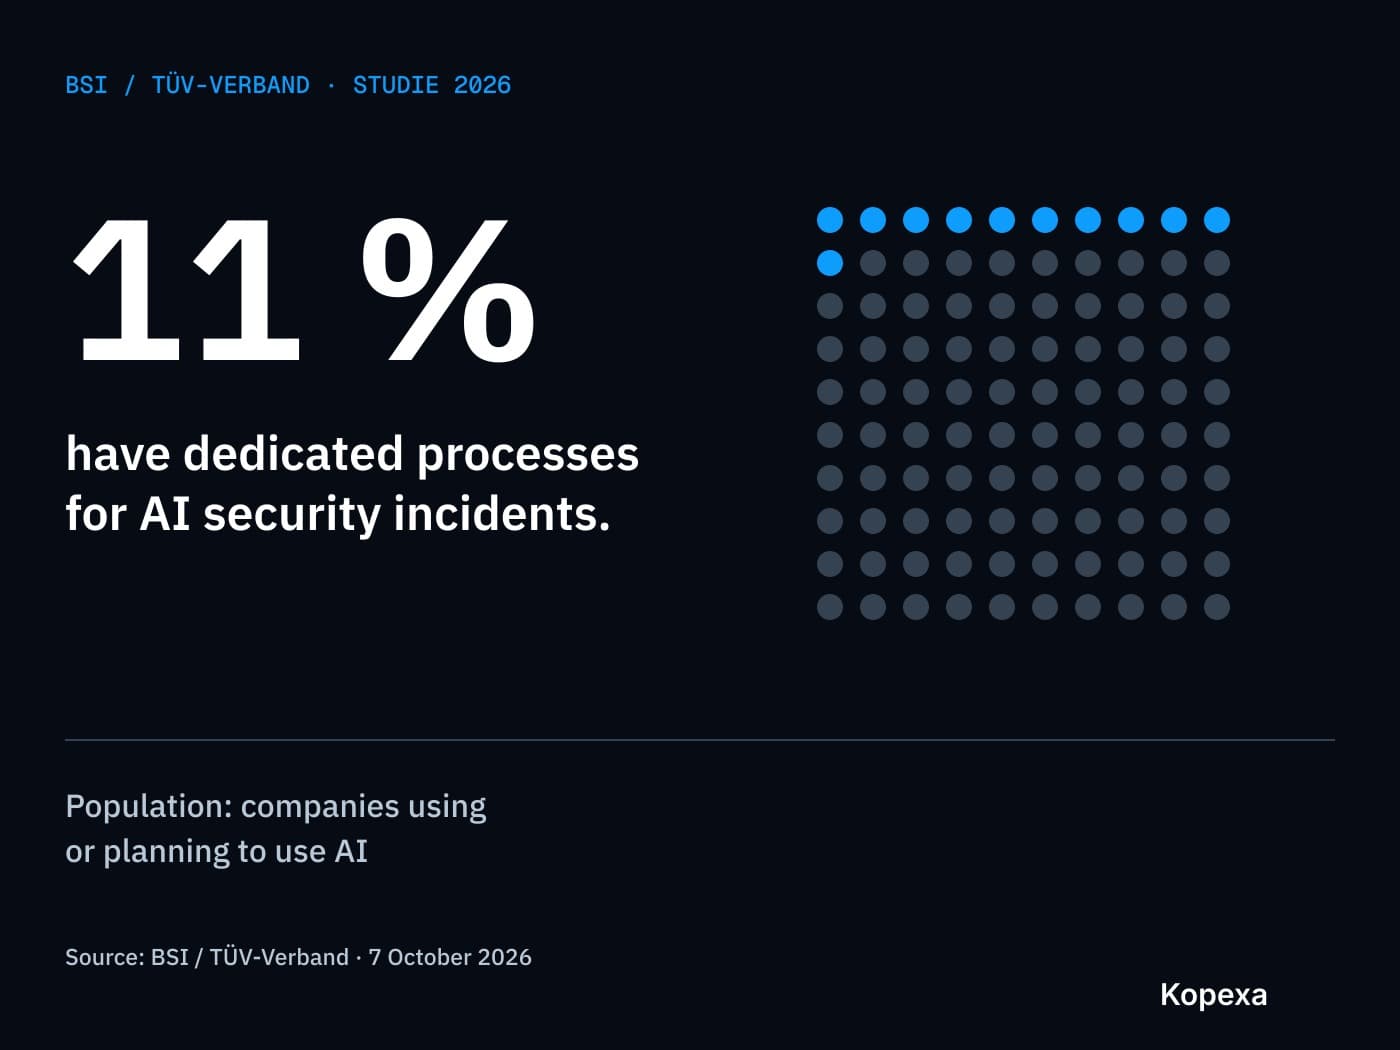
BSI/TÜV study: only 11% have dedicated AI incident processes
The 2026 AI security study identifies gaps in organisational preparation. What the 11% figure means and who was surveyed.
Julian Köhn·
October Patch Tuesday: exploited Windows Shell flaw takes priority
The October update cycle includes an exploited Windows Shell flaw. Why affected assets and verified remediation matter more than record counts.
Julian Köhn·