Explore the Kopexa blog
Privacy & Engineering
Connect privacy and technical security. Understand current cases and put safeguards into practice.
11–19 of 47
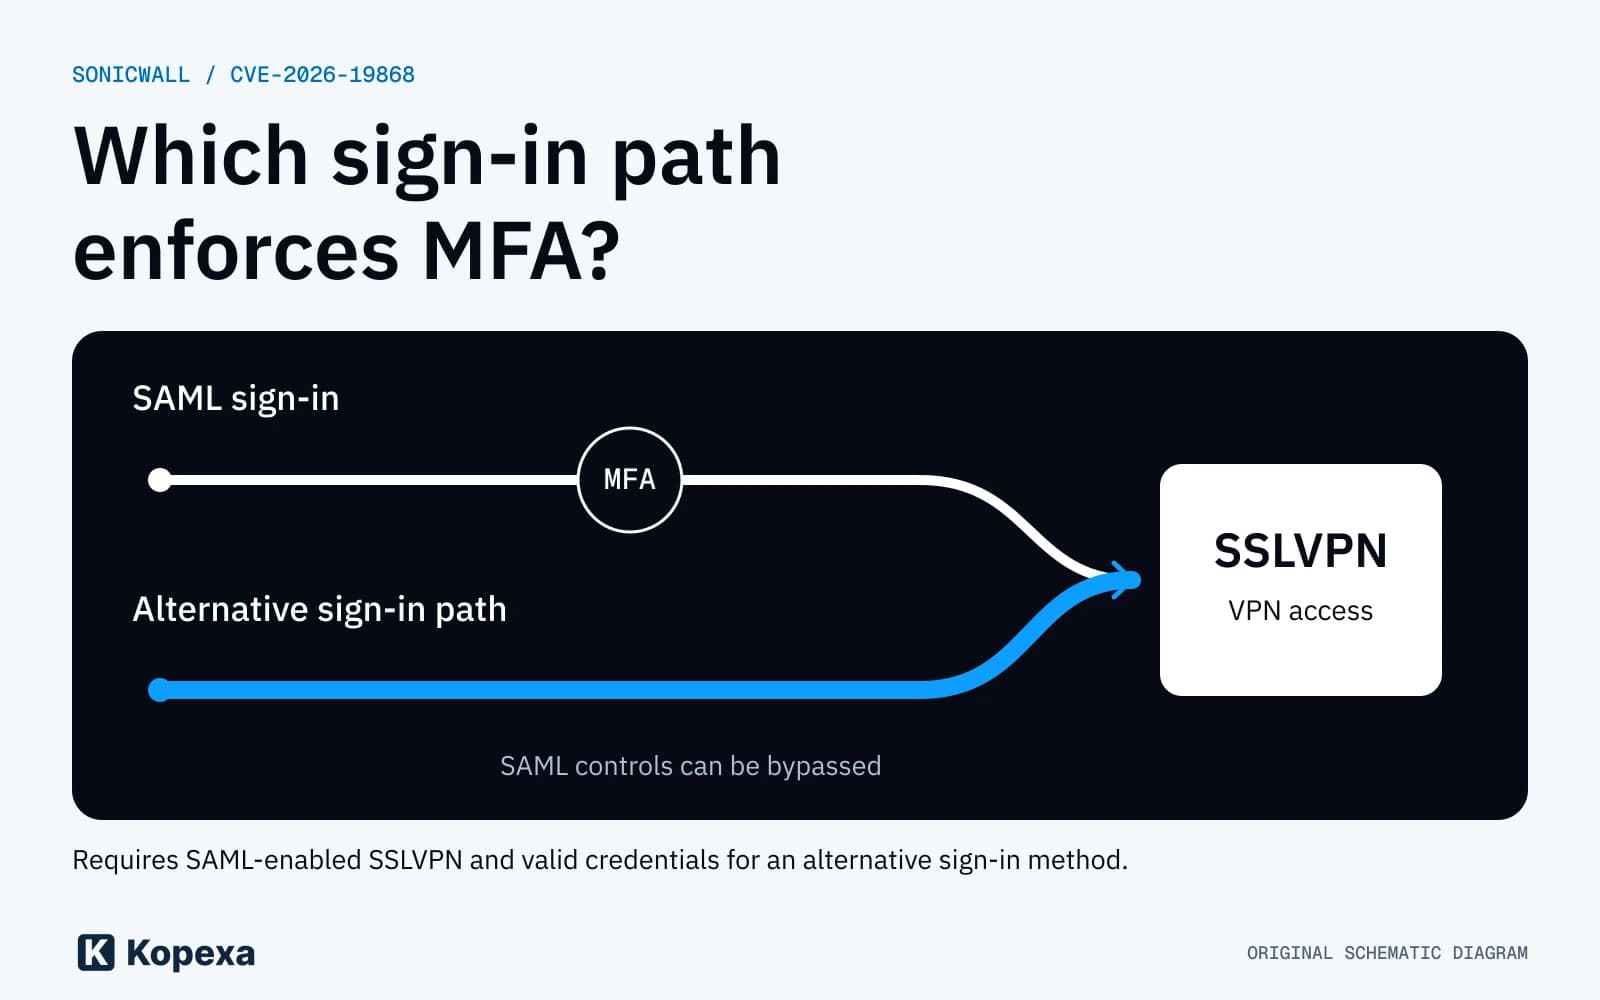
SonicWall flaw: When another sign-in path bypasses MFA
CVE-2026-19868 affects SonicOS SSLVPN with SAML. Check the prerequisites, fixed firmware versions and MFA enforcement across sign-in methods.
 Julian Köhn·
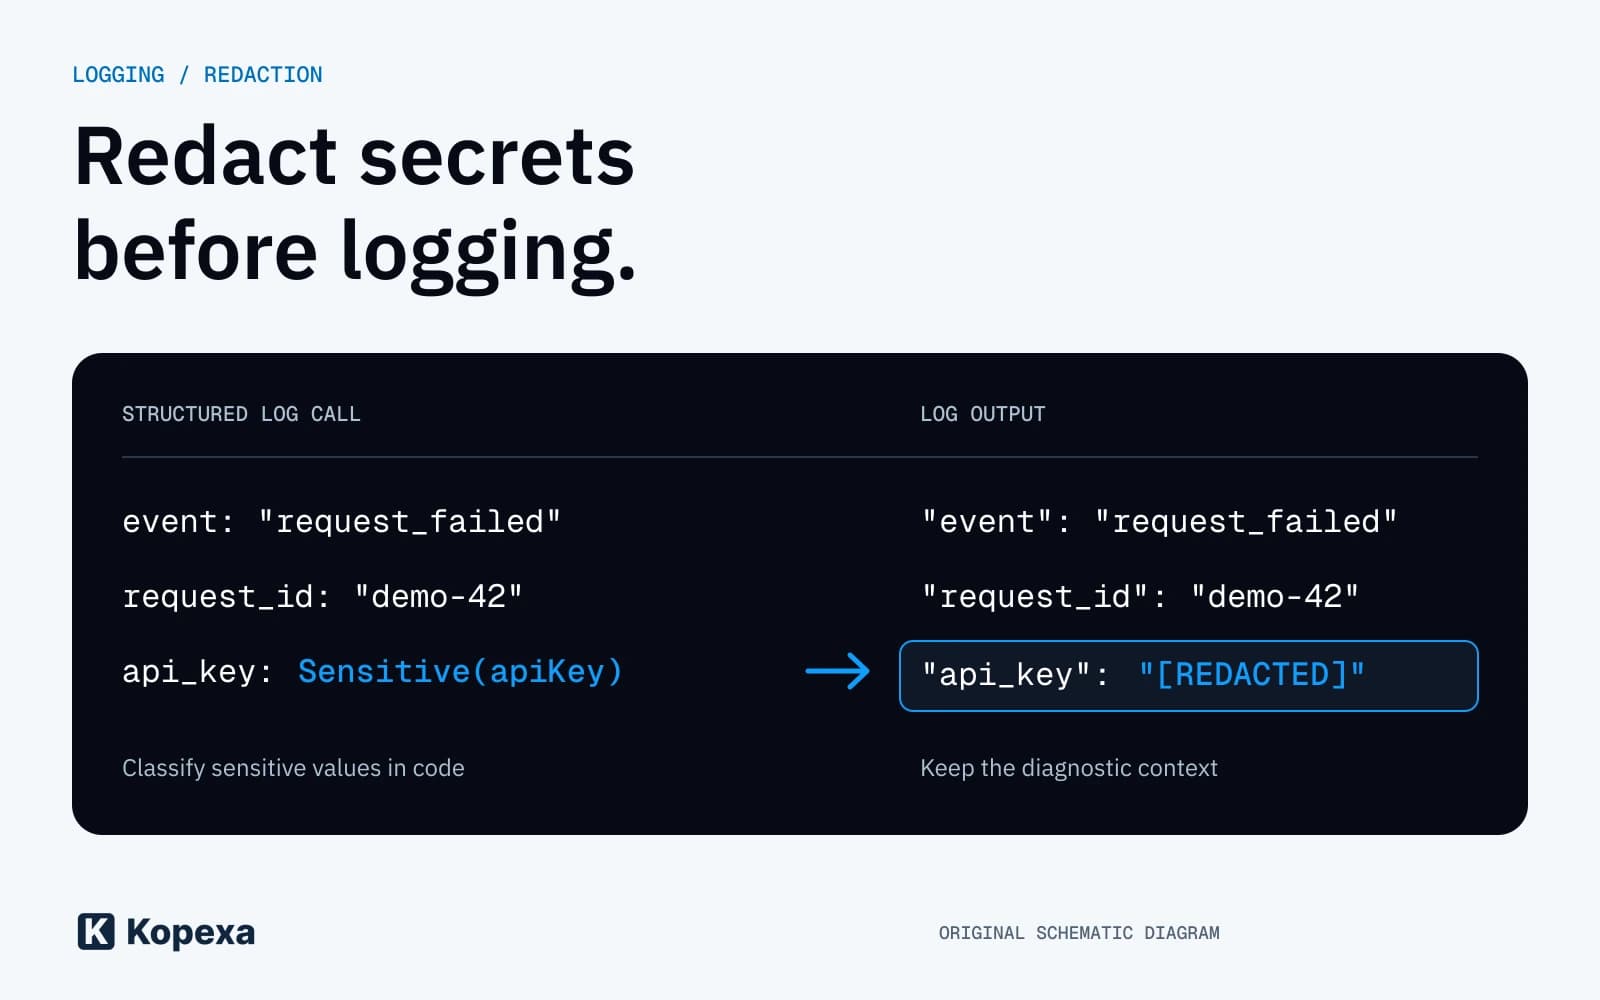
Kernel incident: Protect secrets and PII before logging
API keys and personal data need protection before they reach a log. The Kernel incident, concrete Go slog and Pino examples, and tests for your logging pipeline.
Julian Köhn·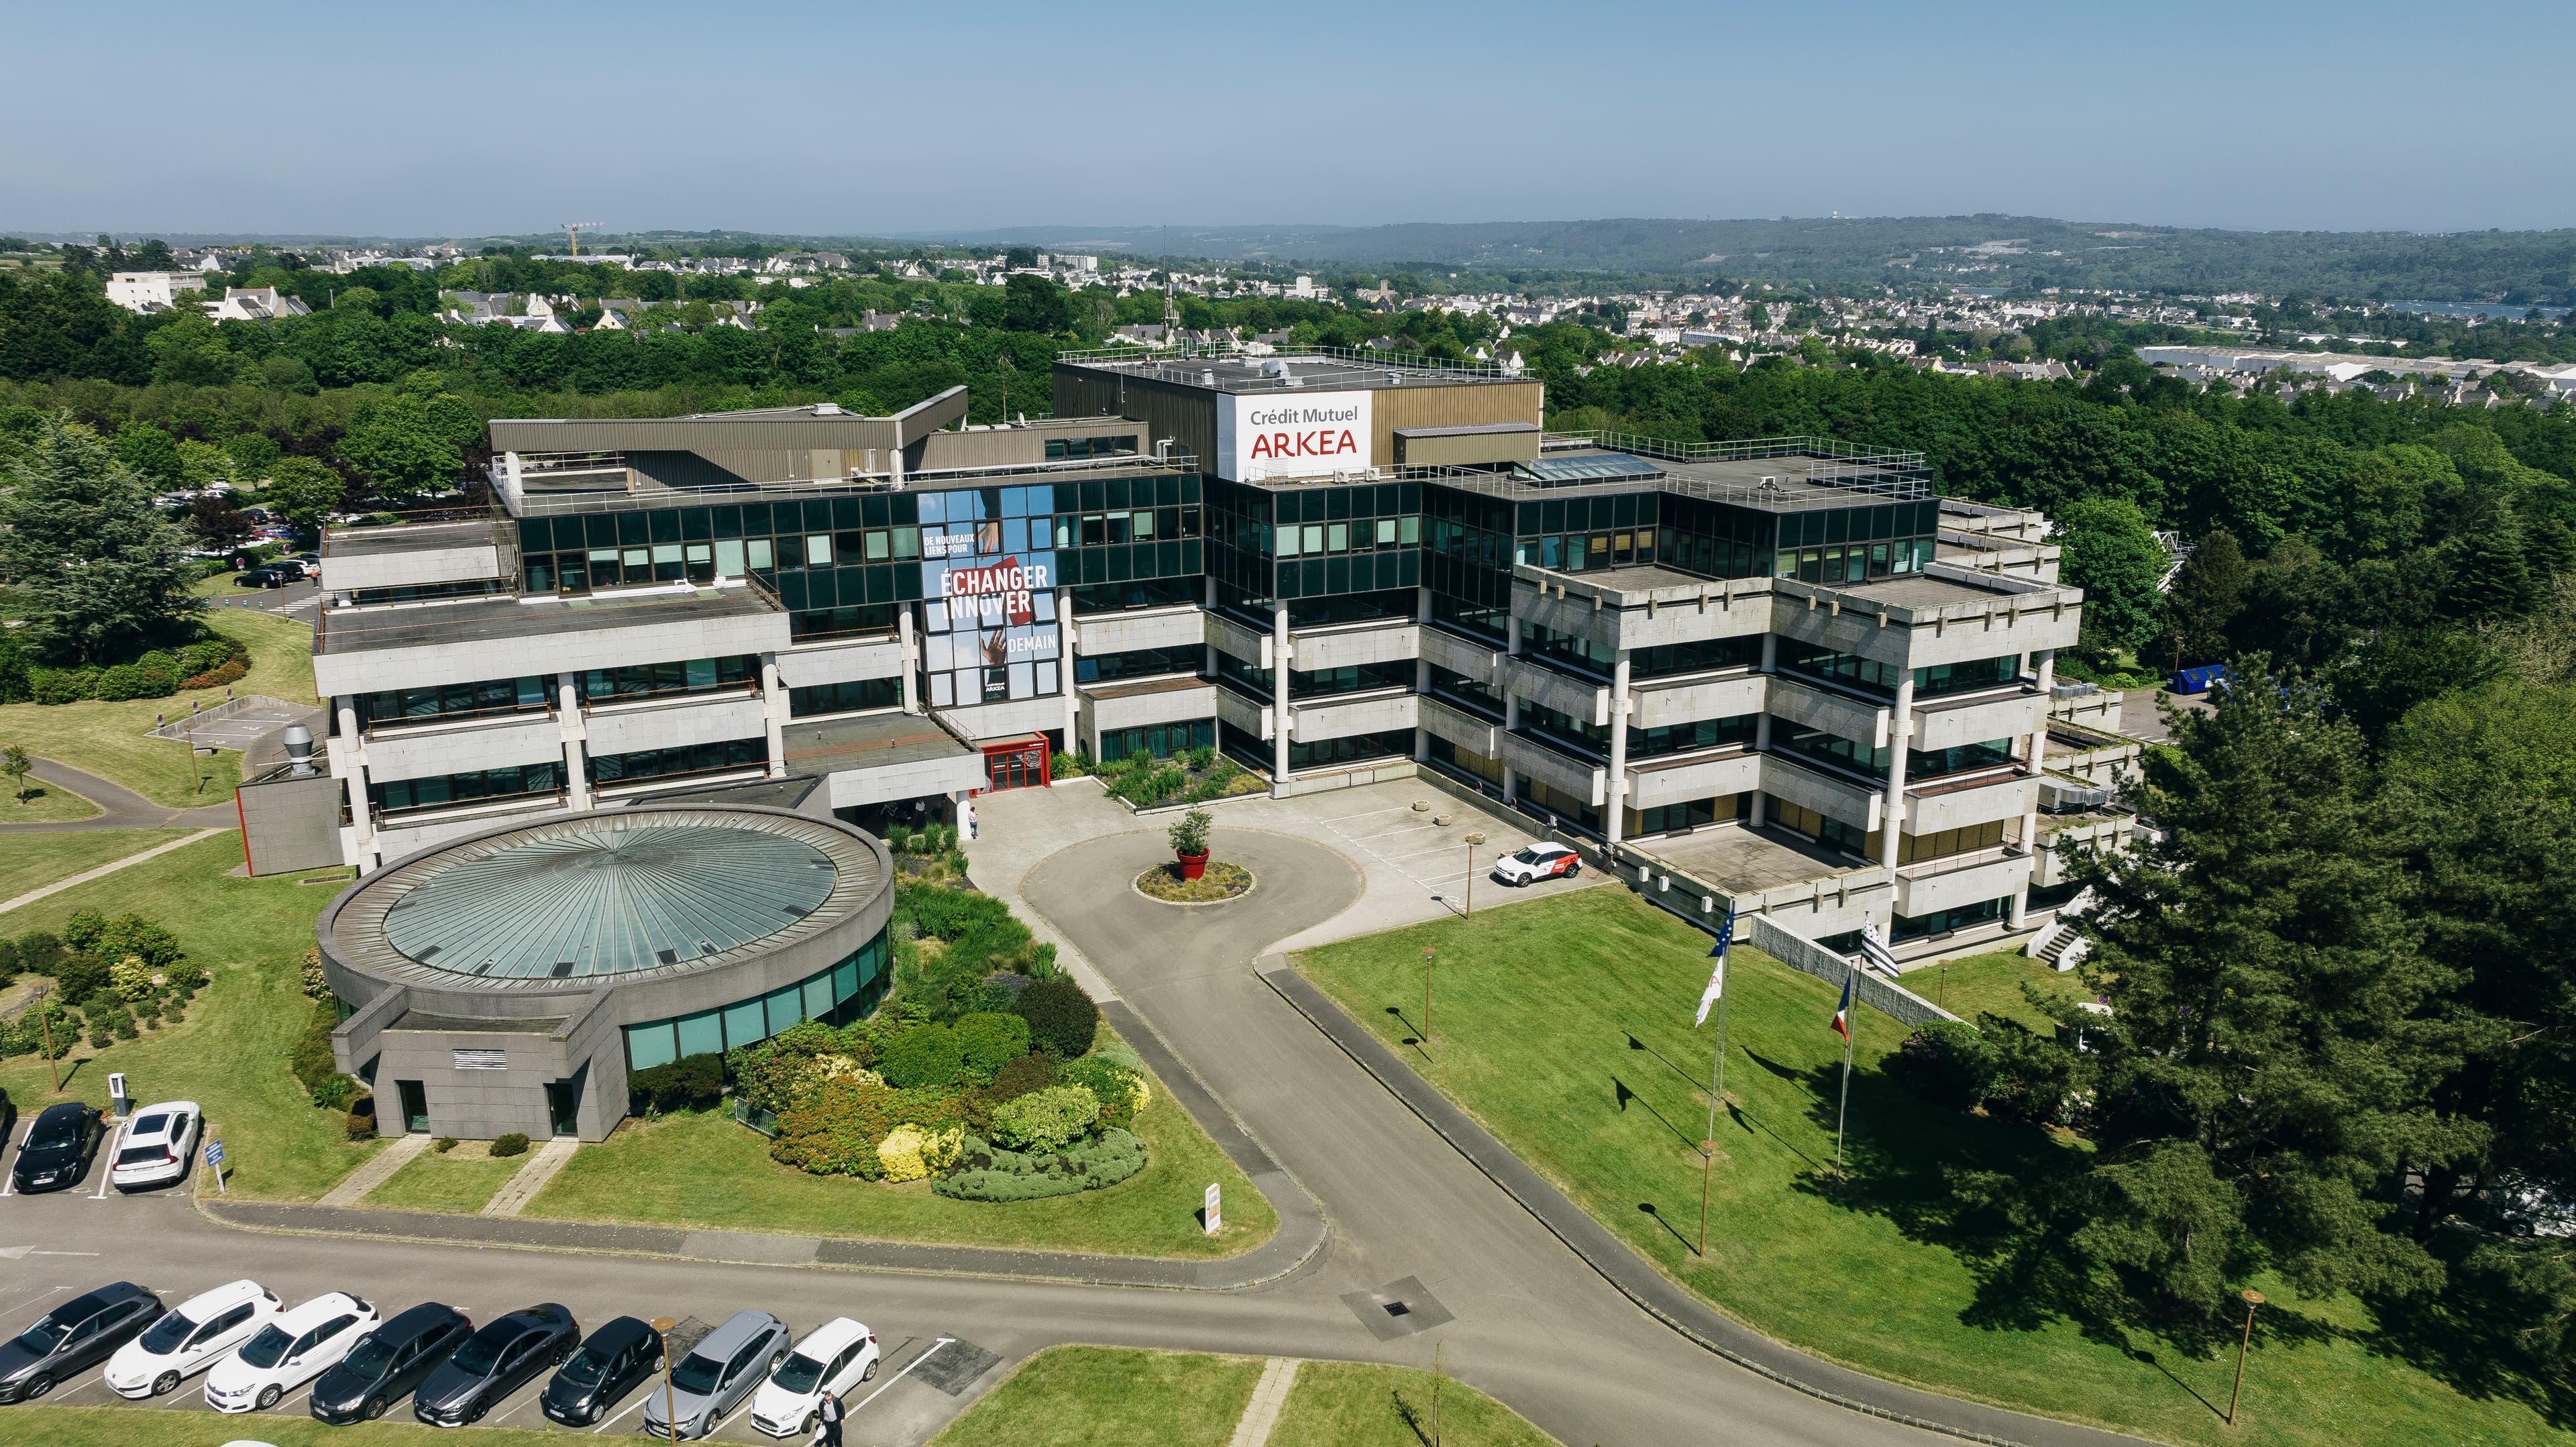
Crédit Mutuel Arkéa: Cyberattack through a service provider
The bank confirms fraudulent transfers following an attack through a provider. What is known, why the final loss remains unclear and what organisations can review.
Julian Köhn·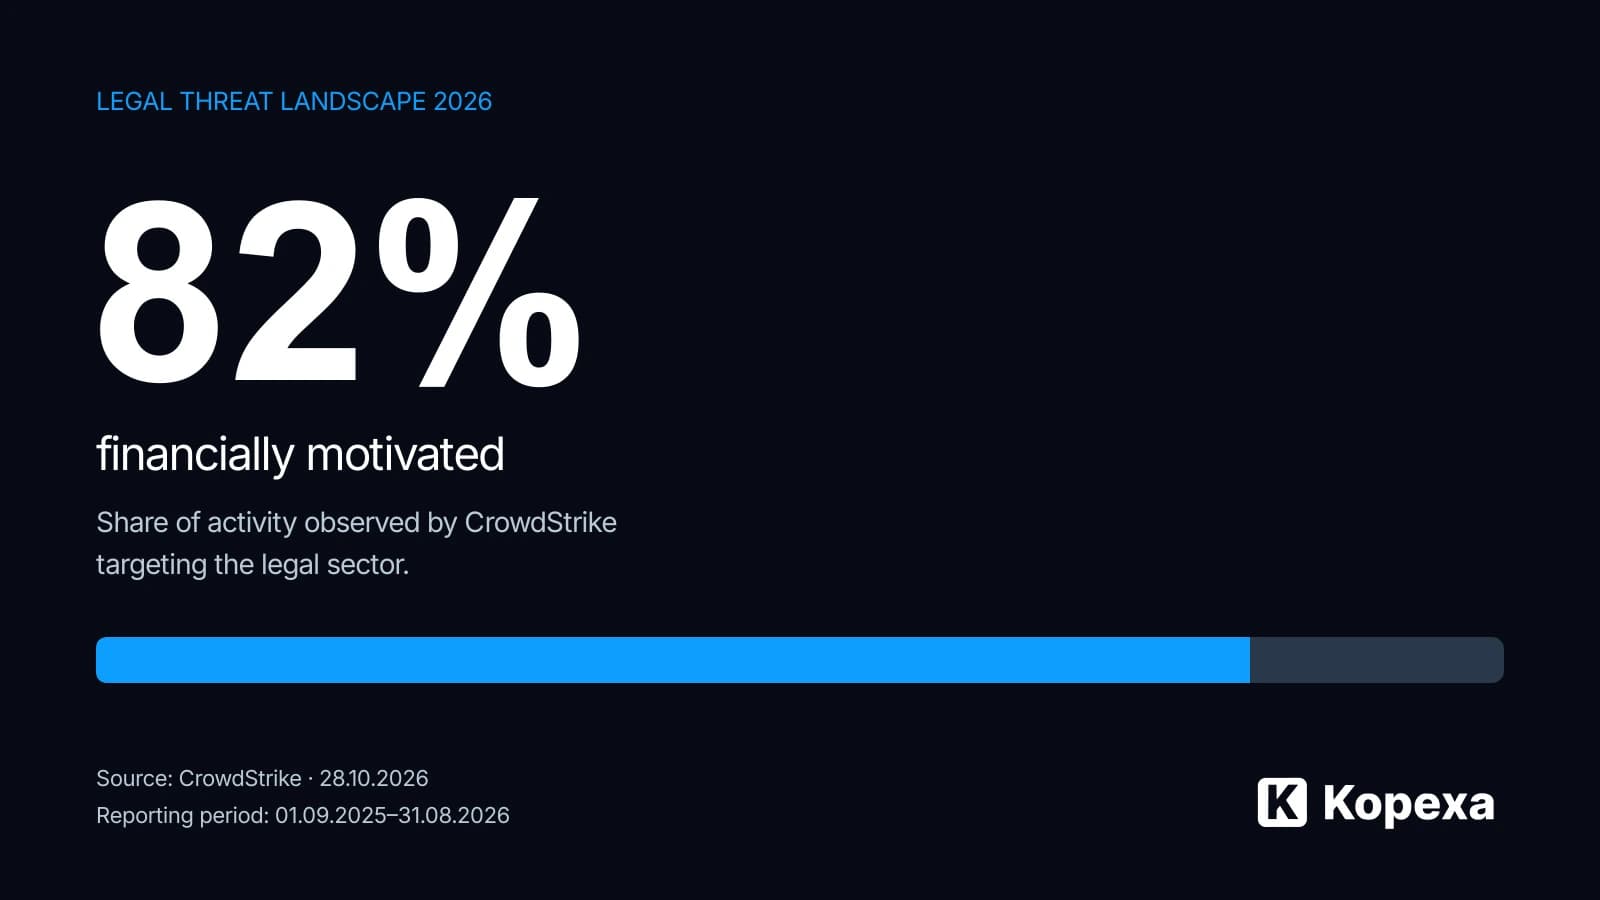
Cyberattacks on law firms: When trust opens the door
CrowdStrike reports rising attacks on the legal sector. What the figures mean and how law firms can review remote access and protect client information.
Julian Köhn·
VMware ESX: CVSS 2.7, yet known exploitation
CVE-2026-41709 concerns insufficient VMware ESX logging. Why its new KEV listing matters to patch and risk owners despite the low CVSS score.
Julian Köhn·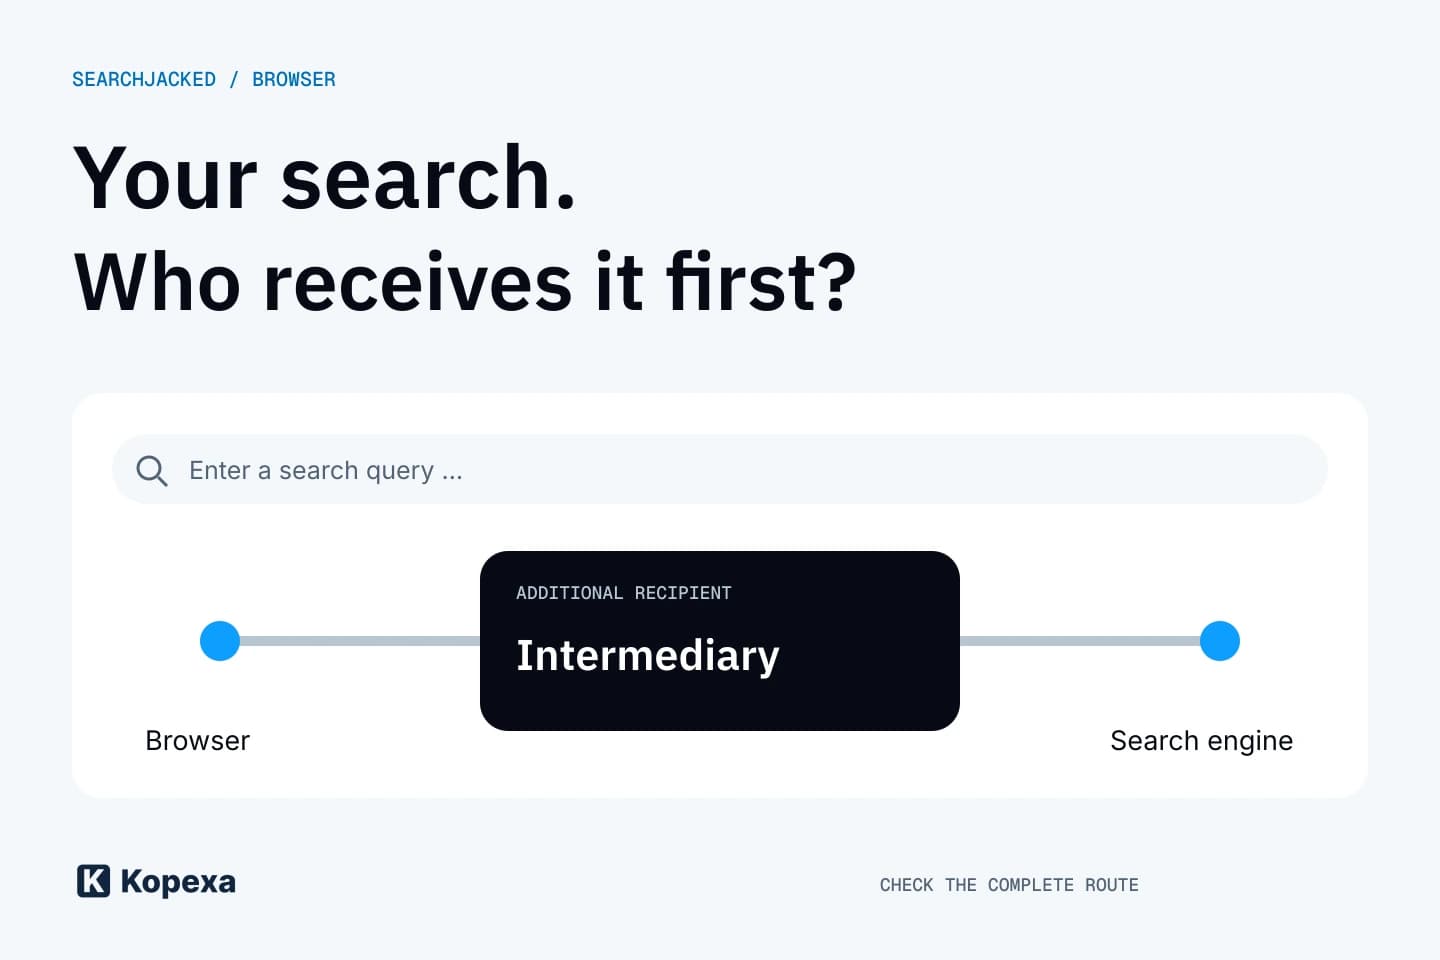
Searchjacked: When browser extensions reroute search queries
Socket reports search redirection through browser extensions. Why an official store is not enough, and how organizations can check extensions and data routes.
Julian Köhn·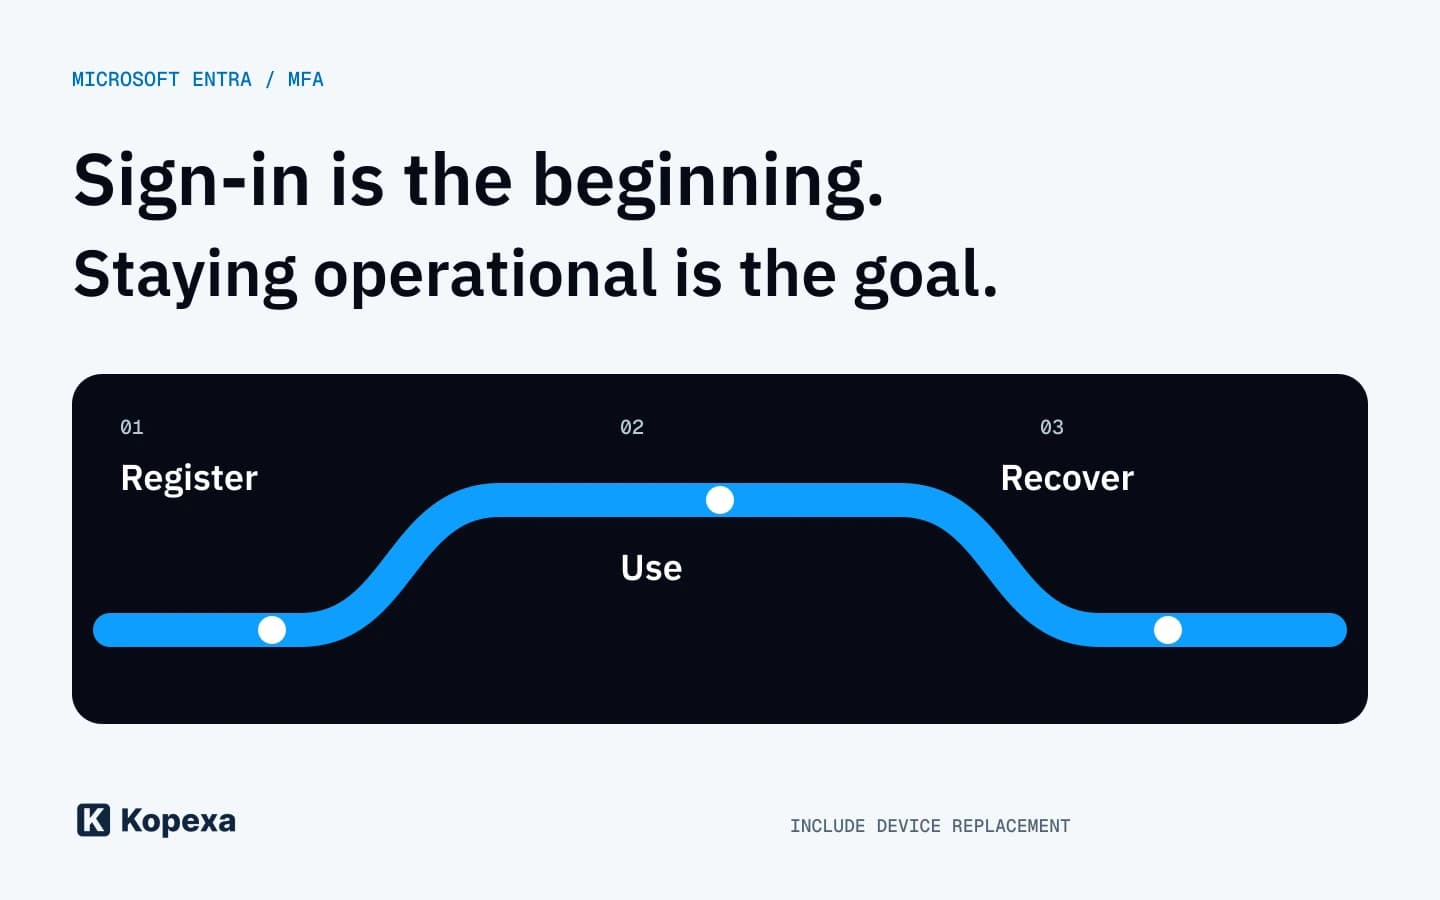
Microsoft Entra: Prepare passkeys before SMS MFA retires
Microsoft is retiring its own SMS and voice delivery for Entra MFA. Understand the affected user groups and prepare migration, recovery and operational acceptance.
Julian Köhn·
WordPress update-process flaw: What to verify now
WordPress 7.1.4 fixes a flaw during Core updates. What operators and agencies should verify about the running version and completion of the update.
Julian Köhn·
AI relays: Genuine tools, a different data route
Symantec warns about unofficial relays for Codex and Claude Code. Why AI approval needs to cover sourcing, destinations and permissions as well as the tool.
Julian Köhn·