Guide
ISO 27001 Certification: Process, Timeline, Costs & Preparation
How does ISO 27001 certification work? Plan your ISMS with a roadmap, Stage 1 and Stage 2 checklists, and a calculator to compare cost scenarios.

Your next major customer wants to work with you. One condition remains: an ISO 27001 certificate. Now there are three questions: What do we need to do? Can we meet the deadline? And what will it cost?
Here you will find the process, the documents needed and a cost calculator. Use them to define scope, assign outstanding tasks and plan your path to the certificate.
What is ISO 27001 certification?
An independent certification body assesses whether your information security management system (ISMS) meets ISO/IEC 27001 requirements. An ISMS connects people, processes and technology to keep information confidential, accurate and available when needed. ISO explains the ISMS foundations.
You assess risks, assign control owners and demonstrate implementation. An appropriately scoped certificate can satisfy a contract condition. The processes behind it help you answer customer questions and manage security work day to day.
Scope is crucial: Which services, sites and organisational units are listed on the certificate? If your customer is buying a software service, a certificate covering another business unit may be of limited use. Clarify which evidence they actually require before you start. The standard suits small businesses as well as larger organisations; implementation depends on their risks and requirements.
Germany does not impose a blanket certification requirement on every company. Customer contracts or particular sector requirements can demand evidence. ISO 27001 does not automatically replace NIS2 obligations or a TISAX assessment. TÜV NORD explains evidence requirements (German).
How does ISO 27001 certification work?
First, you establish a working ISMS. The certification body then assesses conformity in two stages. The ISO 27001 roadmap shows the milestones:
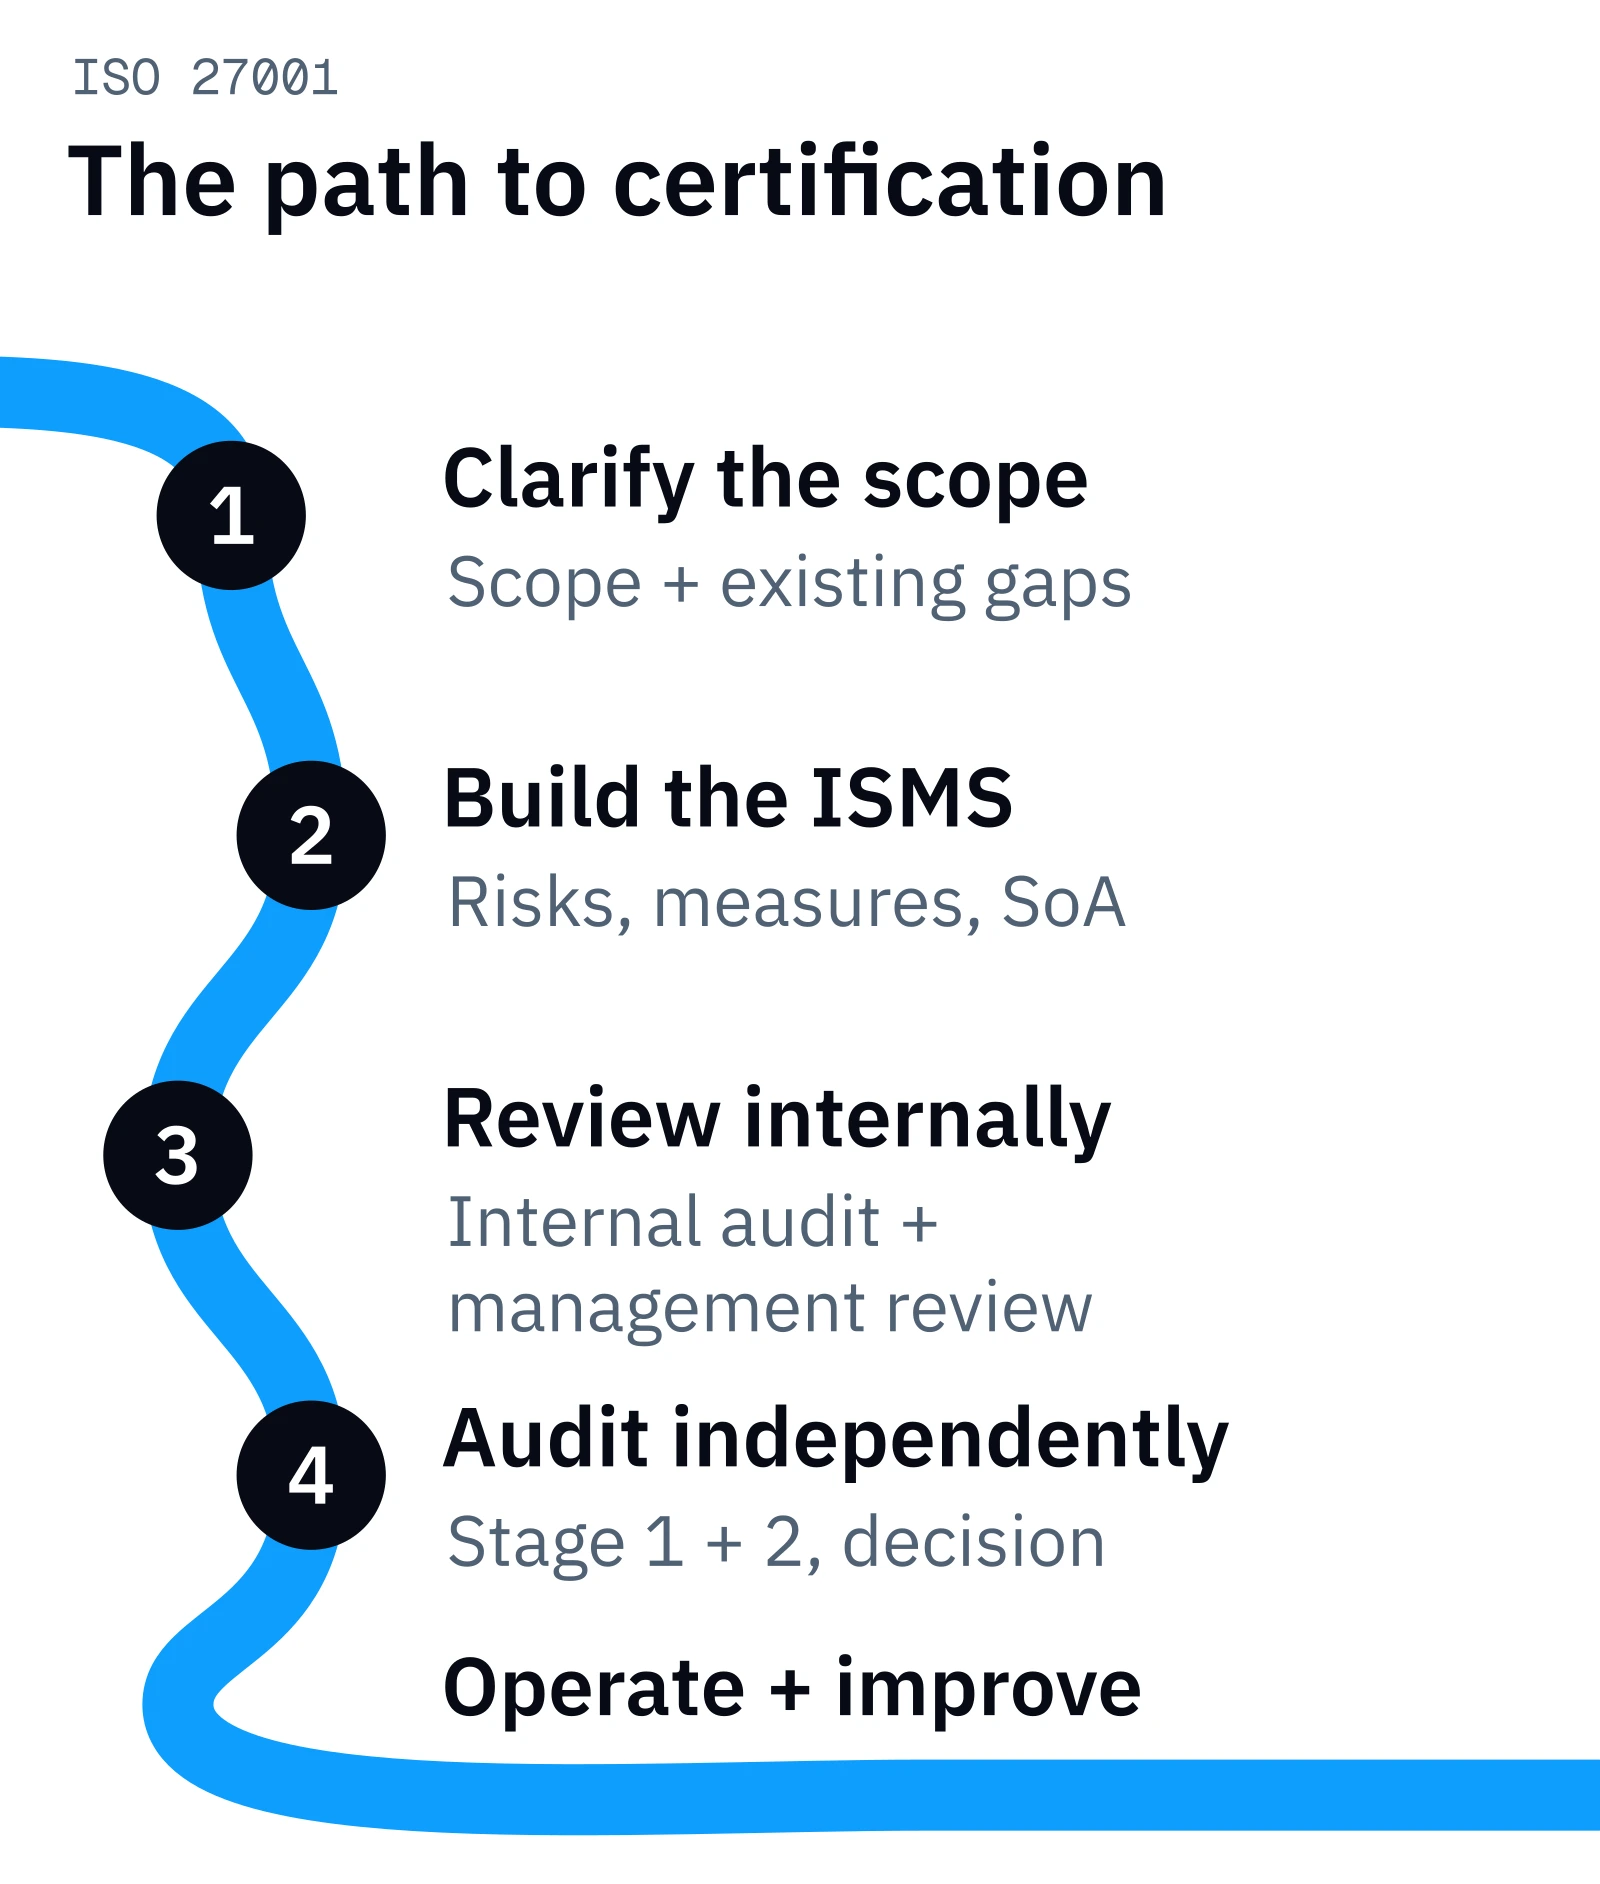
First milestone: Scope and gaps are agreed, with owners assigned. You then assess risks, decide on controls and implement them. This includes rules, technical work, training and operating records.
Before the external assessment: The internal audit reveals outstanding issues. In the management review, leadership decides on improvements and resources. Stage 1 and Stage 2 follow once you are ready. The certification body evaluates the results before making its decision.
Contact the certification body early. Scope, availability and audit planning need agreement; do not leave this until the final policy is ready. DQS describes the two-stage process and decision.
Risks and requirements determine control selection. Compare your selection with the 93 Annex A controls so that nothing necessary is overlooked. The Statement of Applicability (SoA) records selection, implementation status and justified exclusions; add further controls when needed.
How long does ISO 27001 certification take?
For initial certification, these ranges provide a starting point for planning:
| Organisation size | With an ISMS platform | Manually organised |
|---|---|---|
| Fewer than 50 employees | 3–6 months | 6–12 months |
| 50–500 employees | 6–9 months | 9–15 months |
| More than 500 employees | 9–14 months | 12–18 months |
Work backwards from the customer's deadline: When must the certificate be available? Which audit and decision periods does the certification body confirm? When must implementation, internal audit and management review be complete to meet them?
How long does the ISO 27001 audit itself take?
The certification body's quote states the audit effort. Auditor-days are not calendar days: Several auditors may work in parallel, and time for corrections may be needed between Stage 1 and Stage 2. Also allow for the certification decision.
Migrating an existing ISMS to a new platform is different from initial certification. If you want to switch, see our ISMS migration guide.
How do you prepare for Stage 1 and Stage 2?
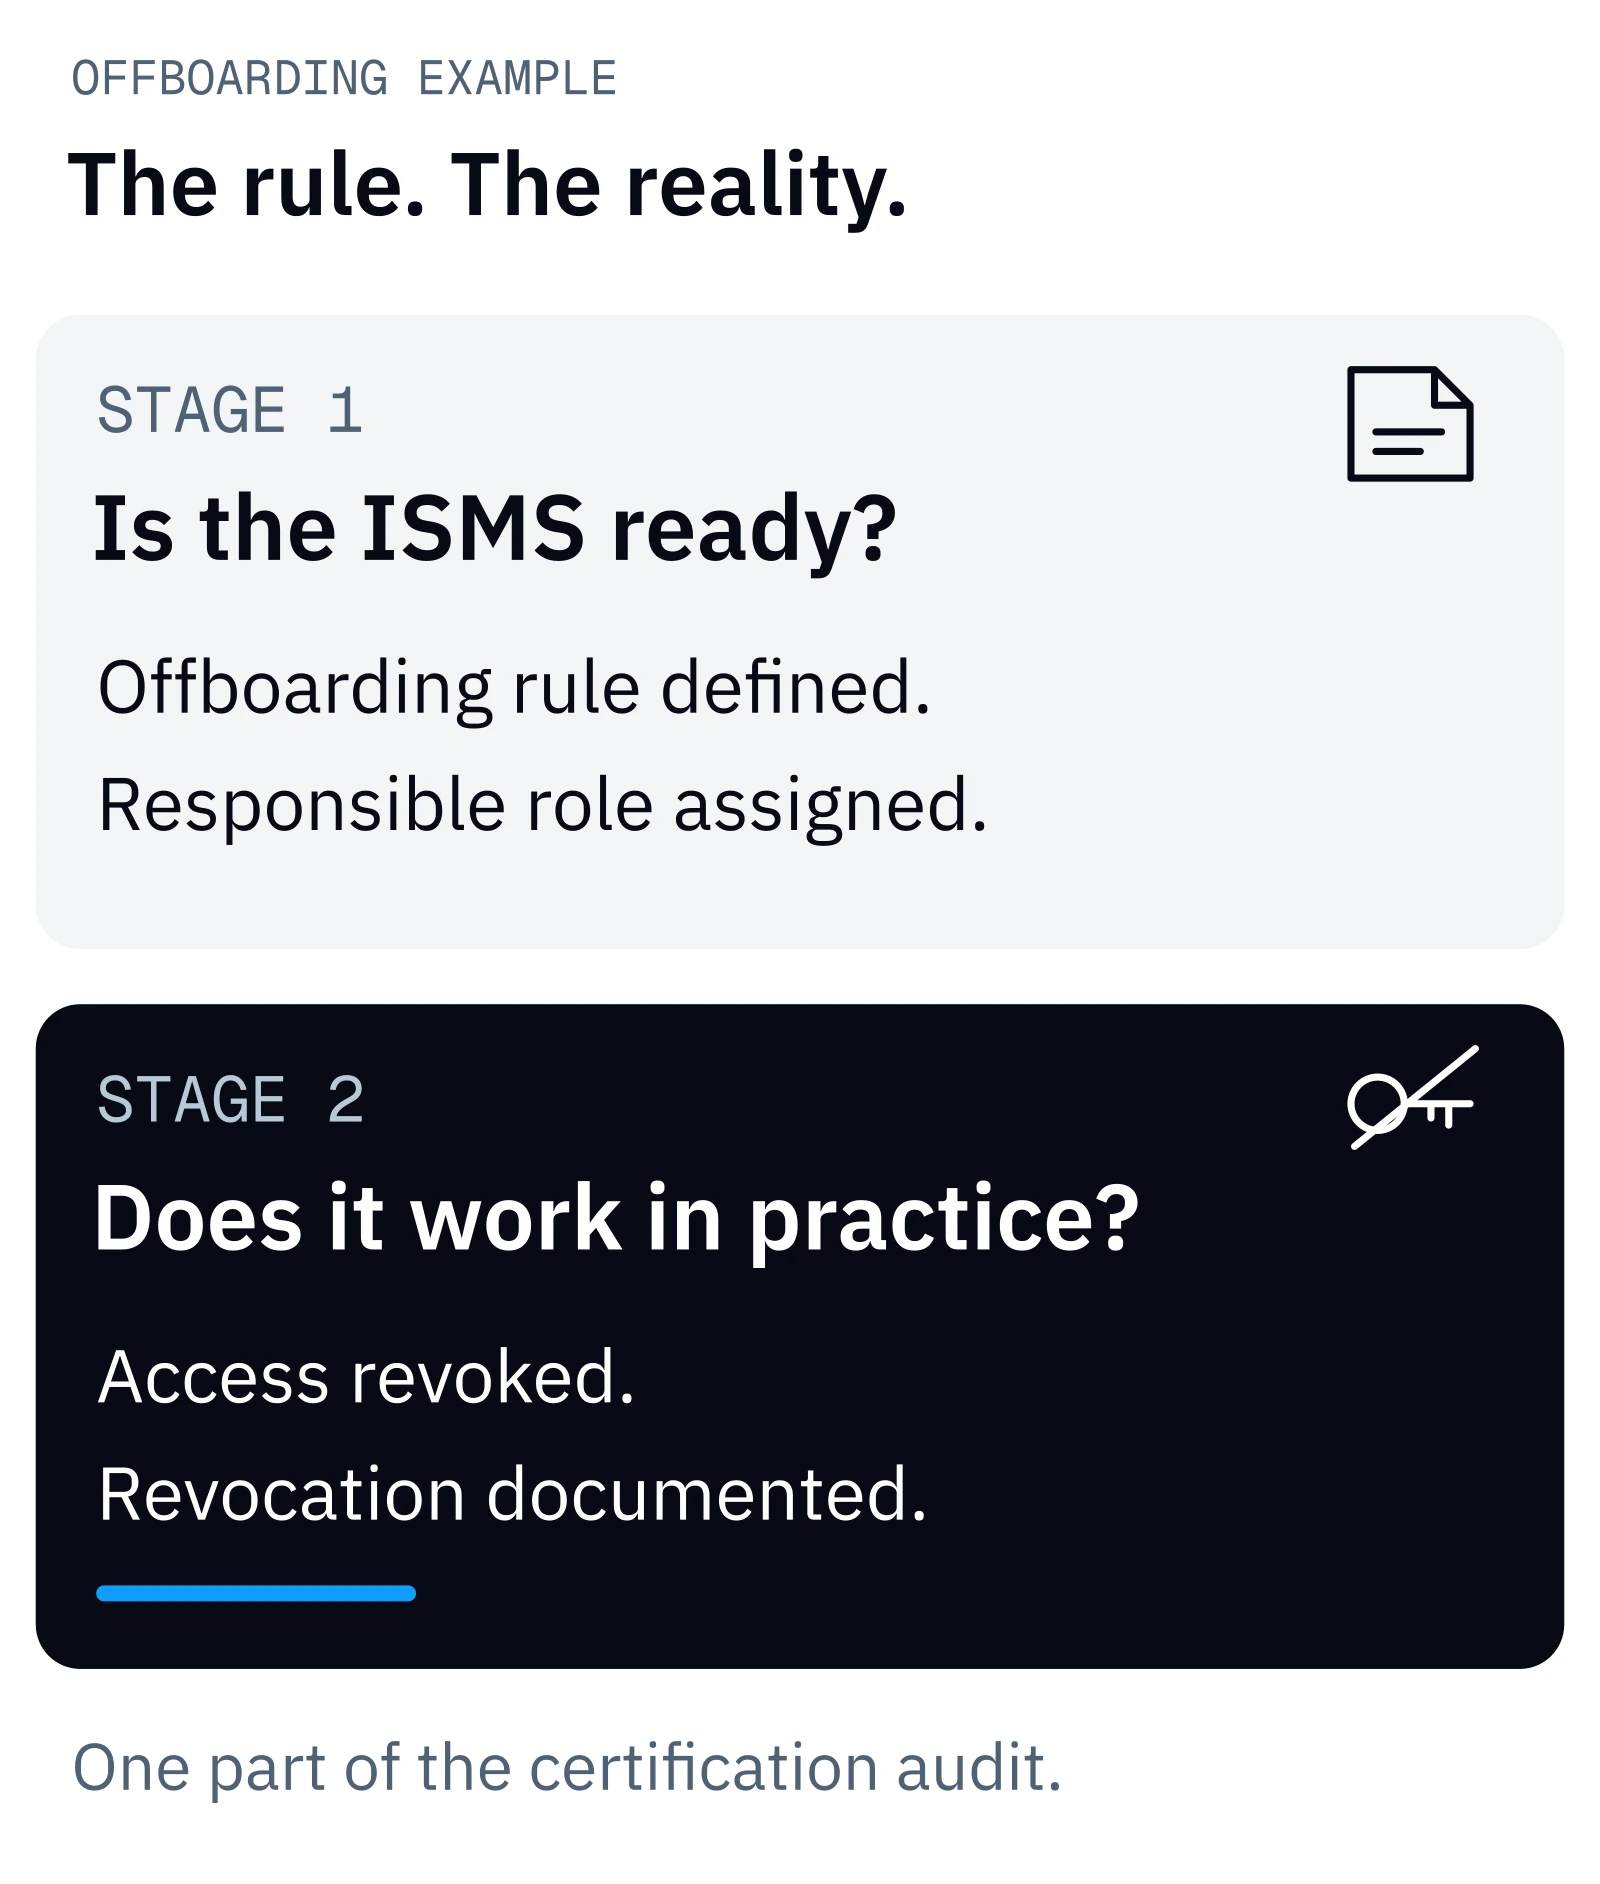
Stage 1 asks: Are we ready? The certification body assesses system readiness and important documentation. Scope, risk process, SoA, internal audit and management review must fit together.
Stage 2 asks: Does it work in practice? Discussions and sampling show whether people apply the processes and controls are effective. Employee offboarding illustrates the distinction:
Stage 2 does not have to take place exclusively on-site. Agree the appropriate format, including remote portions, with the certification body. TÜV SÜD explains the audit rules (German).
Which documents do you need for your first ISO 27001 audit?
Check these seven points when preparing. The audit plan determines the precise advance requirements:
- Scope and policy: Scope, requirements, approved information security policy, roles and objectives.
- Risks and SoA: Assessment method, current risks, treatment plan, approved residual risks and Statement of Applicability.
- Internal assessment: Audit report, management review and traceable handling of nonconformities.
- Access and people: A real approval or access revocation, appropriate training and offboarding records.
- Technical operation: For example, a restore test or a remediated vulnerability with verification.
- Suppliers and incidents: Assessment of a relevant service and a handled incident or suitable exercise.
- Audit organisation: Contacts, dates and secure access to the necessary documents.
Our Stage 1 workbook and Stage 2 evidence checklist are available as PDFs. If you are still building your ISMS, the ISO 27001 template pack includes both checklists and the supporting templates.
For a nonconformity, supplying a missing file may not be sufficient: examine the cause, extent and appropriate corrective action. Agree the required evidence and deadlines with the certification body based on the finding.
What does ISO 27001 certification cost?
ISO 27001 costs extend beyond the audit. Budget for the services you actually need rather than adopting a blanket package price:
| Cost category | What belongs in the budget |
|---|---|
| Internal working time | Project management, risk work, departmental tasks, approvals and evidence |
| External support | Agreed consulting, internal audit or specialist expertise |
| Software and implementation | ISMS platform plus additional technical controls, training and tests |
| Certification body | Stage 1, Stage 2 and other agreed services and incidental costs |
| Subsequent years | Ongoing maintenance, surveillance audits and eventual recertification |
What does an ISMS cost, and which part is certification? Implementation and operation are your own responsibilities. Audit fees pay for independent assessment. This distinction matters when comparing quotes and discussing budgets. TÜV NORD also distinguishes these costs (German).
An example for internal work: 20 project days × 8 hours × EUR 60 produce EUR 9,600. These are illustrative assumptions, not market prices. Add your quotes for consulting, licences, technical implementation and certification. Comparing a CISO's full salary with a software licence would be unfair; internal work remains necessary with software.
ISO 27001 cost calculator: compare effort scenarios
The calculator combines audit time from our audit cost calculator with the current Kopexa Pro price. Optionally add four hours of onboarding and one hour of coaching per week. Adjust the number of people, audit day rate and weeks of coaching to your project.
Interactive cost calculator
What does ISO 27001 cost in your setup?
Calculate audit and software costs. Add coaching for your ISMS setup if you need it.
Include external staff working within your scope.
Adjust the day rate to your certification body's quotation.
4 hours onboarding + 1 hour per week · €180 / hour
Year 1 breakdown
- Certification audit (Stage 1 + 2)12 audit days × €1,200
- €14,400
- Kopexa Pro license (year 1)
- €7,188
- Onboarding + coaching16 hours × €180
- €2,880
Audit, software + coaching, year 1
€24,468 excluding VAT
Surveillance audit + Pro license per following year
€11,988
How it is calculated
Audit time follows ISO/IEC 27006-1:2024, Table C.1, at typical complexity, without blanket reductions. The starting rate is the lowest configured estimate in our audit cost calculator. The standard does not set euro prices. Coaching includes a one-off four-hour onboarding session and one hour per selected week; your team implements the ISMS. The number of weeks sets the coaching budget, not the certification date. The Pro license covers one space. Add certificate fees, travel and additional sites where applicable.
See how your team manages risks, measures and evidence in one place.
Planning several standards? The audit cost calculator helps compare them. For automotive requirements, see the TISAX cost guide.
How long is an ISO 27001 certificate valid?
The usual certification cycle lasts three years: surveillance audits in the first two years, with recertification before expiry. NQA describes the cycle.
Keep recurring work in your plan: review risks, assess access rights and suppliers, train people, and conduct internal audits and management reviews. New services or sites may require a scope review. The certificate remains useful evidence when the system behind it continues to operate.
How does Kopexa support your ISO 27001 project?
When risks are in Excel, policies in Word and evidence in SharePoint, even one customer question can trigger several requests for information. Kopexa ISMS software connects requirements, measures, risks, tasks and evidence. You can see who is responsible, what remains open and which evidence belongs to a measure.
Measures mapping helps you reuse an implemented measure for several appropriate requirements. You can extend your ISMS to further frameworks without maintaining the same work several times. Work internally or involve a partner. Independent certification remains the certification body's responsibility.
Bring an open action or a specific audit question to the demo. We will show you who takes on which task and how you demonstrate implementation, from risk to evidence.
Quick answers
Frequently Asked Questions
Still have a question? Find the answers here.
What does an ISO 27001 certificate confirm?
An independent certification body confirms that your ISMS meets the standard's requirements within the assessed scope. Check which services and sites appear on the certificate. It provides evidence about the management system, not a guarantee against every security incident. ISO itself does not issue certificates.
Which version of ISO 27001 applies today?
The international edition is ISO/IEC 27001:2022 with Amendment 1:2024 concerning climate-related considerations. ISO 27001 is the usual short form. The German adoption is DIN EN ISO/IEC 27001:2024-01, supplemented by A1:2024-11. Different years do not automatically mean different requirements here; this does not refer to an international ISO 27001:2024.
How long does ISO 27001 certification take?
Planning ranges for initial certification with an ISMS platform are 3–6 months below 50 employees, 6–9 months for 50–500 and 9–14 months above 500. The manually organised comparison ranges are 6–12, 9–15 and 12–18 months respectively. These are vendor estimates, not fixed deadlines. Scope, maturity, capacity and audit planning determine the schedule. Our eight-week case was recertification with an existing ISMS and platform migration, not a new implementation.
Which documents do I need for Stage 1 and Stage 2?
Have the scope, policy, objectives, risk method, assessments, treatment plan, SoA, internal audit and management review available. Stage 1 assesses readiness. At Stage 2, you also need appropriate operating examples, such as an access revocation or restore test, to demonstrate implementation and effectiveness. The audit plan determines what to submit in advance.
Is EUR 15,000 enough for ISO 27001 certification?
That cannot be promised credibly without knowing the starting point and scope of work. Check whether internal work, consulting, software, technical gaps and audit fees are included. An existing ISMS changes the effort compared with a new implementation. Add your own costs to a certification quote and plan subsequent years separately. The calculator helps compare scenarios; its assumptions are not a binding total price.
Do I need a consultant, or can I implement ISO 27001 myself?
You can lead implementation internally if expertise and time are available. External support can fill specific gaps, such as risk methodology or internal audit. Kopexa lets you work on tasks and evidence yourself or with a partner. Agree deliverables, handover and internal ownership when engaging external support so the ISMS continues to operate afterwards.