Topic in the Kopexa blog
ISO 27001
Explore ISO 27001: background information, practical examples and recent developments from the Kopexa blog.
1–10 of 20
Can you maintain ISO 9001 and ISO 27001 together in one system?
Connect quality management and your ISMS: shared processes, distinct assessment objectives and suitable evidence, with a new-provider example.
 Julian Köhn·
ISO 27001 Annex A: Controls by category in 2026
Use Annex A’s four themes practically: allocate ownership, connect measures and assess evidence meaningfully.
Julian Köhn·
ISO 27001 for cloud and hosting providers: Protect the service traceably
ISMS for cloud and hosting providers: test responsibility boundaries, shared infrastructure and recovery using a specific service.
Julian Köhn·
ISO 27001 software for IT providers: Answer customer questions faster
Assess ISO 27001 software for IT providers: keep customer engagements, privileged access and shared evidence clearly scoped.
Julian Köhn·
ISO 27001 software: Prepare for certification and close open gaps
Choose ISO 27001 software by testing scope, risk treatment, SoA and dependable evidence during a pilot, beyond comparing document templates.
Julian Köhn·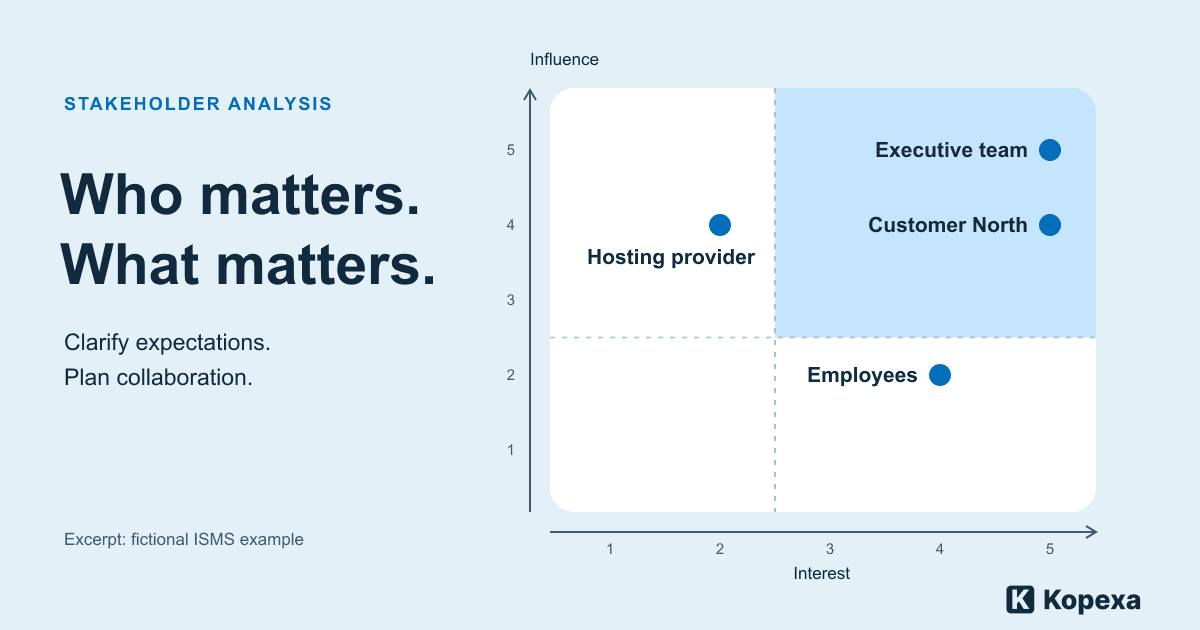
Stakeholder analysis: template, matrix and worked example
Identify whose requirements matter and who will act on them. A stakeholder analysis guide with an Excel template, matrix and worked ISMS example.
Julian Köhn·
ISO/IEC 27090: bringing AI security risks into your ISMS
Understand the scope of ISO/IEC 27090 and connect AI applications, suppliers and data risks to practical work in your existing ISMS.
Julian Köhn·
ISO 27001 Checklist: What Is Missing Before Your Audit?
Use this ISO 27001 checklist to identify gaps before your audit and plan the next steps towards certification. Includes a free PDF download.
Julian Köhn·
ISMS Software Comparison: What Matters for ISO 27001, TISAX and NIS2?
ISMS software compared: selection criteria, features and costs for ISO 27001, TISAX and NIS2. The practical guide for your decision.
Julian Köhn·