Companies working with Kopexa







“I often didn't know where to put the evidence. Now it's: bring it on, I find the right place instantly!”
Where are you today?
Your management system grows. Your team needs to keep up.
Bring several standards together
ISO 27001 is established and TISAX or NIS2 adds requirements. Reuse shared actions and evidence while keeping track of what each standard still needs.
Explore framework mappingImprove an existing ISMS
Risks live in Excel, documents in SharePoint and tasks in separate boards. Bring their relationships and responsibilities into one shared working context.
Run your ISMS day to dayBuild your first ISMS
A customer requires information security evidence. Plan the work, assign responsibilities and prepare your team for the audit.
Explore the ISO 27001 roadmapFramework mapping
Organise shared work once. Map it to each standard.
One action, one owner, one implementation status. Link shared work and evidence to the relevant requirements in ISO 27001, NIS2 and TISAX. Additional requirements remain visible for each standard.
Review access rights
Owners check existing permissions and document the changes needed.
- Responsibility
- One shared owner
- Shared evidence
- Access rights inventory and documented review
Shared work supports these requirements
- ISO 27001:2022 · A.5.18
- Manage and review access rights
- NIS2 · Art. 21(2)(i)
- Access control within security policies
- TISAX / VDA ISA 6 · 4.1.3
- Review user accounts periodically
Also check for each standard
- ISO 27001: Document applicability and implementation within the ISMS.
- NIS2: Also address personnel security and asset management.
- VDA ISA: Check account lifecycle and protected login information.
Example mix: ISO 27001:2022, NIS2 and VDA ISA 6. Evidence supports shared topics; scope and full coverage are assessed for each requirement.
Explore standards and requirementsBusiness processes and outage risks
Know what needs to recover first when a process stops.
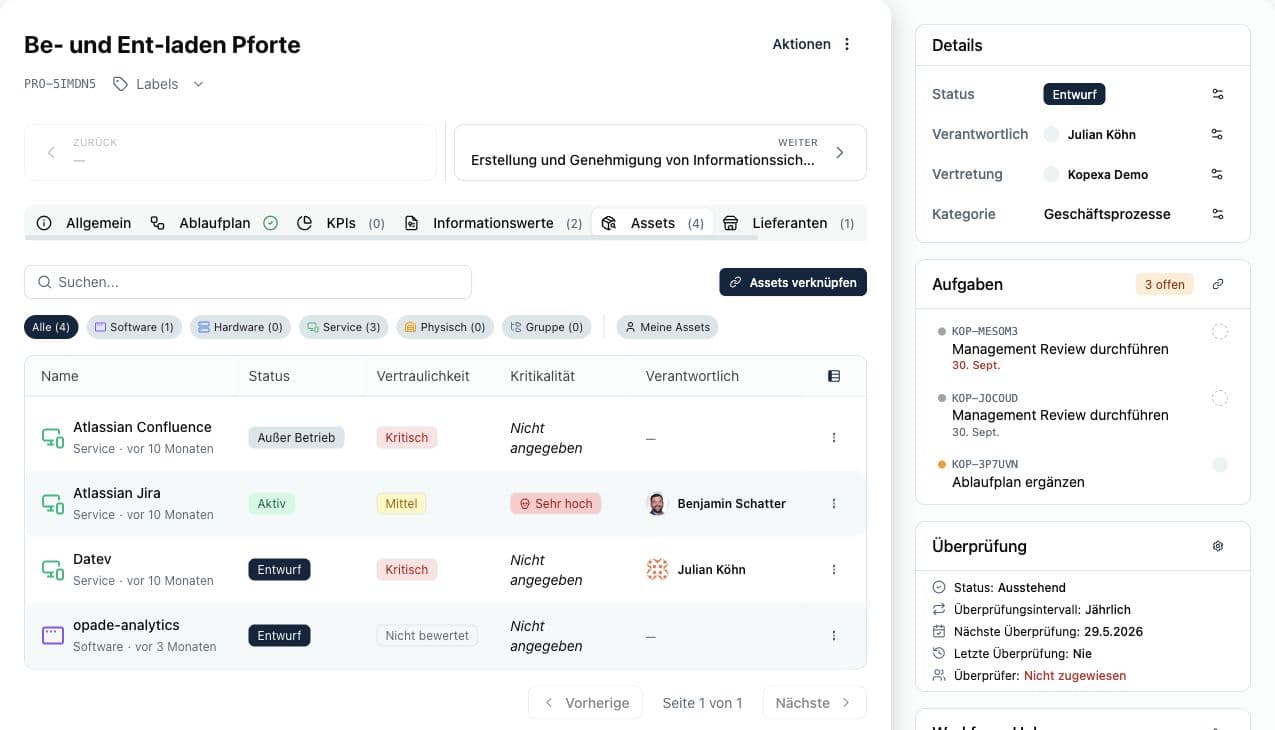
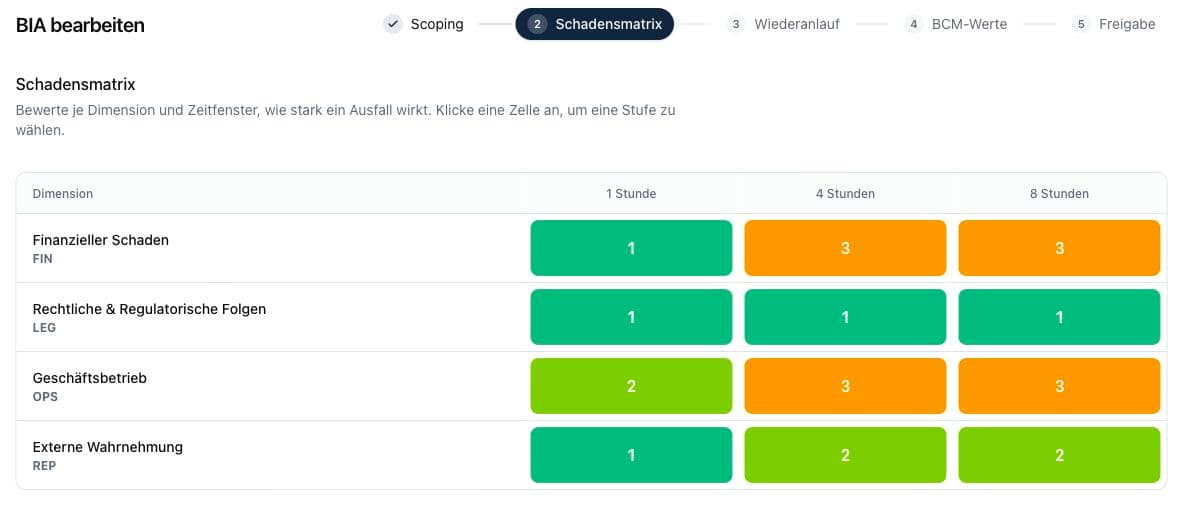
An IT outage also affects customer service, order processing or production. Connect business functions and processes to the assets and suppliers they need. Use a Business Impact Analysis to assess how an outage affects the business over time, then prioritise recovery.
- Make workflows and handovers clear with BPMN
- Bring dependencies and owners into the process context
- Connect risks and tasks to the affected workflow
Supply chain and vendor assessments
Assess suppliers without chasing every response.
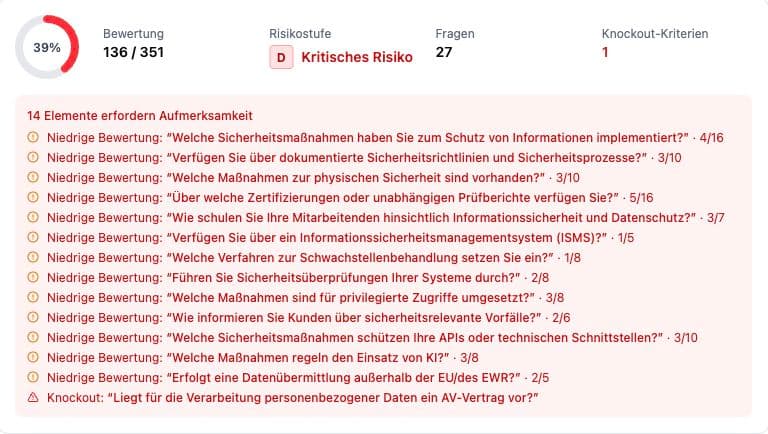
A key service provider or supplier can affect several processes. Keep the supply chain connected and assessments traceable. Kopexa sends surveys and reminders automatically; configurable rules rate risks based on the answers.
From finding to action
An open action needs more than a row in Excel.
Framework requirements explain why work is needed. Processes and suppliers provide the context, risks establish priority. Tasks, owners and evidence connect the follow-up work in the same platform.
Whether a task comes from a risk assessment, a vendor assessment or a review, it stays connected to its business context. Your team can see why work is needed, who owns it and when it is due.
- 01
Establish the context
Link the task to the affected risk, document or process.
- 02
Assign an owner and deadline
Manage work with configurable boards, states, labels and milestones.
- 03
Keep it current
Periodic reviews remind your team to check whether risks and documents are still up to date.
Customer perspective · ISO 27001
How an established ISMS moves forward with Kopexa.
„Because everything in Kopexa is linked and task management is built in, the system practically guides you through. For me, the real value is the focus I've gained: I no longer get lost in evidence management, and I have a clear head to assess risks more soundly and drive strategic topics like BCM, NIS2 and QMS.“
Getting started and ongoing operations
Build on what you have. Plan the next step together.
Your existing ISMS is the starting point. In the demo, we look at your current documents, risk registers and standards. Together, we discuss which content to bring over, how to represent responsibilities and what support you need.
- 01
Agree the scope and existing content
Review policies, controls, risks and evidence. Decide which standards, departments and owners will start working in Kopexa.
- 02
Bring over structure and content
Map existing content to the relevant requirements. Discuss available import options and any preparation needed using your own files.
- 03
Trial a working process
Assign owners and recurring tasks. Check with your team that evidence stays traceable from the initial finding to completion.
With your own team
Security, IT, quality management and process owners work in a shared context. Responsibilities stay visible when several departments are involved.
With external support
Bring your consultants or external security leads into the same platform. Discuss software and consulting services based on your needs.
Questions about compliance and ISMS for mid-market companies
How do we bring over our existing management system?
We start with your standards, files and responsibilities. Together, we agree the structure, required import options and data preparation. Content is then linked and a working process checked with your team. The CSN case study shows a real transition of existing policies, controls and custom actions.
How is pricing structured?
Software is billed by plan. Pro costs 599 EUR/month and includes multiple frameworks, vendor management and cross-framework mapping. The pricing page lists the current included services. Onboarding and external consulting are discussed according to the agreed scope.
Where is Kopexa hosted and how is data protected?
The published sub-processor list specifies France and Germany for application servers, databases and customer data storage. Other services are listed there with their purposes and locations. The security statement describes AES-256 encryption for stored data and TLS 1.2 or higher for data in transit.
Does Kopexa suit an existing ISMS?
Yes. Kopexa connects risks, policies, actions and evidence with owners and processes. We discuss how to bring over and organise your existing content based on your data and working practices in the demo.
How does Kopexa help with several standards?
Shared actions and evidence can be linked to requirements across standards. Coverage and additional requirements are assessed for each standard. A link does not automatically mean that every requirement is fully met.
How does a BIA help a manufacturing company?
A Business Impact Analysis evaluates the consequences of a process outage over different time periods. Together with dependencies and recovery values, it helps establish priorities and assess risks in their business context.
Can we rate suppliers automatically?
Kopexa sends assessment surveys and reminders automatically. Its survey engine supports configurable, answer-based risk ratings. Results can then be followed up through risks and tasks.
Do we need a dedicated compliance department?
You can share work across your existing team and involve external support. Professional decisions, implementation and responsibility for your management system remain with your organisation and its appointed owners.
Show us how you work today.
We will show you how your team can bring existing standards, business processes and supplier risks together in Kopexa.
Book a demo