28–36 of 54 articles
By publication date
ISO 27001 Certification Explained Simply: Process & Costs
What ISO 27001 certification means, who actually needs it, and how the process runs from Stage 1 to recertification, explained clearly for beginners.
 Julian Köhn·
AI Dependency as a Compliance Risk: What the Anthropic Case Teaches Every CTO
A US decree cut off access to leading AI models overnight. Why AI dependency is a real compliance risk that belongs in NIS2, ISO 27001 and DORA.
 Nikolai Shulgin·
ISO 27001 and Data Protection: GDPR, TOMs and Evidence
Does ISO 27001 cover GDPR? Understand Article 32 TOMs and follow eight practical steps, with evidence, ownership and a worked example.
Julian Köhn·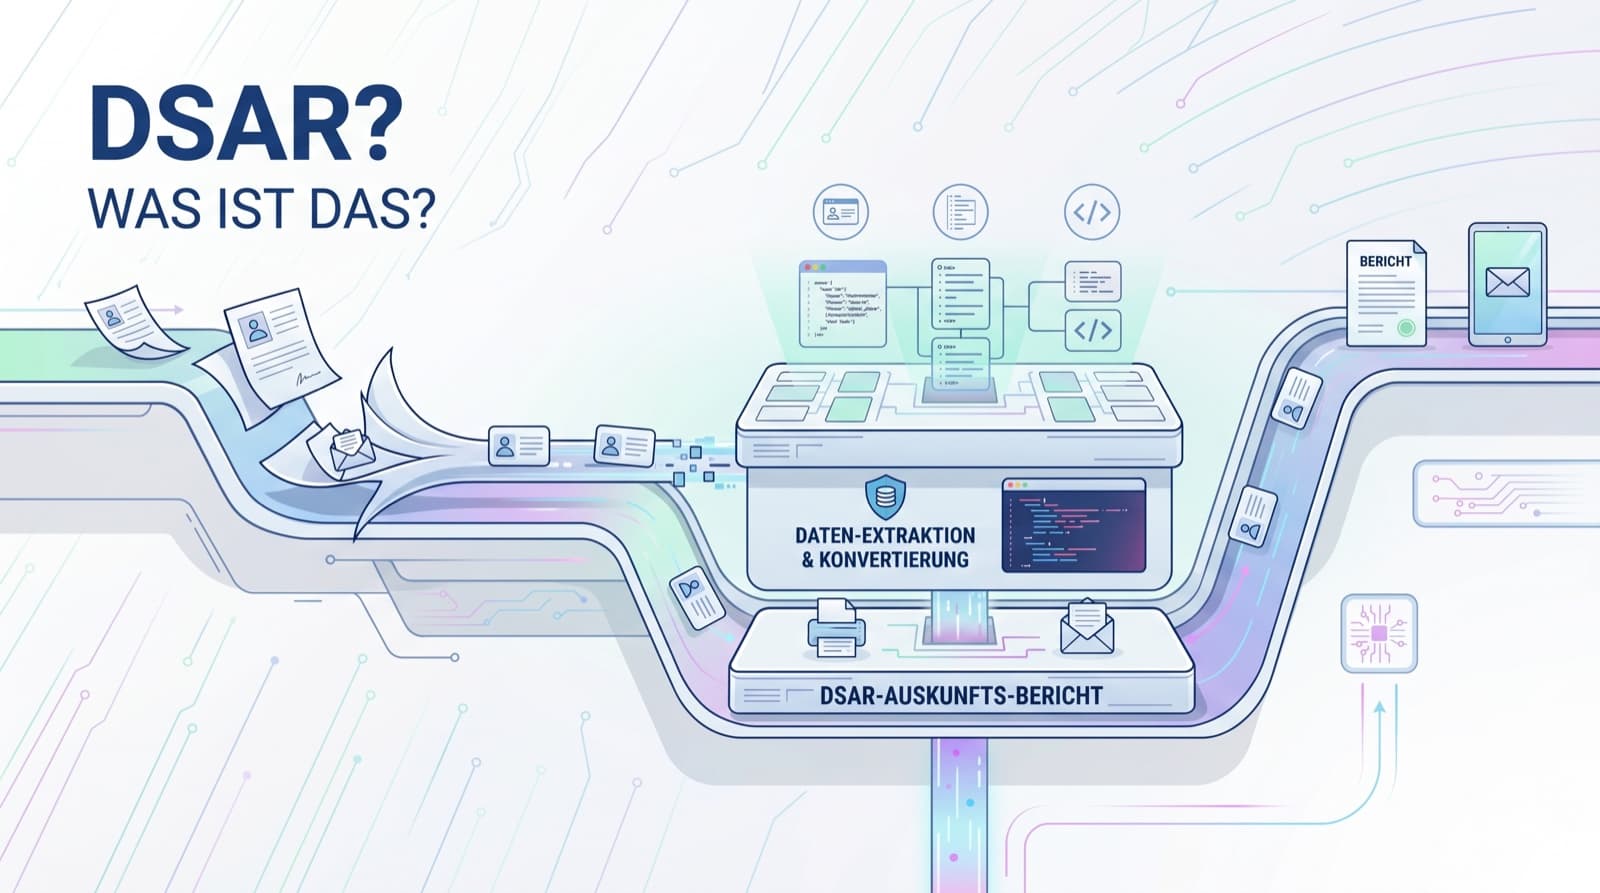
GDPR Subject Access Request: How to Answer a DSAR Lawfully
A DSAR (Data Subject Access Request) under Art. 15 GDPR must be answered within 30 days. We walk you through the 8-step workflow from identity verification to data extraction and redaction, and which grounds for refusal are legally defensible.
Julian Köhn·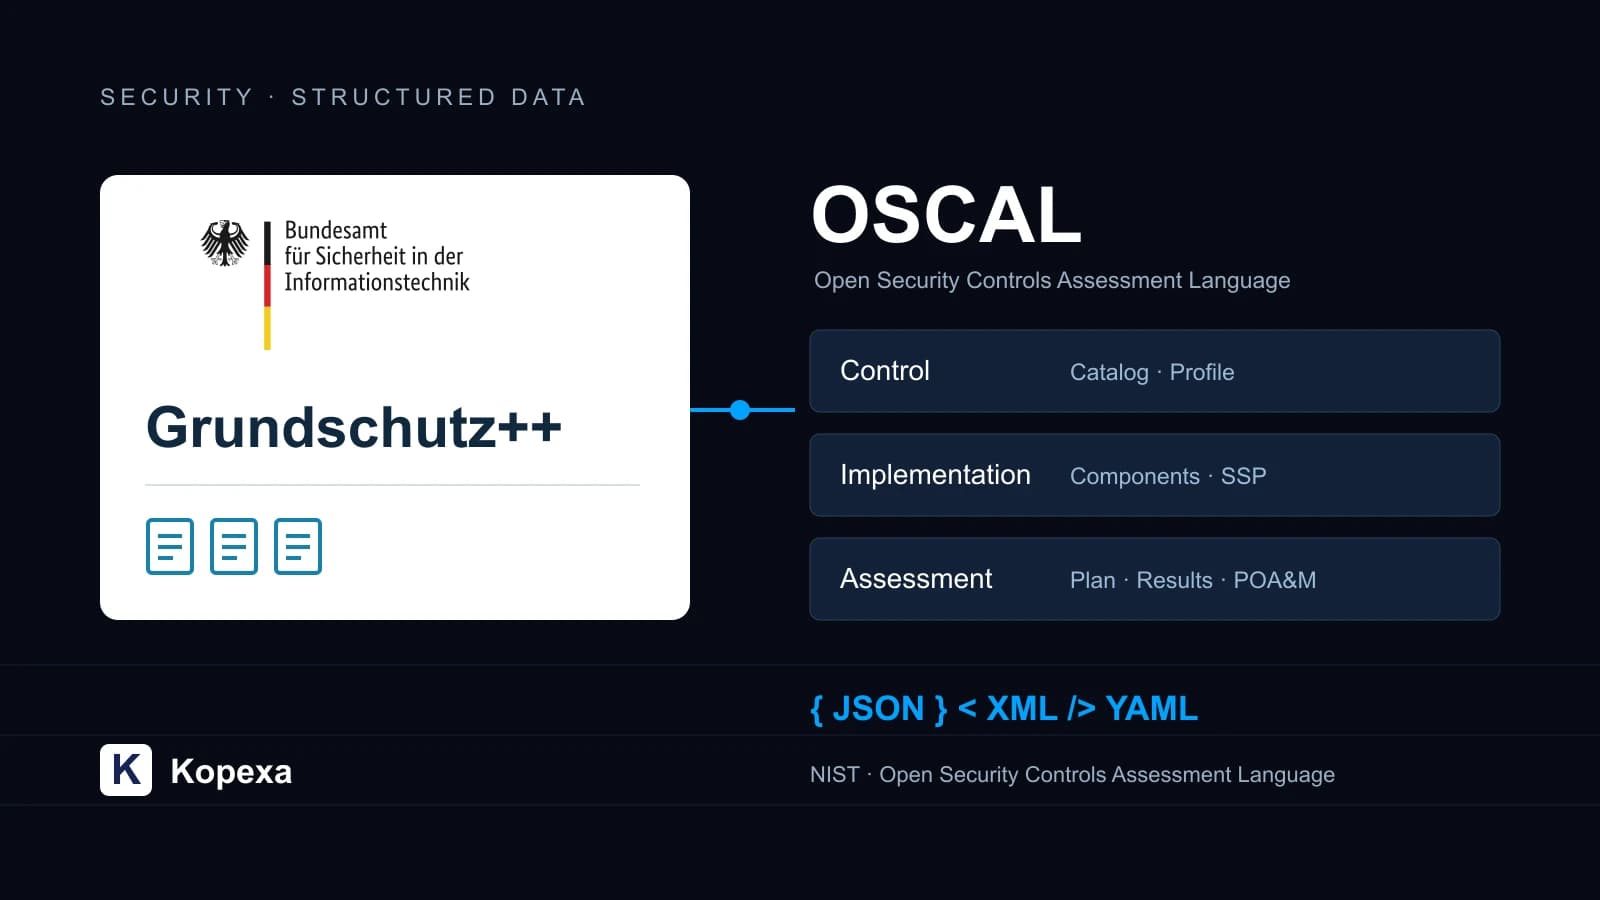
What Is OSCAL? A Deep Dive Into Compliance as Code and BSI Grundschutz++
What is OSCAL? Understand the data standard, its three layers and its relationship to BSI Grundschutz++, evidence and Compliance as Code.
Julian Köhn·NIS2 Germany: Complete Guide for International Companies (2026)
Everything an international company with operations in Germany needs to know about NIS2 / NIS2UmsuCG: who is in scope, deadlines, registration with the BSI, fines, and how DORA and KRITIS fit in.
Julian Köhn·
Third-Party Risk: Make Your Suppliers Audit-Ready
A practical guide to vendor risk management under NIS2, DORA and ISO 27001. With concrete checklists and documentation templates for your compliance team.
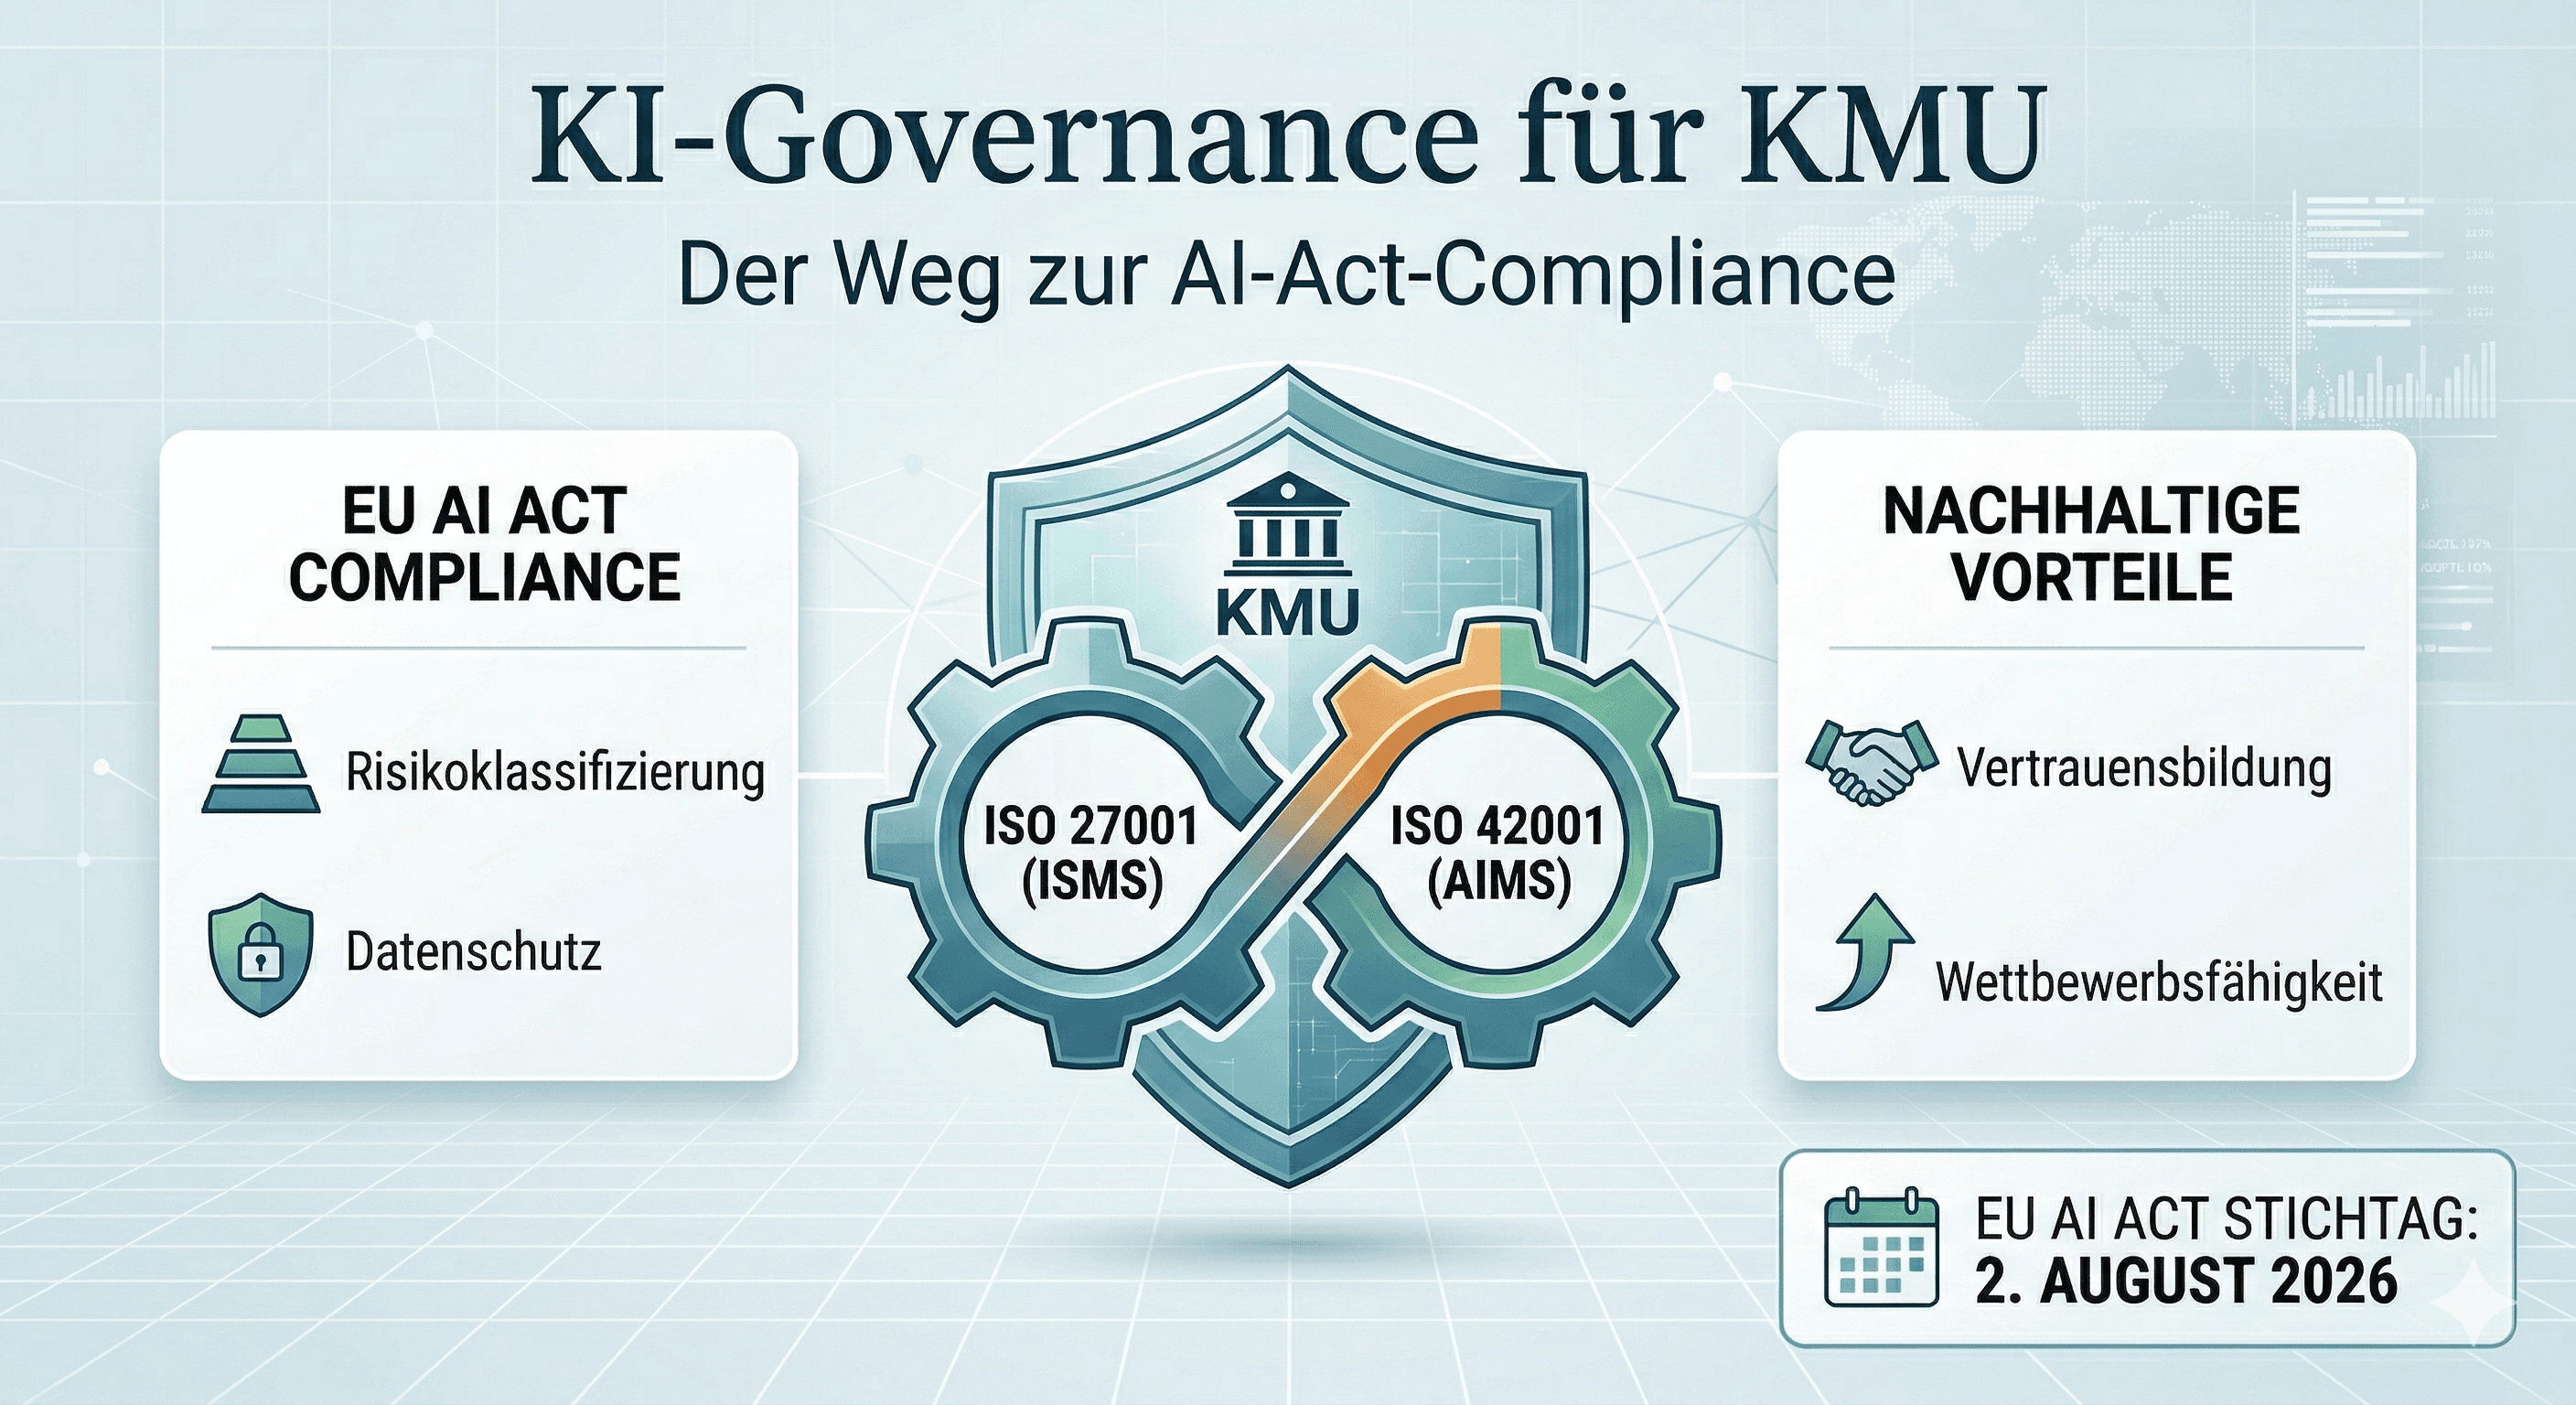
AI Governance for SMEs: The Path to AI Act Compliance
The EU AI Act will come into force in August 2026. Learn how, as an SME, you can systematically identify AI risks, integrate them into ISO 27001 and ISO 42001, and remain compliant.
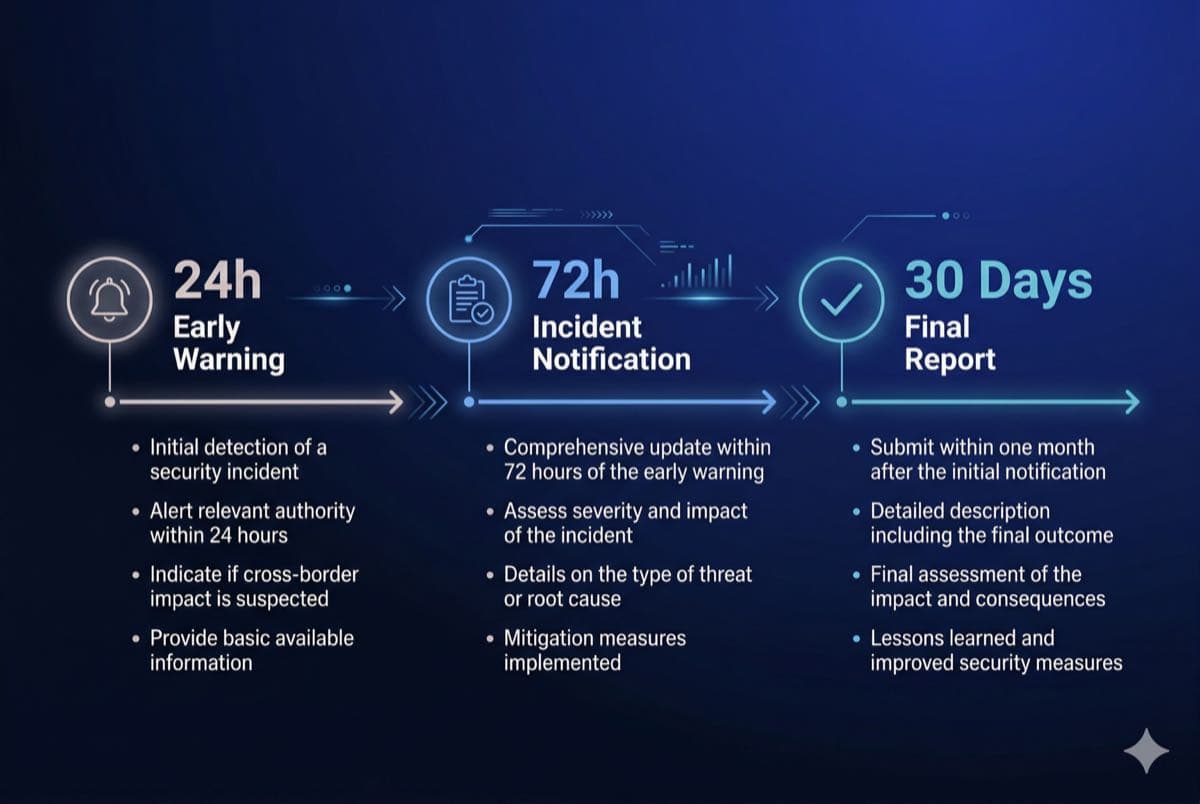
NIS2 Incident Response: The 72-Hour Reporting Obligation
Learn how to prepare your company for the new NIS2 reporting obligations and build a working incident response plan.