37–45 of 175 articles
By publication date
TISAX preparation software: Close site gaps before assessment
Choose TISAX software by testing scope, assessment objectives and measures against a customer order. Includes a site-specific test case.
 Julian Köhn·
GRC software in healthcare: Protect care delivery and recovery
Choose healthcare GRC by connecting care delivery, IT dependencies, sensitive data and practical fallback procedures during a software pilot.
Julian Köhn·
NIS2 software for SMEs: Implement with a small team and IT partner
Implement NIS2 with a limited team: choose software using ownership, external providers and a small, dependable initial scope.
Julian Köhn·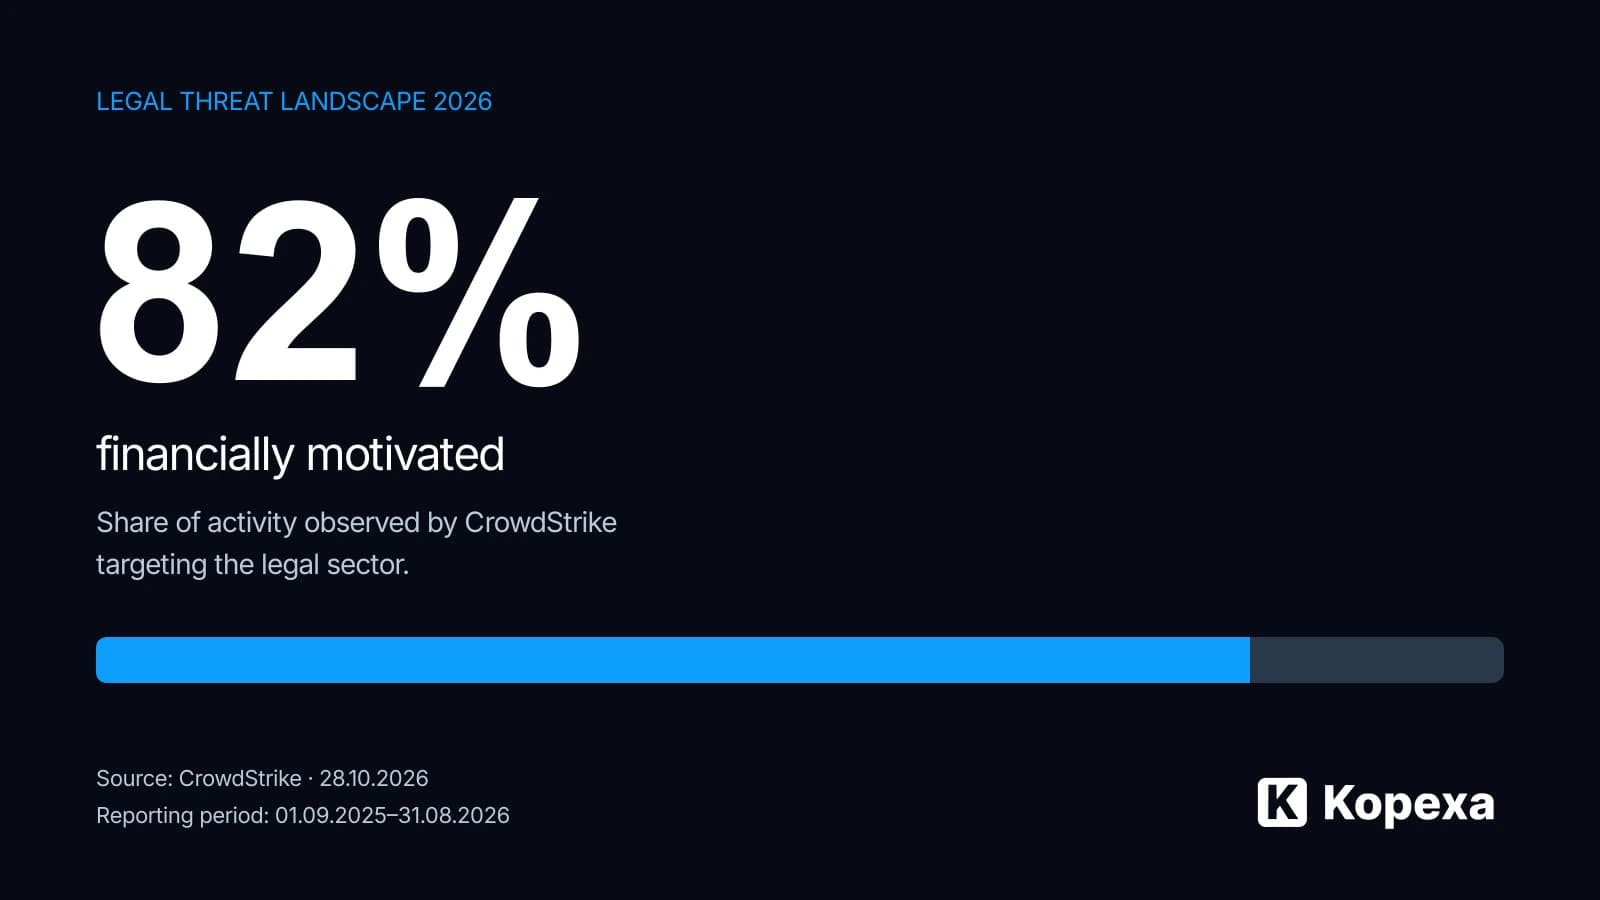
Cyberattacks on law firms: When trust opens the door
CrowdStrike reports rising attacks on the legal sector. What the figures mean and how law firms can review remote access and protect client information.
Julian Köhn·
Software for NIS2 implementation: Coordinate measures across departments
Choose NIS2 software: separate scope assessment, measures, incidents and management decisions. Includes a practical supplier test case.
Julian Köhn·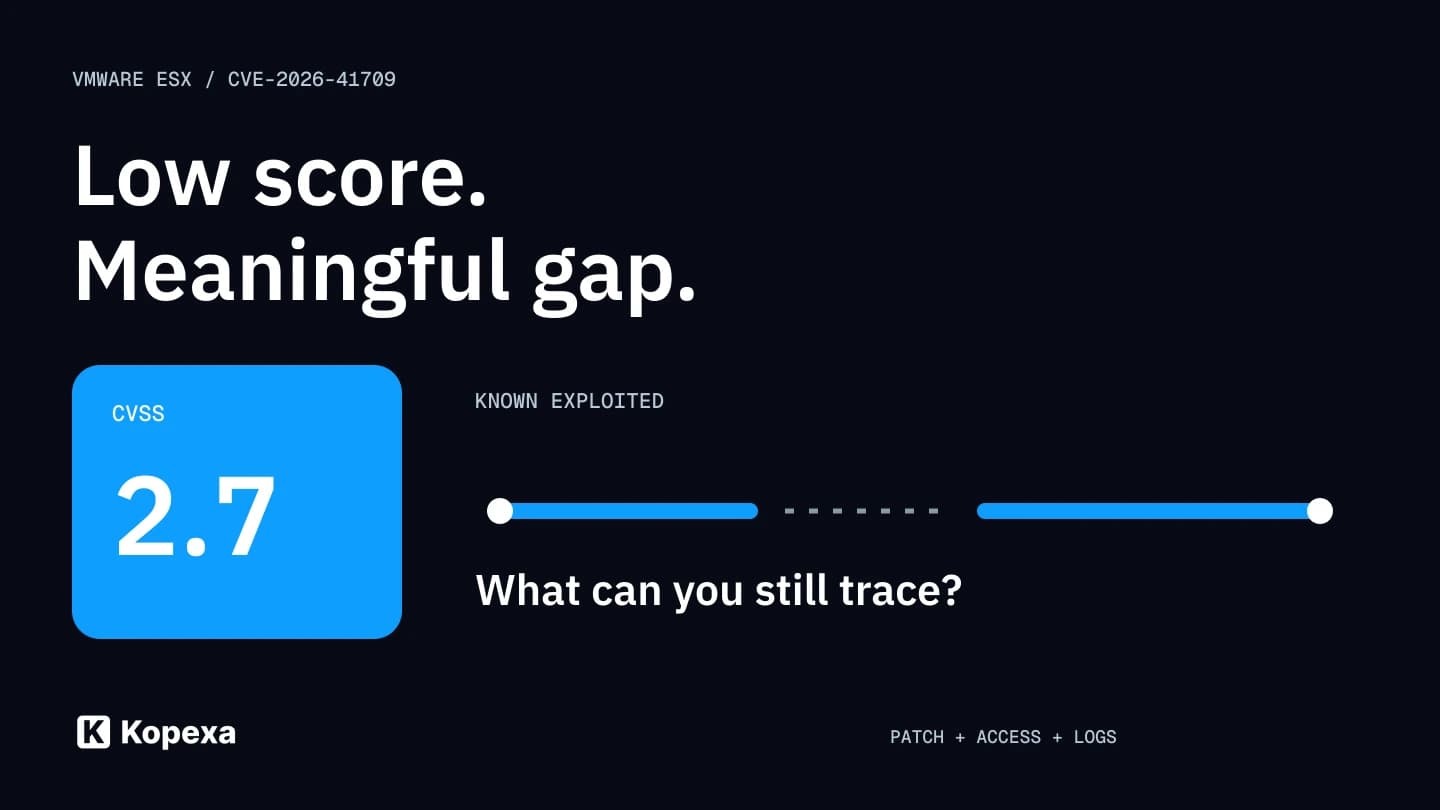
VMware ESX: CVSS 2.7, yet known exploitation
CVE-2026-41709 concerns insufficient VMware ESX logging. Why its new KEV listing matters to patch and risk owners despite the low CVSS score.
Julian Köhn·
ISO 27001 software for IT providers: Answer customer questions faster
Assess ISO 27001 software for IT providers: keep customer engagements, privileged access and shared evidence clearly scoped.
Julian Köhn·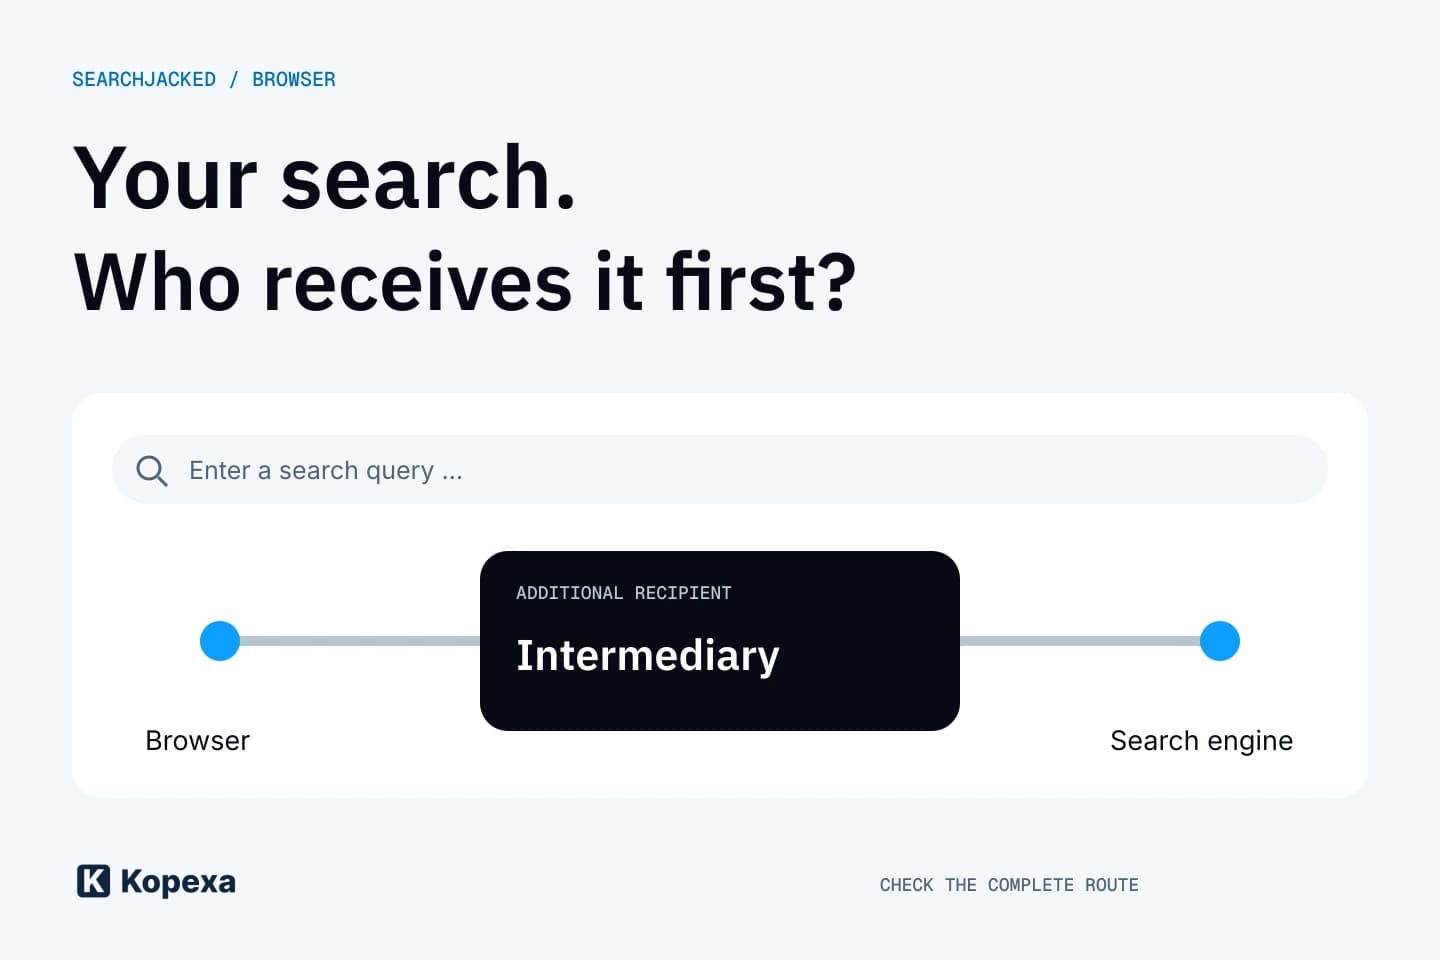
Searchjacked: When browser extensions reroute search queries
Socket reports search redirection through browser extensions. Why an official store is not enough, and how organizations can check extensions and data routes.
Julian Köhn·ISO 27001 software: Prepare for certification and close open gaps
Choose ISO 27001 software by testing scope, risk treatment, SoA and dependable evidence during a pilot, beyond comparing document templates.
Julian Köhn·