Explore the Kopexa blog
Guides & How-To
From your first ISMS to your next audit: practical guides, concrete examples and knowledge for everyday work.
11–19 of 23
Create a risk matrix: Excel template and worked example
Build an information-security risk matrix. Free Excel template with dynamic matrices, a risk register and initial and residual risk examples.
 Julian Köhn·
ISO 27001 Checklist: Step by Step to Certification
ISO 27001 checklist with about 30 checkpoints for certification and ISMS setup, every step explained, free PDF download.
Julian Köhn·
Choosing ISMS Software: Requirements Catalog & Checklist
Choosing ISMS software: requirements catalog with about 30 criteria, must-have vs nice-to-have, and a free checklist download.
Julian Köhn·
ISMS Software: Which One Helps with ISO 27001, TISAX and NIS2?
ISMS software compared: selection criteria, features and costs for ISO 27001, TISAX and NIS2. The practical guide for your decision.
Julian Köhn·
ISO 27001 Certification Explained Simply: Process & Costs
What ISO 27001 certification means, who actually needs it, and how the process runs from Stage 1 to recertification, explained clearly for beginners.
Julian Köhn·
ISO 27001 and Data Protection: GDPR, TOMs and Evidence
Does ISO 27001 cover GDPR? Understand Article 32 TOMs and follow eight practical steps, with evidence, ownership and a worked example.
Julian Köhn·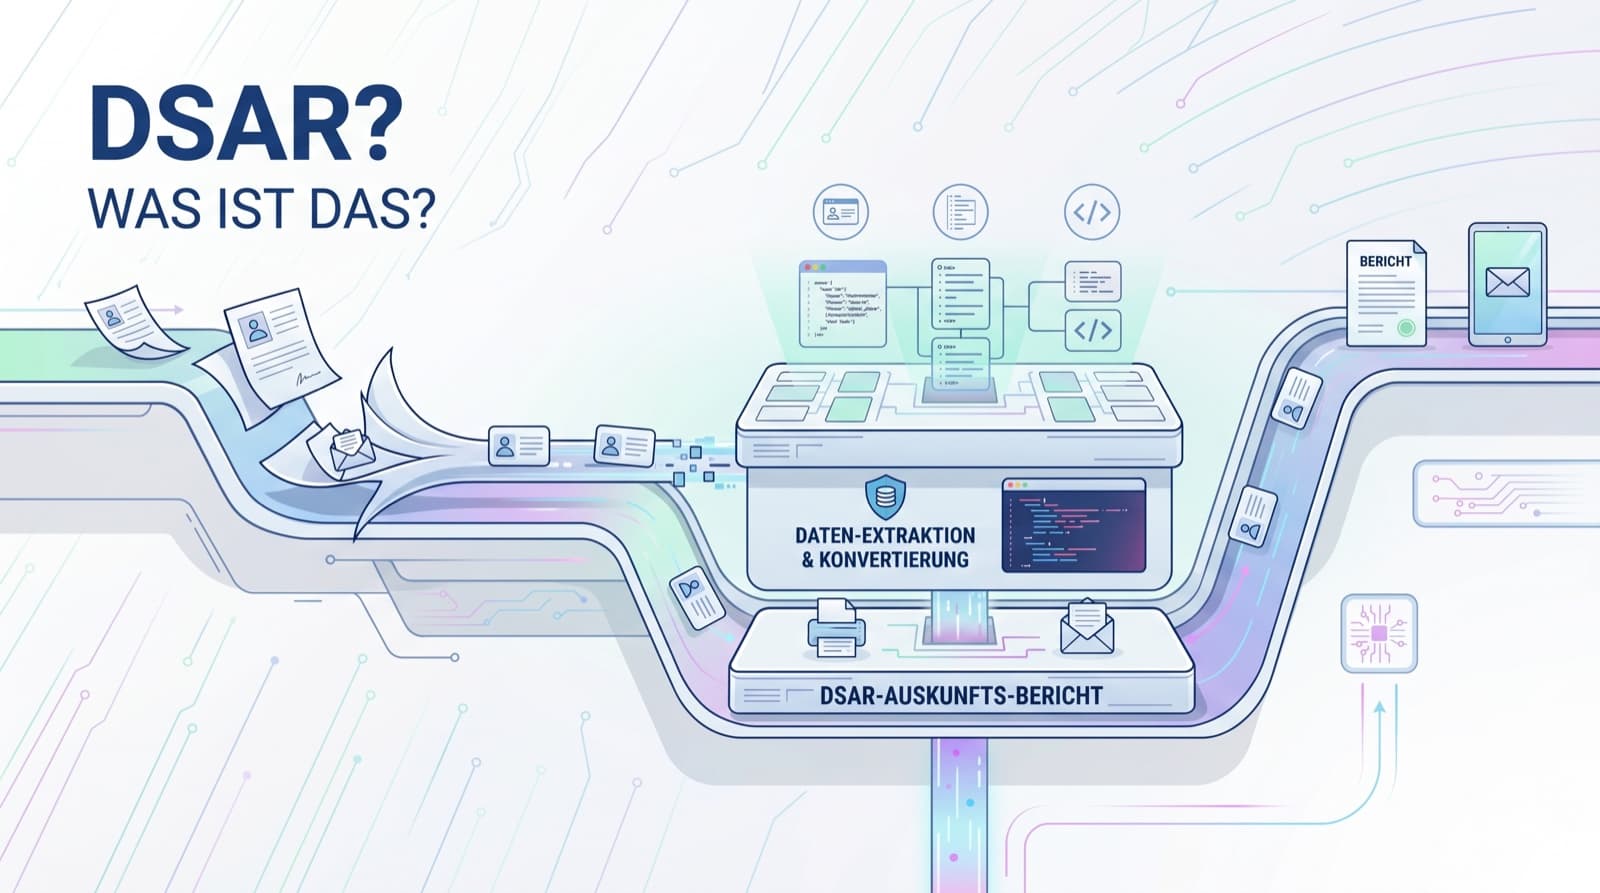
GDPR Subject Access Request: How to Answer a DSAR Lawfully
A DSAR (Data Subject Access Request) under Art. 15 GDPR must be answered within 30 days. We walk you through the 8-step workflow from identity verification to data extraction and redaction, and which grounds for refusal are legally defensible.
Julian Köhn·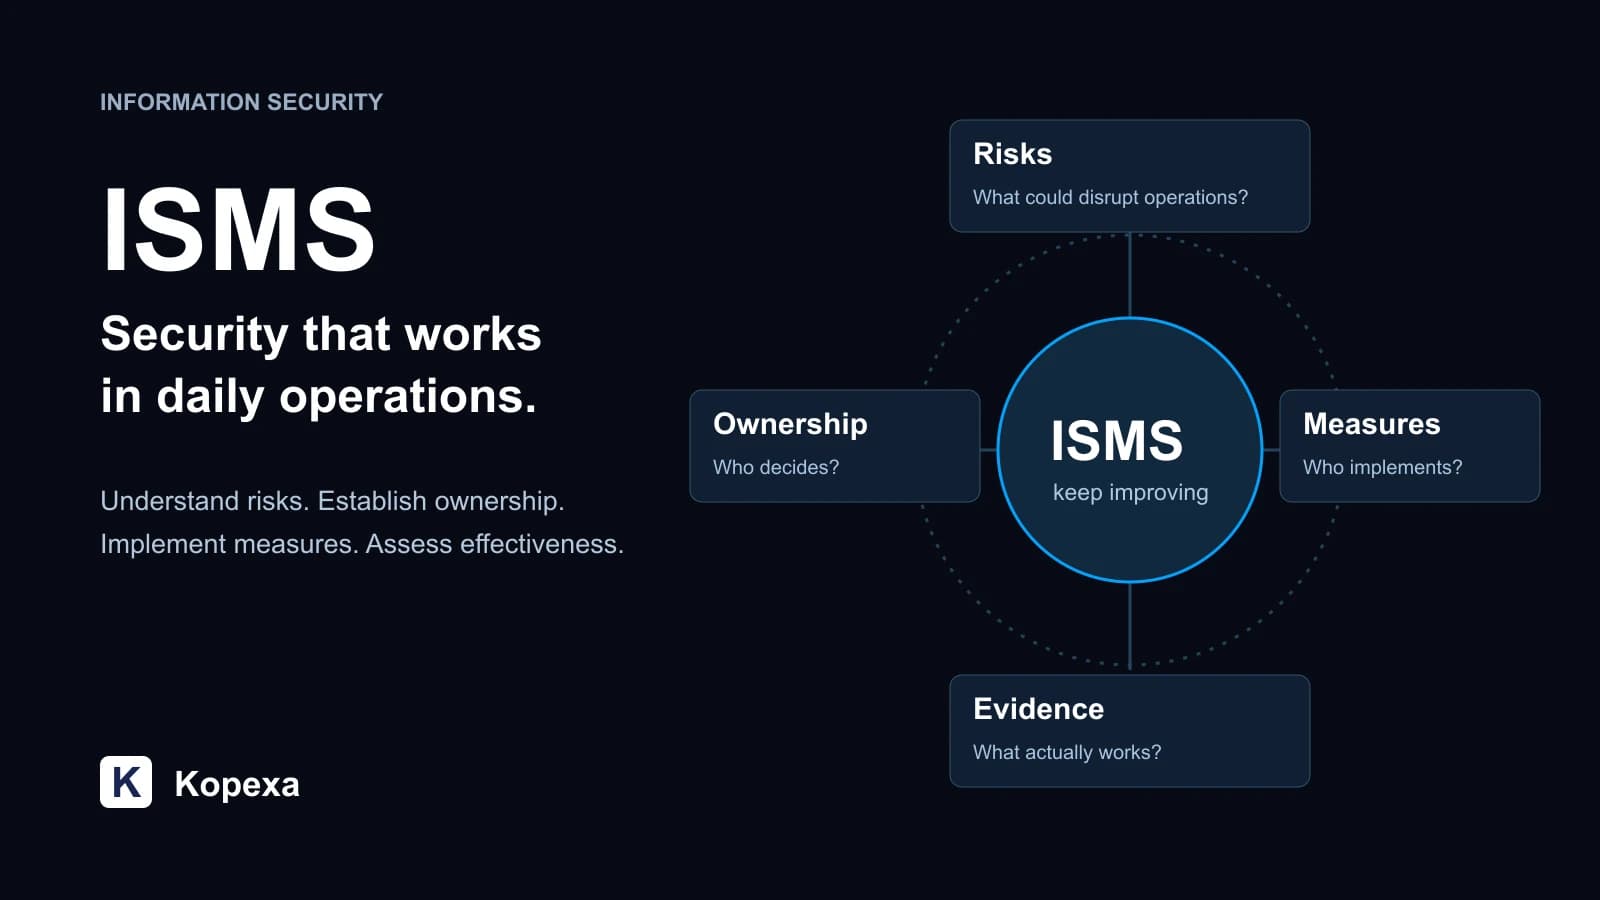
What Is an ISMS? Definition, Examples and Implementation Guide
What an ISMS is, which documents you need and how to build it: a clear definition, three examples and a practical implementation plan.
Julian Köhn·
5 Benefits of Automated Risk Analysis for Mid-Sized Companies
Learn how automated risk analysis helps SMEs detect risks early, ensure compliance and improve decision-making.
Julian Köhn·