Topic in the Kopexa blog
ISMS
Build, operate and improve an ISMS: explore guides, examples and practical answers on information security.
11–19 of 37
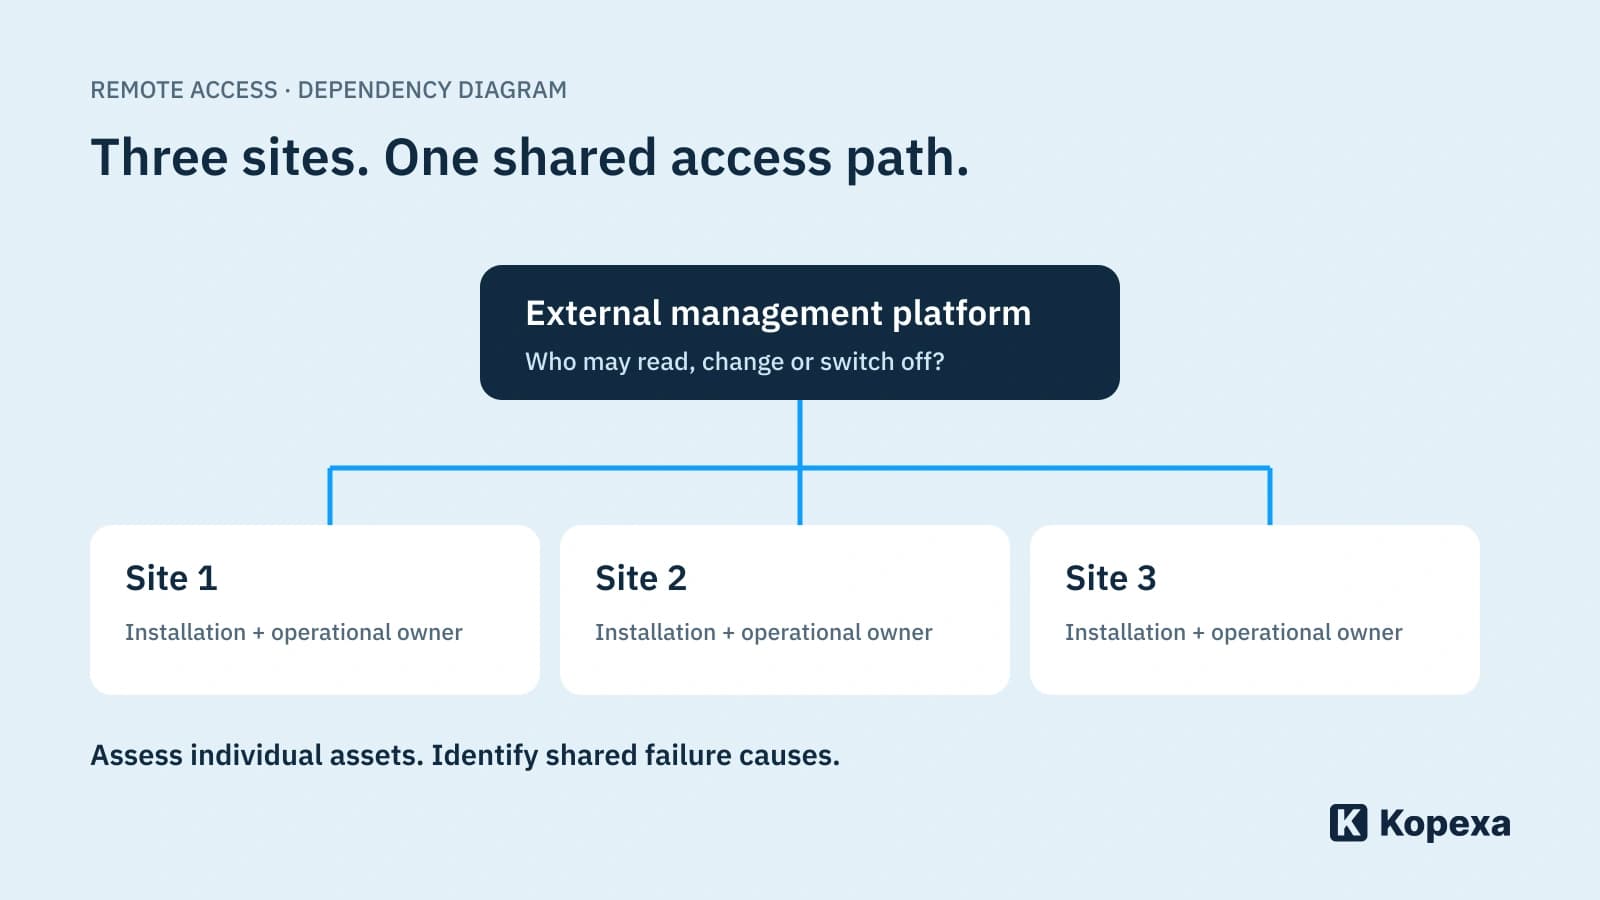
Sungrow: Who can control your equipment remotely?
The fixed iSolarCloud vulnerability illustrates an operational risk: central remote access to many installations. Review access, dependencies and fallback operation.
 Julian Köhn·
Introducing GRC software: Who takes responsibility for what?
A role model for GRC implementation: distinguish decision-makers, business owners and administrators, then test the handover to daily operations.
Julian Köhn·
ISMS risk review: When do you need to reassess?
Identify changes, new information and ineffective safeguards, review your risk assessment and keep decisions traceable.
Julian Köhn·
ISMS management review: How do you prepare decisions?
Turn ISMS reports into a basis for decisions: show action needed, resources, owners and verifiable follow-up.
Julian Köhn·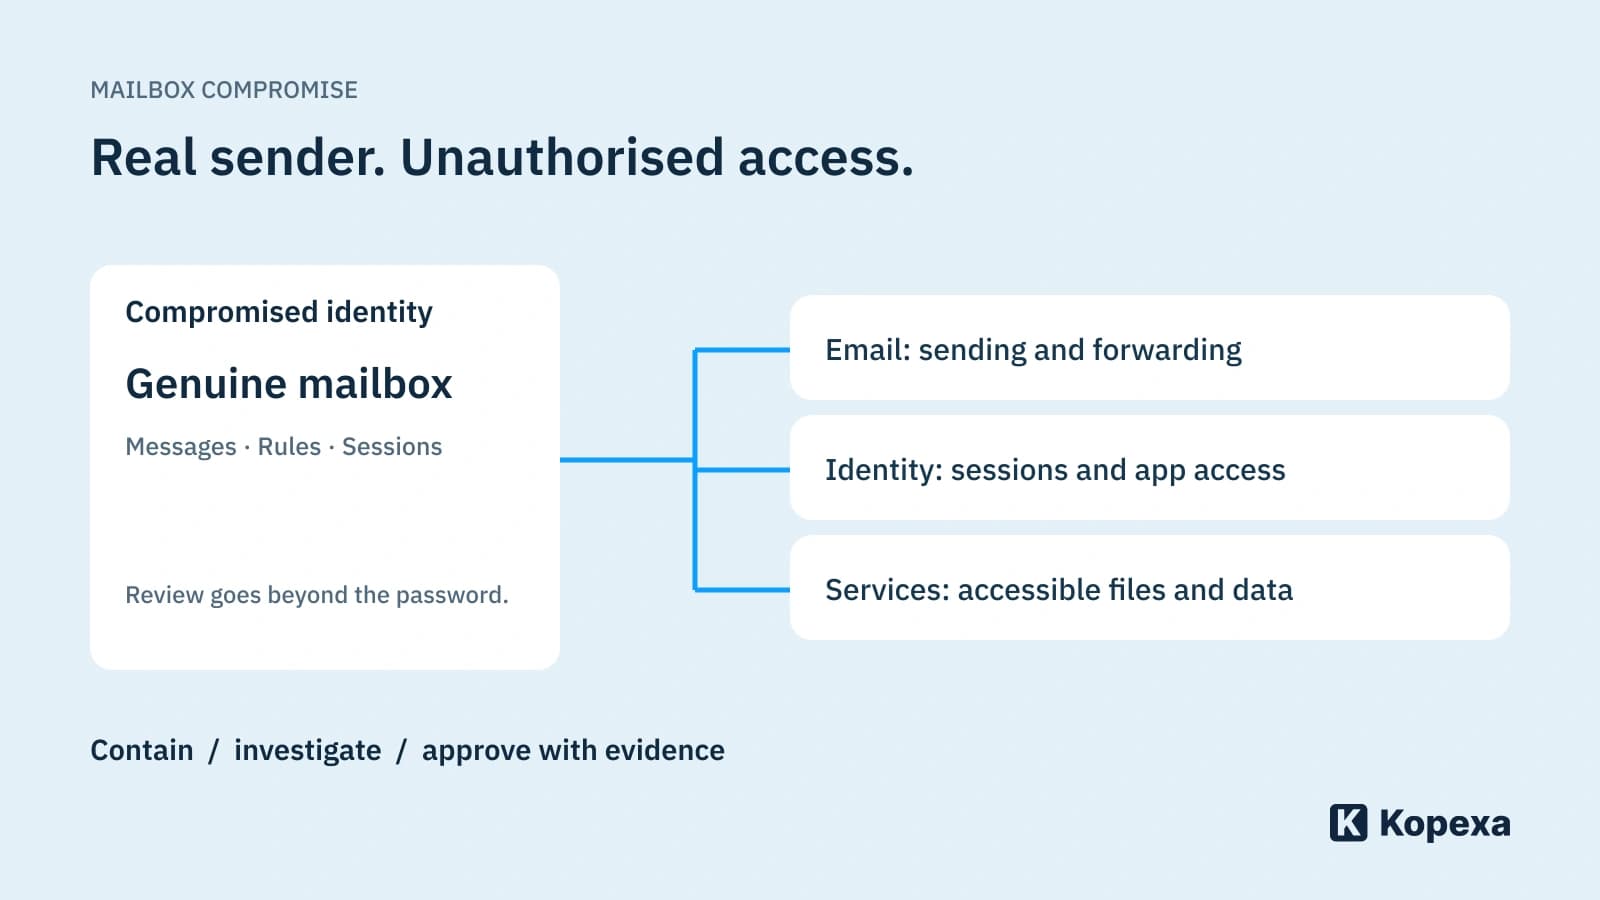
The phishing email comes from a real colleague. What now?
A compromised business mailbox makes the sender credible. Organise containment, investigation and a controlled return to work.
Julian Köhn·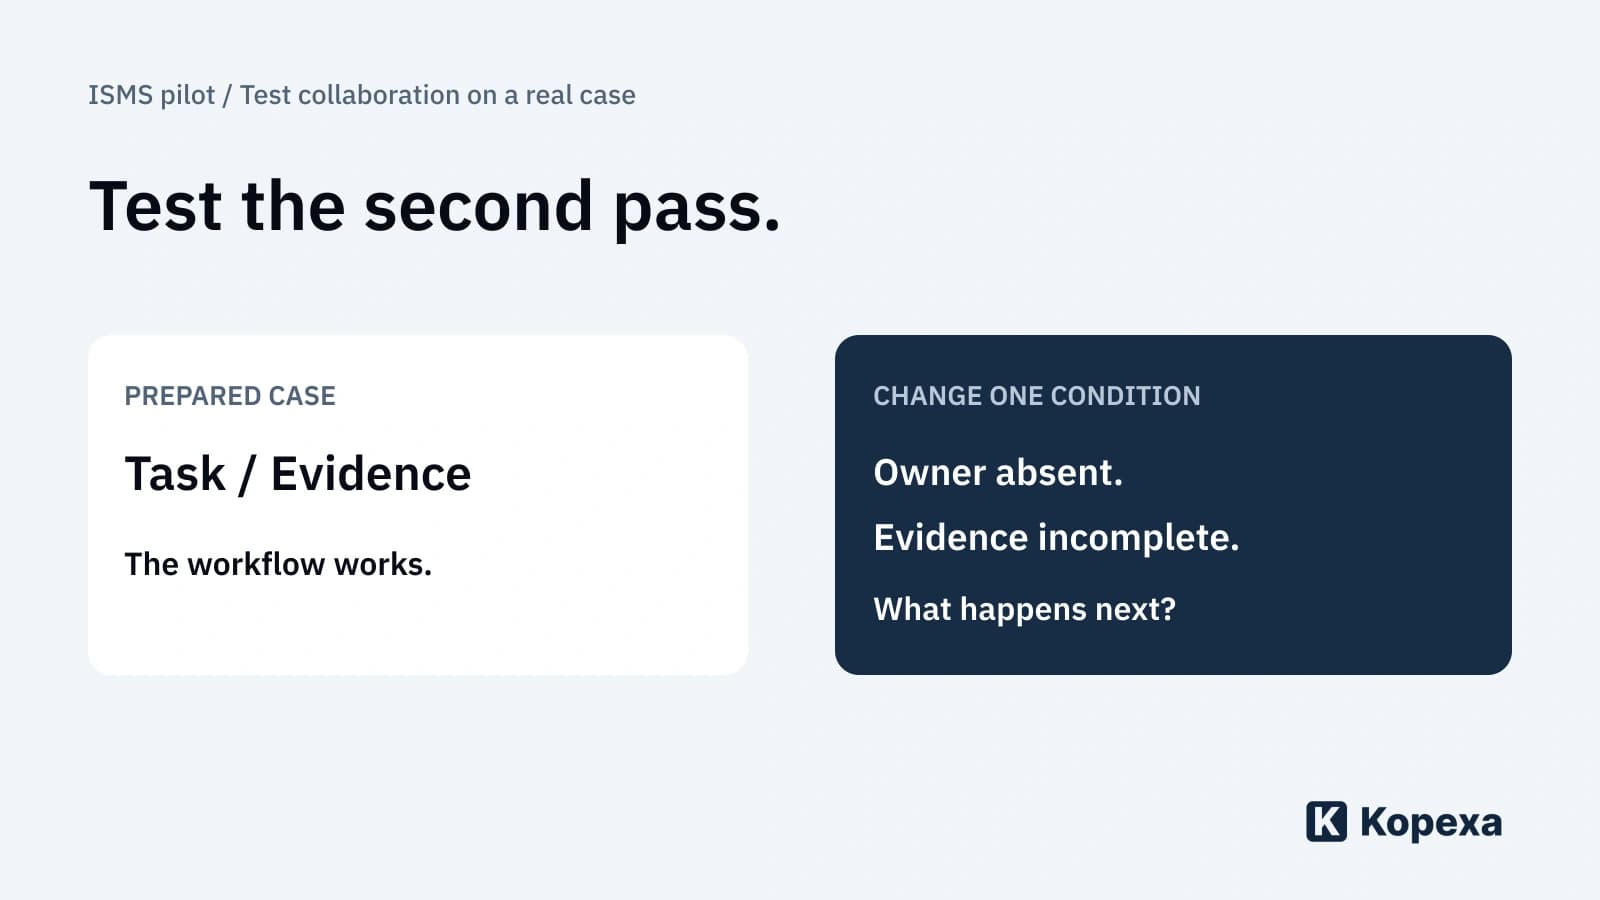
ISMS pilot project: Test the workflow, not just the interface
Assess ISMS software using a real case: hand over responsibility, replace evidence and follow an open measure through to a decision.
Julian Köhn·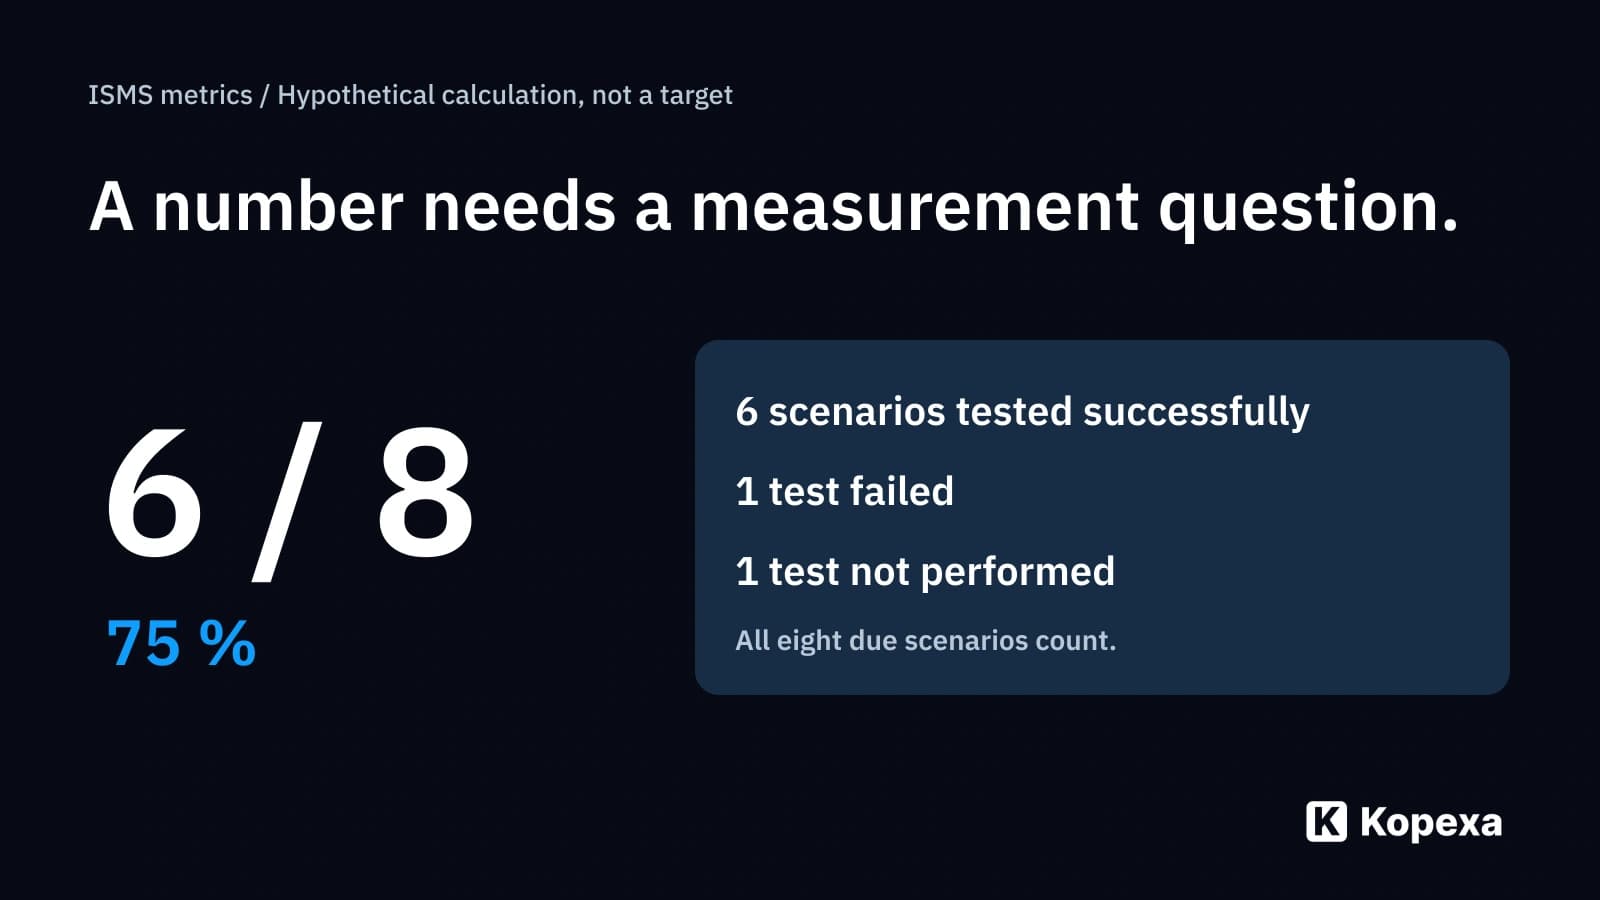
ISMS metrics: How do you measure effectiveness rather than tasks?
A green task status does not prove a safeguard works. Define ISMS metrics with a clear measurement question, data source and action rule.
Julian Köhn·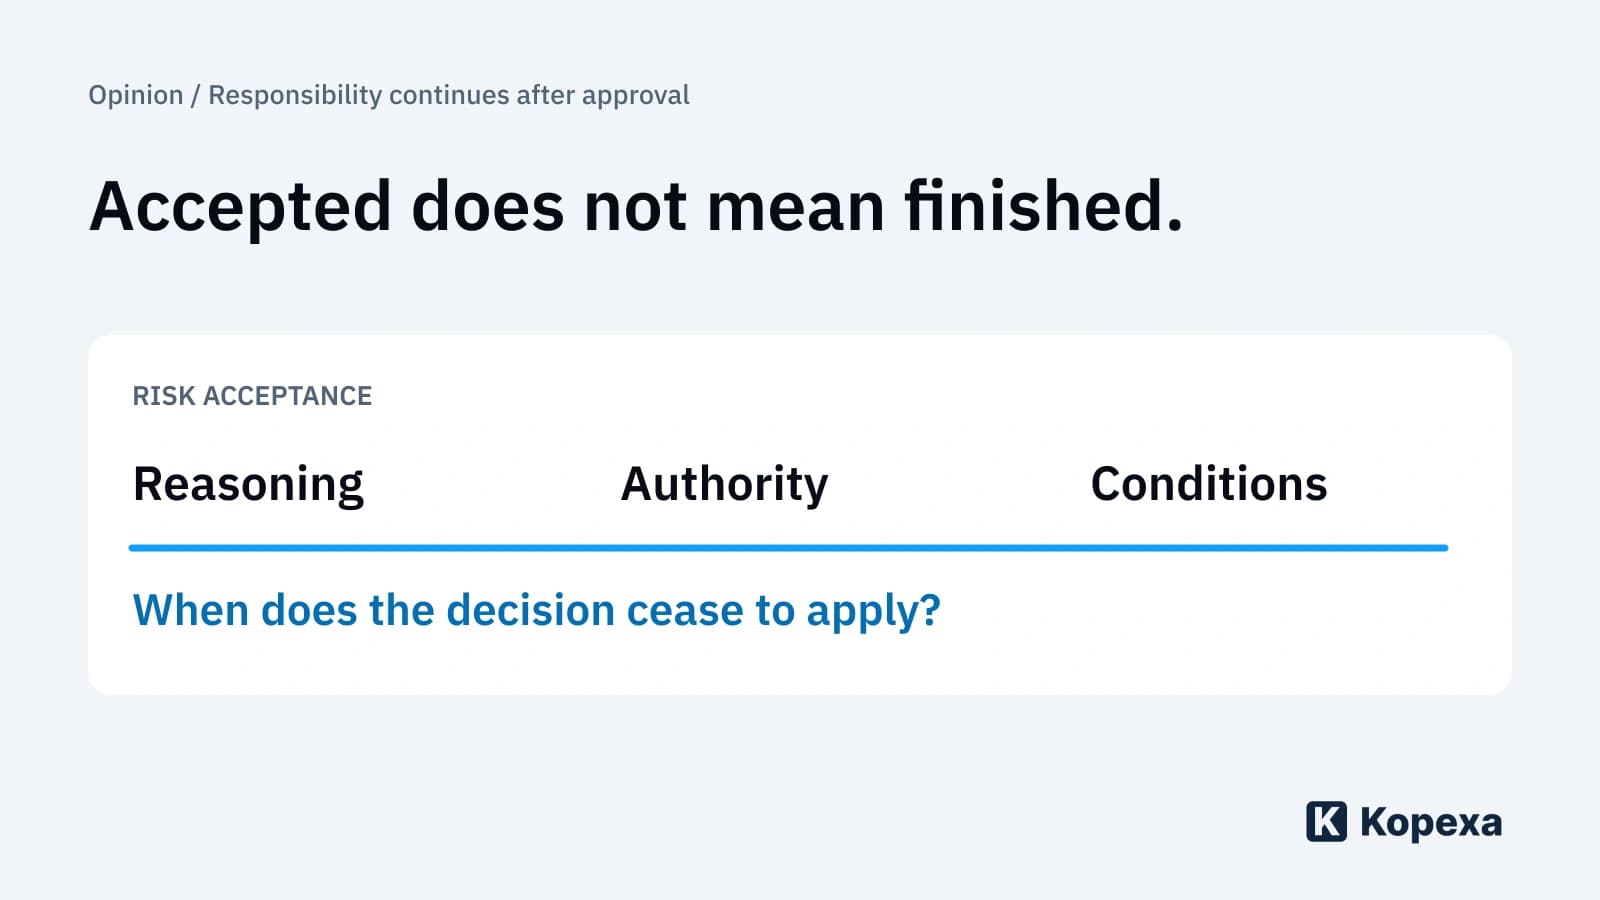
Risk acceptance: Accepted does not mean finished
An accepted risk remains a risk. Document the decision, authority, conditions and reassessment triggers so acceptance stays defensible.
Julian Köhn·
How much ongoing maintenance does ISMS software need?
Which ISMS tasks stay with your team, and what can be automated? Test evidence maintenance, policy reviews and multiple standards through a real workflow.
Julian Köhn·