Automotive · Information security & TISAX
Demonstrate security. Be ready for the next contract.
Whether you supply components, test equipment or software, customers expect you to protect their information. Kopexa helps you organise TISAX, risks and evidence while your team keeps developing and delivering.
For your first customer assessment and for an ISMS spanning multiple sites.

Cofinity-X relies on Kopexa, too.
The operating company in the Catena-X ecosystem is one of our customers. Information security connects manufacturing, engineering and digital data exchange.
From a small supplier team to an international group
Manufacturing & components
Protect drawings, production data and availability, even when IT and security are only part of your role.
Engineering & test equipment
Work with confidential customer data, measurements and development information while keeping obligations in view.
Software & data ecosystems
Manage access, cloud suppliers and customer security requirements with a traceable working record.
Day-to-day supply chain work
Your customer asks about security. You need a reliable answer.
A new contract, a customer assessment or another site: security requirements arrive on top of everyday work. Kopexa connects them to implementation.
Be ready to answer customer requests
Procurement asks for a TISAX label, a self-assessment or current evidence. Different colleagues hold the answers.
Connect requirements, measures and evidence so your team can demonstrate the current position and address open items.
Explore TISAX preparationKnow what needs to recover first after an outage
CAD data, code repositories, test benches and production depend on one another. An outage or inappropriate access can affect customer projects.
Understand dependencies between processes, assets and providers. Use the business impact analysis to assess outage consequences and prioritise measures and recovery.
Understand outage risks and recoveryKeep supply chain providers in view
An external developer, cloud service or maintenance provider accesses sensitive information. Their risks form part of your security picture.
Assess suppliers, follow up reviews and link outstanding tasks. You can also record sub-suppliers within the supply chain.
Manage supplier risksBring security rules into everyday team work
New colleagues, changing project teams and contractors handle customer information. A policy in a folder does not show whether the rules have reached them.
Provide relevant policies and training through the Workforce Hub and follow up acknowledgements. Owners can see where knowledge or evidence is still missing.
Involve people in implementation
When evidence is needed
The customer is waiting. The answer cannot depend on one colleague.
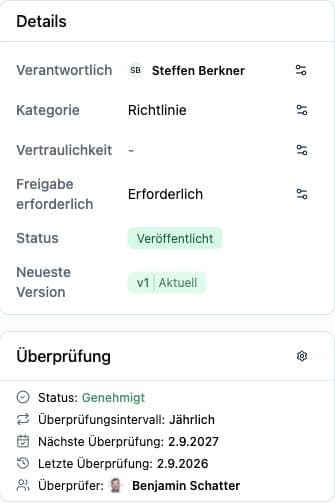
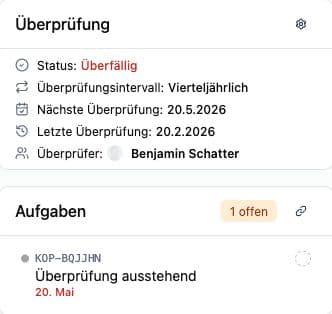
A customer assessment is approaching, but the person responsible is away. Instead of searching folders and emails, your team can see what is approved, which review is due and where an answer is still missing.
- Answer customer requests reliably when colleagues are away.
- Identify outdated evidence before the next assessment.
- Respond to open items together with clear ownership.
TISAX is a trigger. Your ISMS continues.
Address customer requirements together.
Kopexa separates requirements from measures. When your team completes a shared measure, its implementation status is automatically reflected in the linked requirements. You can create or upload custom frameworks and customer catalogues.
Automotive compliance: understand the requirements and connections ↗TISAX / VDA ISA
Prepare for assessment, address gaps and link relevant evidence.
TISAX in Kopexa ↗ISO 27001
Build on your existing ISMS and include measures already implemented.
ISO 27001 in Kopexa ↗Further requirements
Manage customer requirements, data protection and NIS2 where applicable in the same working context.
Explore frameworks ↗
TISAX assessments are conducted by ENX-approved audit providers. Kopexa supports preparation and ongoing implementation.
FAQ
What automotive teams want to know before starting
Does Kopexa work for a small supplier?
Yes. Start with the requirement at hand, such as a customer's TISAX request. Assign owners and evidence to the relevant measures. Add processes, sites and standards as needed without creating a separate document collection for each request.
Is this relevant to software and engineering providers?
Yes. Consider the information, access and services you handle for customers, including source code, development data, cloud services and external developers. Customer requirements and the assessment scope determine whether a TISAX assessment is needed and which objectives apply.
Can we build on our existing ISO 27001 ISMS?
Yes. Existing risks, policies, measures and evidence are the starting point. Bring them together with additional requirements in Kopexa and use relevant overlaps. Whether existing evidence sufficiently addresses a specific TISAX requirement still needs professional review.
Does Kopexa replace our consultant or TISAX auditor?
Kopexa is the platform for implementation and evidence management. Internal owners and external consultants can base their work on it. The independent TISAX assessment and evaluation by an approved audit provider remain separate.
More room for your next customer project
Show us where you are. See the work ahead.
Bring a customer requirement, an open measure or your current ISMS setup. Together, we will walk through how tasks and evidence connect in Kopexa.