France Travail: CNIL closes order following security improvements
France Travail has demonstrated the required security improvements. CNIL closes its order: what changed and what the decision means.
A privacy story with a different ending from another fine: France’s supervisory authority CNIL has closed its security order against France Travail. The public employment agency demonstrated the required improvements within the deadline. The announcement appeared on 8 October; the decision dates from 23 September 2026.
What the authority has decided
The CNIL announcement describes stronger authentication, active log monitoring and restricted access rights. The threatened daily penalty was not collected. That penalty is distinct from the original fine.
This is news about verified remediation, rather than a general security certification covering every France Travail system.
Why an order was issued
On 22 January, CNIL imposed a €5 million fine. Its January announcement describes an attack in the first quarter of 2024: social engineering enabled attackers to impersonate CAP EMPLOI advisers and access job seekers’ data.
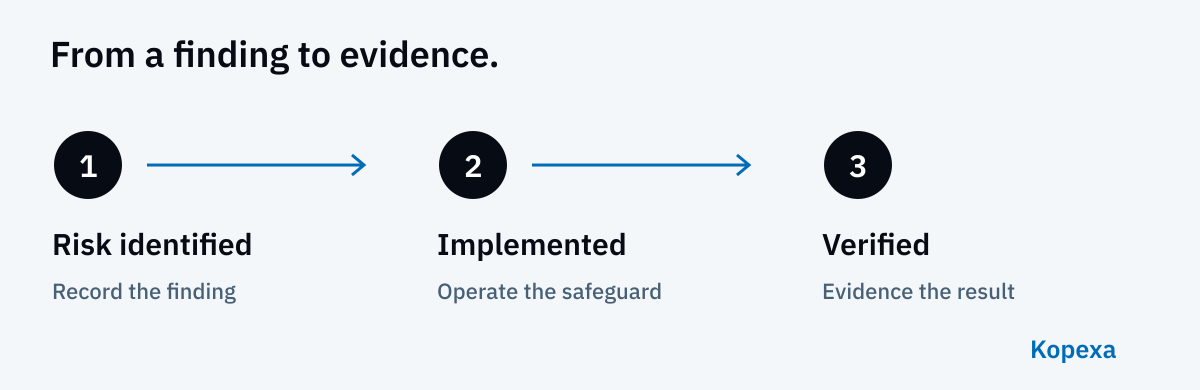
A particularly relevant finding was that appropriate safeguards had already been identified in data protection impact assessments but had not been effectively implemented. The gap lay between documented understanding and operational reality.
Which improvements enabled closure
The decision SAN-2026-013 records the improvements: CAP EMPLOI advisers’ accounts received a stronger password policy and multi-factor authentication. France Travail also improved activity-log analysis and restricted access to the data advisers needed for their work.
The case highlights a distinction that is easily lost in compliance projects: approving a measure does not mean it already works. Technically configuring it does not necessarily mean its implementation is supported by evidence an examiner can follow.
Our view: closure is part of the story
The opening of an enforcement procedure often attracts attention. Its conclusion shows here that specific remediation and supporting evidence can bring an order to an end. It does not establish general immunity or promise an outcome for other procedures.
For organisations, the useful connection is between a risk, its treatment and a verifiable result. Our article on ISO 27001 and privacy explains how information security and data protection work together. The ISMS guide covers the organisational framework.
Cover photo: France Travail Nantes Malakoff office, Kalepom, 21 March 2025, Wikimedia Commons, CC0. Archive photograph; crop and design: Kopexa.
