Explore the Kopexa blog
Guides & How-To
From your first ISMS to your next audit: practical guides, concrete examples and knowledge for everyday work.
83–91 of 93
All TISAX Labels at a Glance
The 10 current TISAX labels: confidentiality, availability, prototype and data protection. AL2/AL3 mapping and the change from Info high explained.
 Benjamin Schatter·
TISAX Prototype Protection
Physical and digital prototype security: access controls, encryption, test vehicles, and NDA management.
 Julian Köhn·
TISAX Maturity Model: Levels 0-5
The 6 maturity levels in TISAX assessments: what auditors expect at each level and how to reach Level 3.
Benjamin Schatter·TISAX Recertification After 3 Years
What happens after 3 years: re-assessment process, scope changes, costs, and tips for minimizing effort.
Benjamin Schatter·VDA ISA Catalog: The Questionnaire
VDA ISA explained: three criteria catalogues, ISA 6 chapters, must and should requirements, and the transition to ISA 2027.
Julian Köhn·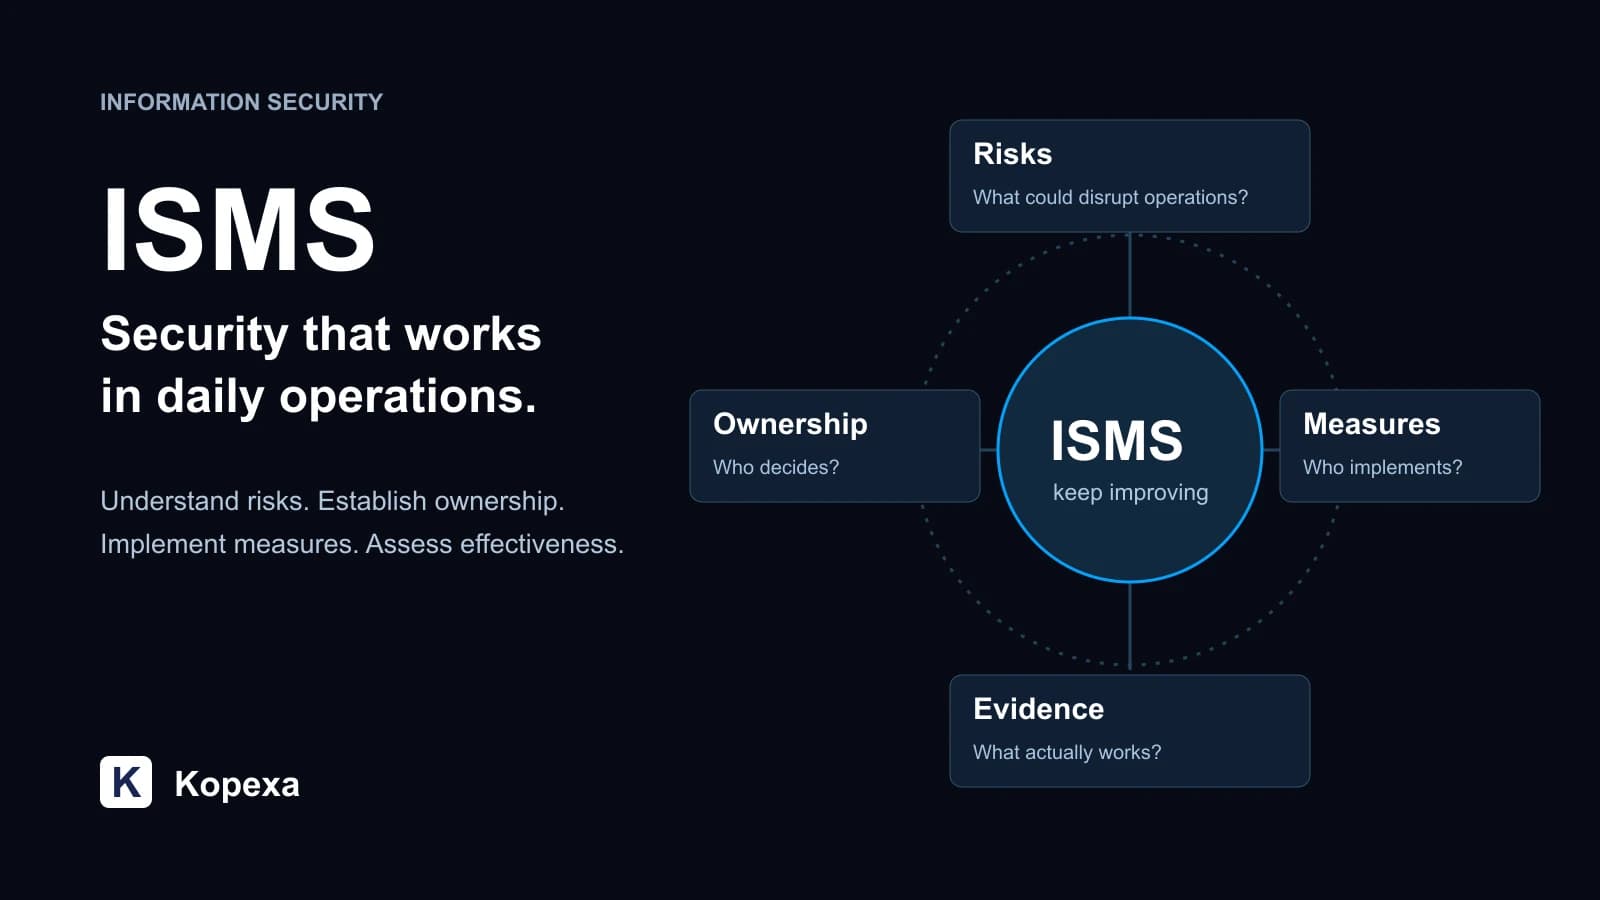
What Is an ISMS? Definition, Examples and Implementation Guide
What an ISMS is, which documents you need and how to build it: a clear definition, three examples and a practical implementation plan.
Julian Köhn·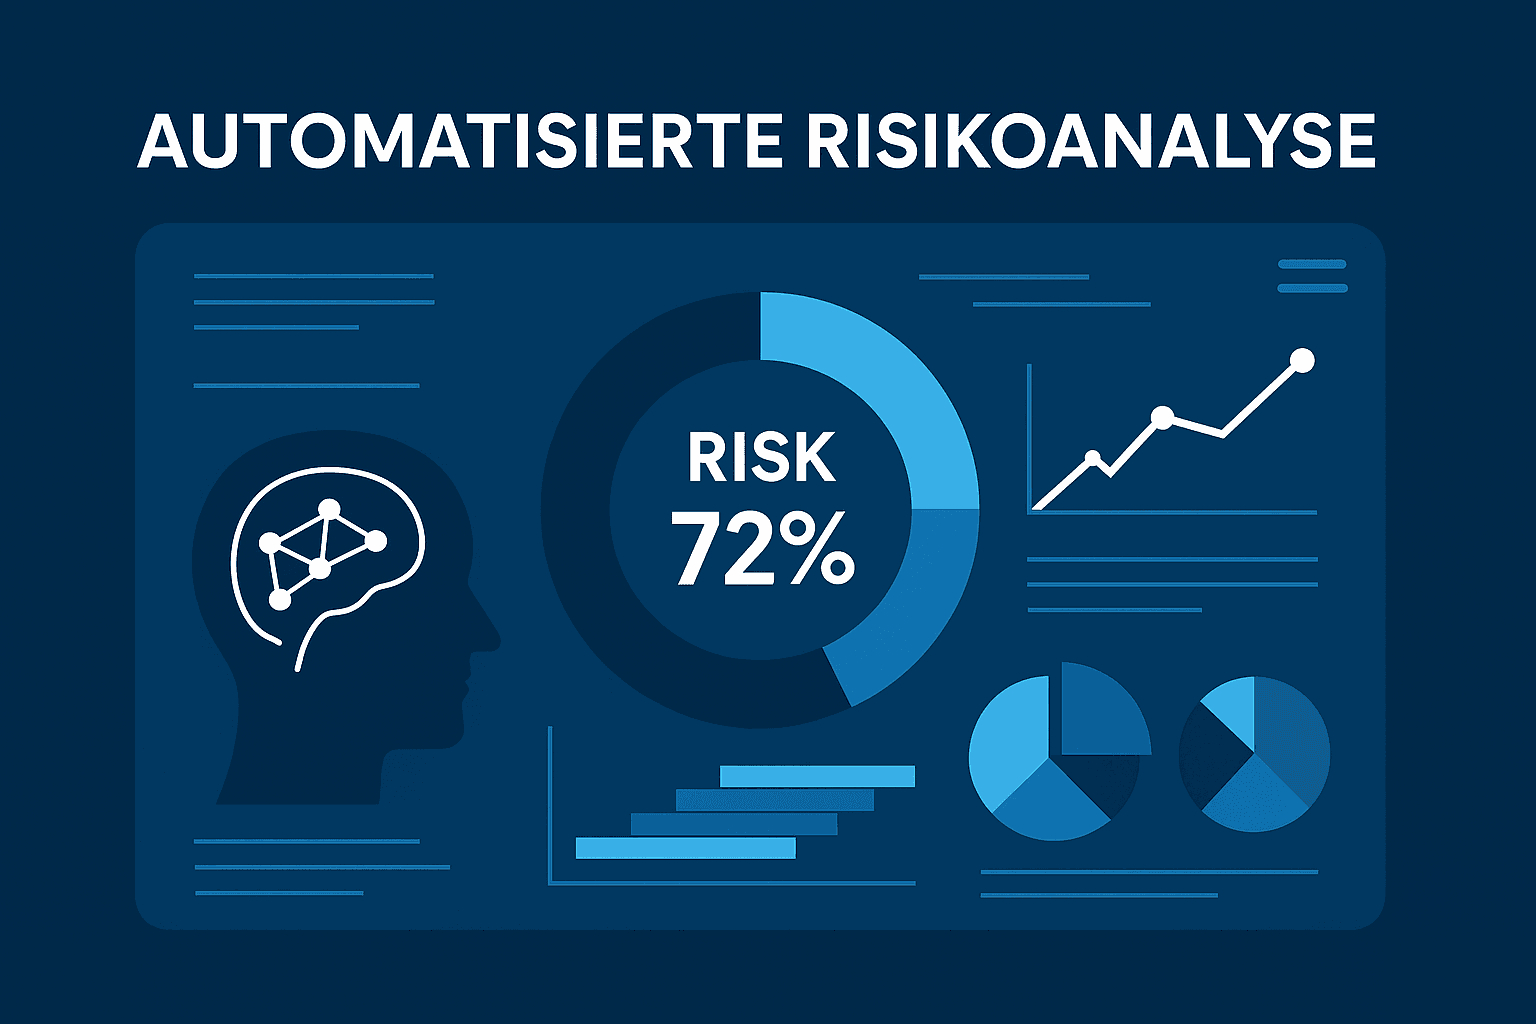
5 Benefits of Automated Risk Analysis for Mid-Sized Companies
Learn how automated risk analysis helps SMEs detect risks early, ensure compliance and improve decision-making.
Julian Köhn·
Incident Management for SMEs: What, How & Who Helps
An SME guide to what incident management is, how to implement it, plus tools, reporting obligations, and risk management with Kopexa.
TISAX Roadmap for SMEs in the Automotive Industry
Achieve the highest information security standards with TISAX certification. Your path to greater trust and competitive advantage!