Topic in the Kopexa blog
NIS2
Understand NIS2 and put requirements into practice: articles on obligations, responsibilities and handling security incidents.
11–19 of 24
ISMS Software Comparison: What Matters for ISO 27001, TISAX and NIS2?
ISMS software compared: selection criteria, features and costs for ISO 27001, TISAX and NIS2. The practical guide for your decision.
 Julian Köhn·
AI Dependency as a Compliance Risk: What the Anthropic Case Teaches Every CTO
A US decree cut off access to leading AI models overnight. Why AI dependency is a real compliance risk that belongs in NIS2, ISO 27001 and DORA.
 Nikolai Shulgin·
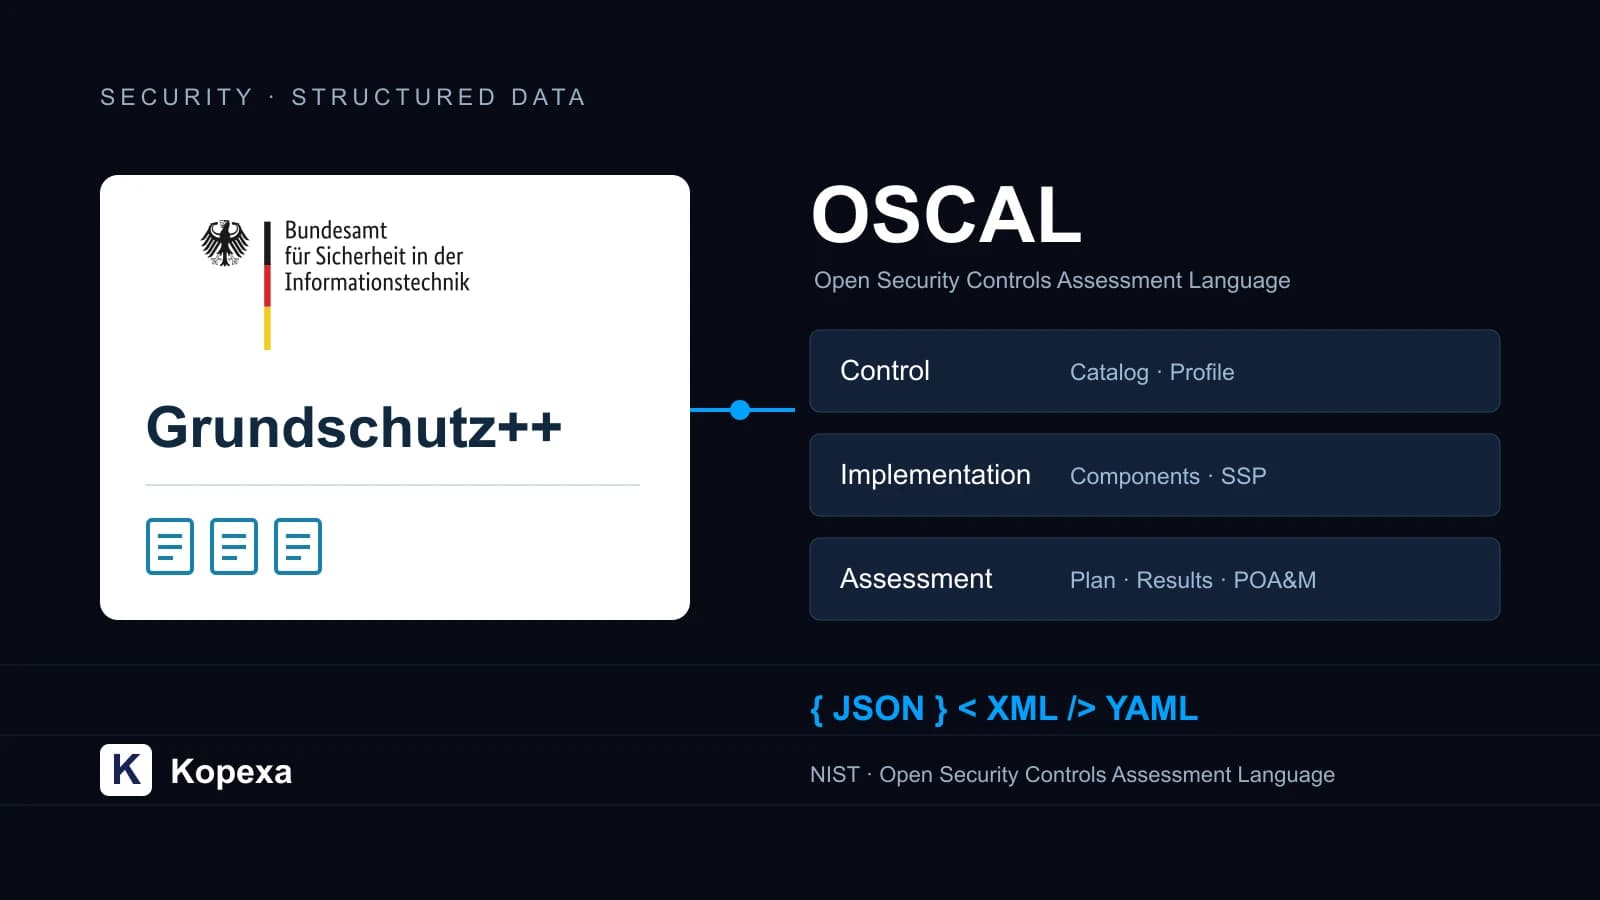
What Is OSCAL? A Deep Dive Into Compliance as Code and BSI Grundschutz++
What is OSCAL? Understand the data standard, its three layers and its relationship to BSI Grundschutz++, evidence and Compliance as Code.
Julian Köhn·NIS2 Germany: Complete Guide for International Companies (2026)
Everything an international company with operations in Germany needs to know about NIS2 / NIS2UmsuCG: who is in scope, deadlines, registration with the BSI, fines, and how DORA and KRITIS fit in.
Julian Köhn·NIS2 supply chain security: Assess suppliers and address risks
Implement NIS2 supply chain security: identify critical providers, assess evidence, review contracts and follow up findings.
 Benjamin Schatter·
NIS2 registration with BSI: Deadline, access and required information
Prepare NIS2 registration in Germany: ELSTER organisation certificate, Mein Unternehmenskonto, BSI portal and information required under section 33 BSIG.
Benjamin Schatter·NIS2 costs: Budget for software, consulting and internal work
Plan NIS2 setup and ongoing costs around your security gaps, internal capacity, software and required expert support.
Benjamin Schatter·
Third-Party Risk: Make Your Suppliers Audit-Ready
A practical guide to vendor risk management under NIS2, DORA and ISO 27001. With concrete checklists and documentation templates for your compliance team.
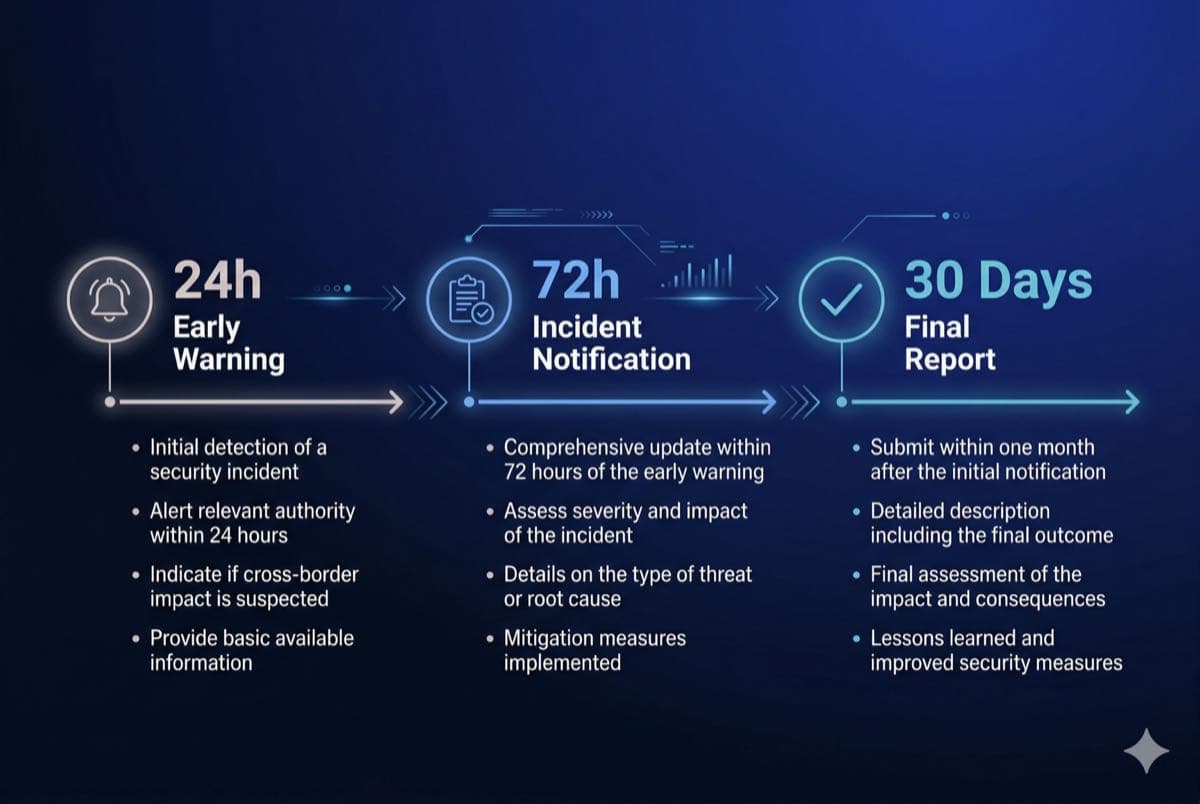
NIS2 reporting: 24 hours, 72 hours and the final report
Report NIS2 incidents in Germany: assess significance, meet section 32 BSIG deadlines and prepare a reliable incident response process.