Guide
TISAX ISA2027: Prepare your supplier security review
Does supplier evidence cover the service you actually buy? Prepare for ISA2027 with a practical review example and a change register.
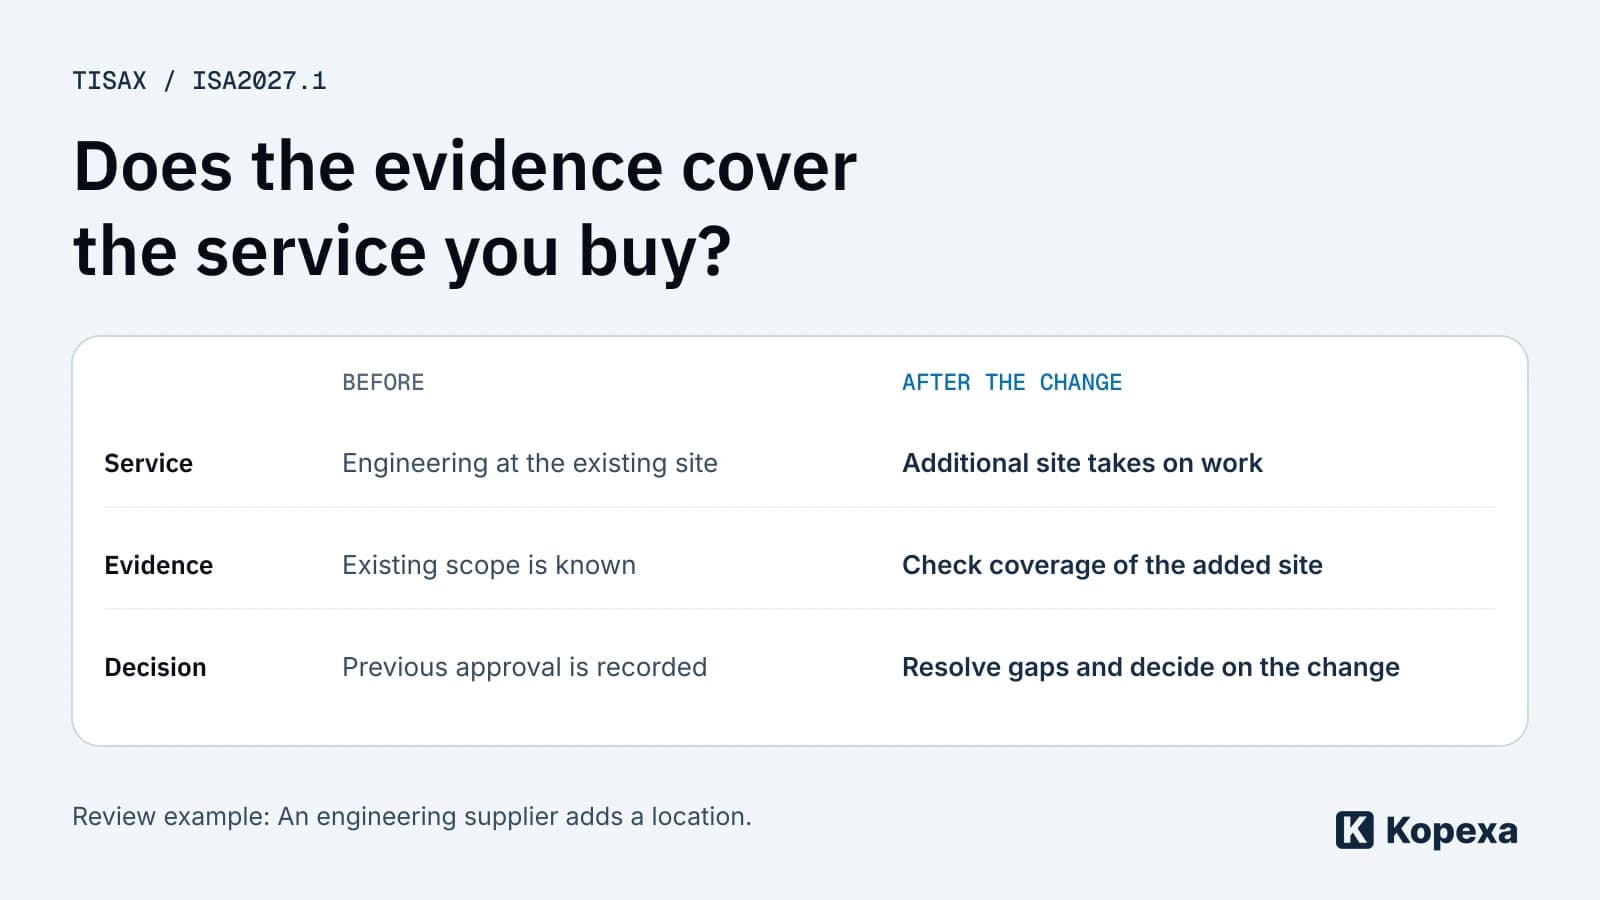
A supplier has security assurance. Does it cover the service you buy today? Ask that question before your next TISAX assessment. Check more than the presence of a file: establish whether the evidence covers the information, locations and services involved.
This guide gives you a working approach to the version change: compare requirements, identify missing evidence and assign responsibility for changes. The template and example are our recommendations, not additional ENX requirements.
Which version applies to your assessment?
According to ENX, ISA2027 applies to assessments ordered from 1 January 2027. Existing labels retain their validity; annual catalogue releases do not mean annual reassessments.
The VDA publication identifies German and English version 2027.1 as available since 1 October 2026. The update from 2027 to 2027.1 is editorial. English remains authoritative.
Record the commissioned version and assessment start with your audit provider. The ENX timeline identifies March as the final point for opening an initial assessment under the previous version. This is not a blanket extension of the ordering deadline. Resolve your specific transition case before basing preparation or scheduling on it.
What should you examine in supplier reviews?
Control 6.1.1 of the English catalogue distinguishes requirements by protection need. For high protection needs, it includes documented, regular and change-triggered reviews of evidence and contractual compliance. For very high protection needs, it identifies TISAX, equivalent third-party assessments or appropriate supplier audits as assurance routes.
Start with the service and information assets involved. A general inventory of supplier certificates does not answer the important questions.
- Which information can the supplier access or modify?
- Which of its services does your operation depend on?
- Which legal entity, sites and subcontractors deliver that service?
- What does the evidence establish, and what remains unresolved?
Mapping to another standard does not replace this assessment. Evidence must cover the relevant service and security requirements.
A review example: An engineering partner adds a site
Fictional example: An engineering provider processes confidential design data. Procurement holds valid security assurance. The provider now plans to deliver part of the work from an additional location.
The existing document does not automatically become worthless. However, it may not establish whether the new site is included. Procurement clarifies the service change. The business owner identifies the affected data. Information security reviews the evidence coverage and any unresolved safeguards.
| Review area | Specific question | Record the outcome |
|---|---|---|
| Service | What work will the additional site perform? | Defined service scope |
| Information | Which design data will it process? | Assigned protection need |
| Evidence | Does the assurance cover the site and service? | Confirmed coverage and gaps |
| Contract | Do agreements and downstream requirements still fit? | Required changes and ownership |
| Decision | Under which conditions may the change proceed? | Decision, responsible roles and review trigger |
Turn missing evidence into a specific request. “Supplier reviewed” would be too vague. A useful entry is: “Coverage of the new site unresolved; evidence requested; decision required before data transfer.” Decision authority depends on your organisation and applicable agreements.
Use a change register instead of creating a second ISMS
Compare the new catalogue with your existing working basis. Do not turn every row into a new task. First identify existing measures that fit and where the implementation, evidence or process needs to change.
Use this template for the comparison:
| Field | What to record |
|---|---|
| Requirement | Catalogue version, control and relevant requirement |
| Applicability | Service, site, information asset and protection need |
| Existing implementation | Measure and supporting evidence |
| Gap | Specific unresolved question or missing implementation |
| Next action | Request, review, change or close with a reason |
| Responsibility | Action owner and decision-making role |
| Date and trigger | Due date and circumstances requiring another review |
| Outcome | Dated decision with supporting evidence |
Try the register with one supplier. If another person can understand the case without searching through email, the structure is useful. Then extend it to other relevant relationships.
What about prototype protection?
The VDA describes a restructured prototype protection module. Check existing mappings against the current catalogue instead of carrying forward old control numbers. The ENX overview highlights traceability and end-of-life handling of protected parts.
For a practical check, follow one protected component: who received it, where is it now, and who confirms its return or disposal? Find the answers in your actual workflow. Assign gaps to a responsible role and the relevant customer requirement. Our TISAX prototype protection guide covers the foundations.
What should you do next?
Confirm the version and schedule with your audit provider. Then take one relevant supplier through the process, from service scope to a documented decision. This helps distinguish a missing document from a process that needs to change.
If requirements, measures and evidence are scattered across tools, use that case in a software demonstration: find an open requirement, connect the existing measure and locate the relevant evidence.
Quick answers
Frequently Asked Questions
Still have a question? Find the answers here.
When does ISA2027 apply to TISAX assessments?
ENX specifies 1 January 2027 for newly ordered assessments. For transition cases, confirm the catalogue version and assessment start with your audit provider.
What is the difference between ISA2027 and ISA2027.1?
According to the VDA, the update to 2027.1 is editorial and does not change the substantive requirements. The German edition has been available since 1 October 2026. The English version remains authoritative.
Does every supplier need a TISAX label?
There is no blanket answer. Review protection needs, the service, applicable requirements and contractual obligations. Control 6.1.1 distinguishes assurance routes; the adequacy of specific evidence must be assessed for the individual case.
What belongs in a version-change register?
A practical structure covers the requirement and version, applicability, existing measure and evidence, gap, next action, responsibility, due date and documented outcome. This is a working template, not a prescribed ENX form.
Sources
- ENX: 10 Years of TISAX – VDA ISA2027 Released — ENX Association () [Accessed ]
- VDA: Information security – ISA2027.1 — VDA [Accessed ]
- VDA ISA 2027.1, English catalogue, control 6.1.1 — VDA / ENX [Accessed ]
- ENX: Information Security Assessment – Versioning and Timeline — ENX Association [Accessed ]