Explore the Kopexa blog
Guides & How-To
From your first ISMS to your next audit: practical guides, concrete examples and knowledge for everyday work.
65–73 of 93
Create a risk matrix: Excel template and worked example
Build an information-security risk matrix. Free Excel template with dynamic matrices, a risk register and initial and residual risk examples.
 Julian Köhn·
ISO 27001 Checklist: What Is Missing Before Your Audit?
Use this ISO 27001 checklist to identify gaps before your audit and plan the next steps towards certification. Includes a free PDF download.
Julian Köhn·
Choosing ISMS Software: Requirements Catalog & Checklist
Choosing ISMS software: requirements catalog with about 30 criteria, must-have vs nice-to-have, and a free checklist download.
Julian Köhn·
ISMS Software Comparison: What Matters for ISO 27001, TISAX and NIS2?
ISMS software compared: selection criteria, features and costs for ISO 27001, TISAX and NIS2. The practical guide for your decision.
Julian Köhn·
ISO 27001 Certification: Process, Timeline, Costs & Preparation
How does ISO 27001 certification work? Plan your ISMS with a roadmap, Stage 1 and Stage 2 checklists, and a calculator to compare cost scenarios.
Julian Köhn·
ISO 27001 and Data Protection: GDPR, TOMs and Evidence
Does ISO 27001 cover GDPR? Understand Article 32 TOMs and follow eight practical steps, with evidence, ownership and a worked example.
Julian Köhn·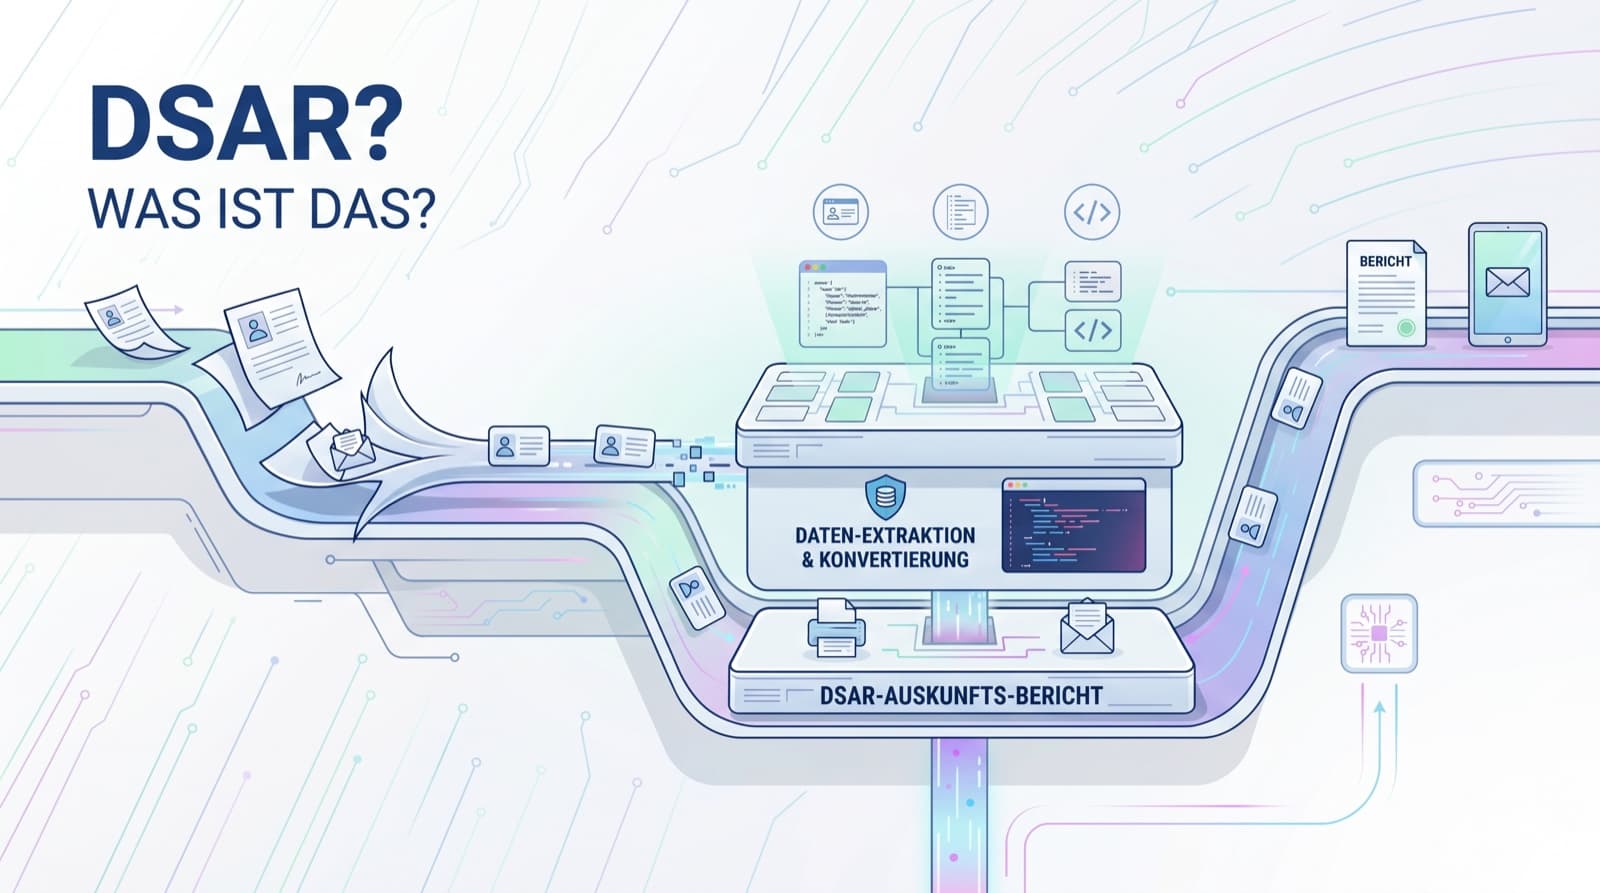
GDPR Subject Access Request: How to Answer a DSAR Lawfully
A DSAR (Data Subject Access Request) under Art. 15 GDPR must be answered within 30 days. We walk you through the 8-step workflow from identity verification to data extraction and redaction, and which grounds for refusal are legally defensible.
Julian Köhn·NIS2 supply chain security: Assess suppliers and address risks
Implement NIS2 supply chain security: identify critical providers, assess evidence, review contracts and follow up findings.
 Benjamin Schatter·
NIS2 registration with BSI: Deadline, access and required information
Prepare NIS2 registration in Germany: ELSTER organisation certificate, Mein Unternehmenskonto, BSI portal and information required under section 33 BSIG.
Benjamin Schatter·