Topic in the Kopexa blog
Vulnerability Management
Explore Vulnerability Management: background information, practical examples and recent developments from the Kopexa blog.
1–6 of 6
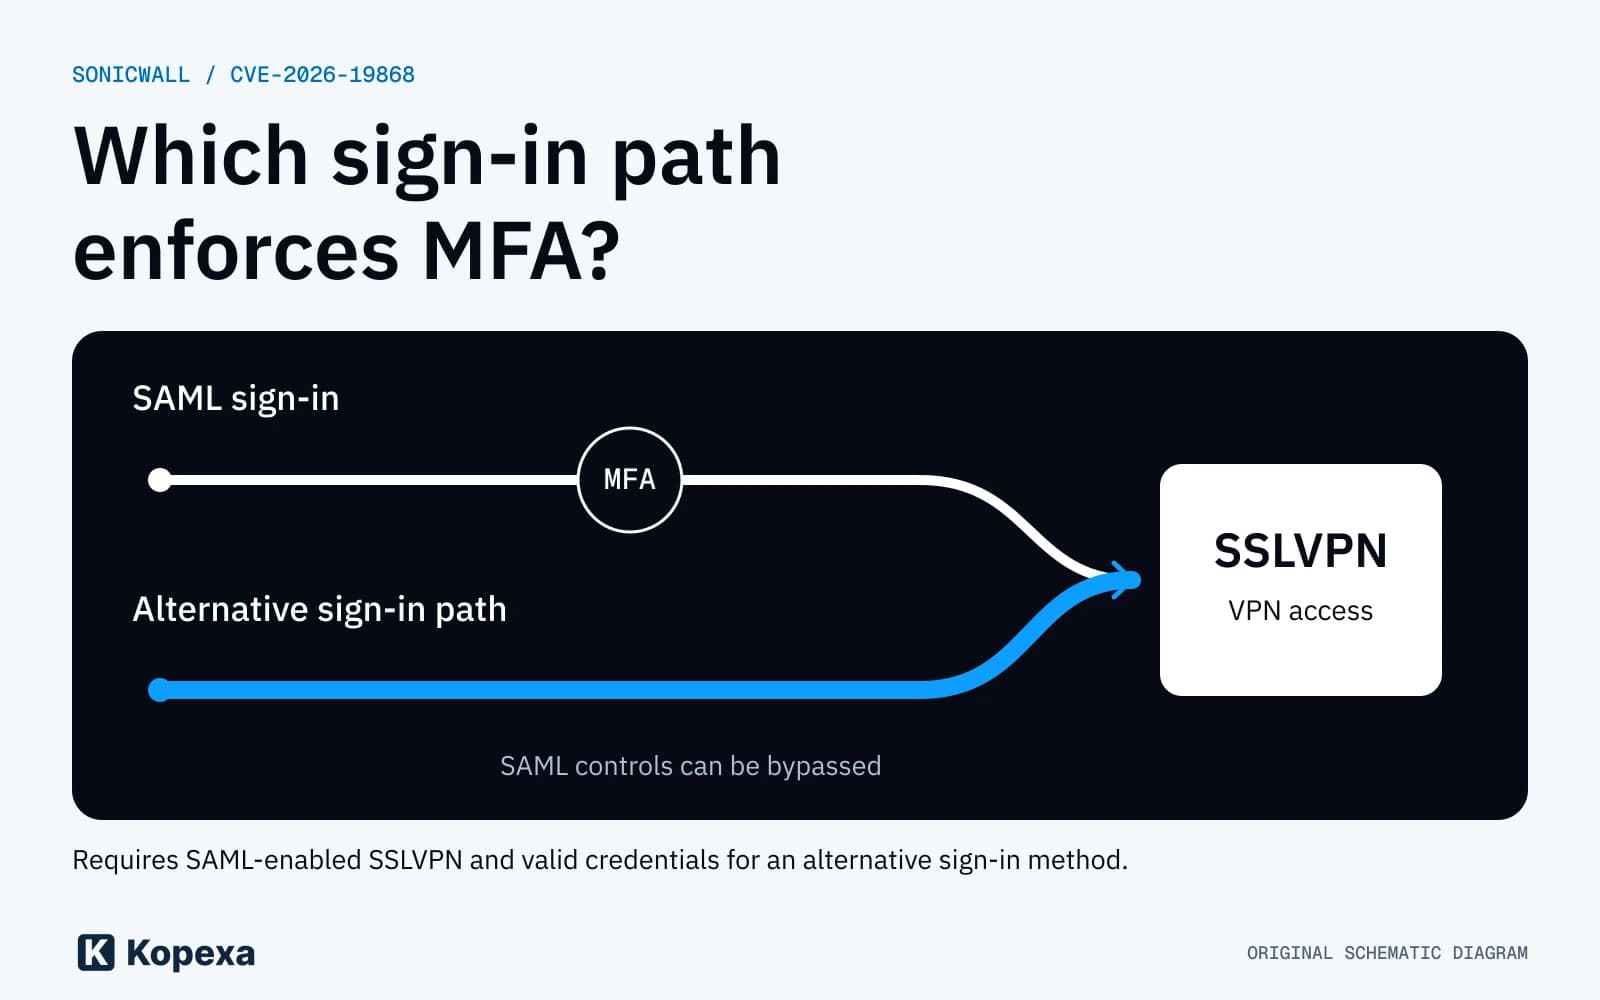
SonicWall flaw: When another sign-in path bypasses MFA
CVE-2026-19868 affects SonicOS SSLVPN with SAML. Check the prerequisites, fixed firmware versions and MFA enforcement across sign-in methods.
 Julian Köhn·
VMware ESX: CVSS 2.7, yet known exploitation
CVE-2026-41709 concerns insufficient VMware ESX logging. Why its new KEV listing matters to patch and risk owners despite the low CVSS score.
Julian Köhn·
WordPress update-process flaw: What to verify now
WordPress 7.1.4 fixes a flaw during Core updates. What operators and agencies should verify about the running version and completion of the update.
Julian Köhn·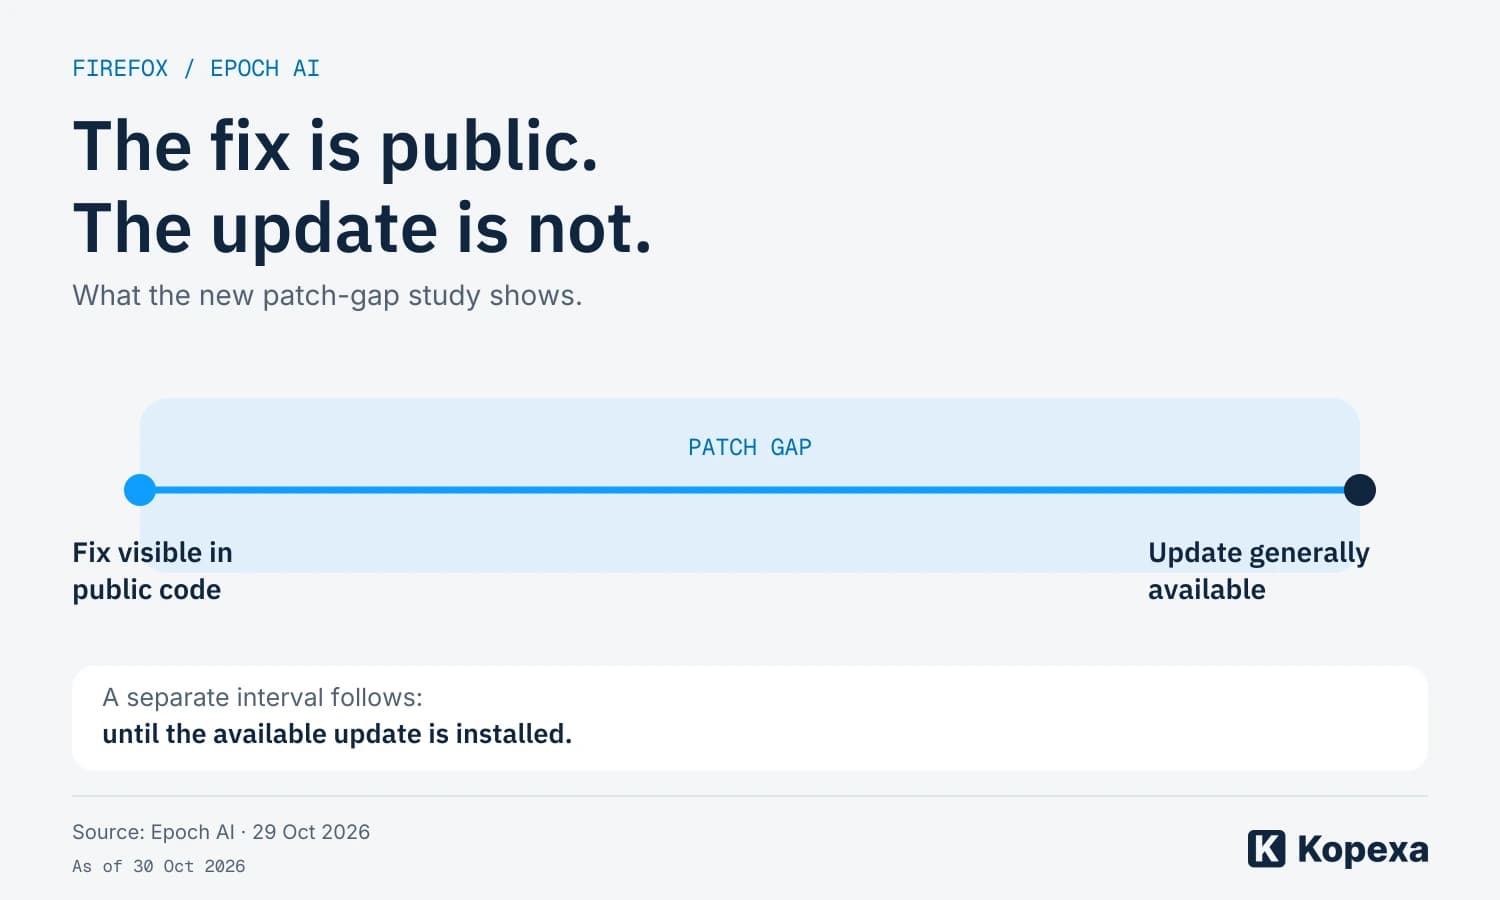
AI exploits in the Firefox patch gap: what Epoch AI shows
Epoch AI demonstrates file access through six Firefox releases. What Firefox 159 fixes and why public fixes, releases and installation are separate states.
Julian Köhn·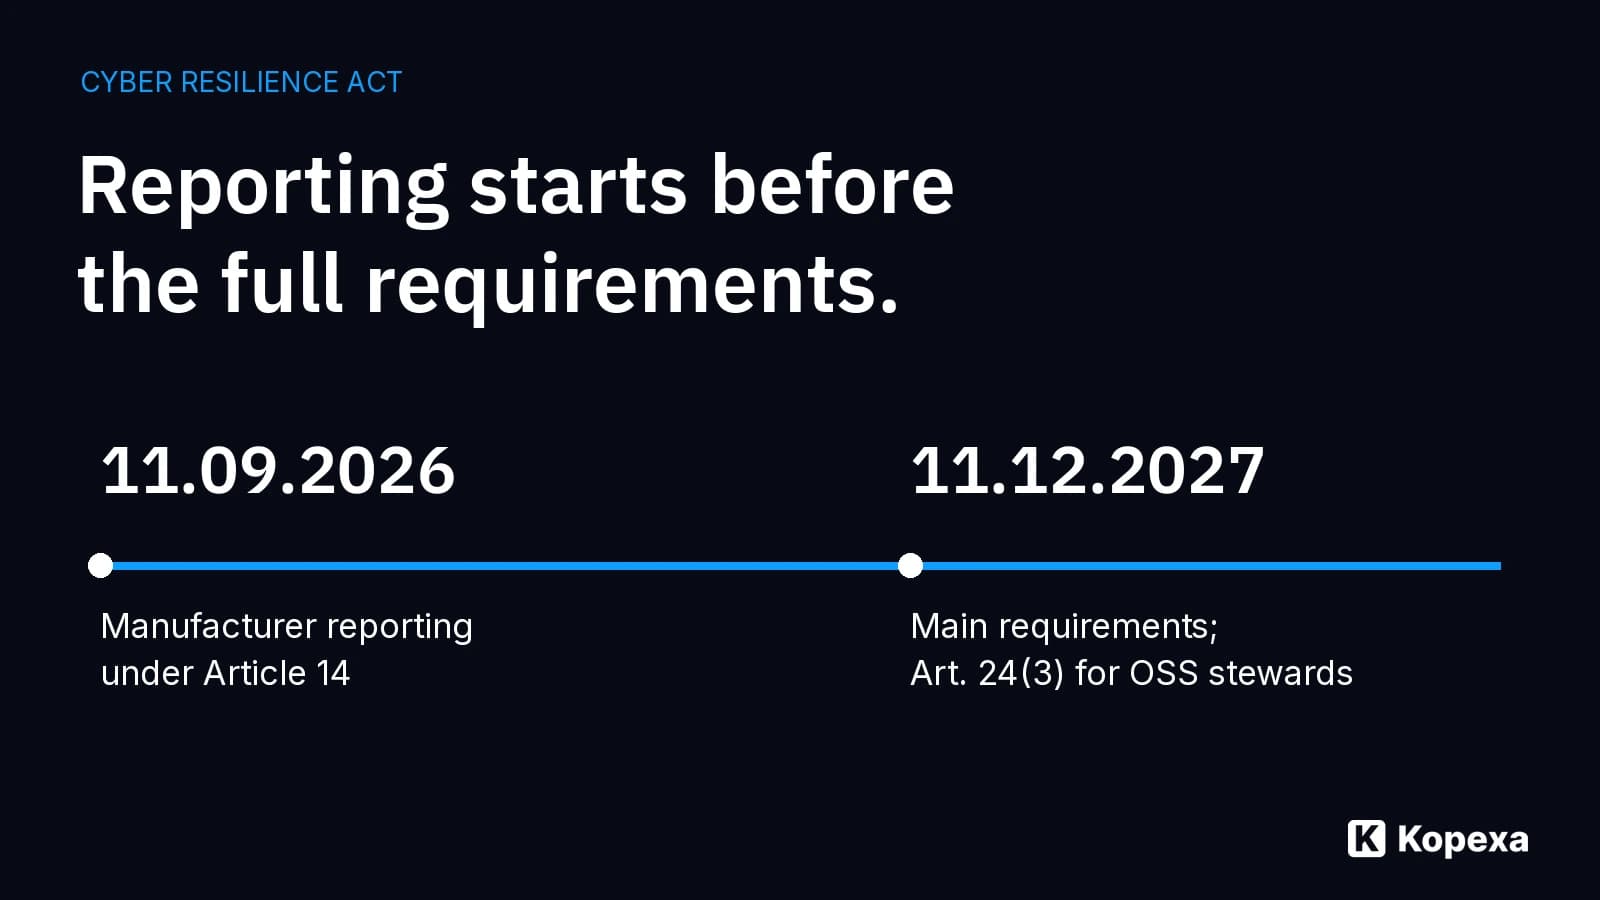
CRA reporting obligations: Why manufacturers cannot wait until 2027
CRA reporting duties have applied since 11 September 2026. Understand the reporting stages, affected manufacturers and the decisions needed before using the SRP.
Julian Köhn·