Explore the Kopexa blog
Guides & How-To
From your first ISMS to your next audit: practical guides, concrete examples and knowledge for everyday work.
29–37 of 93
Best ISMS software for small and medium-sized businesses in 2026
Choose ISMS software for SMEs: assess Kopexa, HiScout, TeamMate and verinice against everyday work, using clear criteria and a shared test case.
 Julian Köhn·
NIS2 and ISO 27001: reuse existing measures with confidence
NIS2–ISO 27001 mapping: compare scope, measures and evidence. Reuse existing ISMS work and identify additional obligations in Germany and Austria.
Julian Köhn·Implementing NIS2: a roadmap and checklist for your action plan
Plan NIS2 implementation: establish applicability, assess existing measures, assign owners and verify effectiveness. Includes a practical checklist.
Julian Köhn·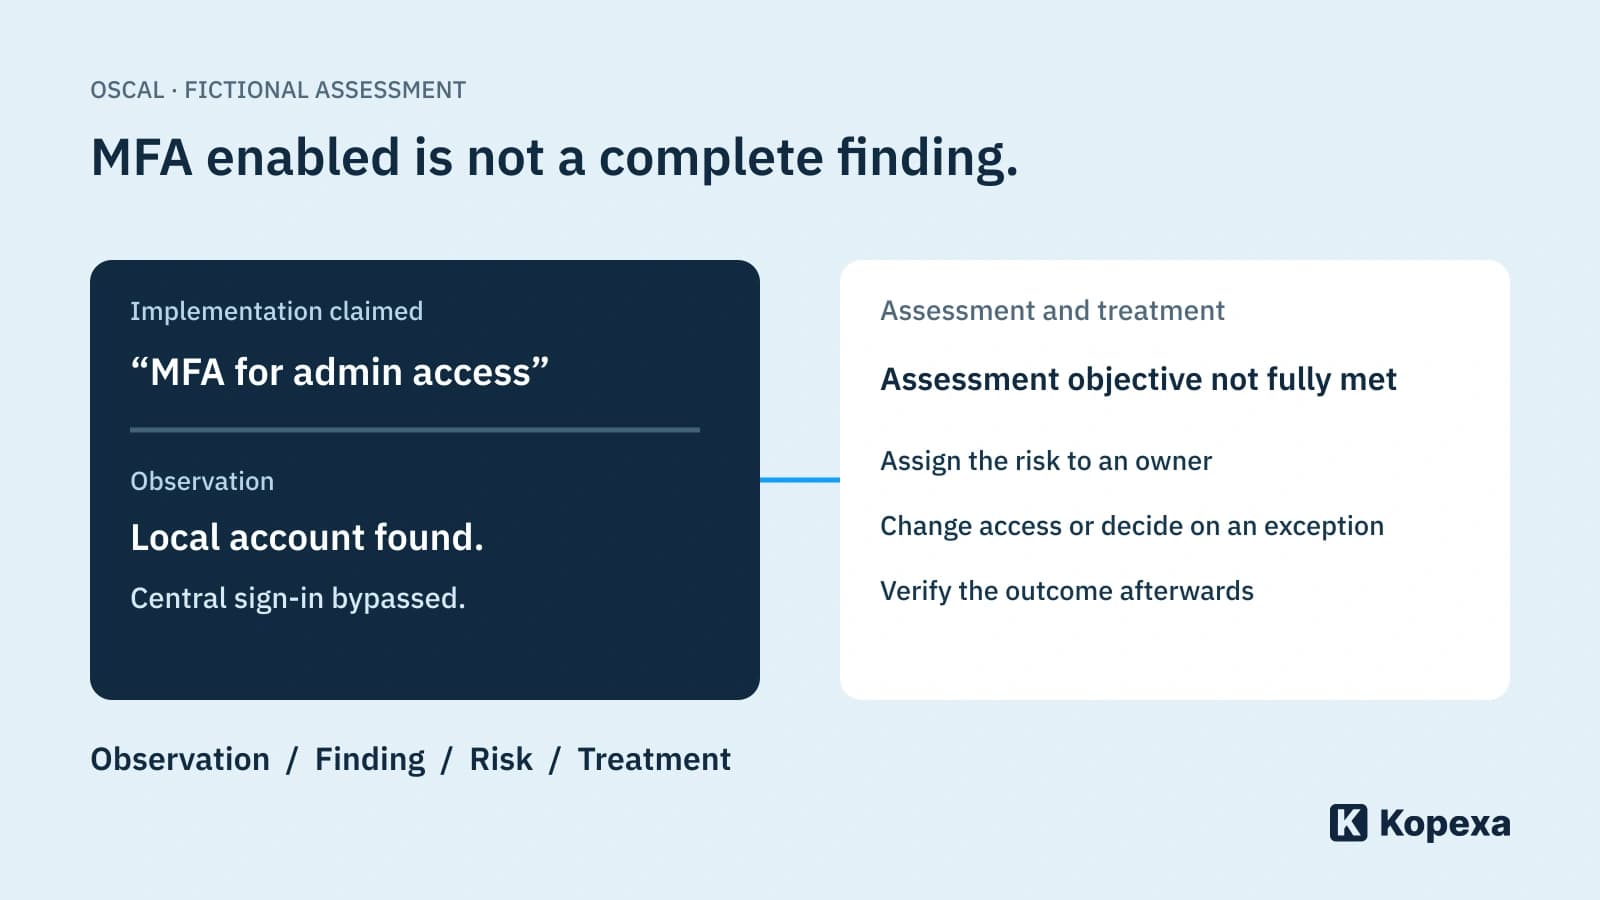
OSCAL in practice: What machine-readable evidence actually demonstrates
Distinguish requirements, implementation, observations and findings. An example shows how OSCAL structures assessments and where expert judgement remains necessary.
Julian Köhn·
ISMS without an internal IT department: Allocate tasks sensibly
Organise information security with outsourced IT: clarify responsibilities, evidence and decisions without building your own IT department.
Julian Köhn·
Changing your risk method: How do assessments remain comparable?
Introduce new risk scales without creating apparent improvement: retain method versions, compare sample cases and separate time series clearly.
Julian Köhn·
DORA register of information: How do you check data quality?
Check relationships between contracts, providers and functions in the DORA register of information: review steps, typical errors and a supplier-change example.
Julian Köhn·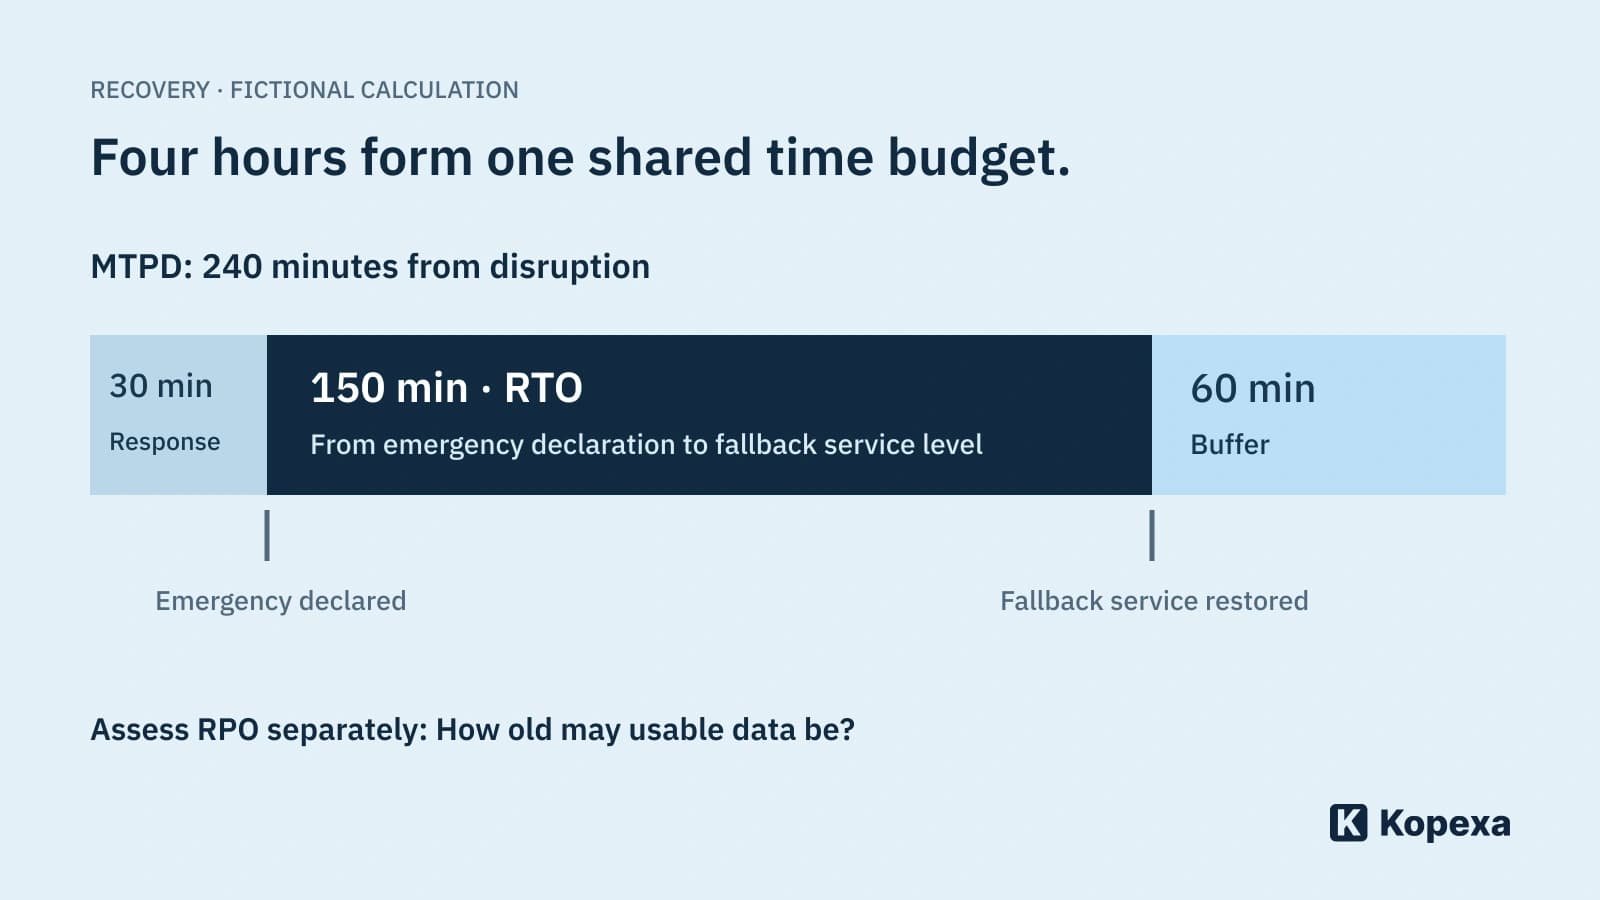
RTO, RPO and MTPD: How much downtime can your process tolerate?
Derive recovery time and tolerable data loss from the business process. Includes a worked example, time buffer and recovery test questions.
Julian Köhn·
GRC for subsidiaries: Central direction, local responsibility
Shared security standards without blanket green group reports: separate central requirements, local implementation and justified exceptions.
Julian Köhn·