Explore the Kopexa blog
Guides & How-To
From your first ISMS to your next audit: practical guides, concrete examples and knowledge for everyday work.
38–46 of 93
ISMS with an external consultant: Agree on collaboration and handover
Keep your ISMS operational after a consulting project with clear decisions, shared records and a handover tested in practice.
 Julian Köhn·
Exporting ISMS data: How to test your future exit
Before buying software, check whether risks, measures, evidence and their relationships can leave with you. Includes a practical export test and acceptance record.
Julian Köhn·
Introducing GRC software: Who takes responsibility for what?
A role model for GRC implementation: distinguish decision-makers, business owners and administrators, then test the handover to daily operations.
Julian Köhn·
ISMS risk review: When do you need to reassess?
Identify changes, new information and ineffective safeguards, review your risk assessment and keep decisions traceable.
Julian Köhn·
ISMS management review: How do you prepare decisions?
Turn ISMS reports into a basis for decisions: show action needed, resources, owners and verifiable follow-up.
Julian Köhn·
ISMS pilot project: Test the workflow, not just the interface
Assess ISMS software using a real case: hand over responsibility, replace evidence and follow an open measure through to a decision.
Julian Köhn·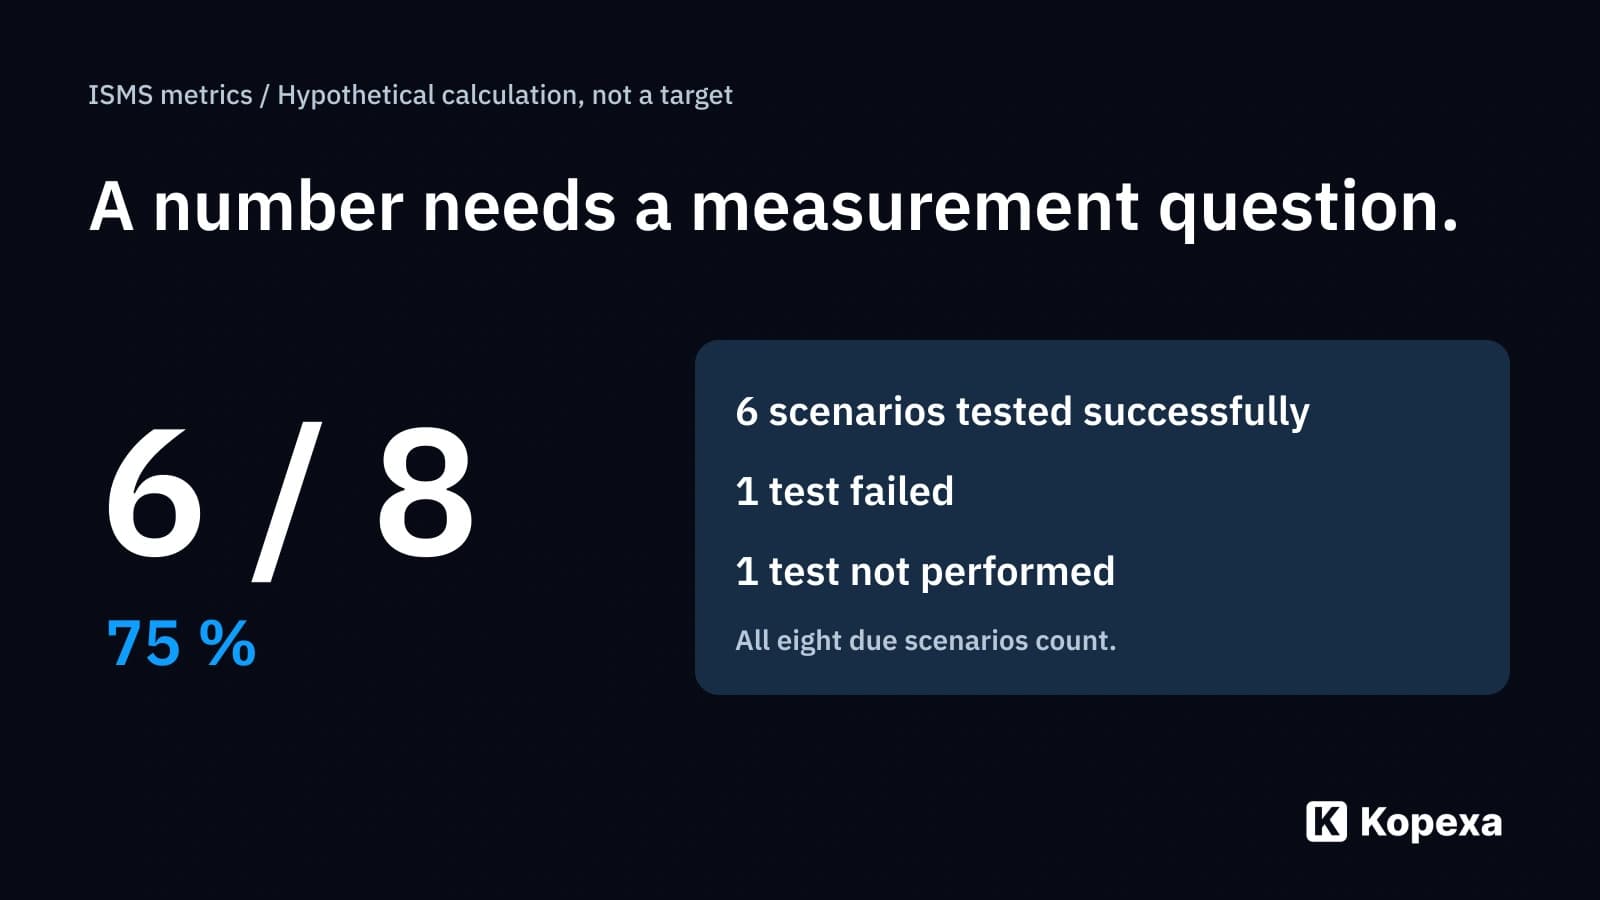
ISMS metrics: How do you measure effectiveness rather than tasks?
A green task status does not prove a safeguard works. Define ISMS metrics with a clear measurement question, data source and action rule.
Julian Köhn·
Risk acceptance: Accepted does not mean finished
An accepted risk remains a risk. Document the decision, authority, conditions and reassessment triggers so acceptance stays defensible.
Julian Köhn·
Supplier audits: turn a yes answer into reliable evidence
Examine a specific service, not just questionnaire answers. With an audit brief, evidence sample and findings record for information security.
Julian Köhn·