100–108 of 175 articles
By publication date
Changing ISMS software: how do you preserve evidence history?
The file has moved. But can you still see when it applied and who approved it? Check historical evidence when changing ISMS systems.
 Julian Köhn·
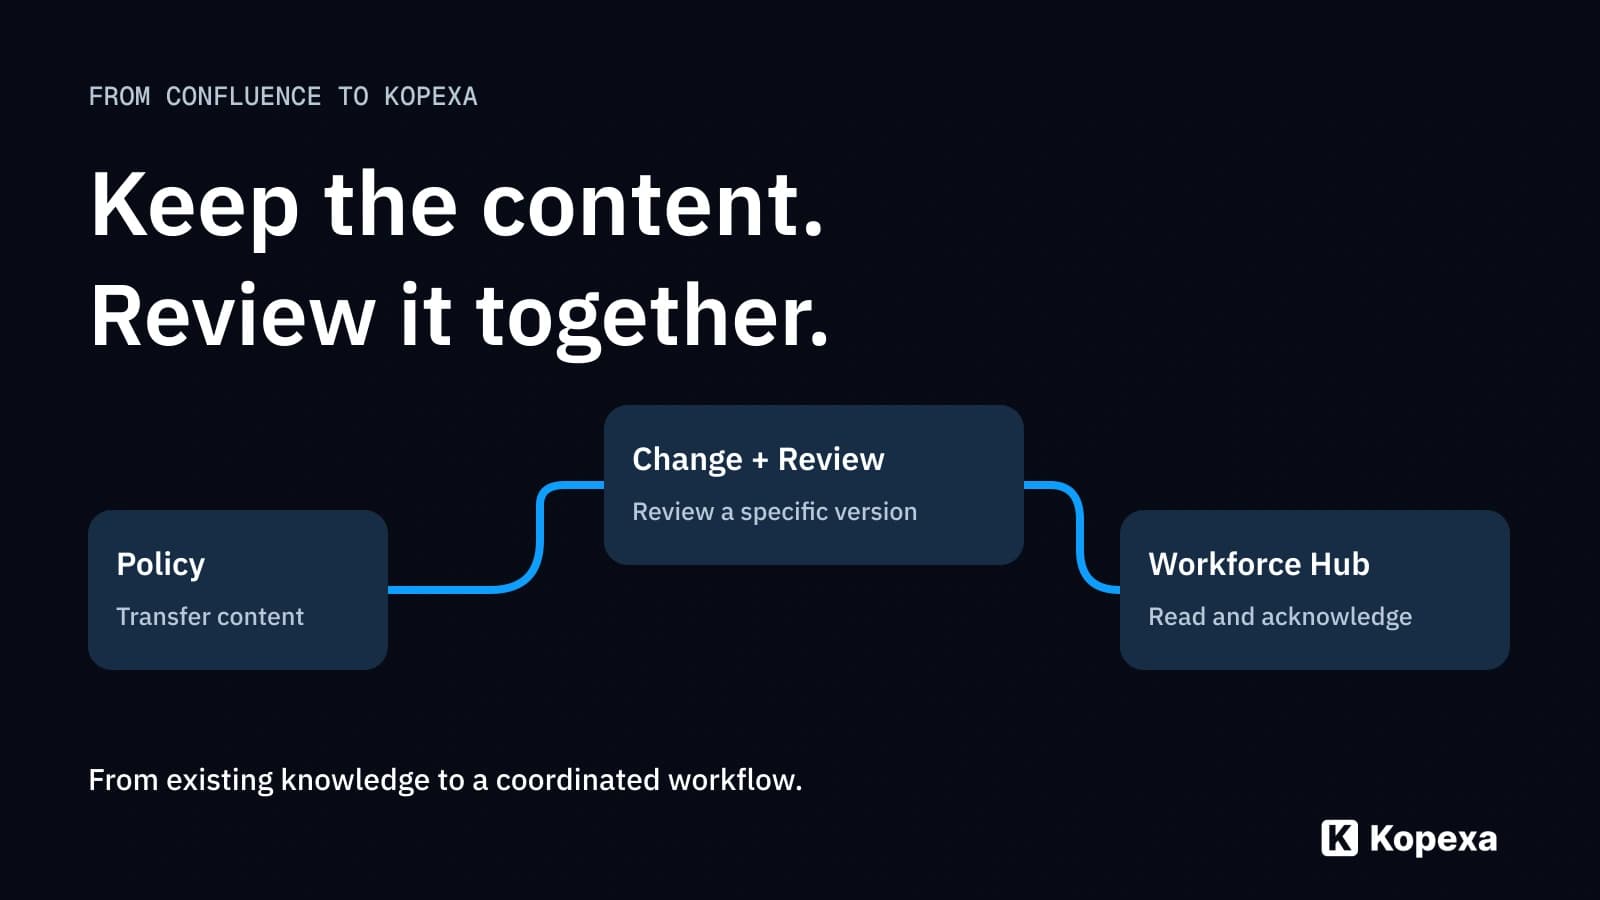
From Confluence to Kopexa: migrate policies and manage them with control
Reuse existing policies, review changes and deliver valid versions to employees. Plan the move from Confluence to Kopexa around the complete workflow.
Julian Köhn·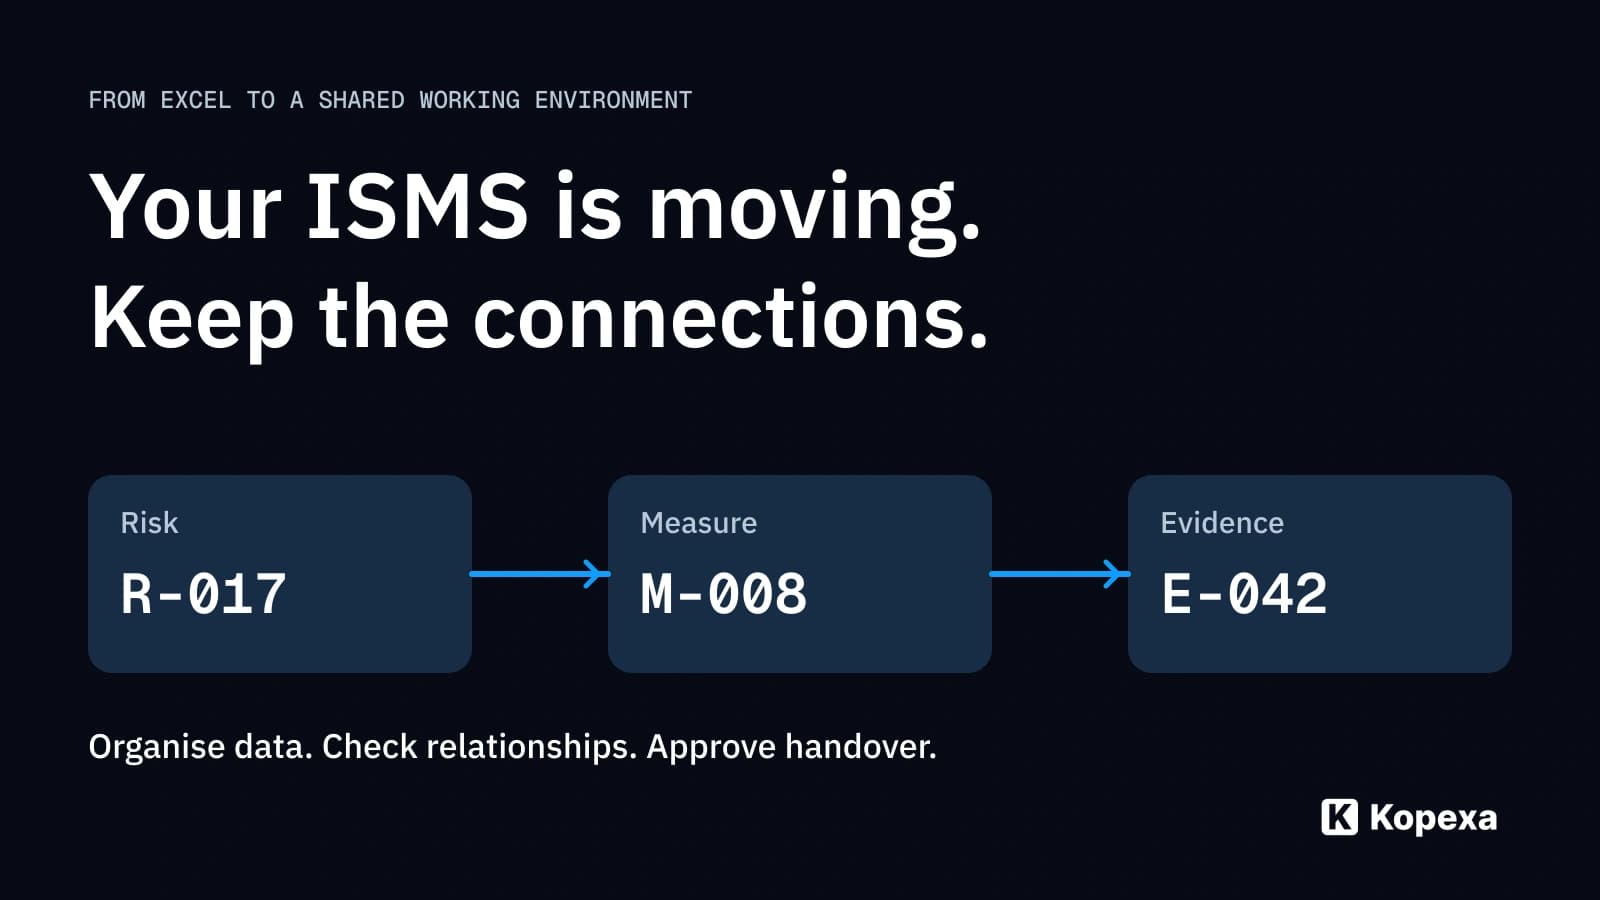
From Excel to an ISMS: planning your data migration
Bring risk registers, measures and evidence across in an organised way, with field mapping, a test dataset and clear acceptance criteria.
Julian Köhn·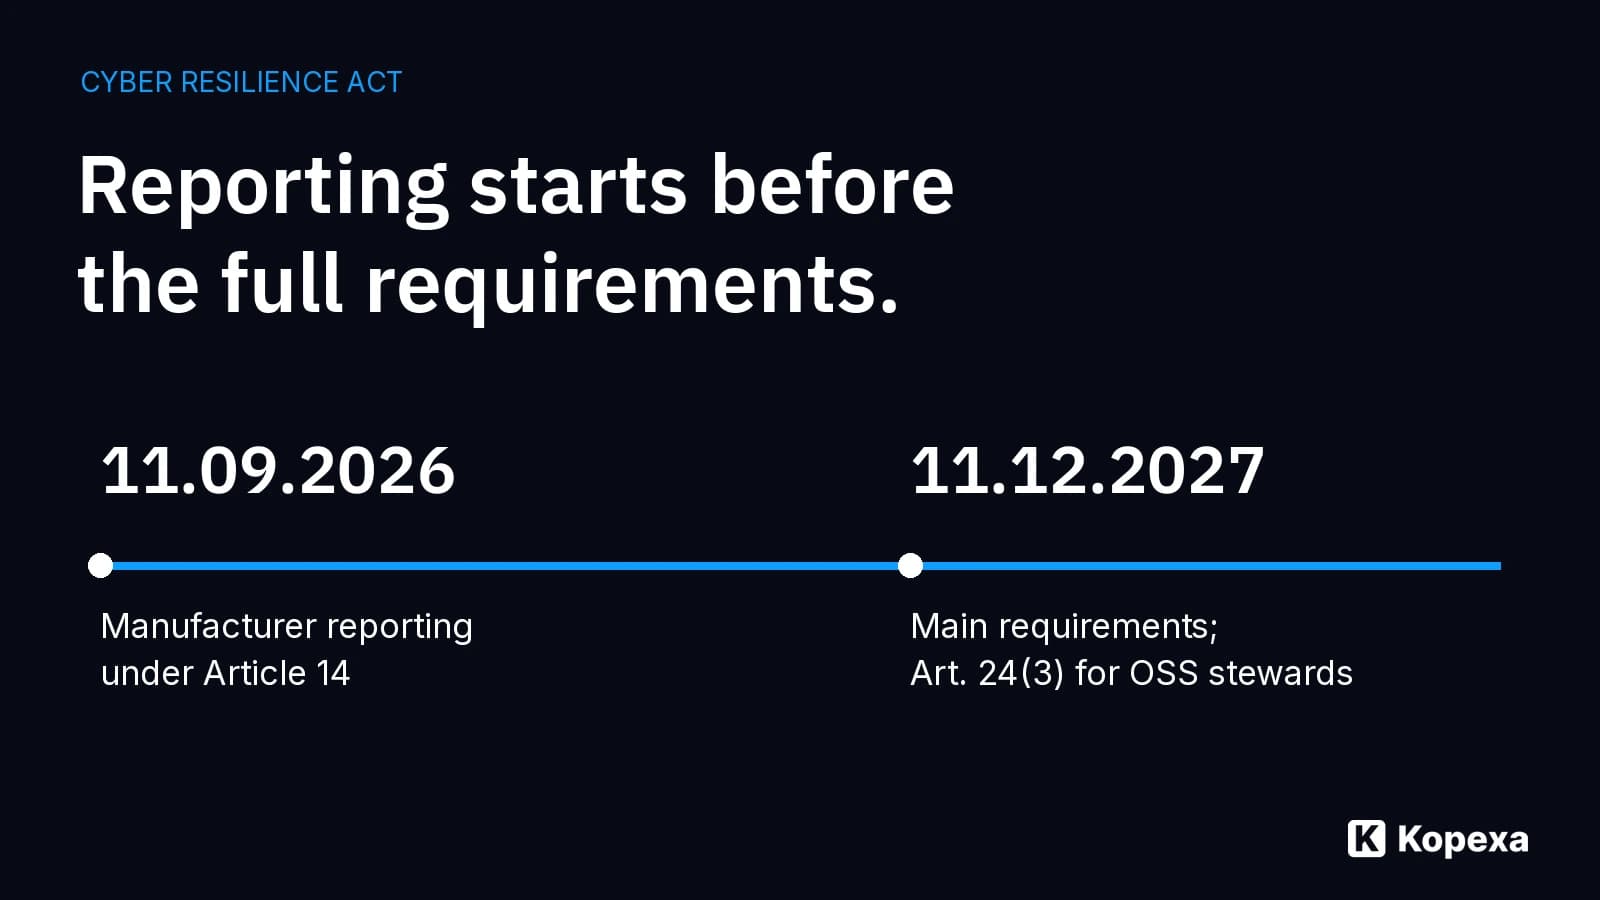
CRA reporting obligations: Why manufacturers cannot wait until 2027
CRA reporting duties have applied since 11 September 2026. Understand the reporting stages, affected manufacturers and the decisions needed before using the SRP.
Julian Köhn·
Data protection and business value: What the new regulators' study shows
CNIL, ICO and CNPD explore the economic role of data protection. What their study means for data governance, due diligence and cyber risk, without promises of returns.
Julian Köhn·
Xandr fine: consent is not an assumption
A NOK 92 million fine over the processing of Grindr users’ data: what the Xandr decision shows about consent and accountability across advertising chains.
Julian Köhn·
Dealership data breach: supplier assurance needs more than a certificate
The GeNesys breach highlights digital supply-chain risk. How to check TISAX scope, current evidence and operational information security.
Julian Köhn·
Ahold Delhaize begins controlled restart after cyber incident
Ahold Delhaize is restarting certain systems after a cyber incident while stores remain open. What the retailer has confirmed.
Julian Köhn·
AhsayCBS: attackers target backup servers; hotfixes available
Attacks on AhsayCBS highlight the need to protect backup management itself. The vendor and Huntress report available hotfixes and compromise guidance.
Julian Köhn·