64–72 of 178 articles
By publication date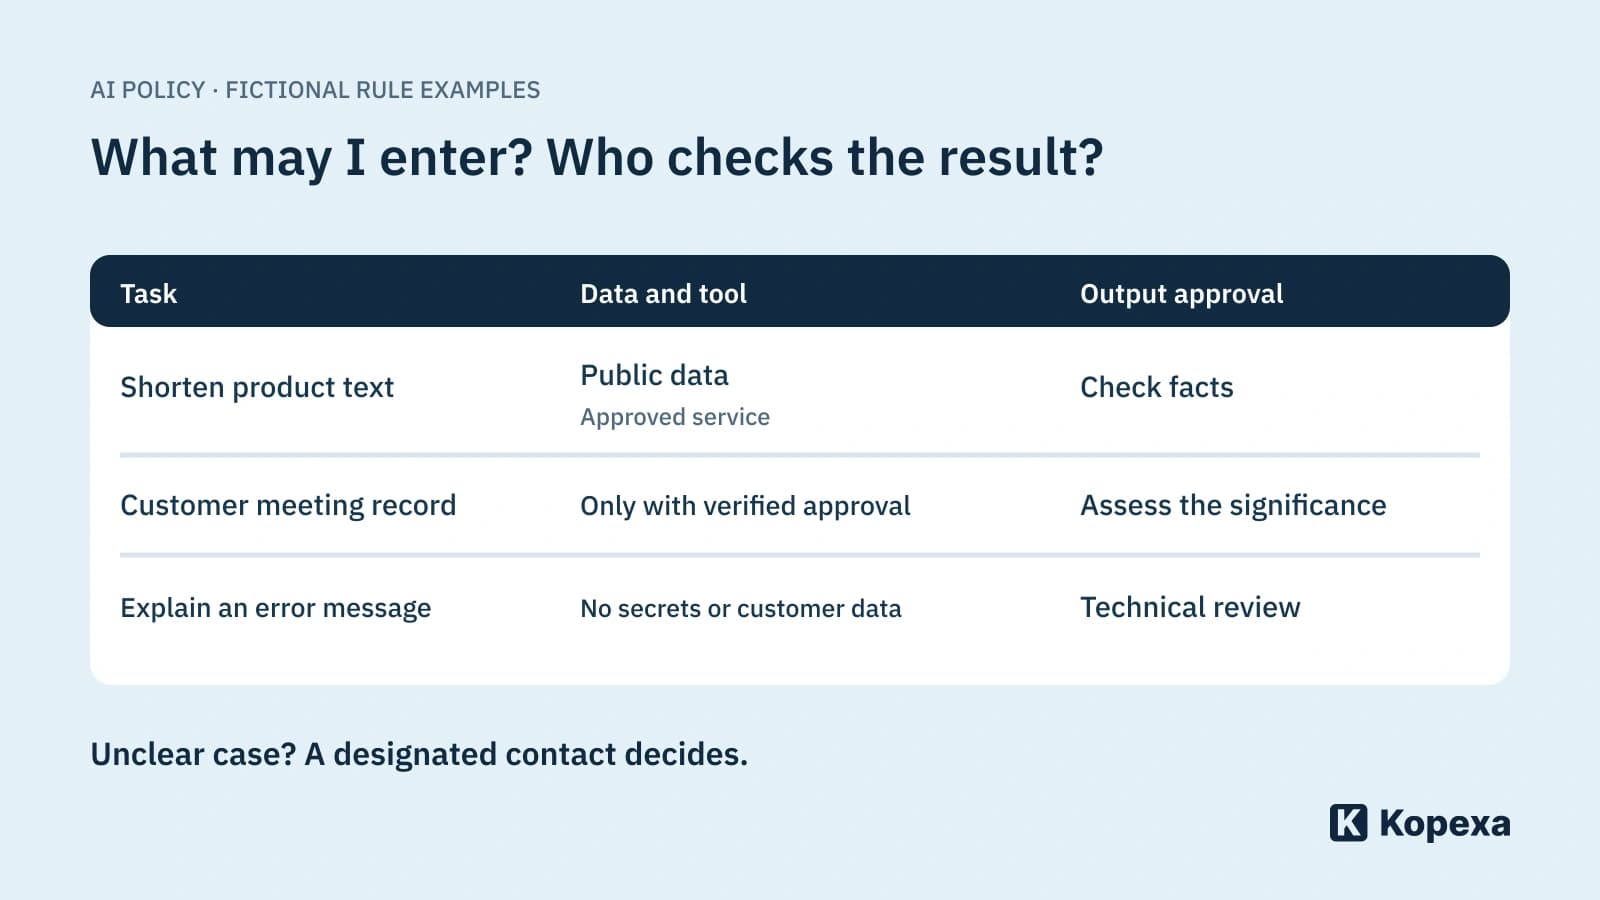
AI policy for employees: Which uses do you actually allow?
Write clear rules for AI tools, data and approvals. Includes example cases, a reporting channel and a workflow for versioning and acknowledgement.
 Julian Köhn·
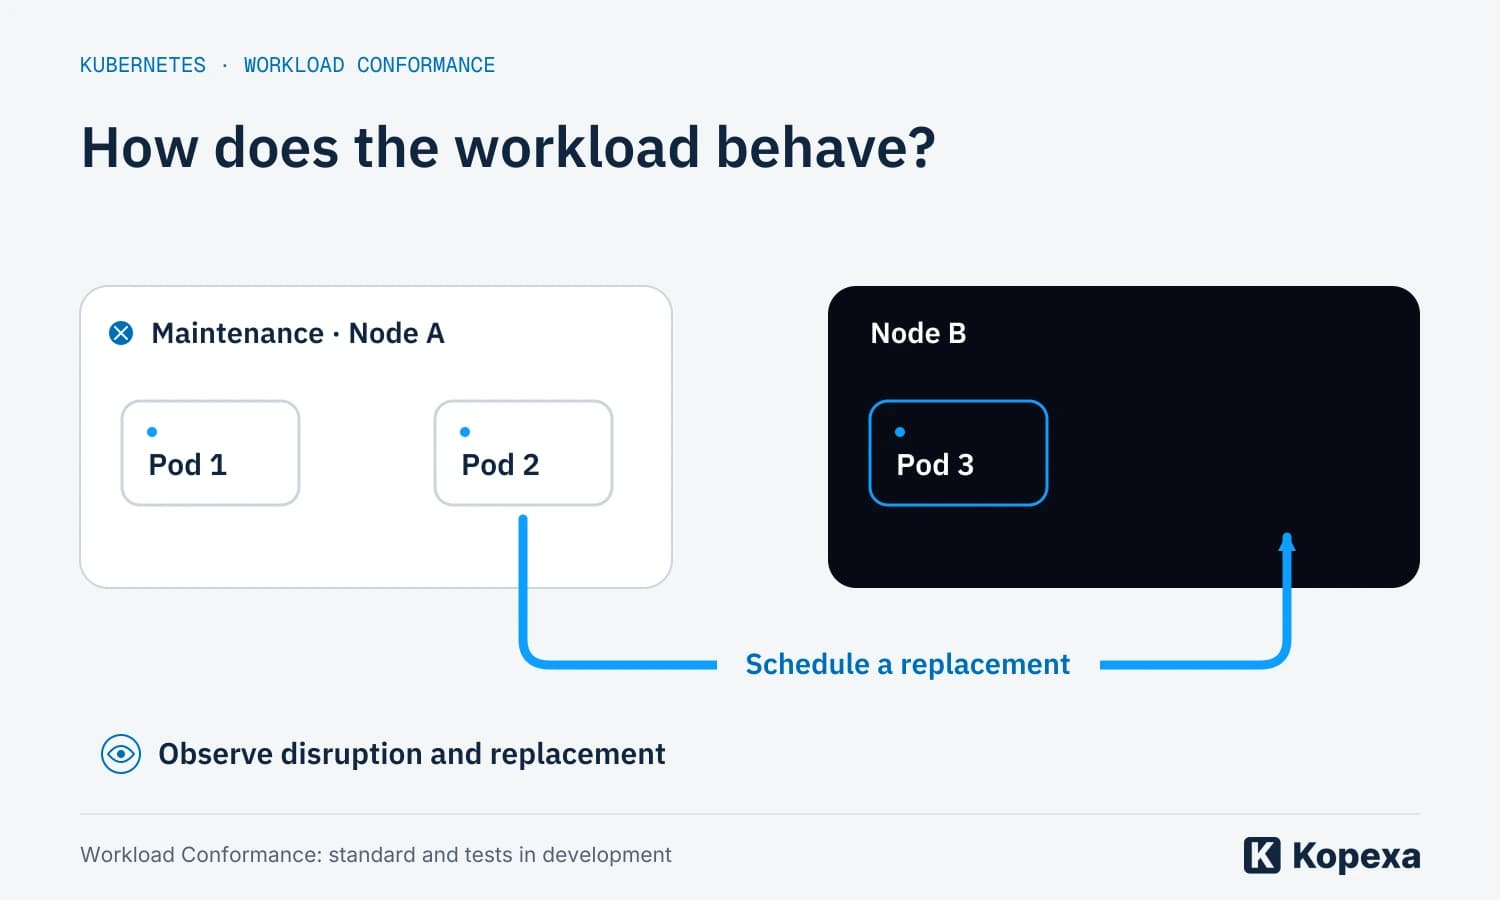
Kubernetes plans Workload Conformance: How resilient is your application?
Kubernetes plans shared runtime tests for applications. What Workload Conformance aims to change, what Kyverno can do today, and where native checks have limits.
Julian Köhn·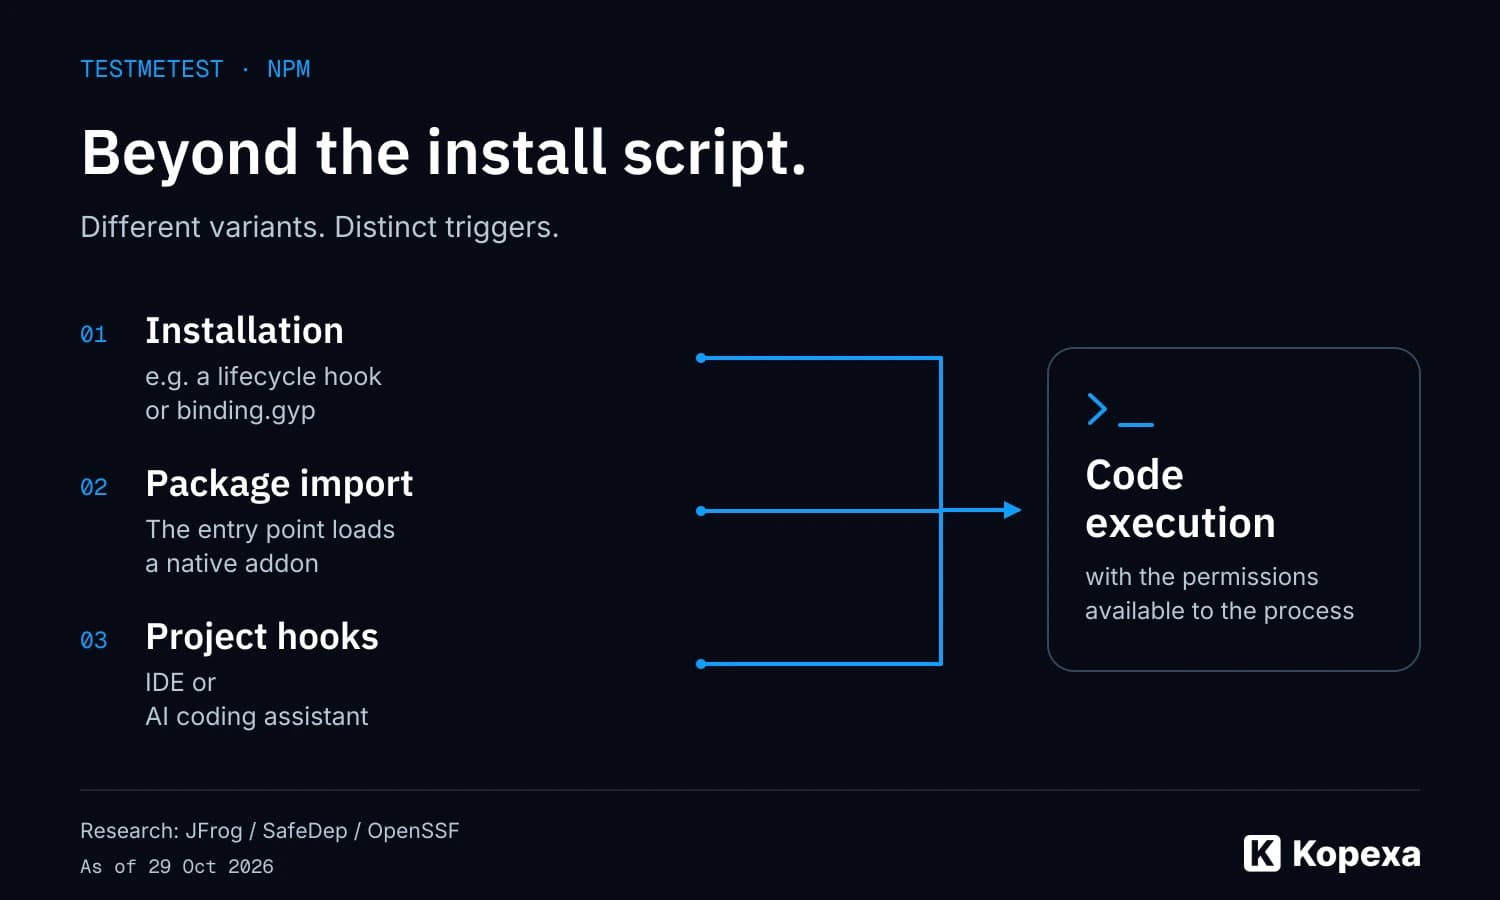
testmetest: 42 GitHub repositories armed for an npm worm
JFrog finds 42 armed GitHub repositories. How testmetest uses npm packages and project hooks, what has been removed and what teams should investigate.
Julian Köhn·
Best GRC software for mid-sized businesses in 2026
Choose GRC software for mid-sized businesses: connect existing processes, departments and security requirements. Includes supplier approaches and a pilot workflow.
Julian Köhn·
Best GRC software for corporate groups in 2026
Compare GRC software for corporate groups: test tenant separation, shared controls, local exceptions and consolidated reporting in practice.
Julian Köhn·
Best ISMS software for small and medium-sized businesses in 2026
Choose ISMS software for SMEs: assess Kopexa, HiScout, TeamMate and verinice against everyday work, using clear criteria and a shared test case.
Julian Köhn·
NIS2 and ISO 27001: reuse existing measures with confidence
NIS2–ISO 27001 mapping: compare scope, measures and evidence. Reuse existing ISMS work and identify additional obligations in Germany and Austria.
Julian Köhn·Implementing NIS2: a roadmap and checklist for your action plan
Plan NIS2 implementation: establish applicability, assess existing measures, assign owners and verify effectiveness. Includes a practical checklist.
Julian Köhn·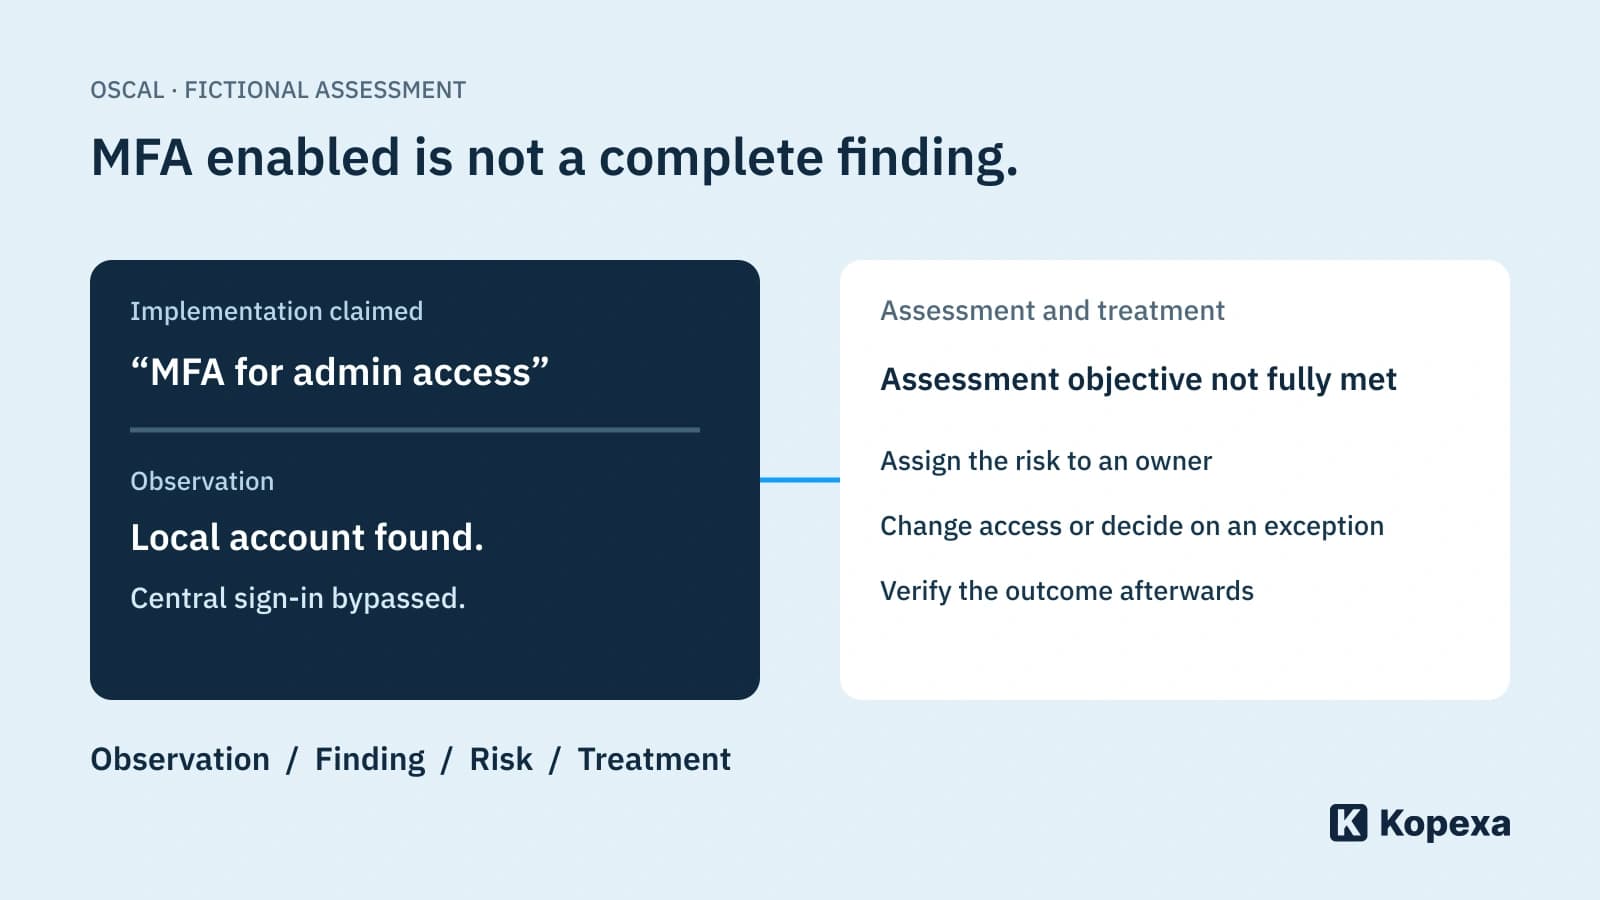
OSCAL in practice: What machine-readable evidence actually demonstrates
Distinguish requirements, implementation, observations and findings. An example shows how OSCAL structures assessments and where expert judgement remains necessary.
Julian Köhn·