82–90 of 178 articles
By publication date
ISMS risk review: When do you need to reassess?
Identify changes, new information and ineffective safeguards, review your risk assessment and keep decisions traceable.
 Julian Köhn·
ISMS management review: How do you prepare decisions?
Turn ISMS reports into a basis for decisions: show action needed, resources, owners and verifiable follow-up.
Julian Köhn·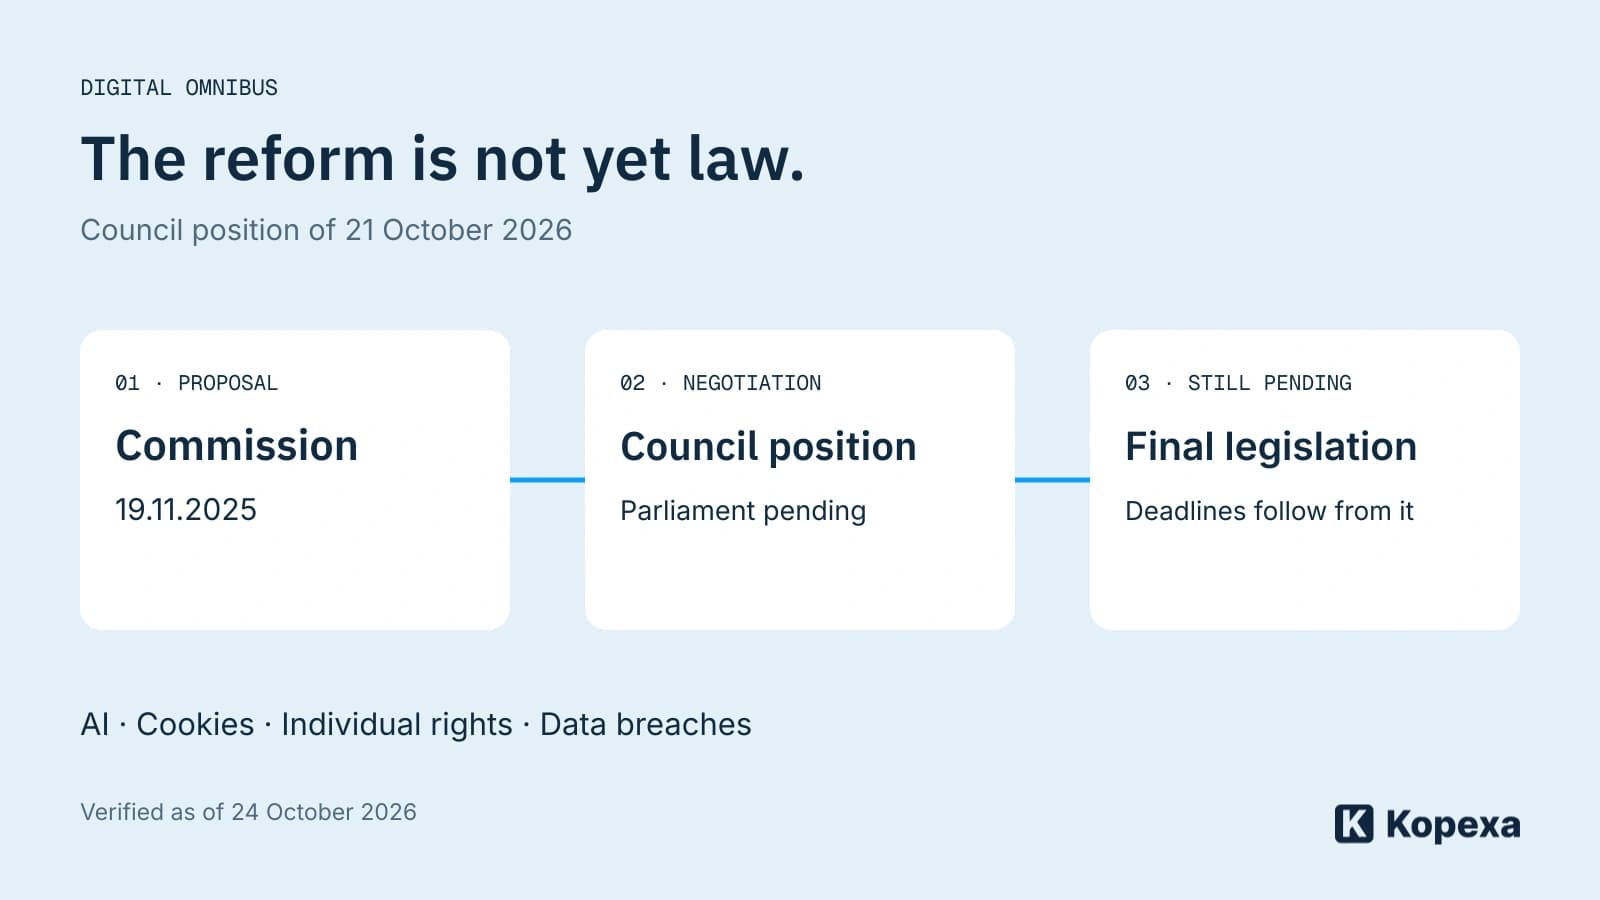
Digital Omnibus: What the GDPR reform would change for AI, cookies and businesses
What the EU Council proposes for AI training, cookies and data breaches: the GDPR reform explained, its current status and implications for businesses.
Julian Köhn·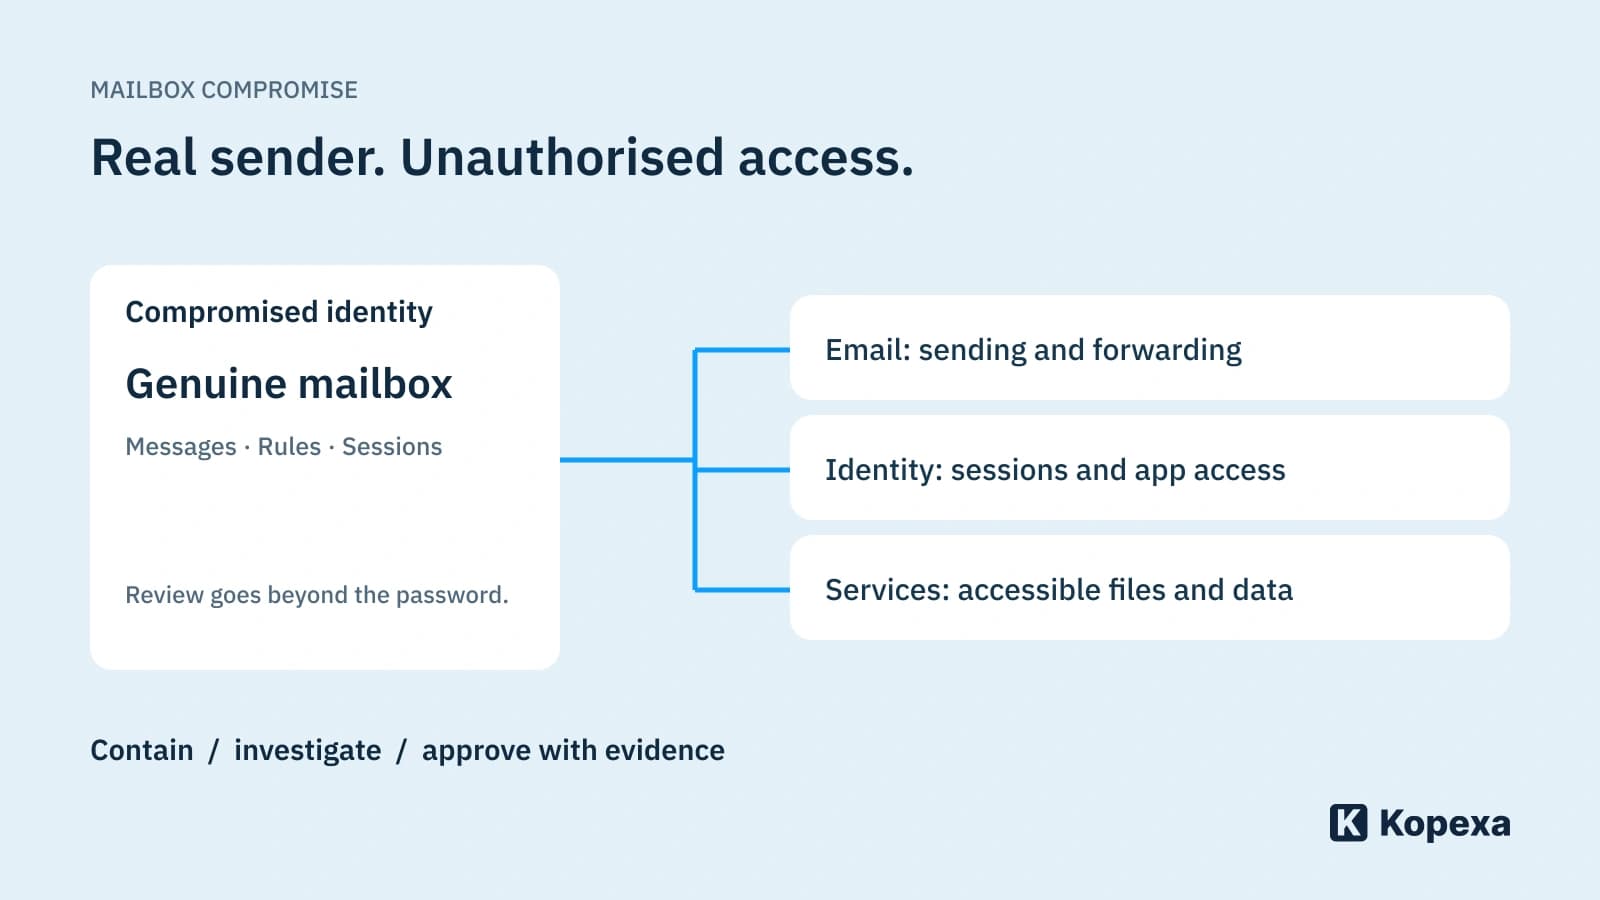
The phishing email comes from a real colleague. What now?
A compromised business mailbox makes the sender credible. Organise containment, investigation and a controlled return to work.
Julian Köhn·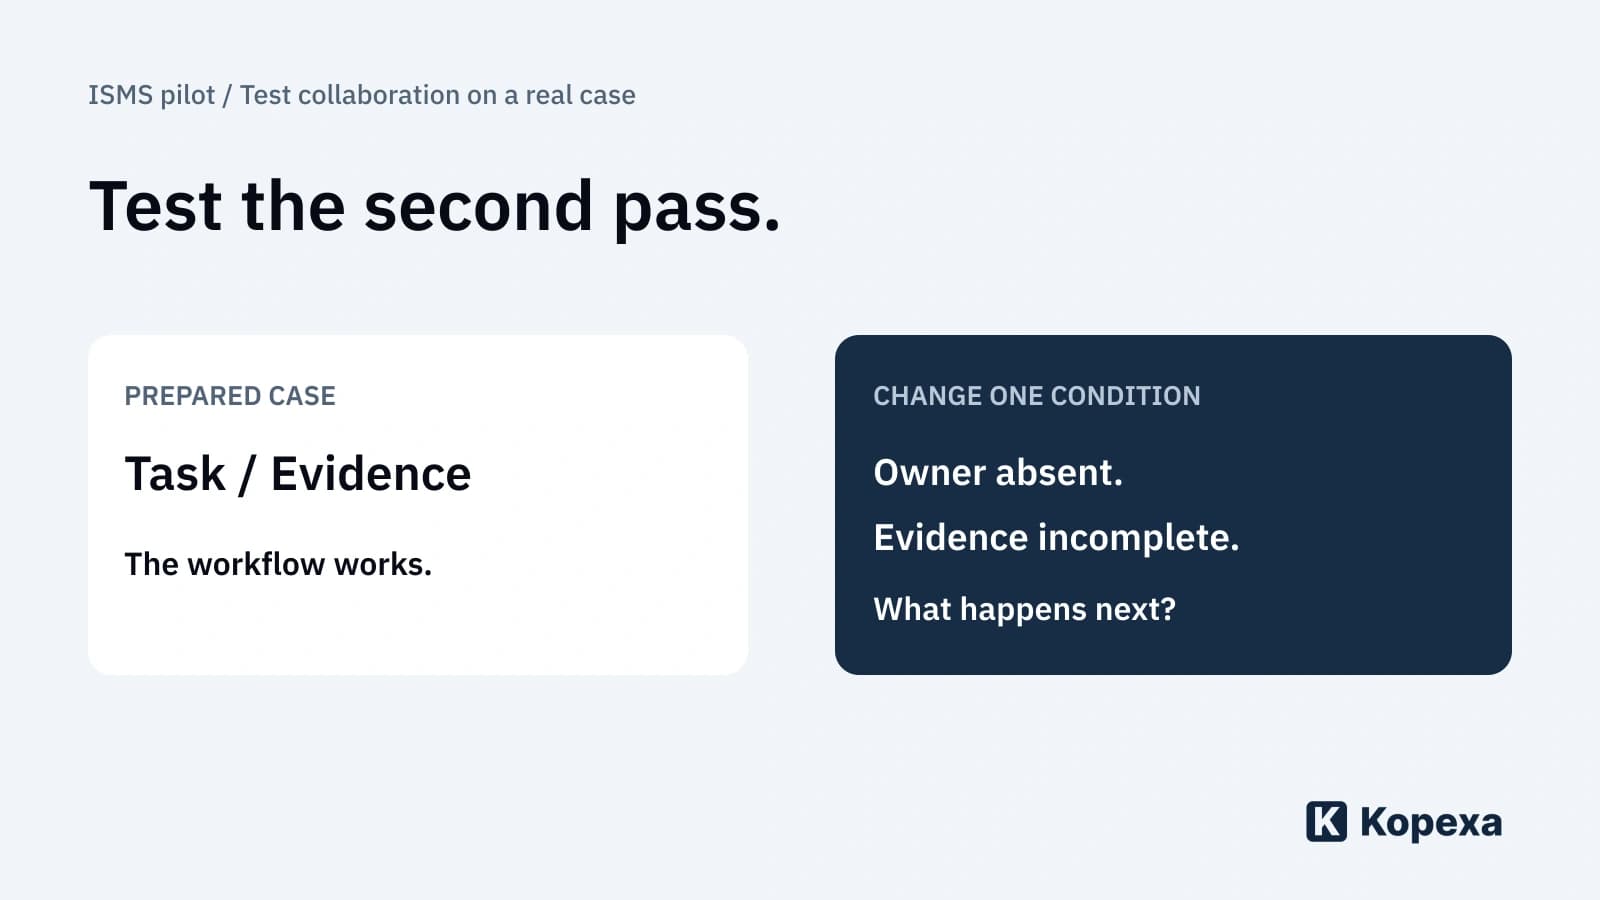
ISMS pilot project: Test the workflow, not just the interface
Assess ISMS software using a real case: hand over responsibility, replace evidence and follow an open measure through to a decision.
Julian Köhn·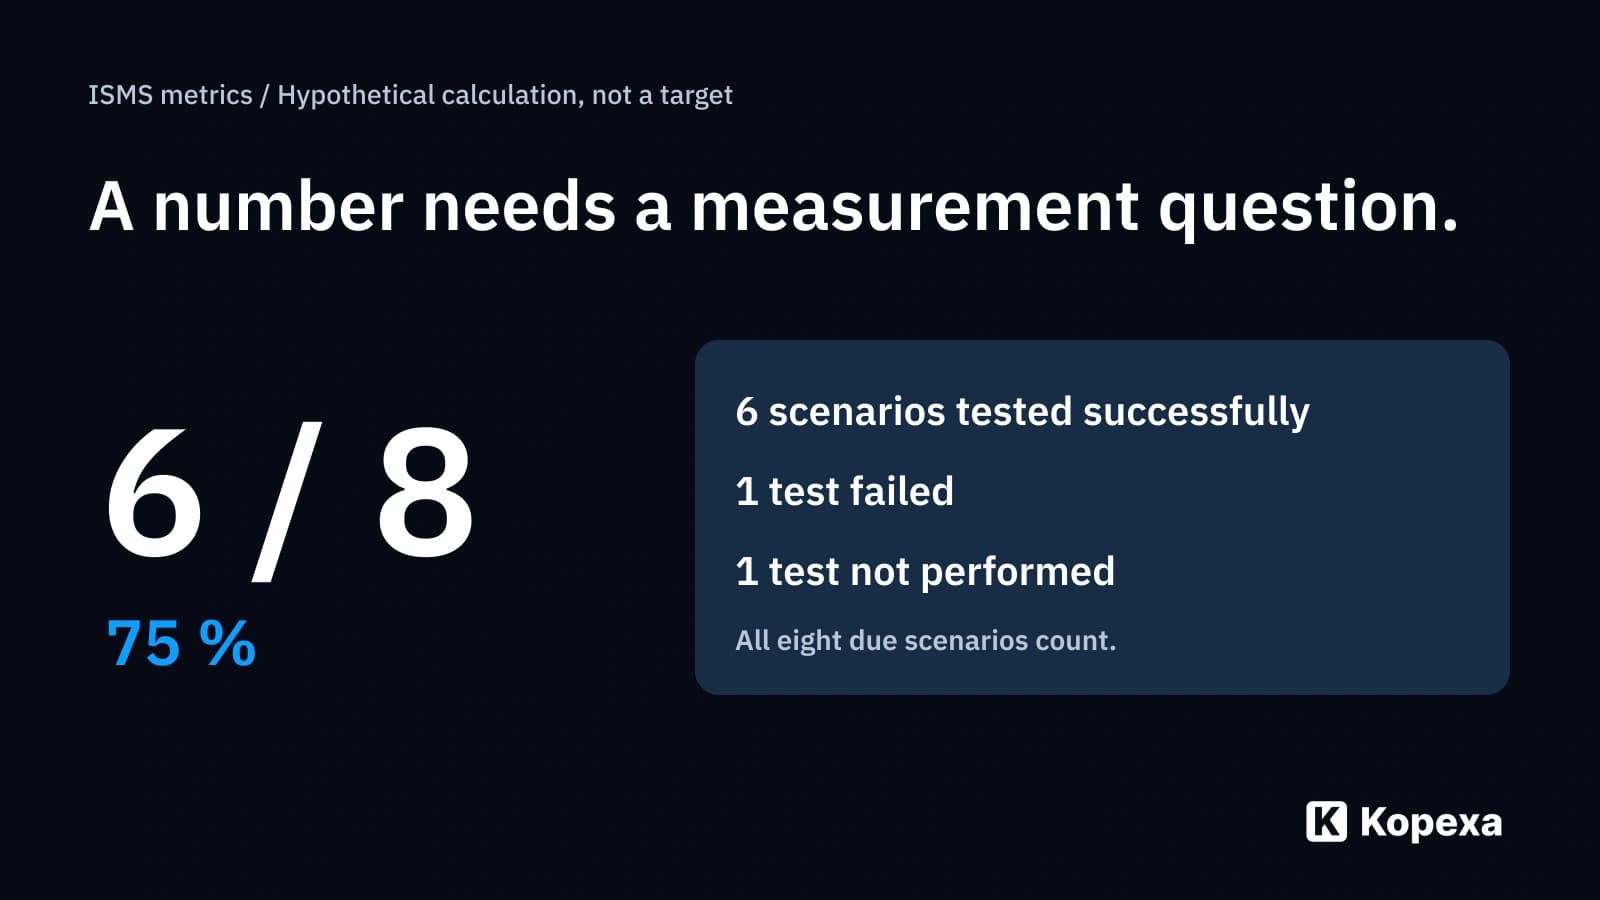
ISMS metrics: How do you measure effectiveness rather than tasks?
A green task status does not prove a safeguard works. Define ISMS metrics with a clear measurement question, data source and action rule.
Julian Köhn·
curl: More security reports do not automatically make us safer
curl changes its reporting procedure from 26 October. A CTO’s view on taking real vulnerabilities seriously and turning reports into reasoned decisions.
Julian Köhn·
GitLab security update: More than a patch to your development platform
A critical GitLab vulnerability requires a verified update and a review of the release path. Check versions, credentials, runners and remaining incident questions.
Julian Köhn·
Risk acceptance: Accepted does not mean finished
An accepted risk remains a risk. Document the decision, authority, conditions and reassessment triggers so acceptance stays defensible.
Julian Köhn·