118–126 of 178 articles
By publication date
Meta’s GitHub data breach: How far can a stolen account reach?
Stolen credentials opened Meta’s GitHub repositories. What businesses should check across access rights, secrets, test data and incident response.
 Julian Köhn·
Malware in job applications: Assess your recruiting workflow
A résumé as a ransomware entry point: What HR and IT should check in intake, sharing and reporting, including an authorised testing scenario.
Julian Köhn·
Smart glasses: EDPB calls for clear recording indicators
The EDPB published its smart-glasses statement on 13 October. The focus is unnoticed recording and the responsibilities of users and service providers.
Julian Köhn·
Windows 10 LTSB 2016: Which legacy devices should you check now?
Windows 10 LTSB 2016 reaches end of support. Assess affected systems, business impact and decisions on migration, ESU or time-limited operation.
Julian Köhn·
Cyber risks in SMEs: Which actions come first?
A practical worksheet for cybersecurity priorities, accountable actions and verifiable outcomes.
Julian Köhn·
Security awareness: Does your team know what to do?
Beyond attendance: a 20-minute exercise to check whether your team can report suspicious messages and improve the process.
Julian Köhn·
Refrigeration cyberattack: Which dependencies put your operations at risk?
The attack on French refrigeration systems highlights an operational risk. Connect critical assets, suppliers, business impact analysis and verifiable actions.
Julian Köhn·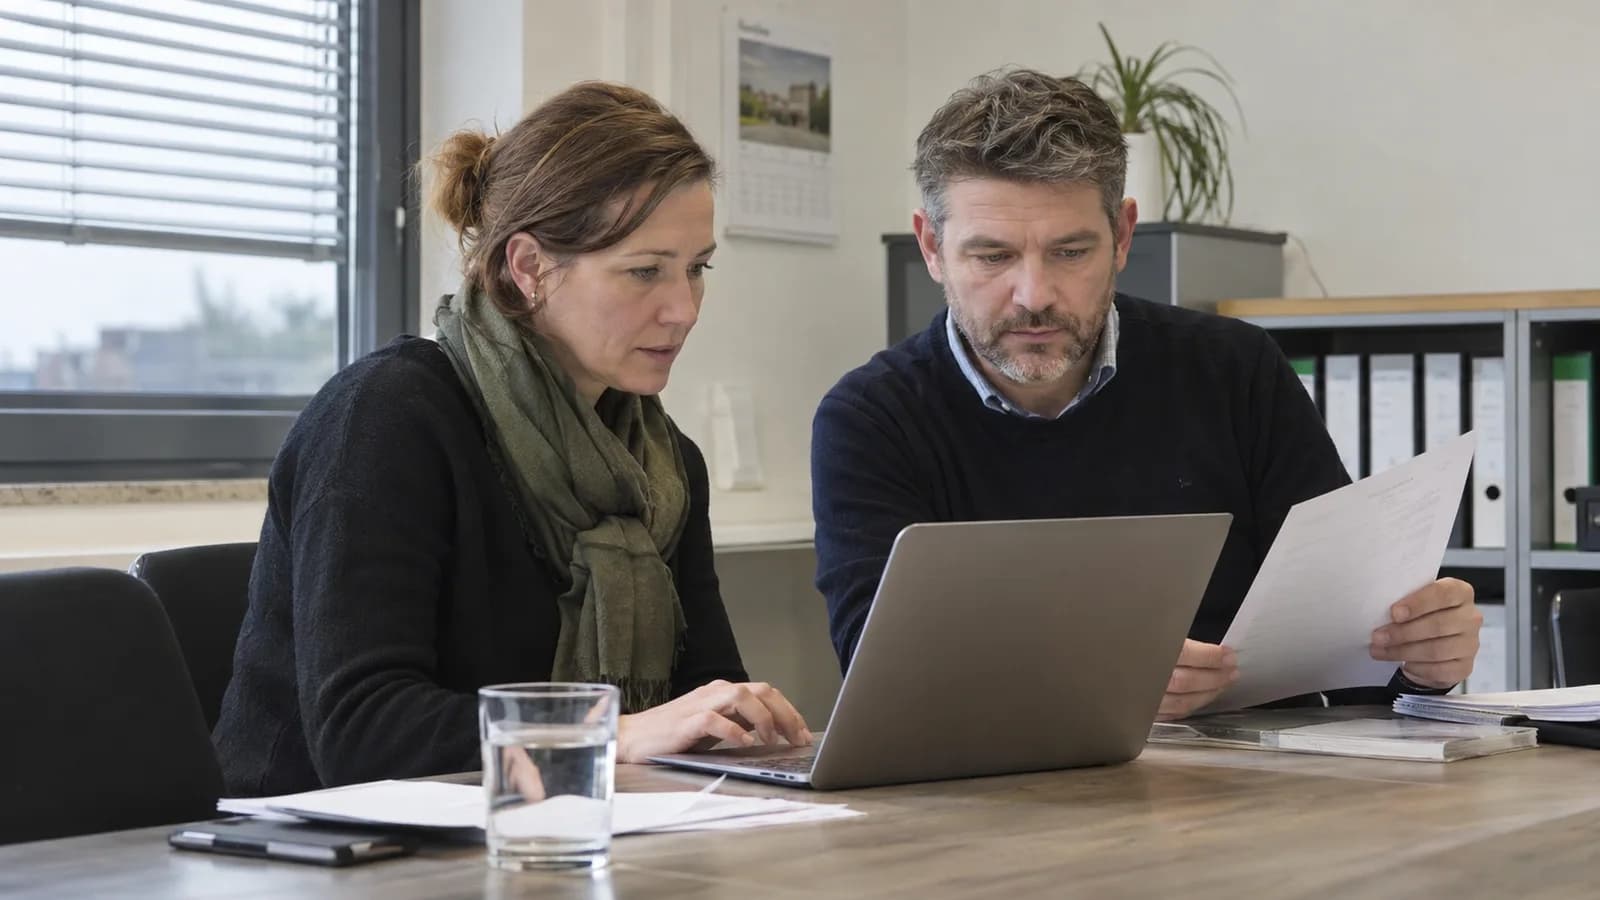
AI agents at work: Who can act, and who stays accountable?
AI agents do more than read. Define access, approvals and ownership, then make their risks and safeguards traceable in your existing ISMS.
Julian Köhn·
ISO/IEC 27090: bringing AI security risks into your ISMS
Understand the scope of ISO/IEC 27090 and connect AI applications, suppliers and data risks to practical work in your existing ISMS.
Julian Köhn·