Explore the Kopexa blog
Privacy & Engineering
Connect privacy and technical security. Understand current cases and put safeguards into practice.
38–46 of 47
Ahold Delhaize begins controlled restart after cyber incident
Ahold Delhaize is restarting certain systems after a cyber incident while stores remain open. What the retailer has confirmed.
 Julian Köhn·
AhsayCBS: attackers target backup servers; hotfixes available
Attacks on AhsayCBS highlight the need to protect backup management itself. The vendor and Huntress report available hotfixes and compromise guidance.
Julian Köhn·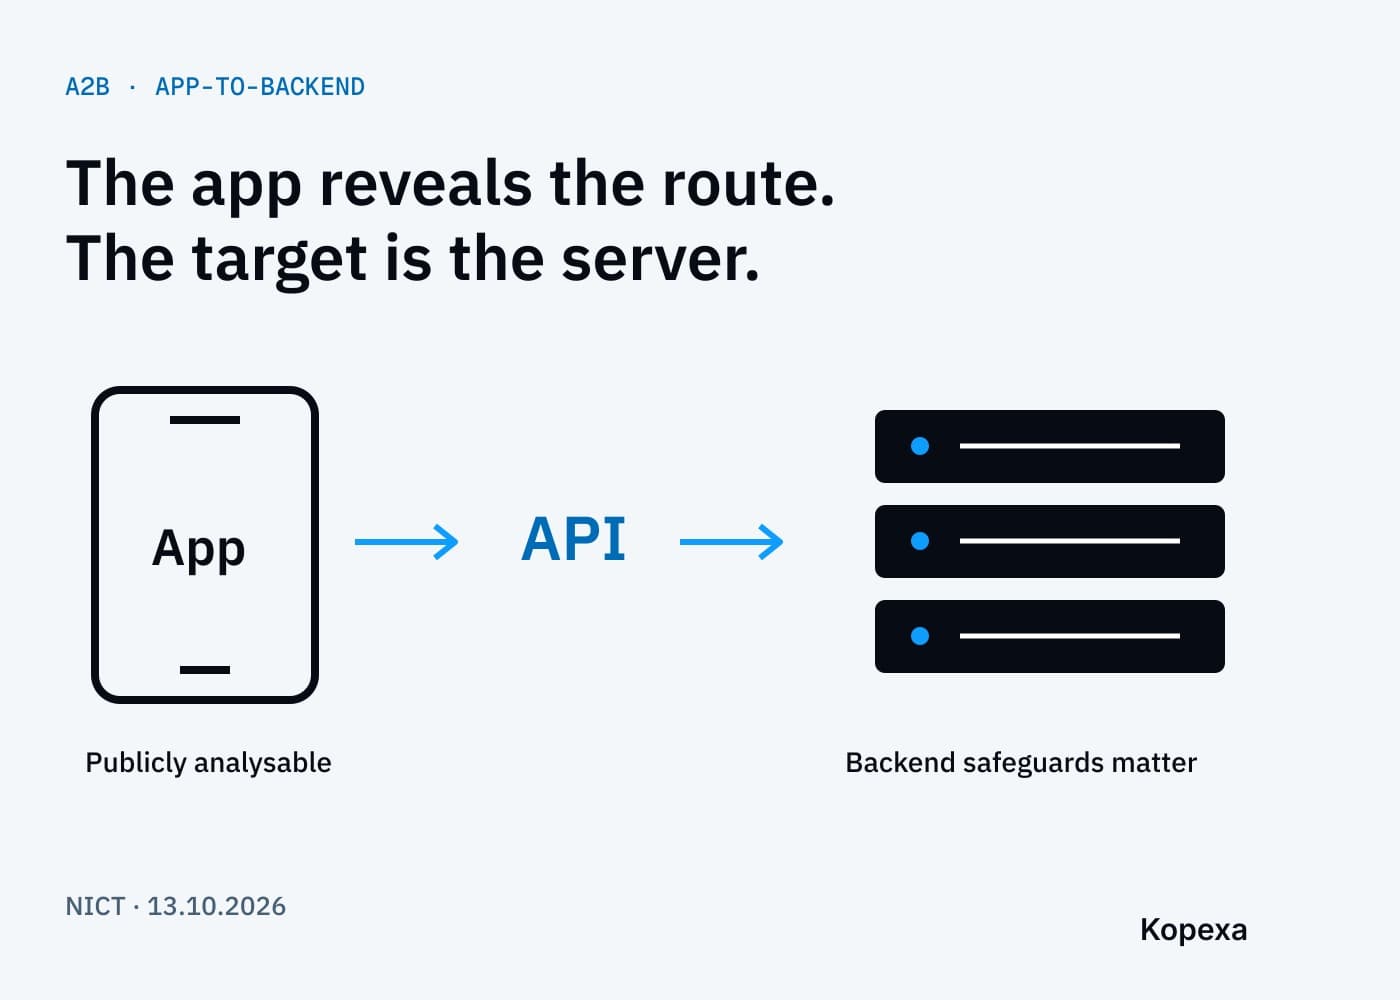
NICT warns of A2B attacks: an app can reveal the route to its server
A new NICT warning describes backend attacks informed by public Android apps. The risk is not confined to the app itself.
Julian Köhn·
October Patch Tuesday: exploited Windows Shell flaw takes priority
The October update cycle includes an exploited Windows Shell flaw. Why affected assets and verified remediation matter more than record counts.
Julian Köhn·
Ransomware in Japan: Cloud attack affects 495 organisations
IDC Frontier confirms ransomware at IDCF Cloud. Verified facts about the disruption, backups and Japan’s response, without assuming AI caused the attack.
Julian Köhn·
Meta’s GitHub data breach: How far can a stolen account reach?
Stolen credentials opened Meta’s GitHub repositories. What businesses should check across access rights, secrets, test data and incident response.
Julian Köhn·
Smart glasses: EDPB calls for clear recording indicators
The EDPB published its smart-glasses statement on 13 October. The focus is unnoticed recording and the responsibilities of users and service providers.
Julian Köhn·
Running Matomo in a Privacy-Compliant Way: How to Do It Without a Cookie Banner
Configure cookieless Matomo: JavaScript, Tag Manager, IP masking and privacy notice, with real screenshots and a German privacy-law assessment.
Julian Köhn·
DevOps & GDPR: Anonymising Data Automatically
How to maintain GDPR compliance in DevOps: automated anonymisation and pseudonymisation, PostgreSQL RLS/data masking, CI/CD integration for risk-free testing.
Julian Köhn·