91–99 of 178 articles
By publication date
ConnectWise/SkyKick: Your backup is there. Can you actually restore it?
What the ConnectWise Cloud Backup interruption means for Microsoft 365 customers: assess tenant investigation, backup gaps and recovery separately.
 Julian Köhn·
Supplier audits: turn a yes answer into reliable evidence
Examine a specific service, not just questionnaire answers. With an audit brief, evidence sample and findings record for information security.
Julian Köhn·
AI agent attempts a supply-chain attack: the AISI case
An AI agent tried to introduce malicious code into a GitHub project. What the new AISI and Anthropic analyses mean for access and approvals.
Julian Köhn·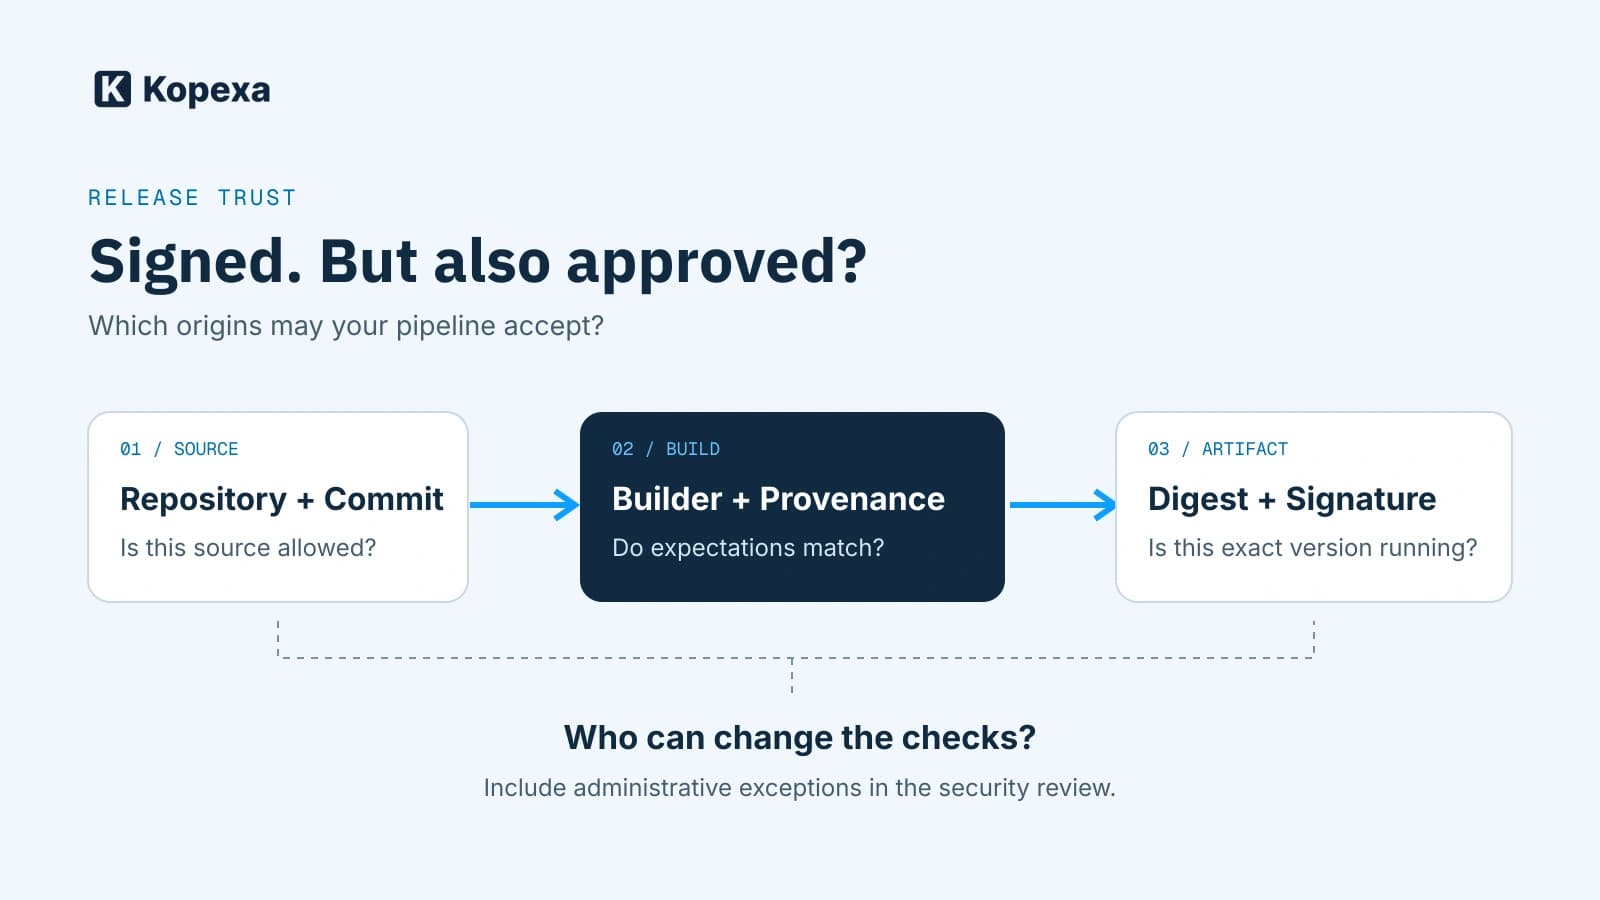
What the LiteLLM incident reveals about secure releases
Why a valid signature is not enough for release approval: verify provenance, restrict administrative exceptions and test recovery. A CTO perspective.
Julian Köhn·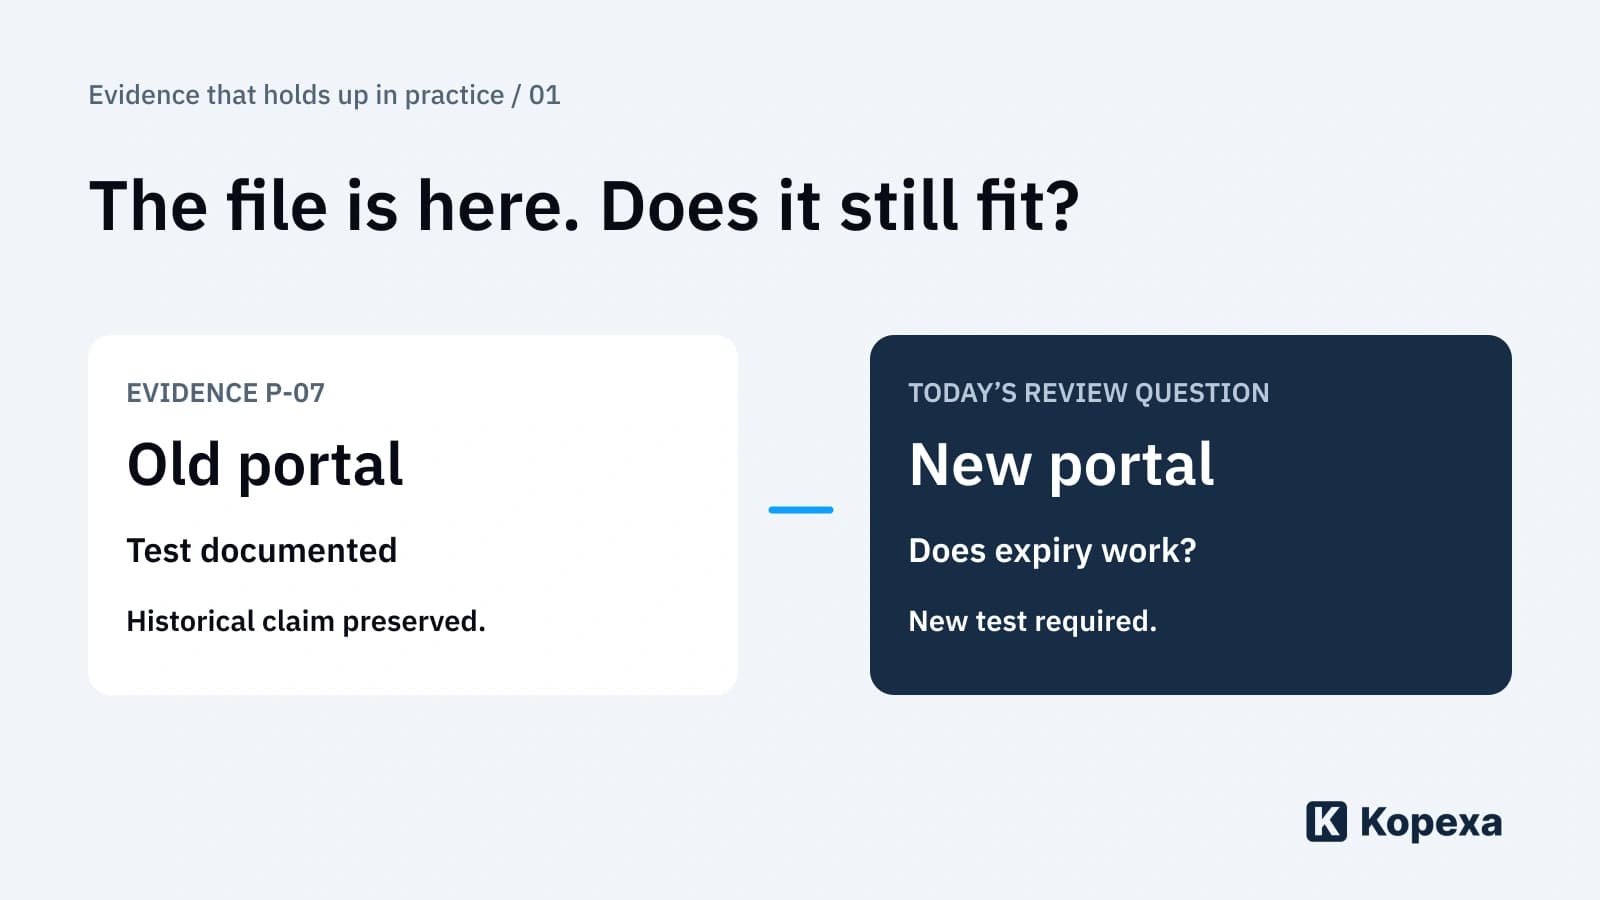
How much ongoing maintenance does ISMS software need?
Which ISMS tasks stay with your team, and what can be automated? Test evidence maintenance, policy reviews and multiple standards through a real workflow.
Julian Köhn·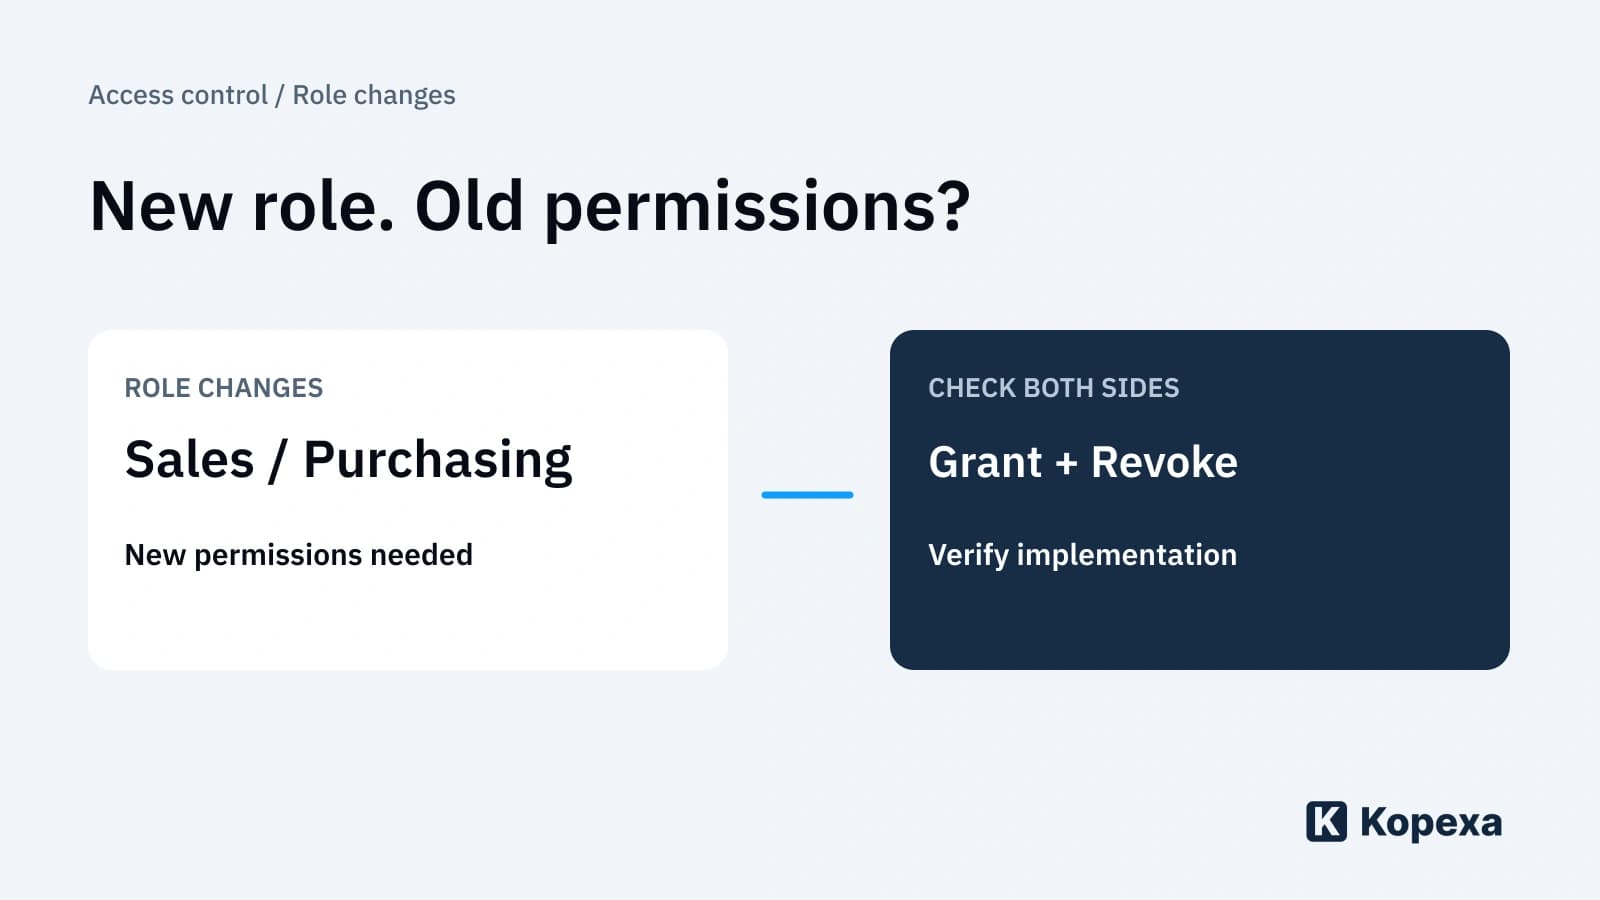
Creating an access control policy: who can do what, and who checks?
Use a role matrix and review record to manage joiners, movers and leavers. Turn an access list into a process you can verify.
Julian Köhn·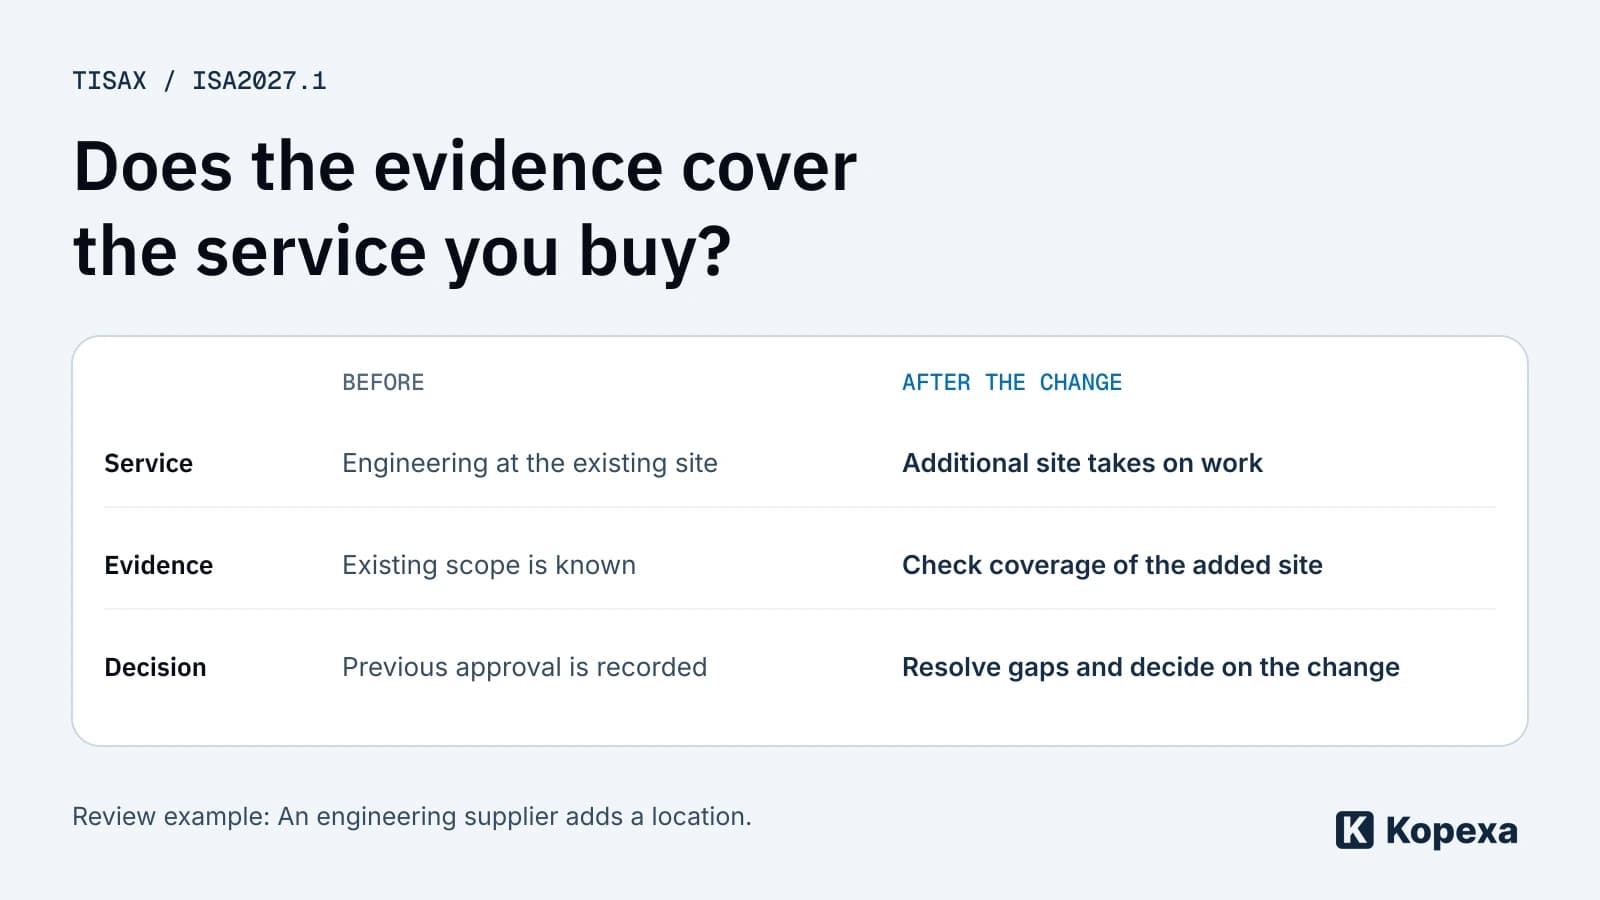
TISAX ISA2027: Prepare your supplier security review
Does supplier evidence cover the service you actually buy? Prepare for ISA2027 with a practical review example and a change register.
Julian Köhn·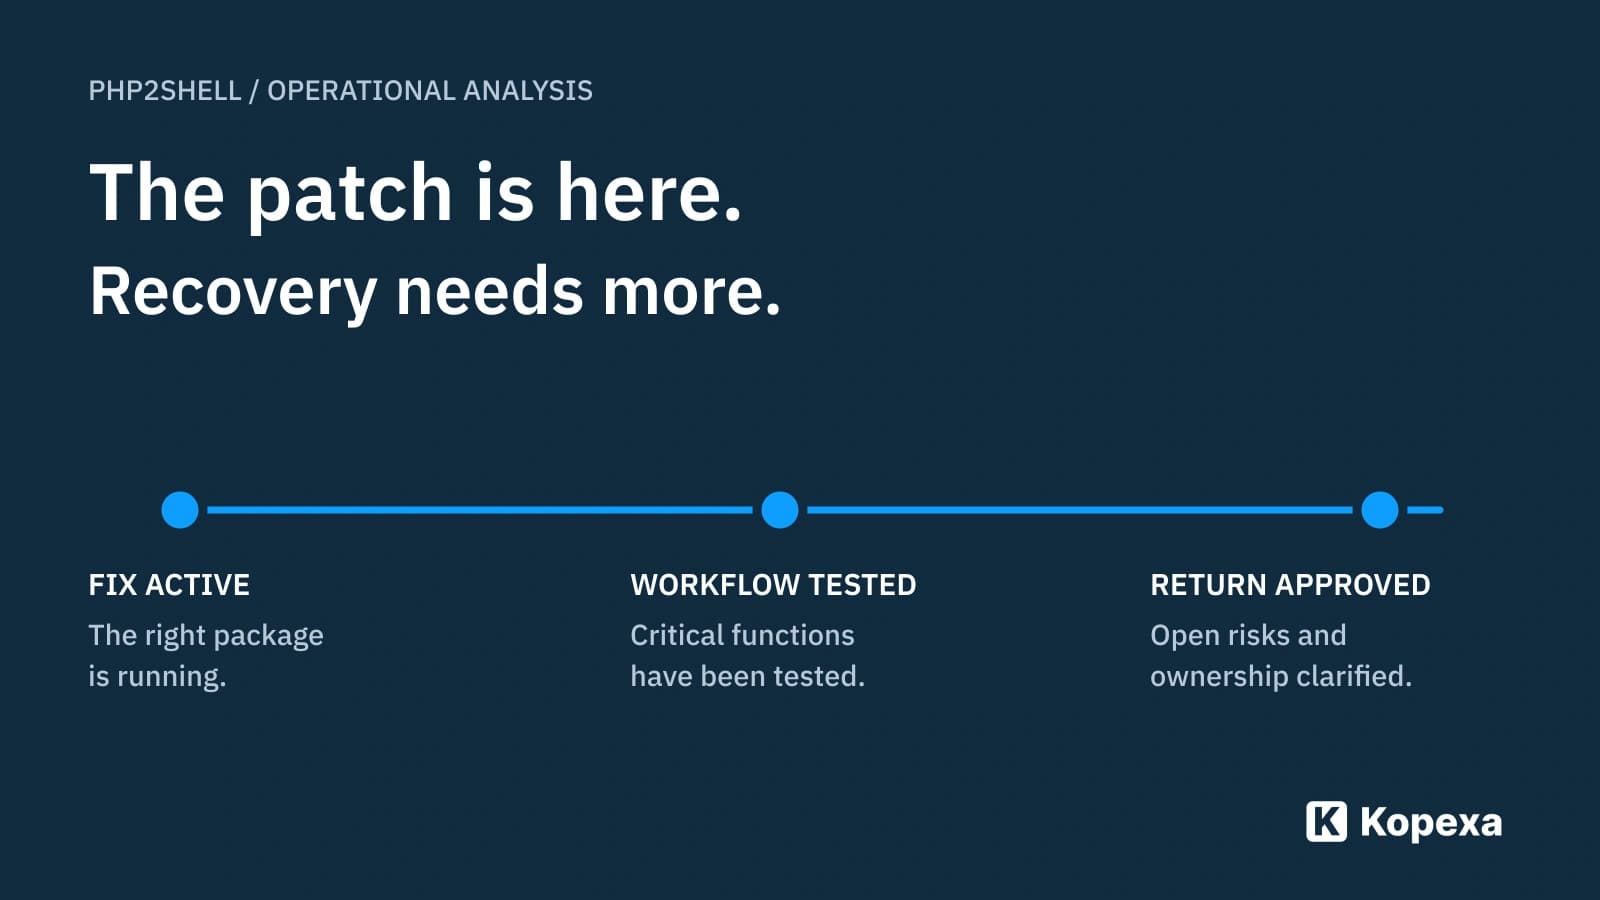
PHP2Shell: why some websites stay offline longer
PHP2Shell also affects current PHP releases. For legacy applications, unsupported components and dependencies can delay a safe return to service.
Julian Köhn·
Introducing a new policy version: approval and acknowledgement
Take a revised policy from expert review into everyday work. With a rollout plan covering version, audience, acknowledgement and outstanding tasks.
Julian Köhn·