109–117 of 178 articles
By publication date
Dealership data breach: supplier assurance needs more than a certificate
The GeNesys breach highlights digital supply-chain risk. How to check TISAX scope, current evidence and operational information security.
 Julian Köhn·
Ahold Delhaize begins controlled restart after cyber incident
Ahold Delhaize is restarting certain systems after a cyber incident while stores remain open. What the retailer has confirmed.
Julian Köhn·
AhsayCBS: attackers target backup servers; hotfixes available
Attacks on AhsayCBS highlight the need to protect backup management itself. The vendor and Huntress report available hotfixes and compromise guidance.
Julian Köhn·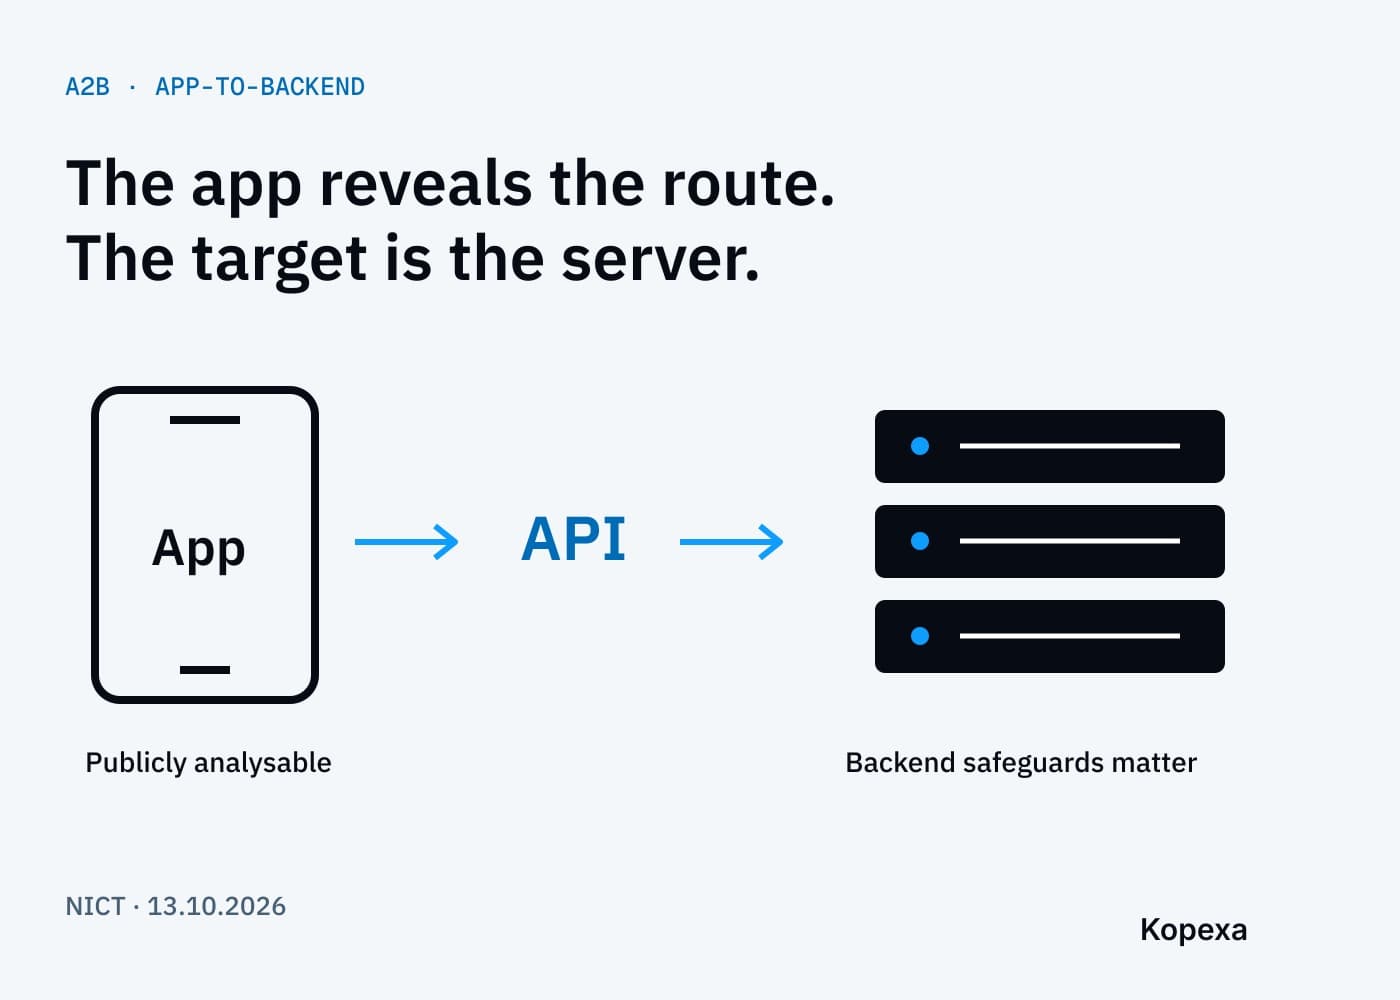
NICT warns of A2B attacks: an app can reveal the route to its server
A new NICT warning describes backend attacks informed by public Android apps. The risk is not confined to the app itself.
Julian Köhn·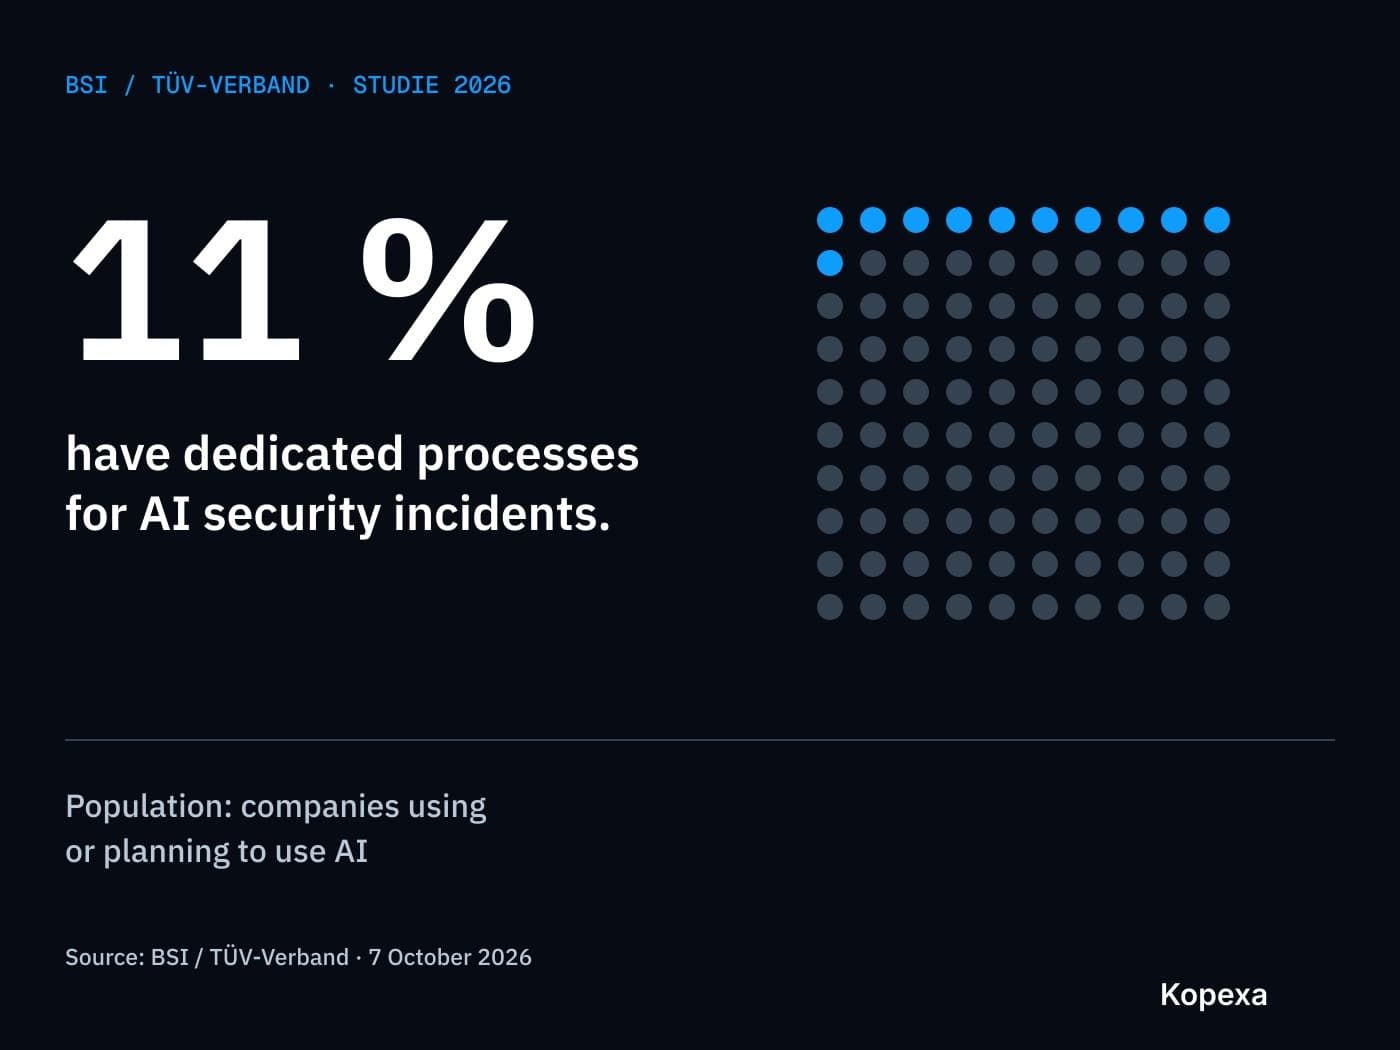
BSI/TÜV study: only 11% have dedicated AI incident processes
The 2026 AI security study identifies gaps in organisational preparation. What the 11% figure means and who was surveyed.
Julian Köhn·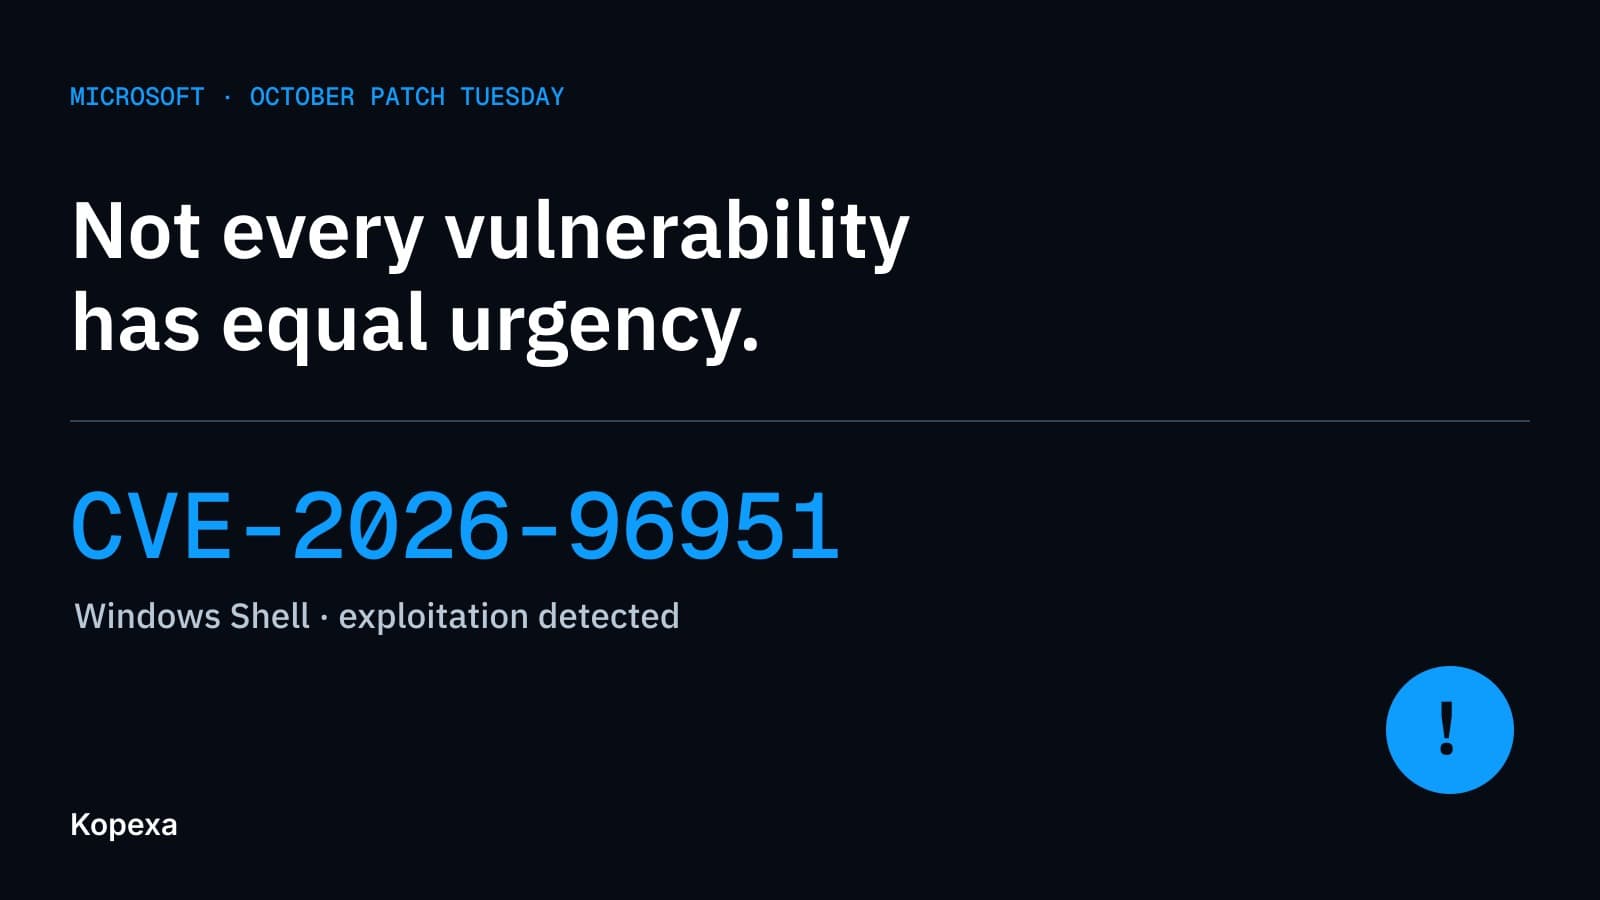
October Patch Tuesday: exploited Windows Shell flaw takes priority
The October update cycle includes an exploited Windows Shell flaw. Why affected assets and verified remediation matter more than record counts.
Julian Köhn·
Fehmarnbelt cyber incident: Can your business work without central IT?
The incident at tunnel contractor FLC raises a continuity question. Review time-critical processes, fallback procedures and recovery priorities.
Julian Köhn·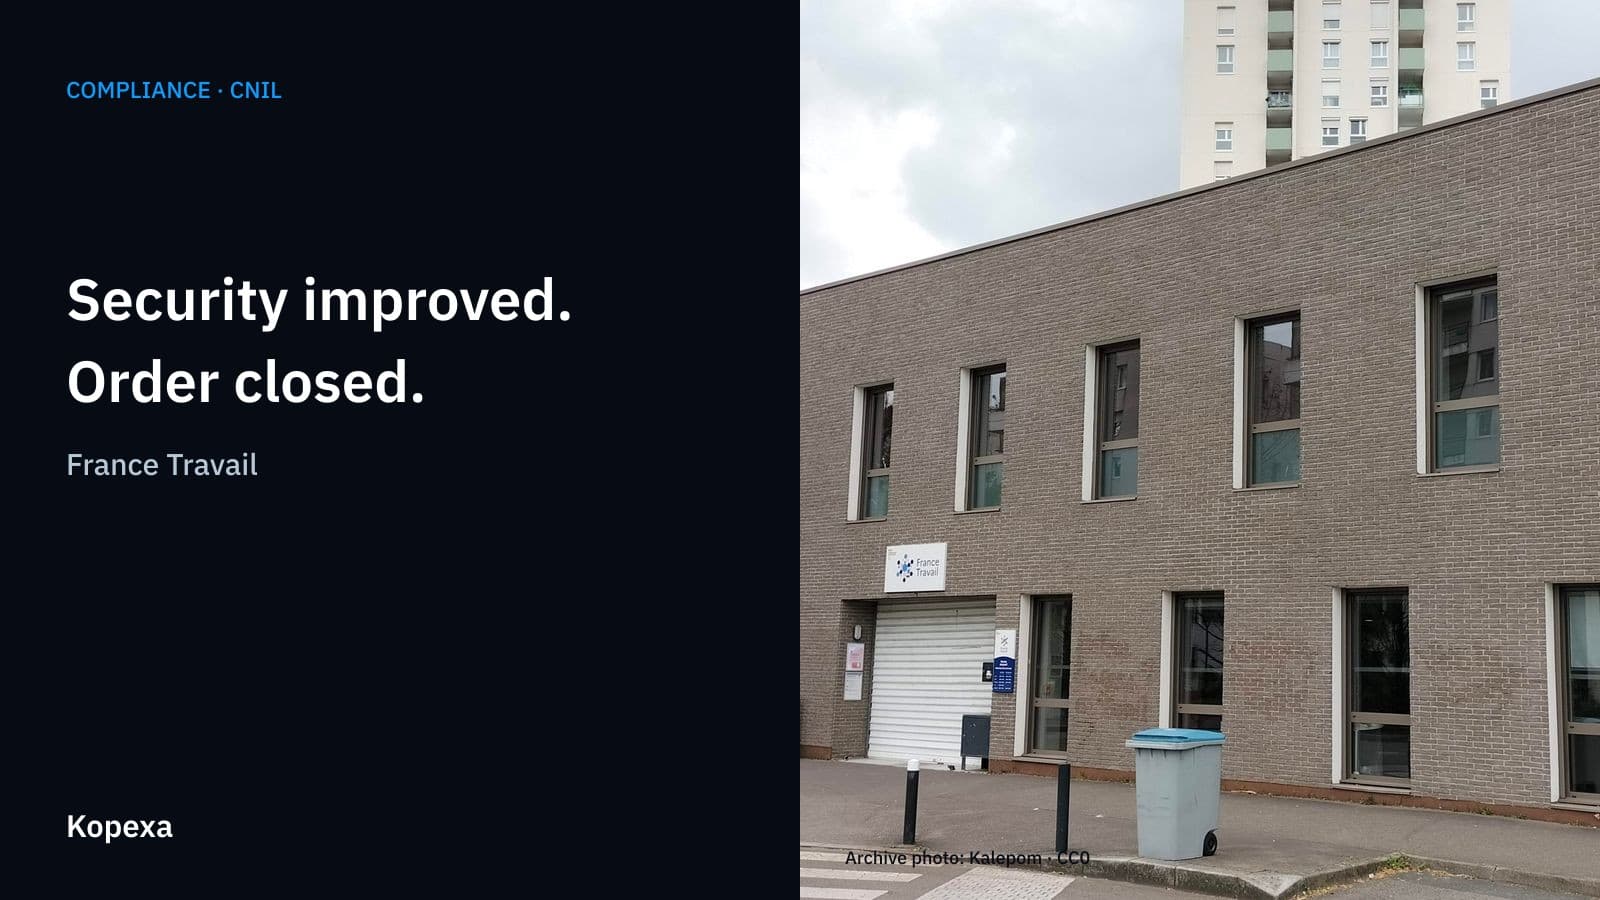
France Travail: CNIL closes order following security improvements
France Travail has demonstrated the required security improvements. CNIL closes its order: what changed and what the decision means.
Julian Köhn·
Ransomware in Japan: Cloud attack affects 495 organisations
IDC Frontier confirms ransomware at IDCF Cloud. Verified facts about the disruption, backups and Japan’s response, without assuming AI caused the attack.
Julian Köhn·