News
Crédit Mutuel Arkéa: Cyberattack through a service provider
The bank confirms fraudulent transfers following an attack through a provider. What is known, why the final loss remains unclear and what organisations can review.
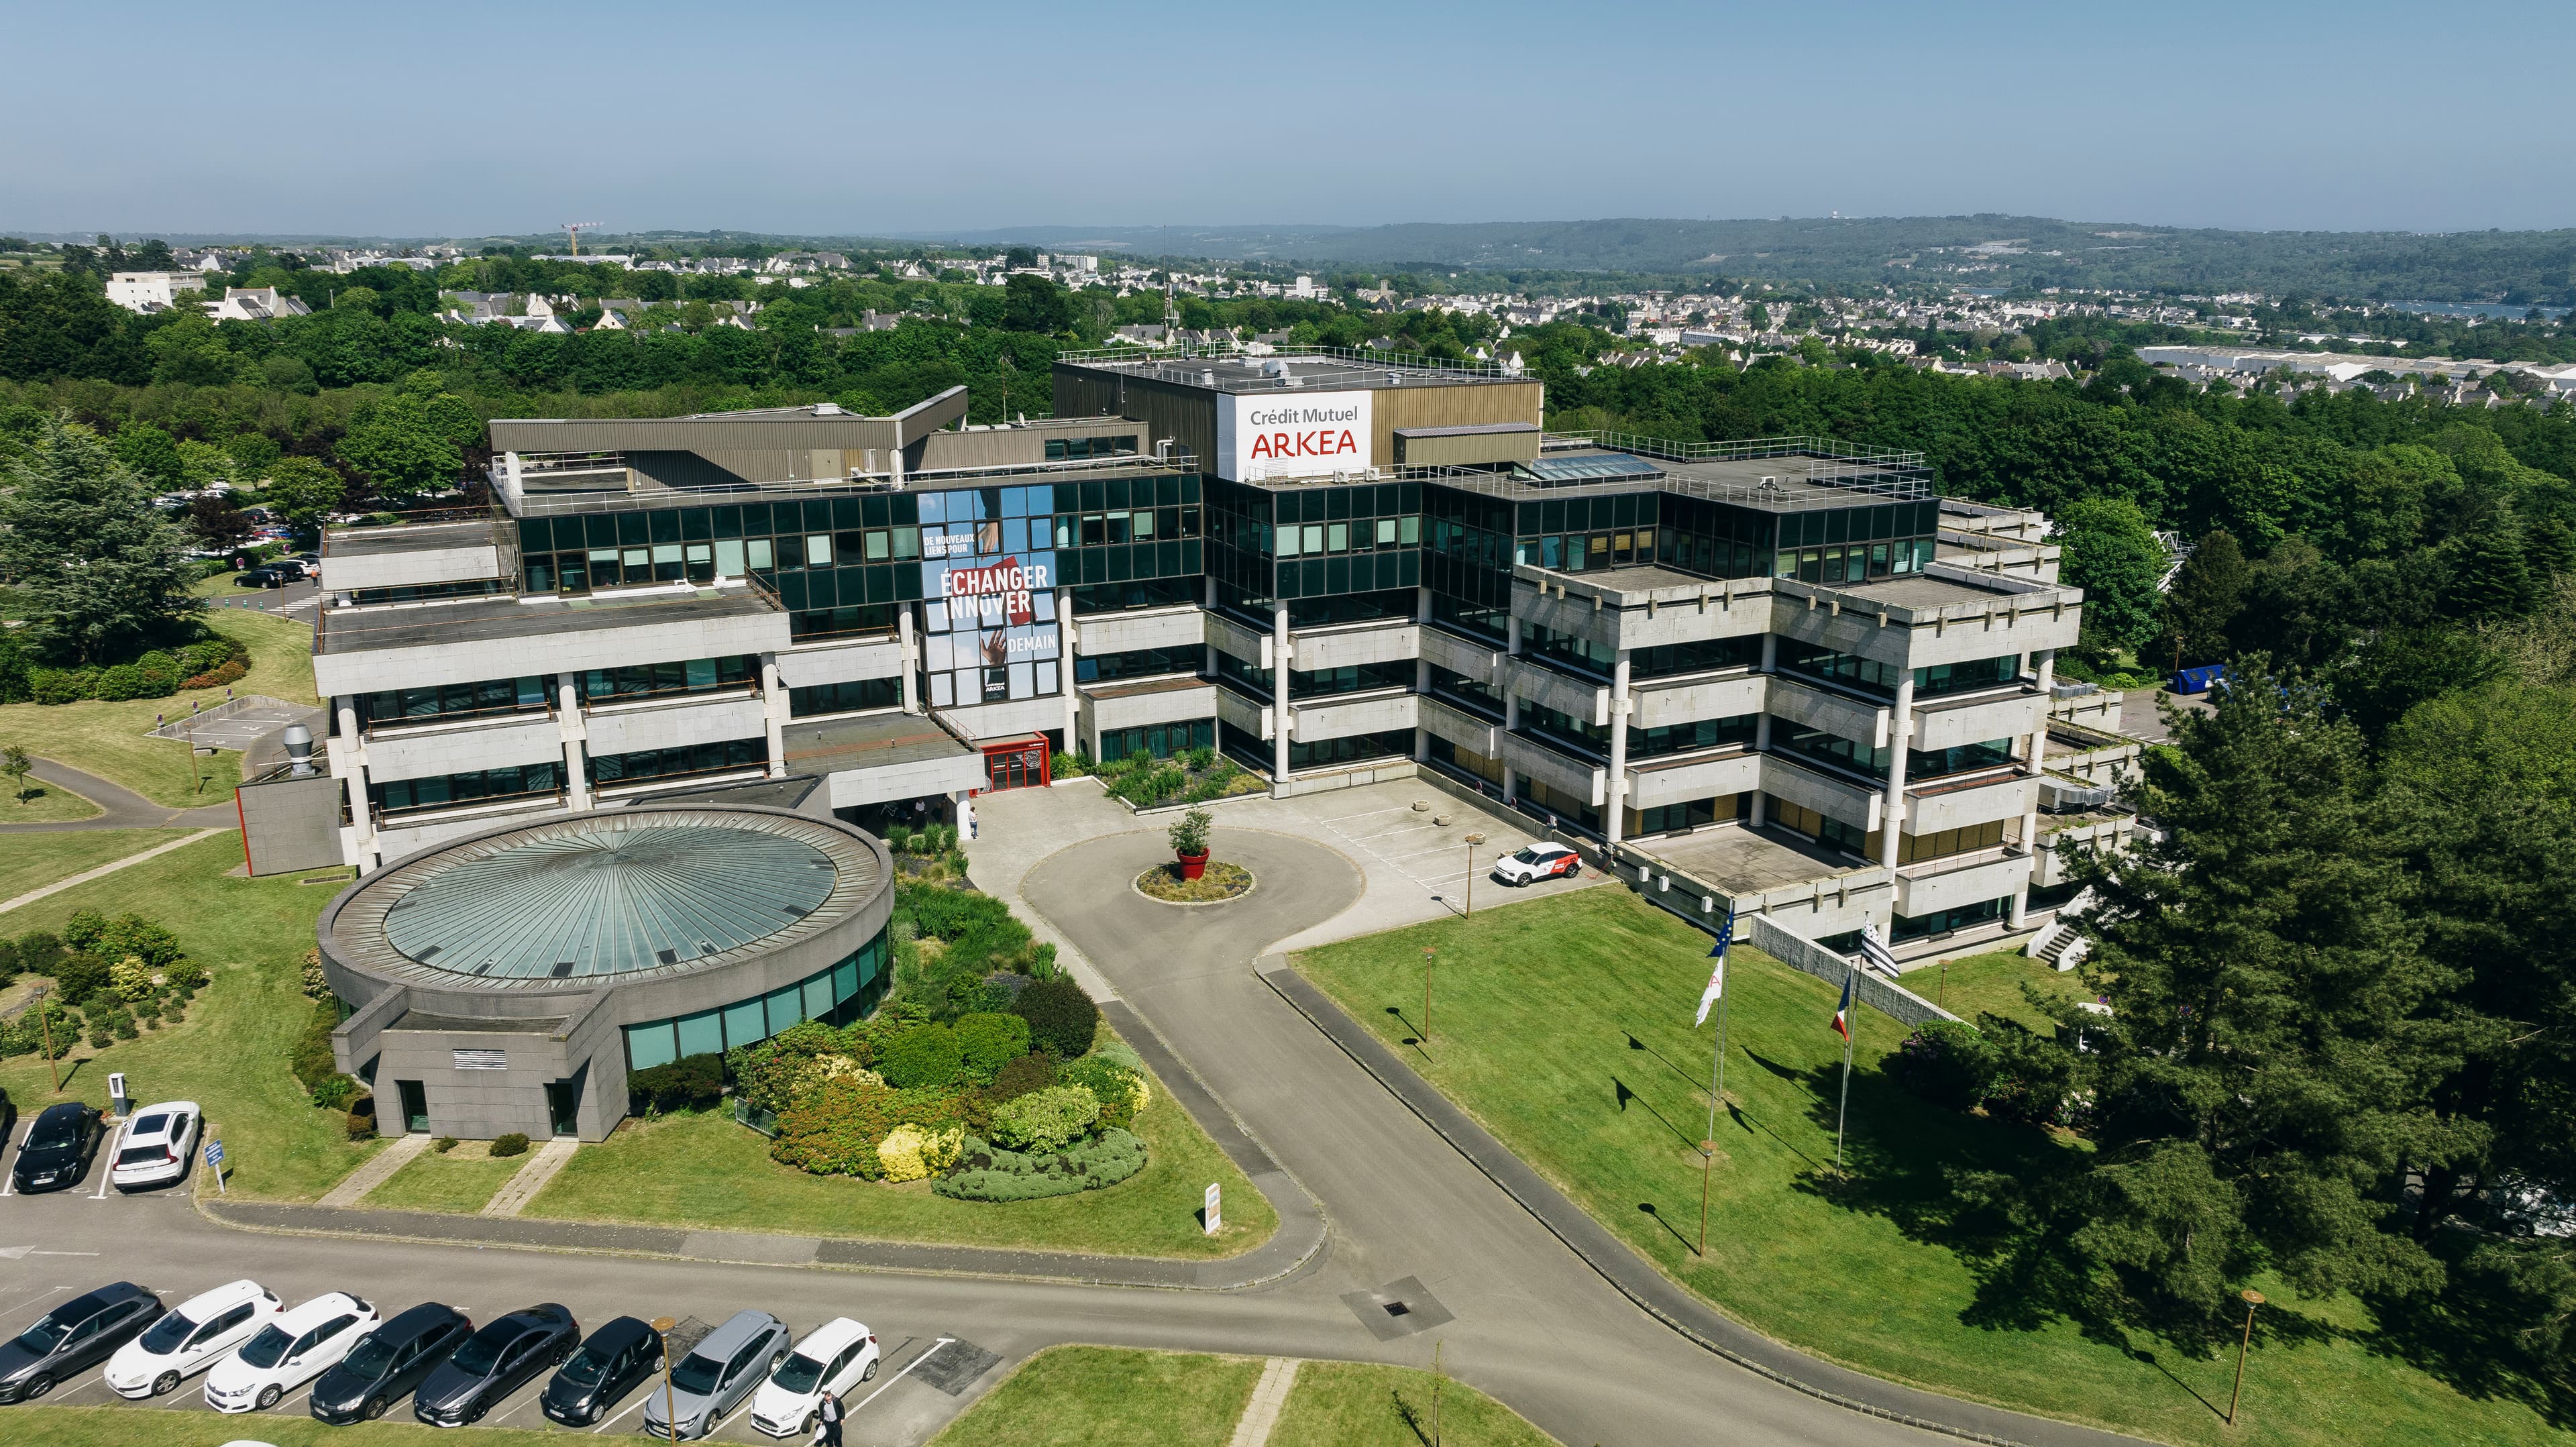
Crédit Mutuel Arkéa headquarters in Le Relecq-Kerhuon, archive photograph taken on 21 September 2023. Photo: Focale fixe / FJaffres, Wikimedia Commons, CC BY-SA 4.0.

Crédit Mutuel Arkéa confirmed a cyberattack on 4 November that enabled fraudulent transfers. Deutschlandfunk reports fears of losses exceeding 100 million euros. The final loss has not yet been established.
What is known about the attack
According to the bank's follow-up statement, the attackers reached Arkéa through an external provider. They used the bank's own account for transactions to other banks. Arkéa describes a subsequent conversion into cryptocurrency as a possible further step. On 4 November, the bank also reported containment and the resumption of most operations.
The initial statement says some transactions were suspended as a precaution. Customers' assets were unaffected, although some transfers were delayed.
AFP also reports an investigation by the Paris public prosecutor's office. Neither the attackers nor a specific exploited vulnerability have been publicly identified.
The loss estimate remains provisional
The bank has not confirmed a final loss figure. It points to blocked funds and ongoing recovery efforts. Affected transactions and the eventual loss must therefore be considered separately.
That distinction also belongs in an organisation's own incident response: record affected amounts, document funds already secured separately, and update the assessment as evidence develops. An early estimate should not silently become the final loss figure.
Our assessment: What can the provider's access actually do?
For other organisations, the relevant aspect is that entry was through an external platform. An external service with the relevant permissions can affect financial operations. The published information does not yet establish which access and approval controls were involved at Arkéa.
For your own review, we suggest three specific questions:
- What action does the external access enable? Reading data, changing bank details and initiating payments are different risks. The assessment should name the permitted actions.
- What independent control limits that action? For example, examine approvals, limits and anomaly detection against a specific transaction. A process name alone does not show that an unwanted transfer would be stopped.
- Who can disable the access during an incident? Record ownership, contact routes and the last tested procedure. A quick decision requires these details to be available.
This connects to ICT third-party risk management under DORA (German): financial entities must consider their dependencies throughout a service's lifecycle. Our DORA overview explains the wider requirements.
Keep the incident and decisions traceable
Kopexa brings supplier assessments, risks, measures and owners together. In a case like this, the task would be to identify the affected service, follow up unanswered questions with the provider and document decisions with supporting evidence. The responsible IT and finance teams implement the resulting decisions on access restrictions and approvals.
Our incident report template offers a practical starting point for recording the sequence of events, impacts and causes.
Sources
- Arkéa: Initial announcement of the attack — Crédit Mutuel Arkéa () [Accessed ]
- Arkéa: Additional information on the attack and financial impact — Crédit Mutuel Arkéa () [Accessed ]
- AFP: Bank reports cyberattack and fraudulent transactions — AFP () [Accessed ]
- Deutschlandfunk: Losses exceeding 100 million euros feared — Deutschlandfunk () [Accessed ]
- FMA: Managing ICT third-party risk under DORA — Austrian Financial Market Authority [Accessed ]