Topic in the Kopexa blog
Risk Management
Explore Risk Management: background information, practical examples and recent developments from the Kopexa blog.
1–10 of 16
VMware ESX: CVSS 2.7, yet known exploitation
CVE-2026-41709 concerns insufficient VMware ESX logging. Why its new KEV listing matters to patch and risk owners despite the low CVSS score.
 Julian Köhn·
Risk management software for financial services: Coordinate ICT risks
Distinguish ICT risk management from credit, market and liquidity risks. Includes a provider-dependency and risk-approval test case.
Julian Köhn·
Choosing risk management software: From assessment to decision
Choose risk management software using a decision case: test assessment methods, measure effectiveness, history and risk acceptance.
Julian Köhn·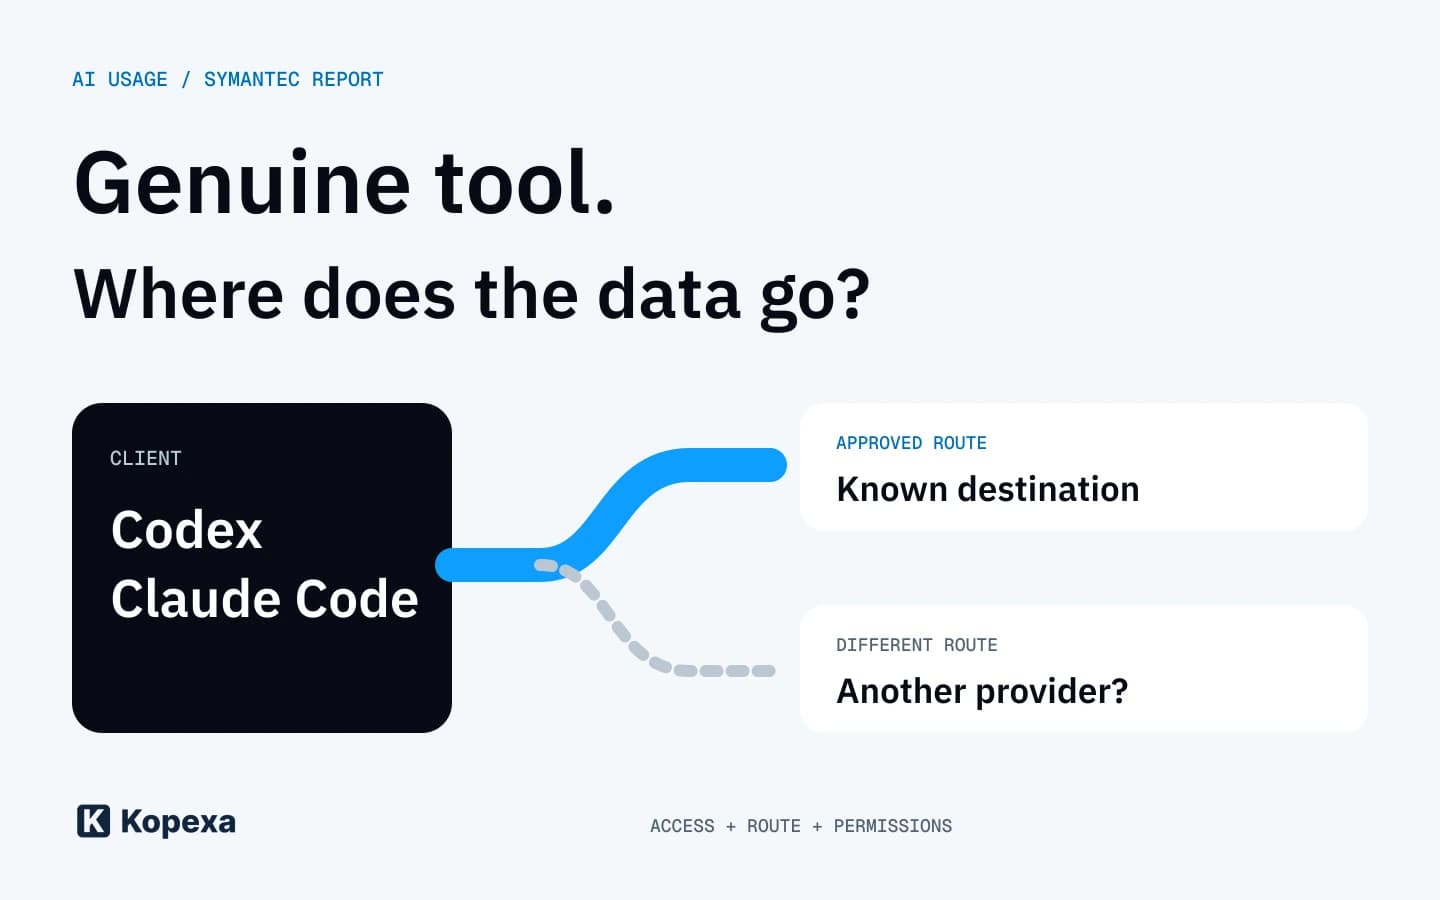
AI relays: Genuine tools, a different data route
Symantec warns about unofficial relays for Codex and Claude Code. Why AI approval needs to cover sourcing, destinations and permissions as well as the tool.
Julian Köhn·
curl: More security reports do not automatically make us safer
curl changes its reporting procedure from 26 October. A CTO’s view on taking real vulnerabilities seriously and turning reports into reasoned decisions.
Julian Köhn·
GitLab security update: More than a patch to your development platform
A critical GitLab vulnerability requires a verified update and a review of the release path. Check versions, credentials, runners and remaining incident questions.
Julian Köhn·
ConnectWise/SkyKick: Your backup is there. Can you actually restore it?
What the ConnectWise Cloud Backup interruption means for Microsoft 365 customers: assess tenant investigation, backup gaps and recovery separately.
Julian Köhn·
AI agent attempts a supply-chain attack: the AISI case
An AI agent tried to introduce malicious code into a GitHub project. What the new AISI and Anthropic analyses mean for access and approvals.
Julian Köhn·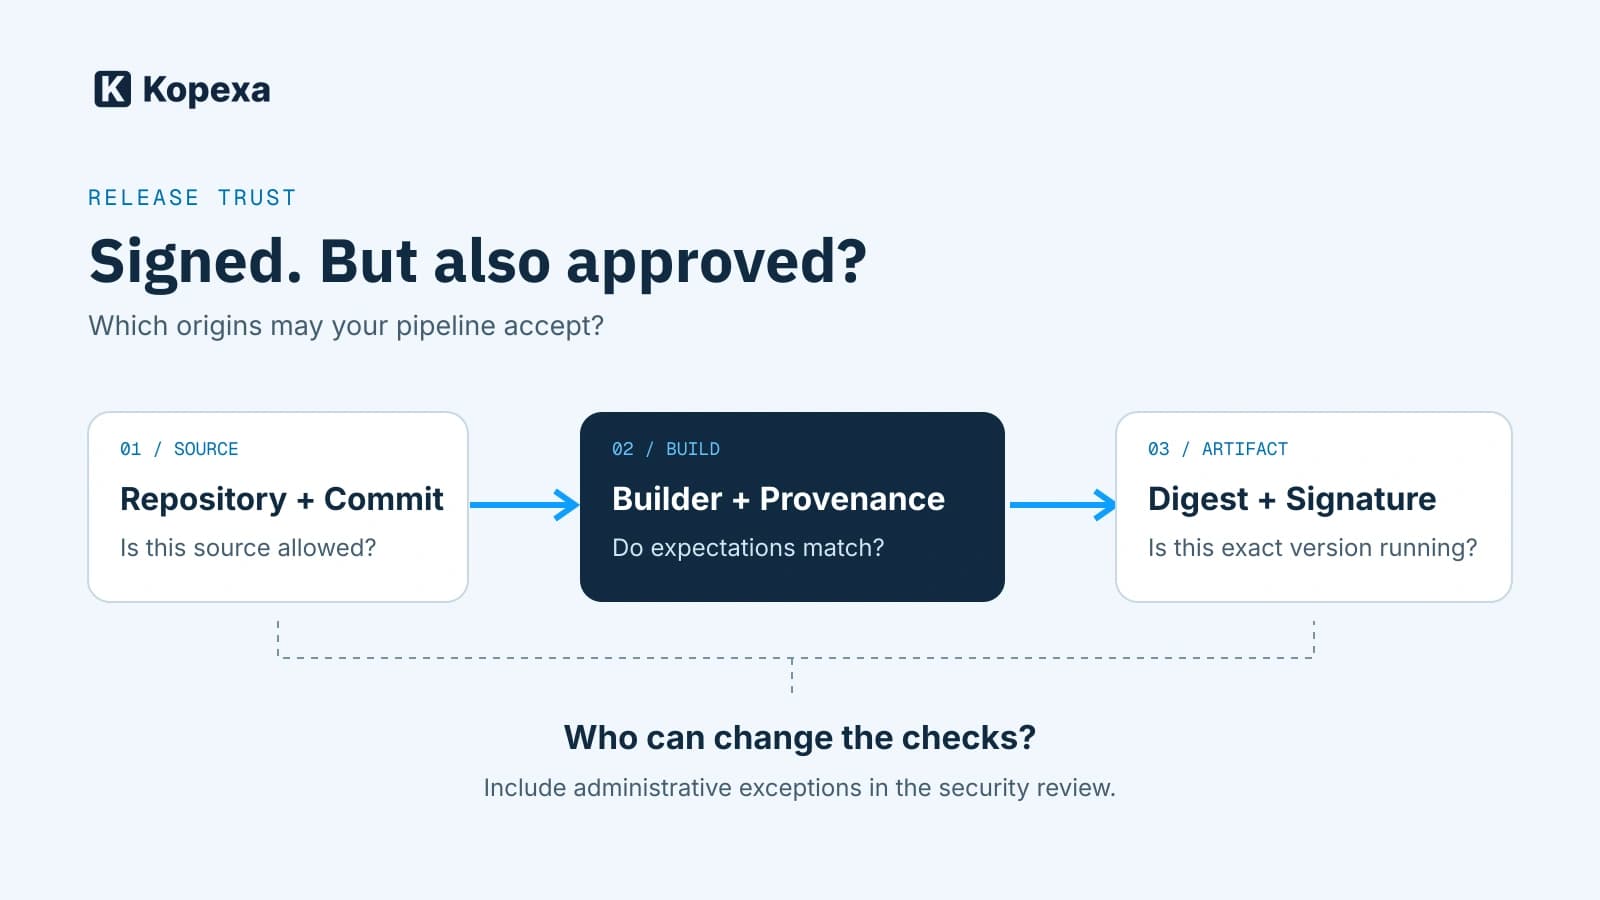
What the LiteLLM incident reveals about secure releases
Why a valid signature is not enough for release approval: verify provenance, restrict administrative exceptions and test recovery. A CTO perspective.
Julian Köhn·