1–9 of 33 articles
By publication date
Cyberattacks on law firms: When trust opens the door
CrowdStrike reports rising attacks on the legal sector. What the figures mean and how law firms can review remote access and protect client information.
 Julian Köhn·
VMware ESX: CVSS 2.7, yet known exploitation
CVE-2026-41709 concerns insufficient VMware ESX logging. Why its new KEV listing matters to patch and risk owners despite the low CVSS score.
Julian Köhn·
Searchjacked: When browser extensions reroute search queries
Socket reports search redirection through browser extensions. Why an official store is not enough, and how organizations can check extensions and data routes.
Julian Köhn·
WordPress update-process flaw: What to verify now
WordPress 7.1.4 fixes a flaw during Core updates. What operators and agencies should verify about the running version and completion of the update.
Julian Köhn·
AI relays: Genuine tools, a different data route
Symantec warns about unofficial relays for Codex and Claude Code. Why AI approval needs to cover sourcing, destinations and permissions as well as the tool.
Julian Köhn·
Japan Airlines: Customer data affected through Amadeus
Japan Airlines reports around 92,000 people affected by unauthorized access at Amadeus. Confirmed facts and the questions businesses should ask suppliers.
Julian Köhn·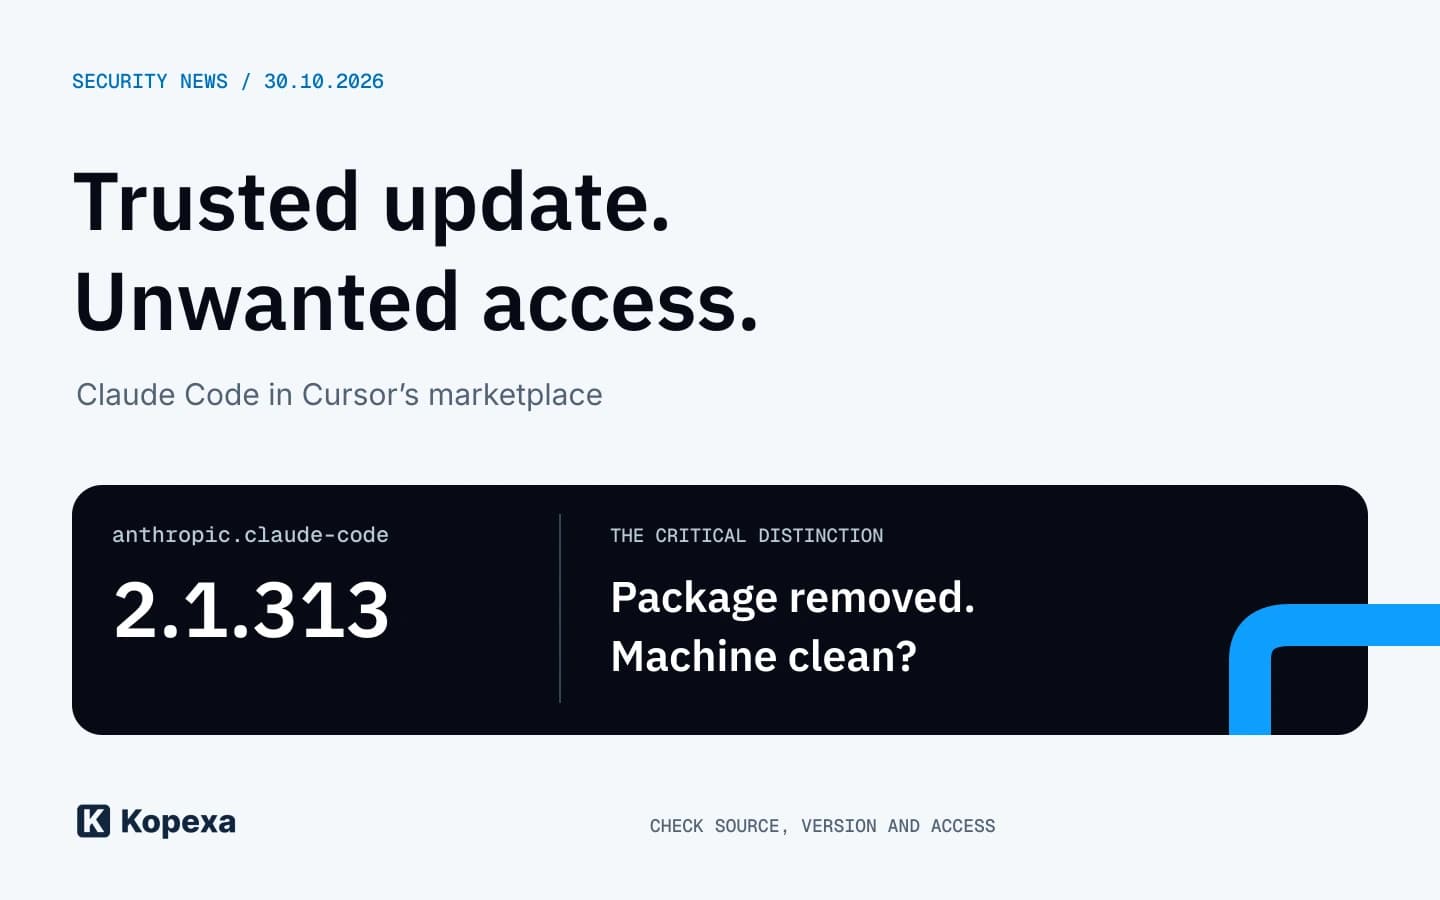
Claude Code tampered with in Cursor: Why an update is not enough
Malicious Claude Code extension 2.1.313 in Cursor’s marketplace: establish exposure, preserve SSH evidence and restore developer access with clear ownership.
Julian Köhn·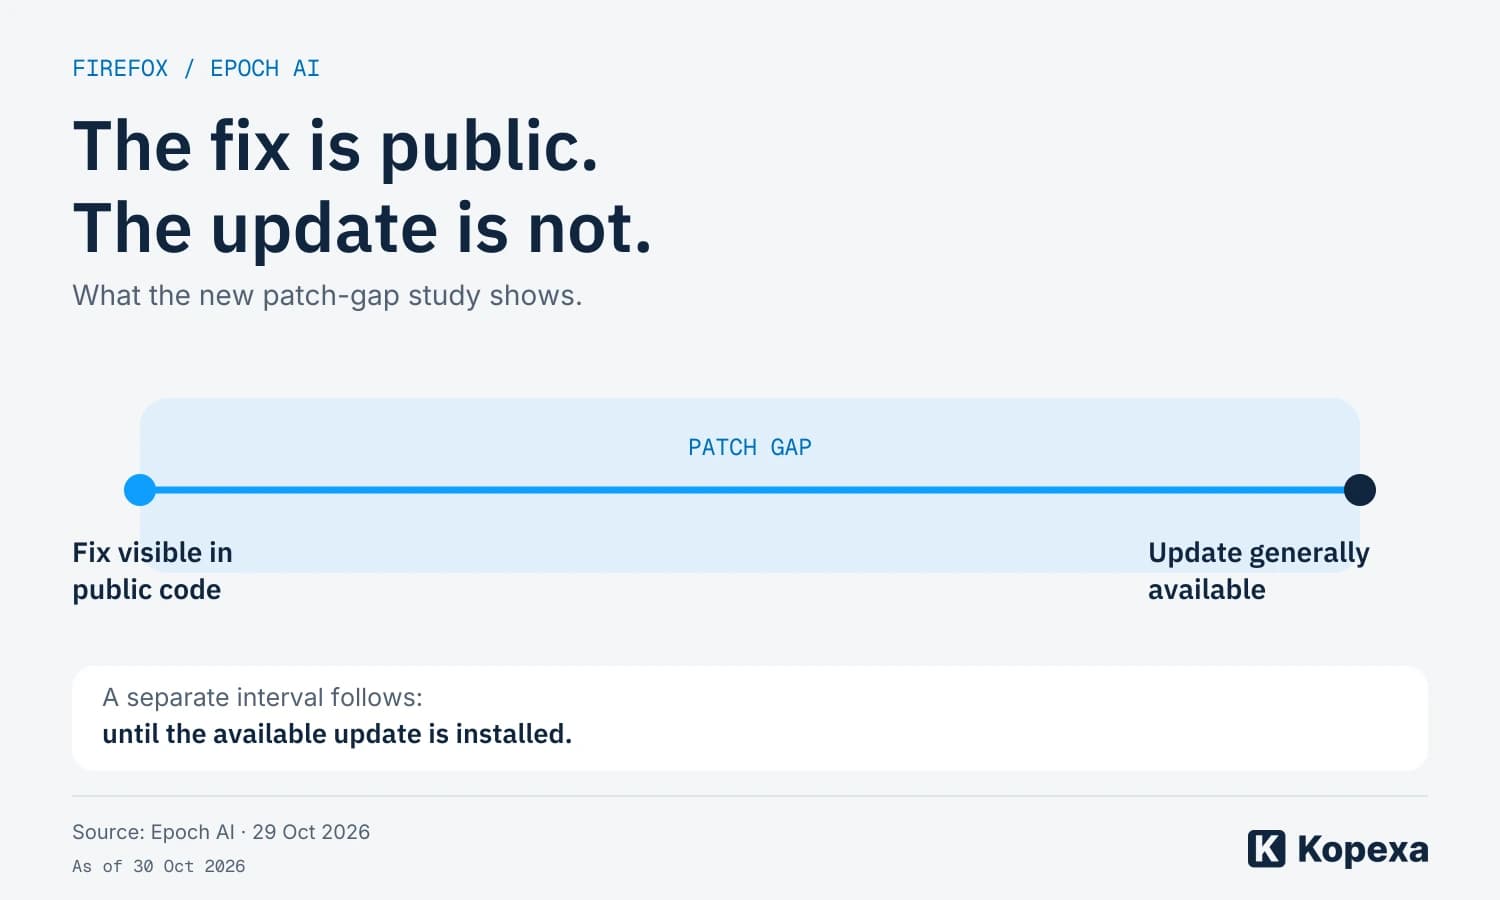
AI exploits in the Firefox patch gap: what Epoch AI shows
Epoch AI demonstrates file access through six Firefox releases. What Firefox 159 fixes and why public fixes, releases and installation are separate states.
Julian Köhn·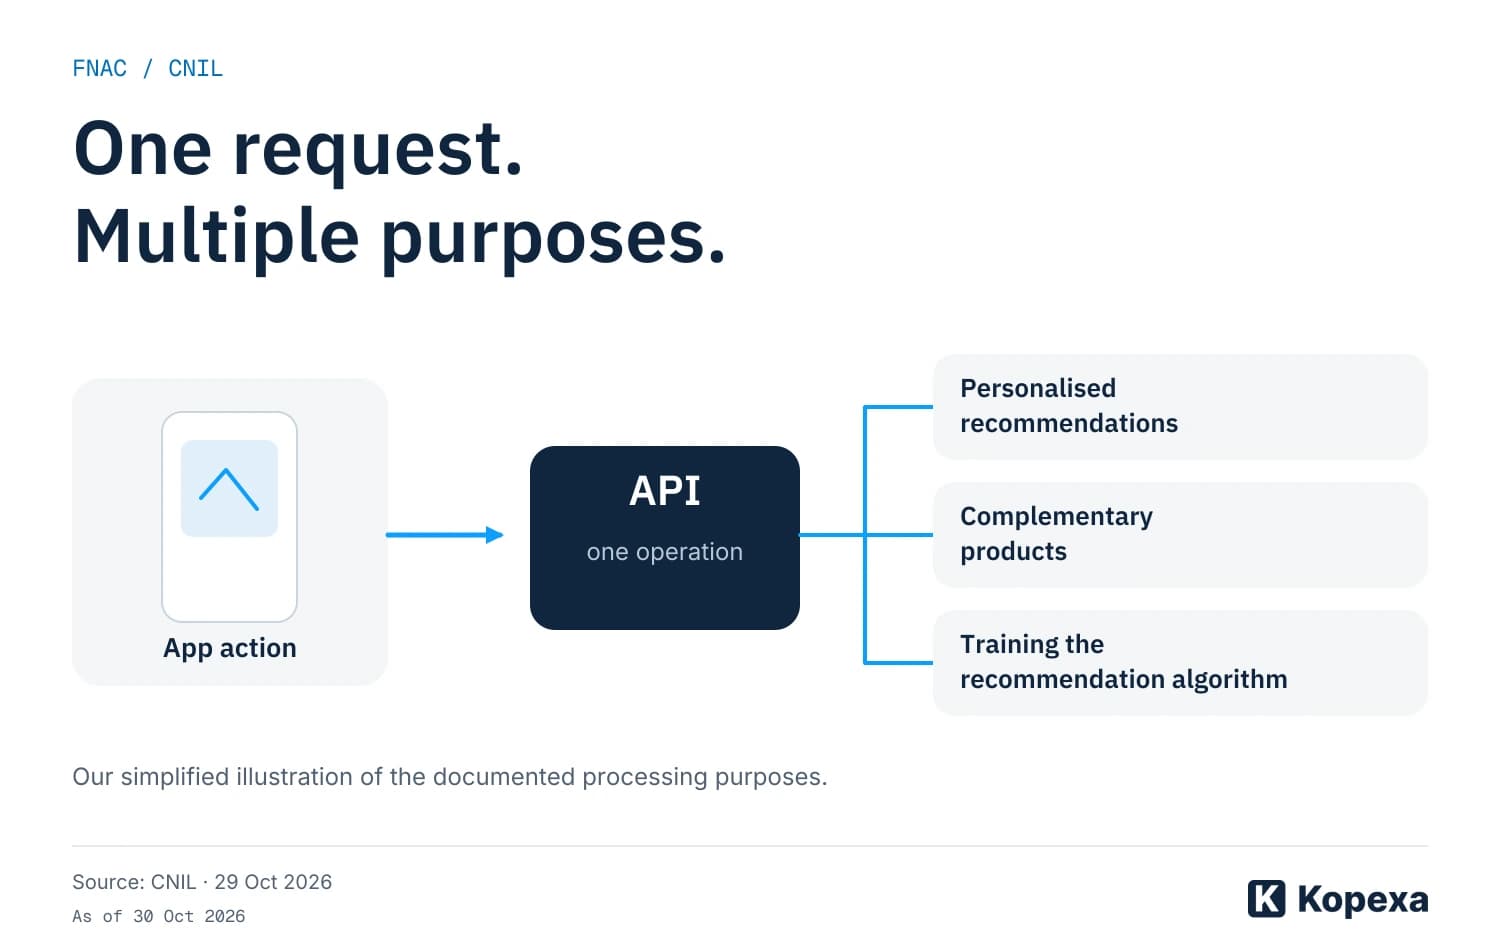
FNAC app: €7 million in fines for tracking after users declined
The CNIL has fined two FNAC companies. After users declined tracking, a multi-purpose API still processed data for product recommendations and training their recommendation algorithm.
Julian Köhn·