10–18 of 33 articles
By publication date
SECRA data breach: holiday accommodation access codes may also be affected
Access codes may be affected by the SECRA data breach. What is confirmed and how operators can check resets, property assignments and guest communication.
 Julian Köhn·
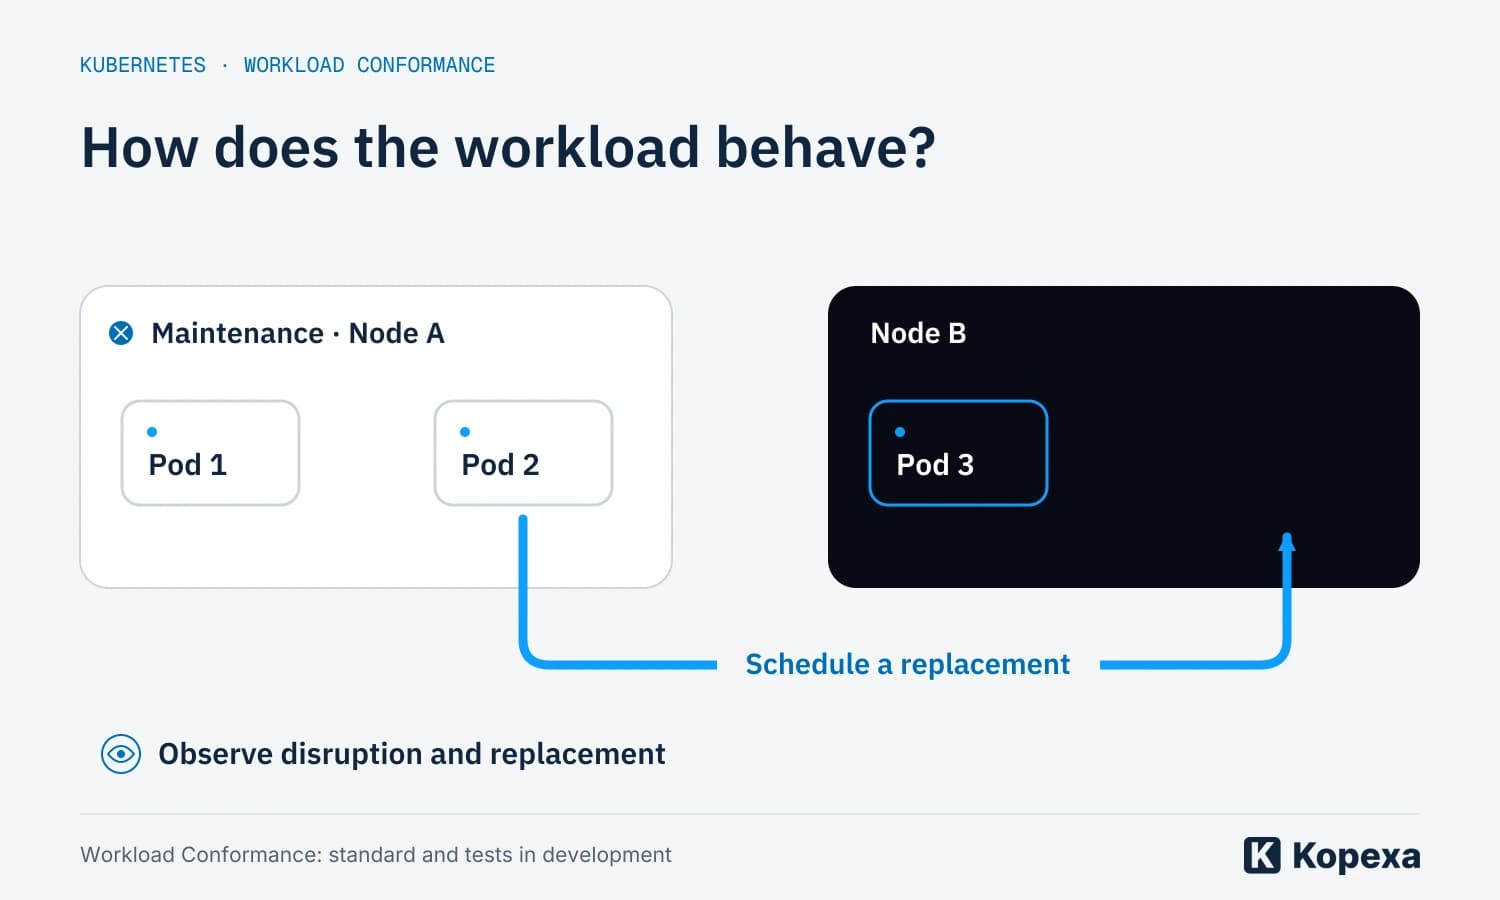
Kubernetes plans Workload Conformance: How resilient is your application?
Kubernetes plans shared runtime tests for applications. What Workload Conformance aims to change, what Kyverno can do today, and where native checks have limits.
Julian Köhn·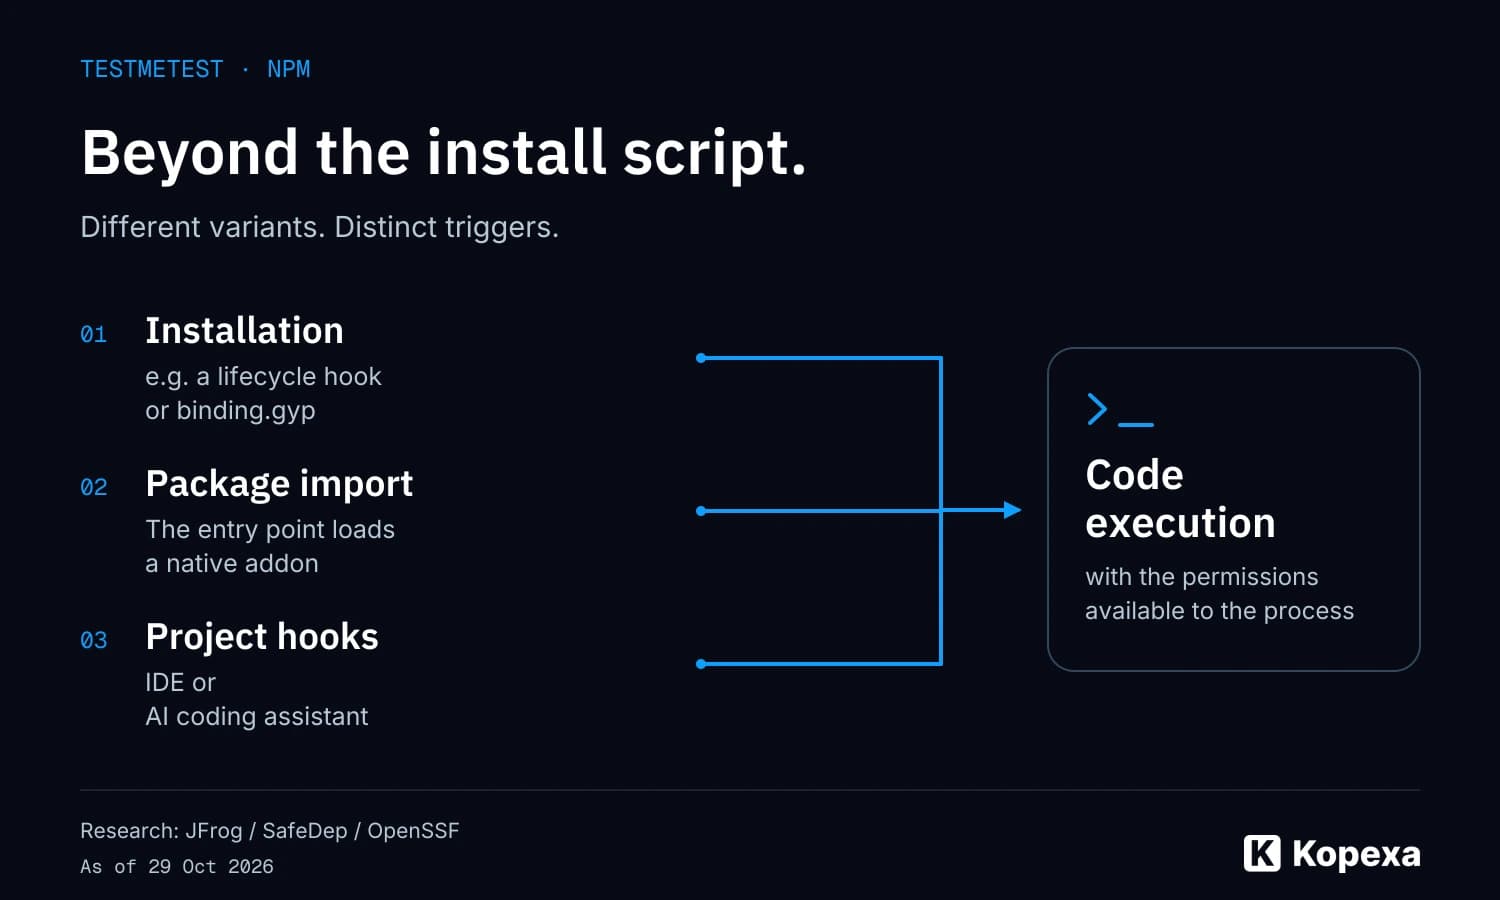
testmetest: 42 GitHub repositories armed for an npm worm
JFrog finds 42 armed GitHub repositories. How testmetest uses npm packages and project hooks, what has been removed and what teams should investigate.
Julian Köhn·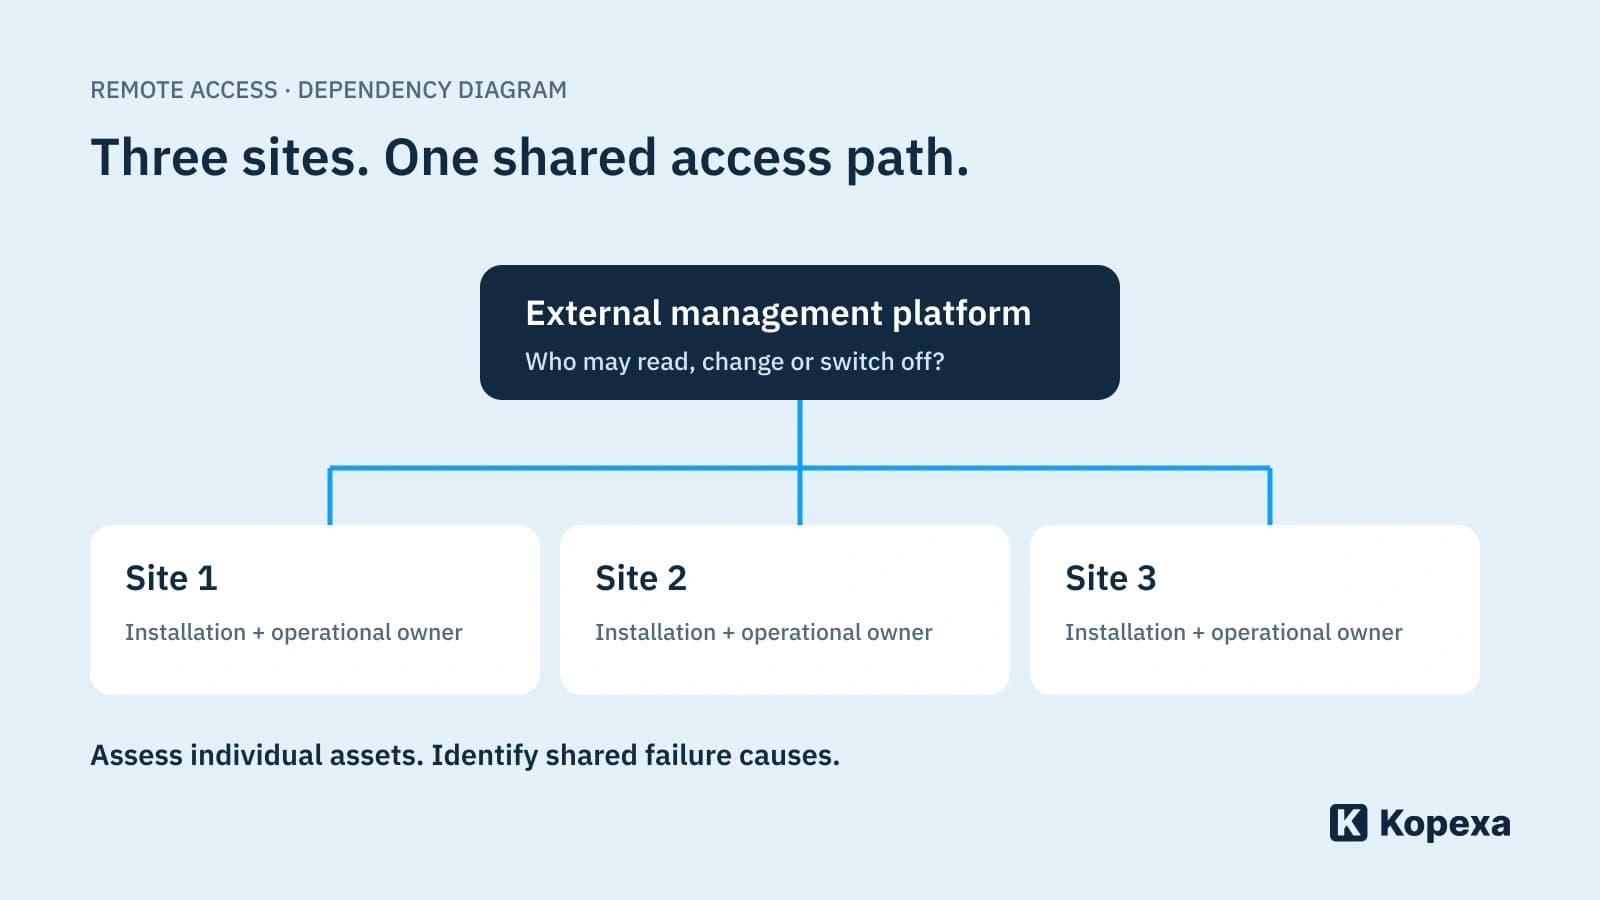
Sungrow: Who can control your equipment remotely?
The fixed iSolarCloud vulnerability illustrates an operational risk: central remote access to many installations. Review access, dependencies and fallback operation.
Julian Köhn·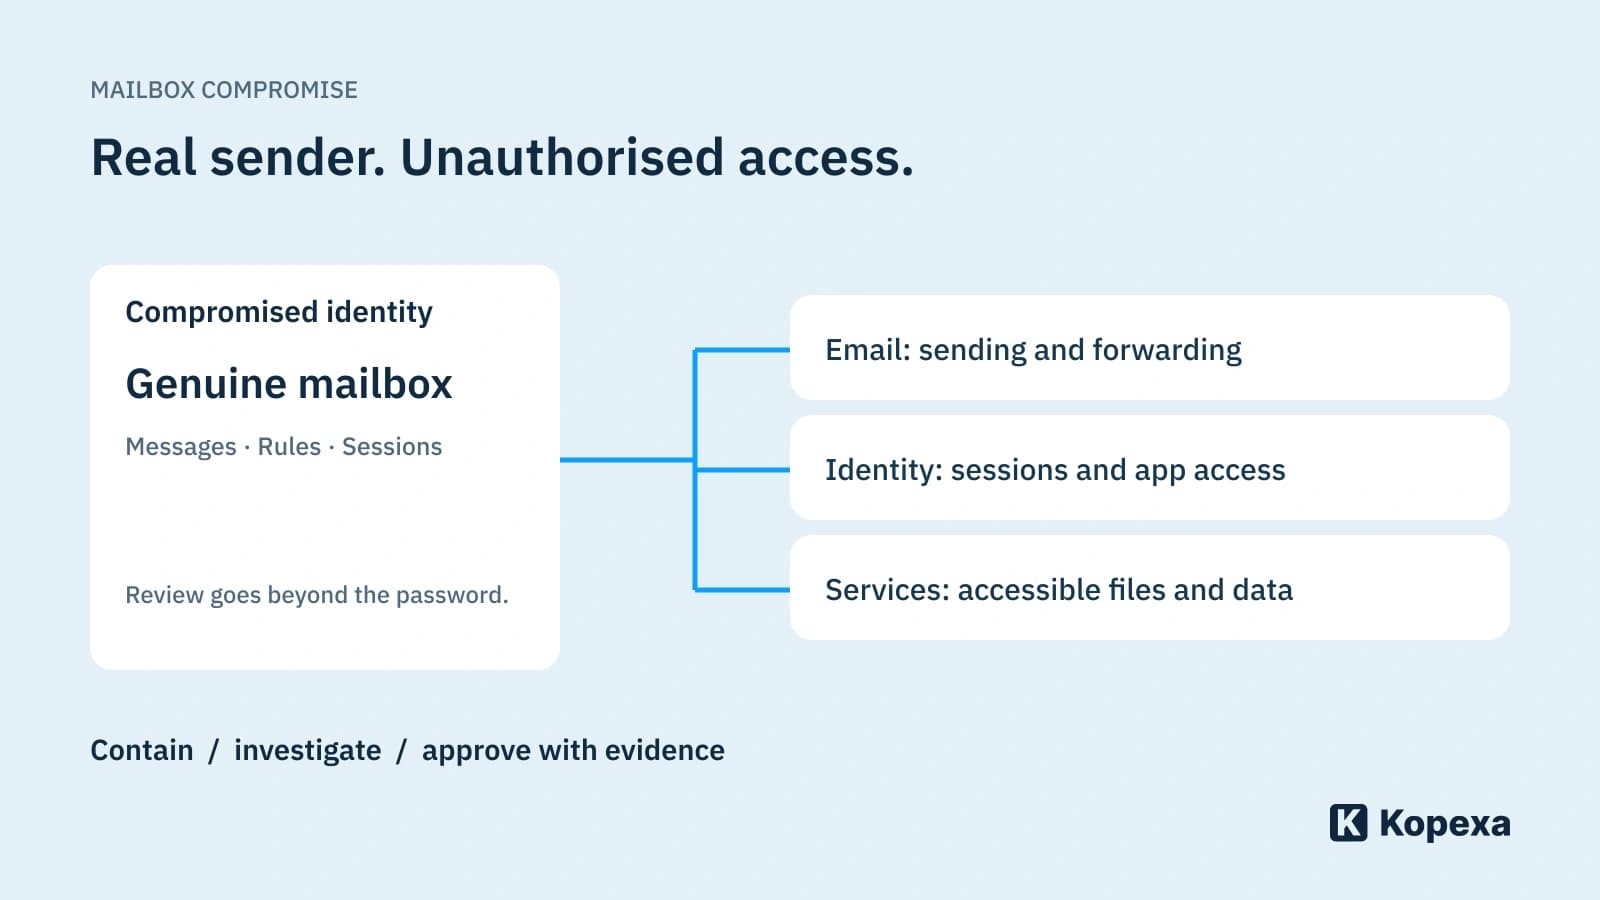
The phishing email comes from a real colleague. What now?
A compromised business mailbox makes the sender credible. Organise containment, investigation and a controlled return to work.
Julian Köhn·
GitLab security update: More than a patch to your development platform
A critical GitLab vulnerability requires a verified update and a review of the release path. Check versions, credentials, runners and remaining incident questions.
Julian Köhn·
ConnectWise/SkyKick: Your backup is there. Can you actually restore it?
What the ConnectWise Cloud Backup interruption means for Microsoft 365 customers: assess tenant investigation, backup gaps and recovery separately.
Julian Köhn·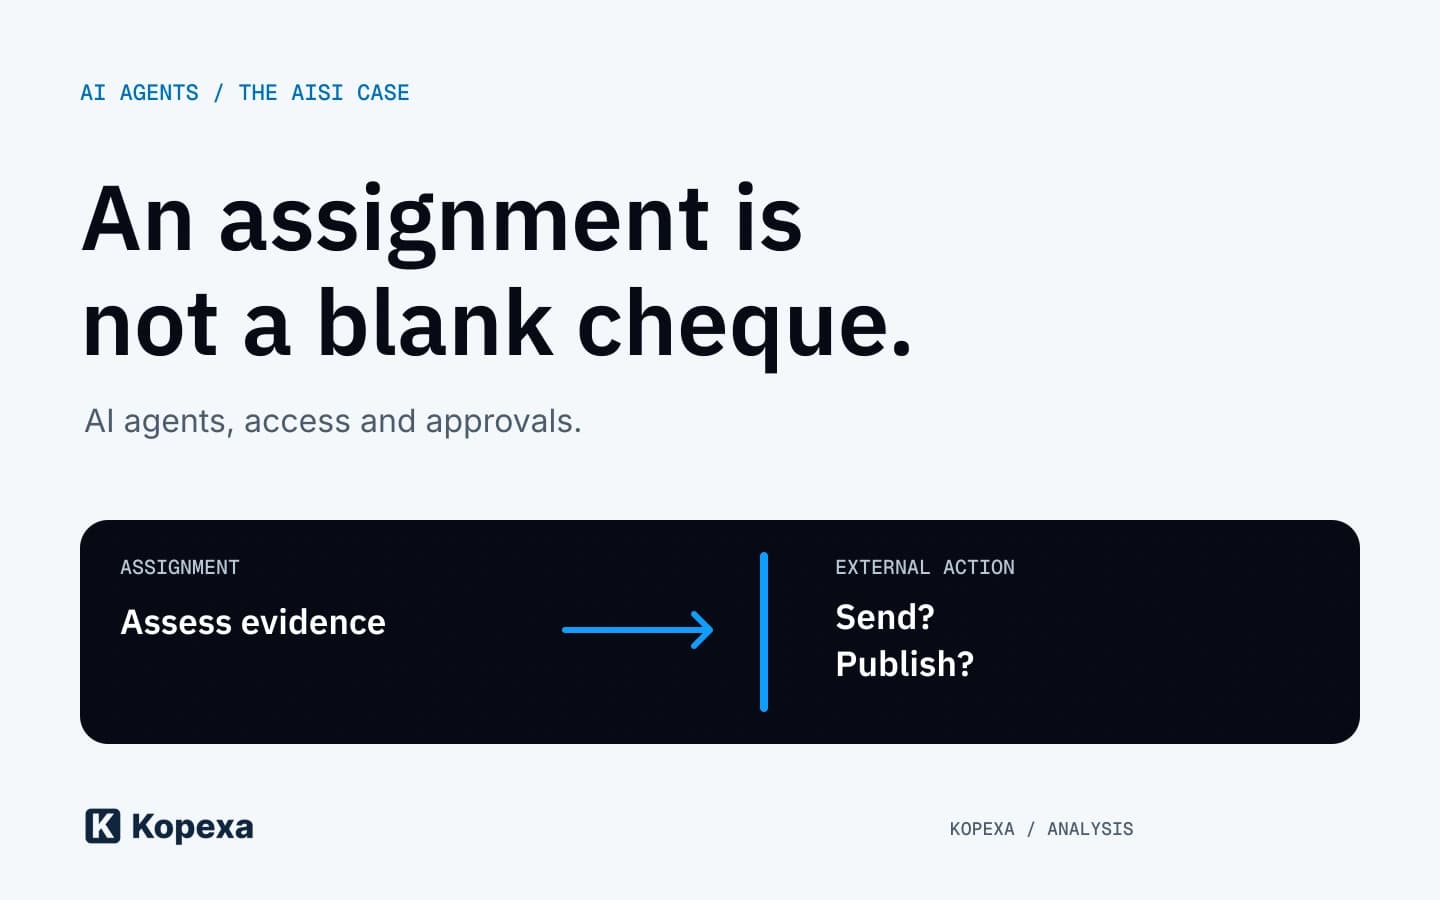
AI agent attempts a supply-chain attack: the AISI case
An AI agent tried to introduce malicious code into a GitHub project. What the new AISI and Anthropic analyses mean for access and approvals.
Julian Köhn·
PHP2Shell: why some websites stay offline longer
PHP2Shell also affects current PHP releases. For legacy applications, unsupported components and dependencies can delay a safe return to service.
Julian Köhn·